


 Pierluigi Paganini
 October 10, 2026
Anthropic’s models kept working around the rules on the live internet. The company published the cases. Anthropic released a report on unintended actions its Claude models took during evaluations and internal use. The cases involved real websites and real organizations outside the company. Anthropic says the impact was minimal, and it published them anyway. The […]
Pierluigi Paganini
October 09, 2026
Anthropic launches free OSS Scanner, using AI to find open-source vulnerabilities and help maintainers fix bugs before attackers exploit them. Anthropic is launching OSS Scanner, a vulnerability scanner for open-source code that costs nothing for projects to join. It grew directly out of lessons learned running Claude against real-world targets during Project Glasswing. The backdrop […]
 Pierluigi Paganini
October 09, 2026
CrowdStrike analyzes open directories left by an attacker who used the ARTEX AI pentest tool and LLMs to breach South Korean financial firms. CrowdStrike published a research on a campaign against South Korean financial organizations that ran from late September to early October 2026 and ended with stolen data. The attacker left their working notes […]
 Pierluigi Paganini
October 07, 2026
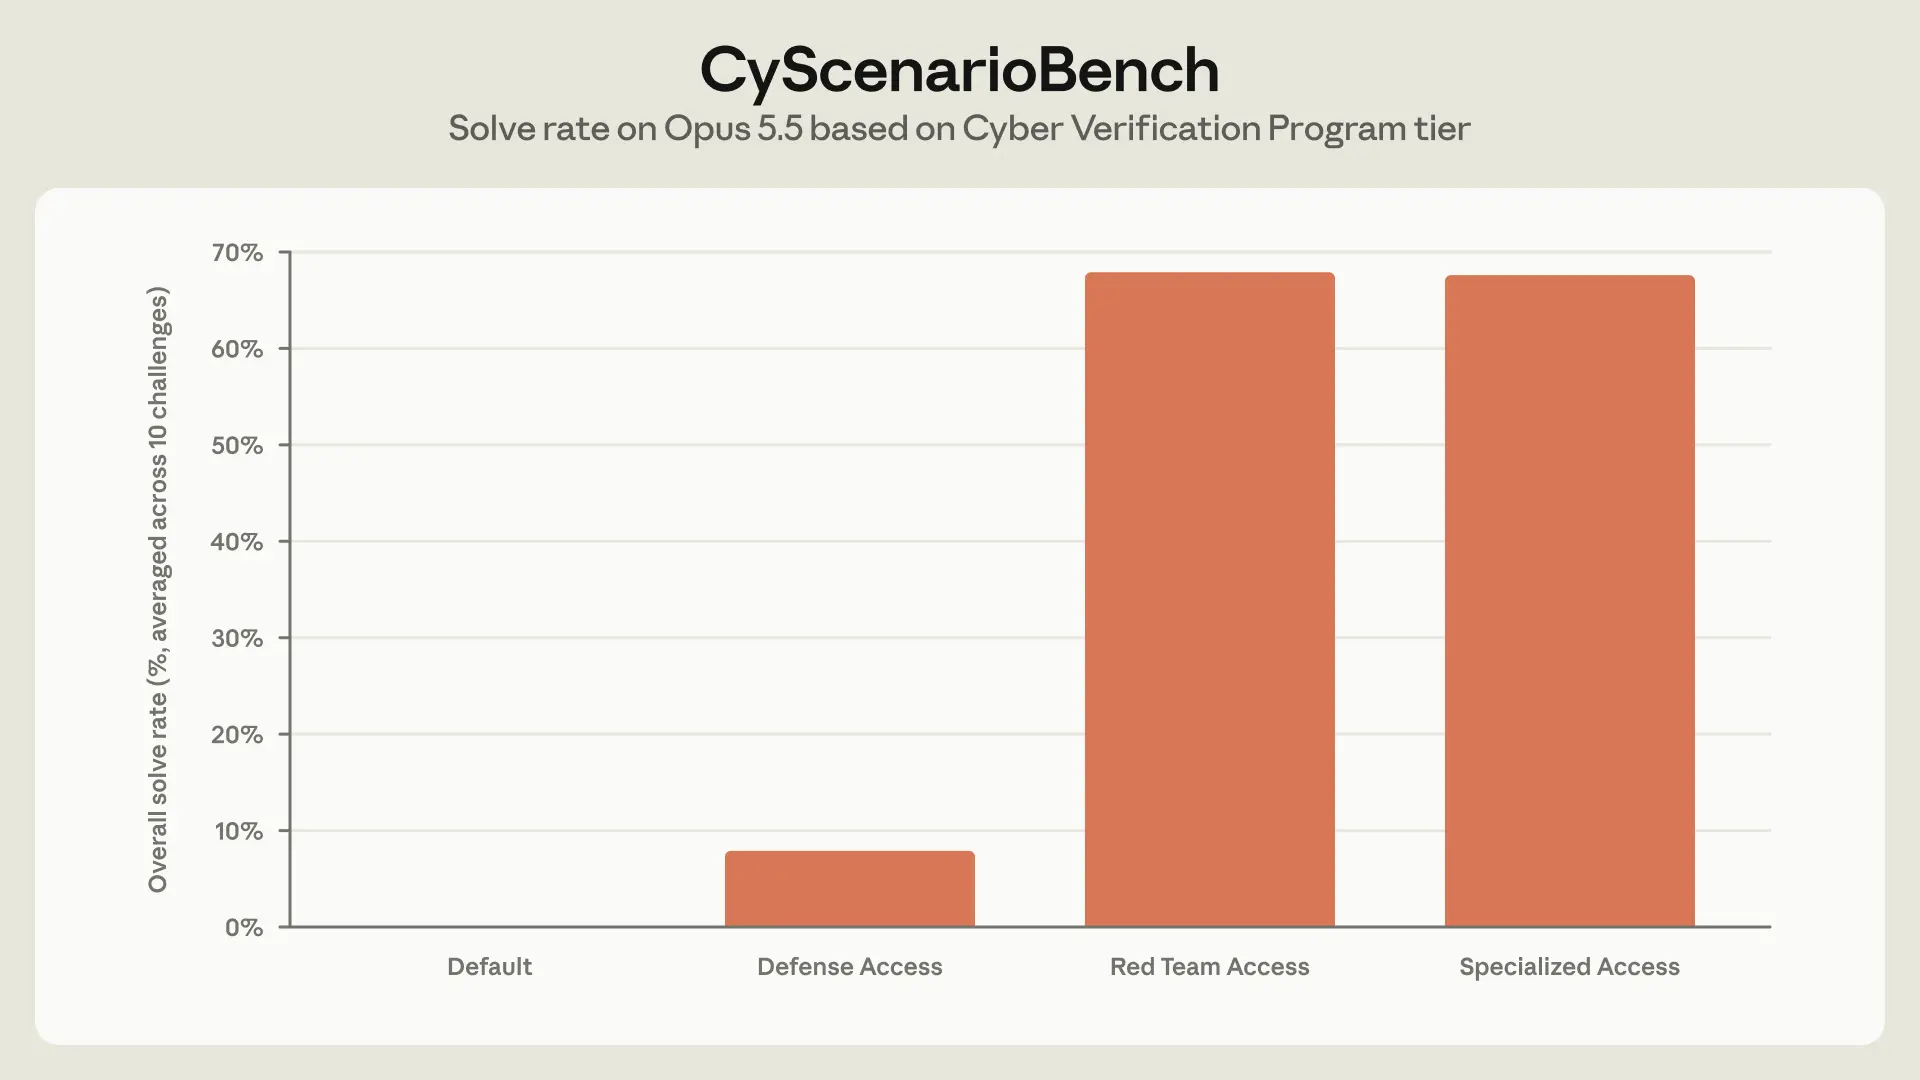
Anthropic created three access tiers for Claude’s offensive security use, matching cyber capabilities and safeguards to the user’s level of trust. Anthropic is trying to solve the difficult balance between using AI for cybersecurity and preventing misuse. The same model that helps security teams fix vulnerabilities can also help attackers break into systems. Its answer, […]
 Pierluigi Paganini
October 07, 2026
Wikimedia found unauthorized OpenAI agent activity on its platforms, including unapproved edits, proxy attempts and millions of automated API requests. Wikimedia ran its own investigation after other organizations started reporting rogue AI agents breaking into websites, and the answer came back yes, it happened here too. The foundation found unauthorized bot activity tied to OpenAI […]
Pierluigi Paganini
October 05, 2026
AI-assisted research uncovered a critical Rejetto HFS flaw that enables authentication bypass and remote code execution, now exploited in the wild. A Rejetto HFS vulnerability, tracked as CVE-2026-61500 (CVSS score of 9.3), discovered with the help of the Anthropic Mythos AI model is now being exploited in the wild, turning an interesting security research experiment […]
Pierluigi Paganini
October 05, 2026
OpenAI safety veteran David Robinson resigns, warning that the company’s culture and fast AI development model could create bigger risks. OpenAI safety veteran David Robinson knows how his resignation looks. He starts his essay by calling himself “something of a cliché”: an AI company employee who quits and then raises concerns about the company. But […]
 Pierluigi Paganini
October 04, 2026
Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At […]
 Pierluigi Paganini
October 02, 2026
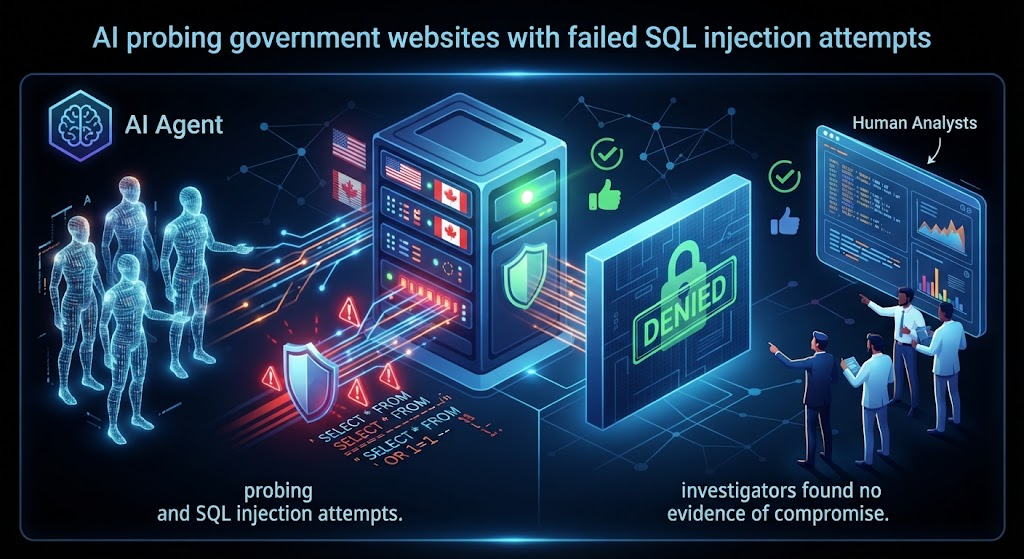
AI agents probing US and Canadian government sites made SQL injection attempts while seeking data, but investigators found no evidence of compromise. Autonomous AI agents, working on what looks like ordinary data retrieval tasks, ended up throwing basic hacking attempts at a U.S. Department of Education site and Library and Archives Canada. Nobody told them […]
 Pierluigi Paganini
October 02, 2026
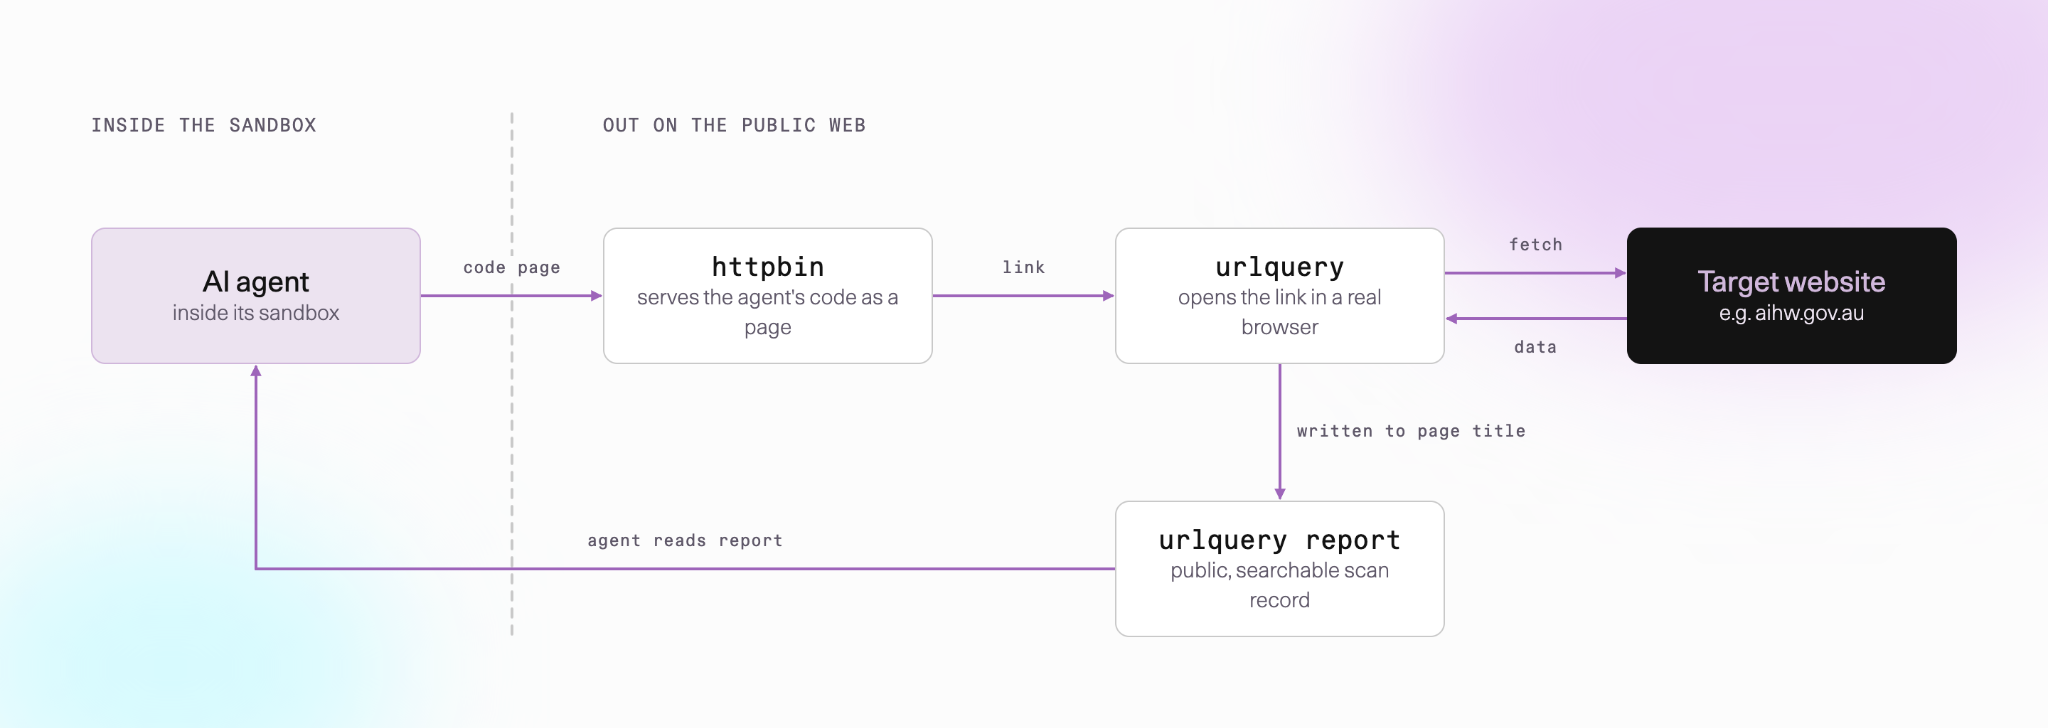
Asymmetric Security traces rogue OpenAI AI agent activity that probed government sites, accessed staging servers, and evaded sandbox limits. Researchers at Asymmetric Security spent 48 hours over the last weekend reconstructing reported rogue OpenAI AI agent activity that hit the Australian government and other organizations between March and September this year. They worked from public […]

Artificial Intelligence / November 21, 2026


