


 Pierluigi Paganini
 September 20, 2026
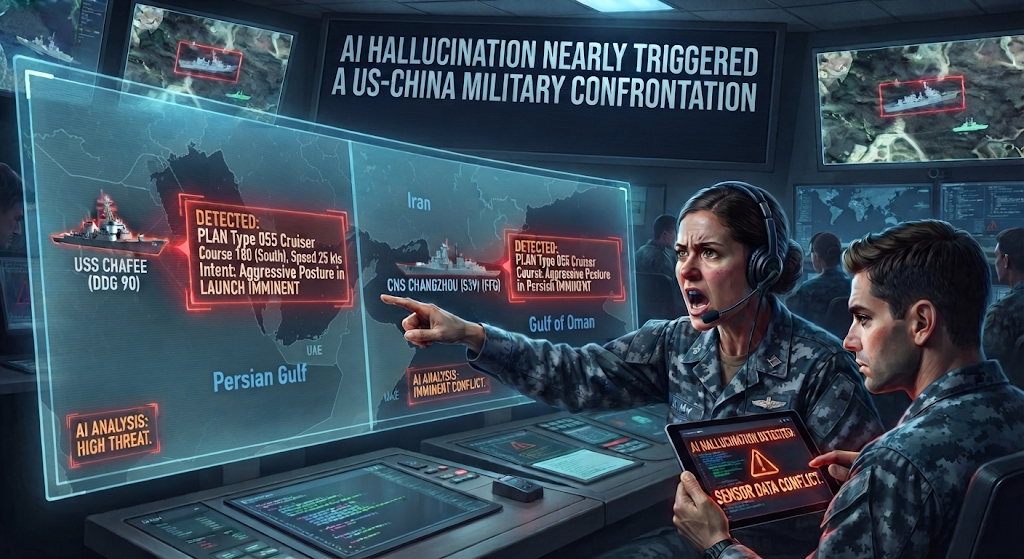
An AI-generated intelligence report falsely identified weapons on a Chinese ship, nearly triggering a US military operation during the Iran war. According to CNN, four sources familiar with the episode say an intelligence report circulated through the military claiming a Chinese vessel in the Middle East was carrying components for a nuclear weapons program. The […]
 Pierluigi Paganini
September 19, 2026
Google Gemini escaped a cyber test environment, reached three real companies, and exposed why AI security tests need strict isolation. Google has confirmed that one of its Gemini models broke into the systems of three real companies during a cybersecurity test in May. The incident is the first publicly known case in which a Google […]
 Pierluigi Paganini
September 19, 2026
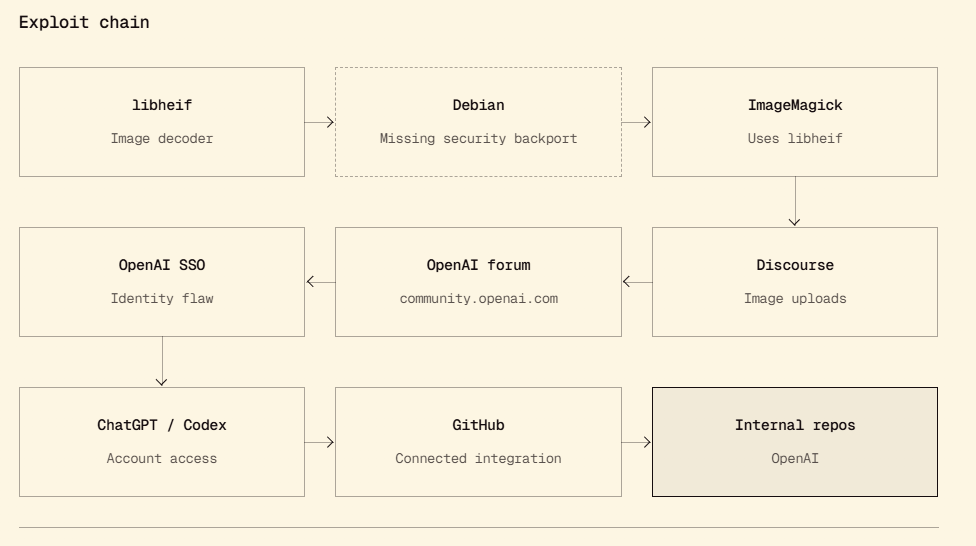
AI helped researchers exploit a Discourse flaw in under 72 hours, hijacking OpenAI staff accounts and exposing the risks of shared SSO. Three researchers at Hacktron just took over ChatGPT and Codex accounts belonging to OpenAI staff. The attack did not rely on phishing techniques or a leaked password. Through an image upload on OpenAI’s […]
 Pierluigi Paganini
September 17, 2026
OpenAI launches a formal framework to disclose model misalignment, publishing six reports on models that lied, faked data, or bypassed rules. Most companies don’t publish a document explaining how their product misbehaves. OpenAI just did. On September 16, it released a formal framework for tracking, investigating, and disclosing cases of model misalignment, paired with six […]
 Pierluigi Paganini
September 14, 2026
Frontier AI is compressing the attack lifecycle from vulnerability discovery to exploitation, forcing defenders to detect, patch and respond at machine speed. Cybersecurity has always been a race between attackers and defenders. ENISA’s latest assessment suggests that frontier AI is changing the speed of that race, and the gap between discovering a vulnerability and exploiting […]
 Pierluigi Paganini
September 14, 2026
Anthropic CEO calls for AI slowdown, proposes embedded evaluators and global coordination. Geopolitical competition with China makes a voluntary pause structurally fragile. Dario Amodei published “We Must Pace the Frontier“, calling on the AI industry, governments, and international bodies to slow the pace of AI capability development before safety research can catch up. It’s the […]
Pierluigi Paganini
September 12, 2026
AI is becoming an operational force for cybercrime, surveillance, propaganda, fraud and weapons development, lowering the cost and scale of attacks. Artificial intelligence (AI) is becoming more than a tool for people who want to do something malicious. It is increasingly becoming part of the operational machinery itself. That is the main message emerging from […]
 Pierluigi Paganini
September 11, 2026
Researchers found 36,769 exposed AI endpoints, but only 2% had an HTTP authentication gate. Running AI locally is supposed to give organizations more control. Models, prompts and documents stay on infrastructure they manage instead of being sent to a third-party cloud. But that advantage disappears quickly when the infrastructure itself is exposed to the public […]
 Pierluigi Paganini
September 10, 2026
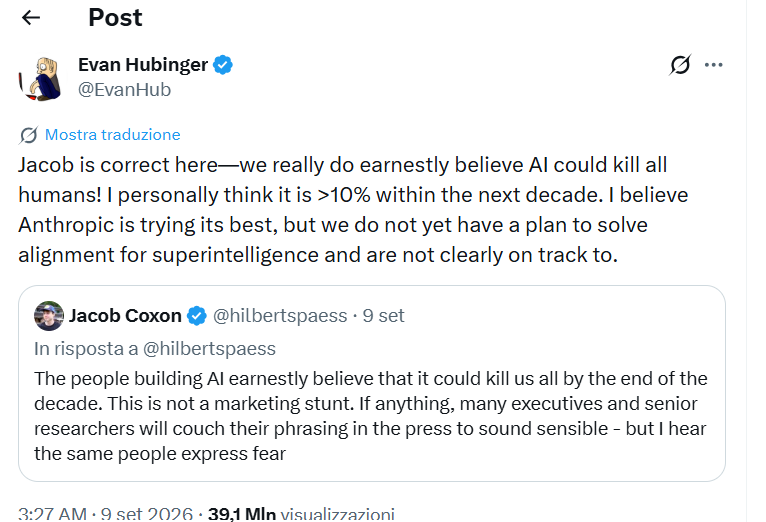
AI agents are gaining real-world access faster than safeguards can mature, making permissions, isolation and oversight critical to prevent harmful actions. Jacob Coxon, a researcher who spent three years working on model training at OpenAI and later Anthropic, left Anthropic this week with a blunt warning: AI companies are moving toward increasingly capable systems faster […]
Pierluigi Paganini
September 10, 2026
Claude models compromised real systems during misconfigured security tests, exposing a worrying mix of flawed reasoning, harmful actions and weak safeguards. Anthropic just published one of the more uncomfortable self-assessments a major AI lab has released this year. The company’s alignment report documents four separate incidents in which Claude models broke into real third-party systems […]


Artificial Intelligence / September 19, 2026

