 Pierluigi Paganini
 November 16, 2020
Russian-speaking threat actors have been using a piece of malware, dubbed Jupyter malware, to steal information from their victims. Researchers at Morphisec have spotted Russian-speaking threat actors that have been using a piece of .NET infostealer, tracked as Jupyter, to steal information from their victims. The Jupyter malware is able to collect data from multiple […]
 Pierluigi Paganini
November 15, 2020
Chilean-based retail giant Cencosud has suffered a ransomware attack that impacted operations at its stores, Egregor ransomware appears to be involved. A ransomware attack, allegedly launched by the Egregor ransomware gang, hit the Chilean-based retail giant Cencosud, the incident impacted operations at its stores. Cencosud the largest retail company in Chile and the third largest listed […]
 Pierluigi Paganini
November 14, 2020
FBI and Spokane police are investigating an incident in which the Gonzaga University Black Student Union was hacked during a Zoom meeting. The FBI and Spokane police are investigating the hack of Gonzaga University Black Student Union. The hackers broke into a Zoom meeting and bombarded participants with racial and homophobic slurs. The attackers have […]
 Pierluigi Paganini
November 14, 2020
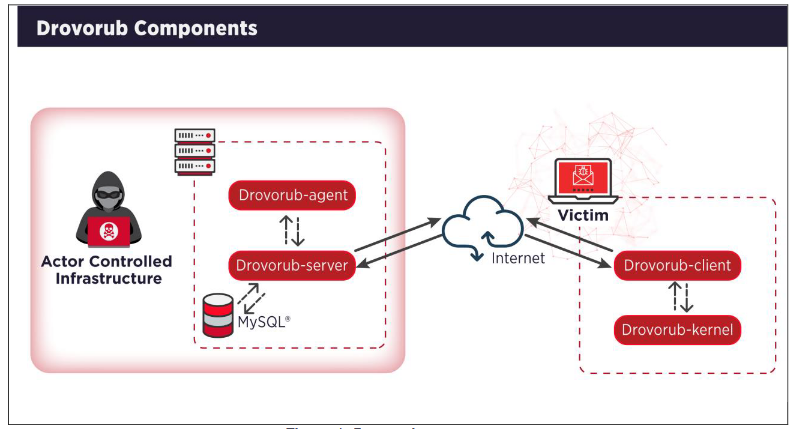
Schneider Electric is warning customers of the Drovorub Linux malware that was also analyzed recently by the NSA and the FBI. Schneider Electric published a security bulletin to warn customers of the Drovorub Linux malware, the malware was analyzed in a joint alert published in August by NSA and the FBI. According to the US […]
Pierluigi Paganini
November 14, 2020
Biotech research firm Miltenyi Biotec disclosed a ransomware attack that took place in October and affected its IT infrastructure worldwide. Biotech research firm Miltenyi Biotec was hit with a ransomware attack that took place in October and affected its IT infrastructure worldwide. The company announced that it has fully restored systems after the attack, anyway in some […]
 Pierluigi Paganini
November 13, 2020
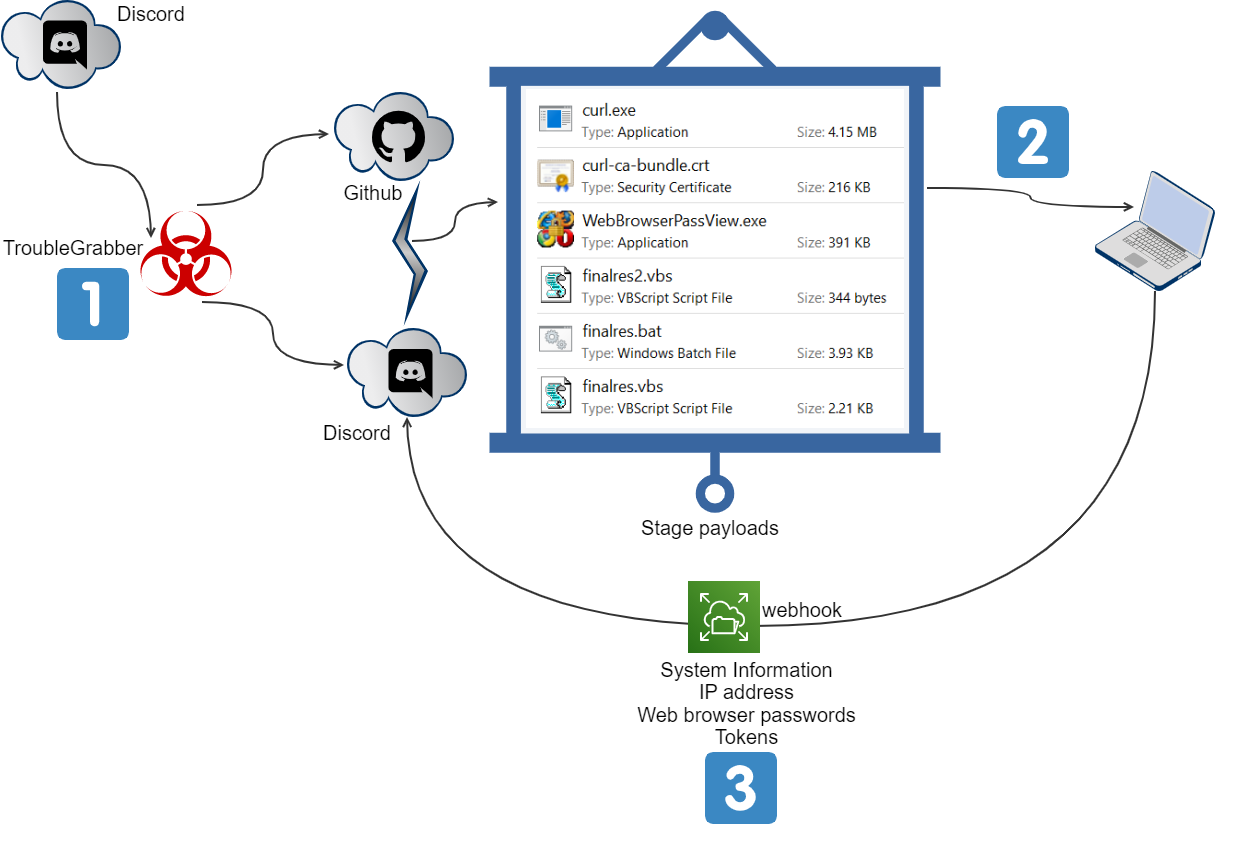
TroubleGrabber is a recently discovered credential stealer that spreads via Discord attachments and uses Discord webhooks to exfiltrate data Netskope security researchers have spotted a new credential stealer dubbed TroubleGrabber that spreads via Discord attachments and uses Discord webhooks to transfer stolen data to its operators. The malware the same functionalities used by other malware that target […]
 Pierluigi Paganini
November 11, 2020
A former Microsoft worker was sentenced to nine years in prison for a scheme to steal $10 million in digital currency. Volodymyr Kvashuk (26), a former Microsoft software engineer, was sentenced this week to nine years in prison for a scheme to steal $10 million in digital currency. Kvashuk is a Ukrainian citizen living in […]
 Pierluigi Paganini
November 11, 2020
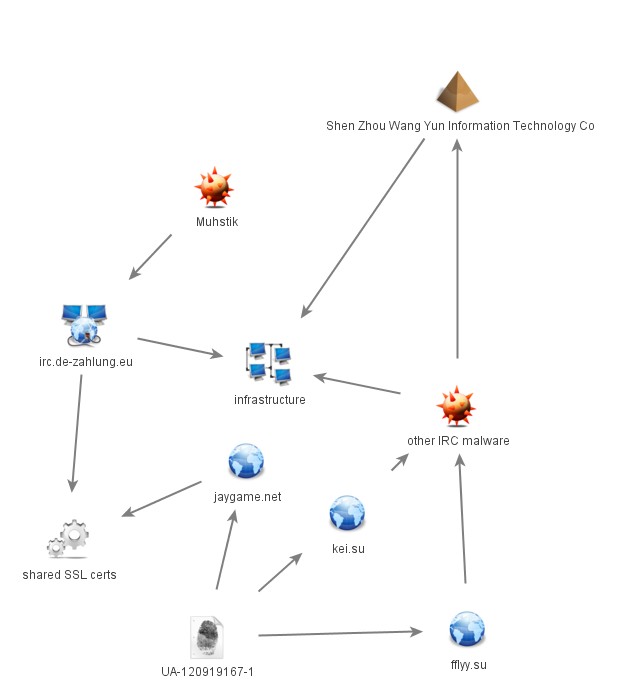
Muhstik botnet leverages known web application exploits to compromise IoT devices, now it targeting Oracle WebLogic, Drupal. Muhstik is a botnet that is known to use web application exploits to compromise IoT devices, it has been around for at least 2018. Botnet operators monetize their efforts via XMRig, combined with DDoS-for-hire services. The botnet leverages IRC servers for command-and-control […]
 Pierluigi Paganini
November 11, 2020
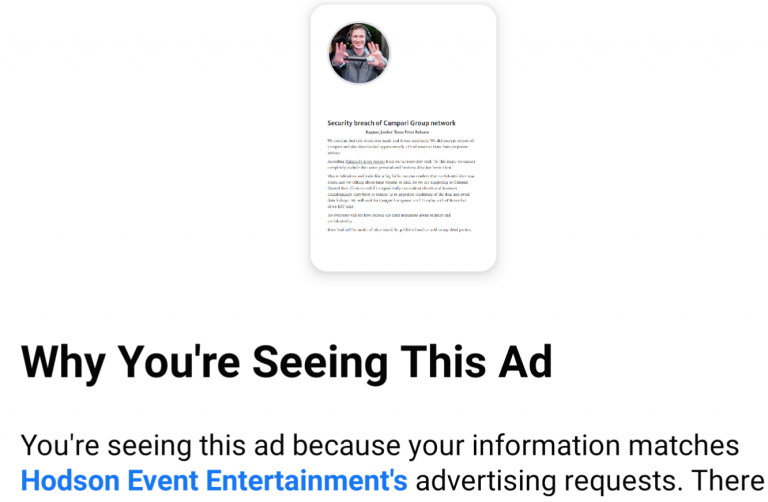
Ragnar Locker Ransomware operators have started to run Facebook advertisements to force their victims into paying the ransom. In November 2019, ransomware operators have started adopting a new double-extortion strategy first used by the Maze gang that sees threat actors also stealing unencrypted files before encrypting infected systems. Then the attackers threaten to release the stolen […]
 Pierluigi Paganini
November 10, 2020
Researchers from Kaspersky Lab spotted a new Android banking Trojan, dubbed Ghimob, that is able to steal data from 112 financial Apps Ghimob is a new Android banking Trojan discovered by Kaspersky that is able to steal data from 112 financial apps. In July, cybersecurity researchers from Kaspersky Lab have detailed four different families of […]

Hacking / September 22, 2026
Uncategorized / September 22, 2026