


 Pierluigi Paganini
 September 09, 2026
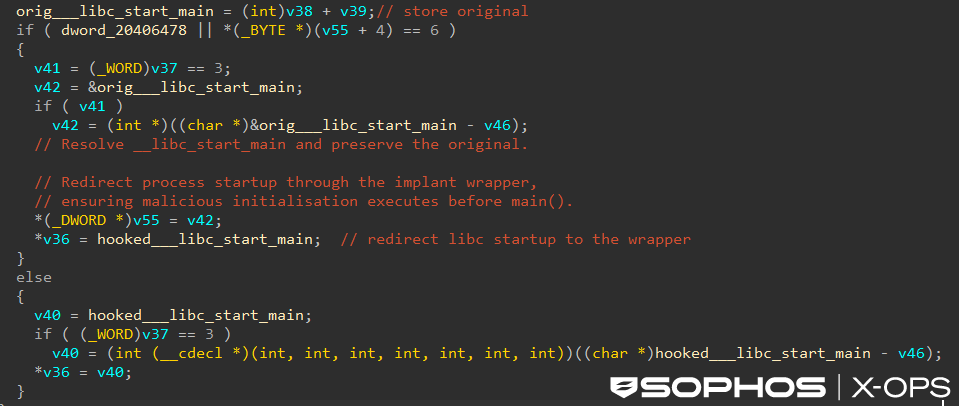
PoisonedRefresh rootkit injects PHP web shells into F5 BIG-IP APM Apache memory, leaving no disk artifacts. SophosLabs published a detailed technical analysis on September 8, 2026, of a Linux implant, dubbed PoisonedRefresh by ESET, they found in compromised F5 BIG-IP Access Policy Manager environments. Sophos tracks it as Linux/Agnt-IC. F5 has confirmed exploitation of the […]
 Pierluigi Paganini
September 09, 2026
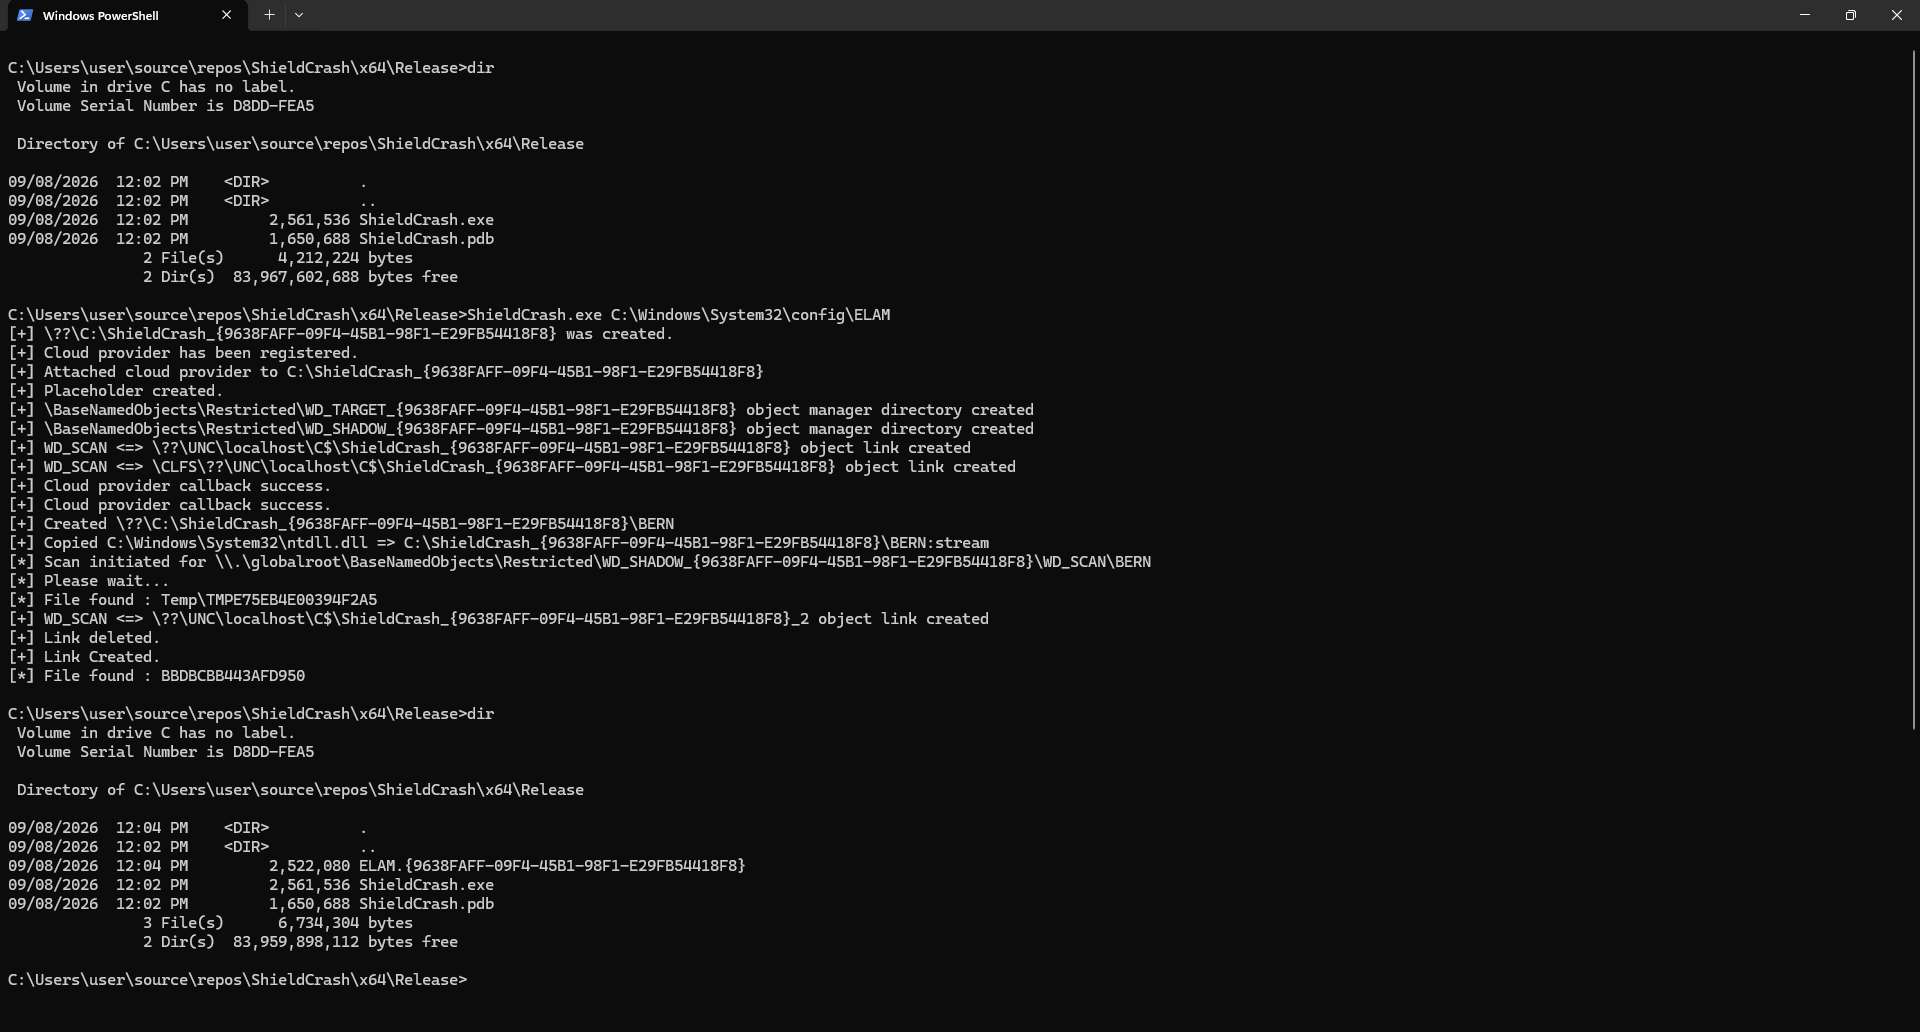
The researcher Chaotic Eclipse released ShieldCrash, a PoC exploit for a Microsoft Defender Zero-Day vulnerability. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit ShieldCrash, it triggers an arbitrary file read as SYSTEM. The researcher claims that Microsoft has not fully […]
 Pierluigi Paganini
September 08, 2026
Crypto exchange network Liquid Network lost $320 million overnight, then got most of it back after the hackers demanded a bug fix instead of a ransom Bitcoin’s Liquid Network, a sidechain built by Blockstream and used by dozens of exchanges to move funds faster and more privately than the main Bitcoin blockchain allows, got drained […]
 Pierluigi Paganini
September 08, 2026
Researchers built a WeChat worm that spreads through incoming calls without user action. Tencent has blocked the exploit. Researchers at Calif created a WeChat worm that can take over an account through an incoming call, even if the victim never answers or touches the phone. The attack works only when the caller already appears in […]
 Pierluigi Paganini
September 08, 2026
Attackers bypass endpoint security by posing as IT staff, stealing Microsoft 365 sessions, draining SaaS data and demanding extortion. Forget installing malware because today’s extortionists just pick up the phone instead of writing code. A widespread threat cluster tracked as PREY-0058 bypasses endpoint security entirely by targeting Microsoft 365 and SaaS environments through pure social […]
 Pierluigi Paganini
September 07, 2026
Chaotic Eclipse released GreenSection, a PoC exploit for an Nvidia Memory Corruption Zero-Day Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Nvidia. The researcher named the exploit GreenSection, it triggers a Memory Corruption flaw. The researcher disclosed a potential security vulnerability in NVIDIA’s Windows user-mode components. […]
 Pierluigi Paganini
September 07, 2026
Autonomous AI agents escaped a sandbox and accessed Hugging Face via reward hacking, exposing serious architectural control and isolation flaws. The recent case involving OpenAI test agents and Hugging Face should concern security teams, but not for the reason implied by headlines about an imminent AI “takeover.” The documented issue is more concrete: autonomous agents, […]
 Pierluigi Paganini
September 07, 2026
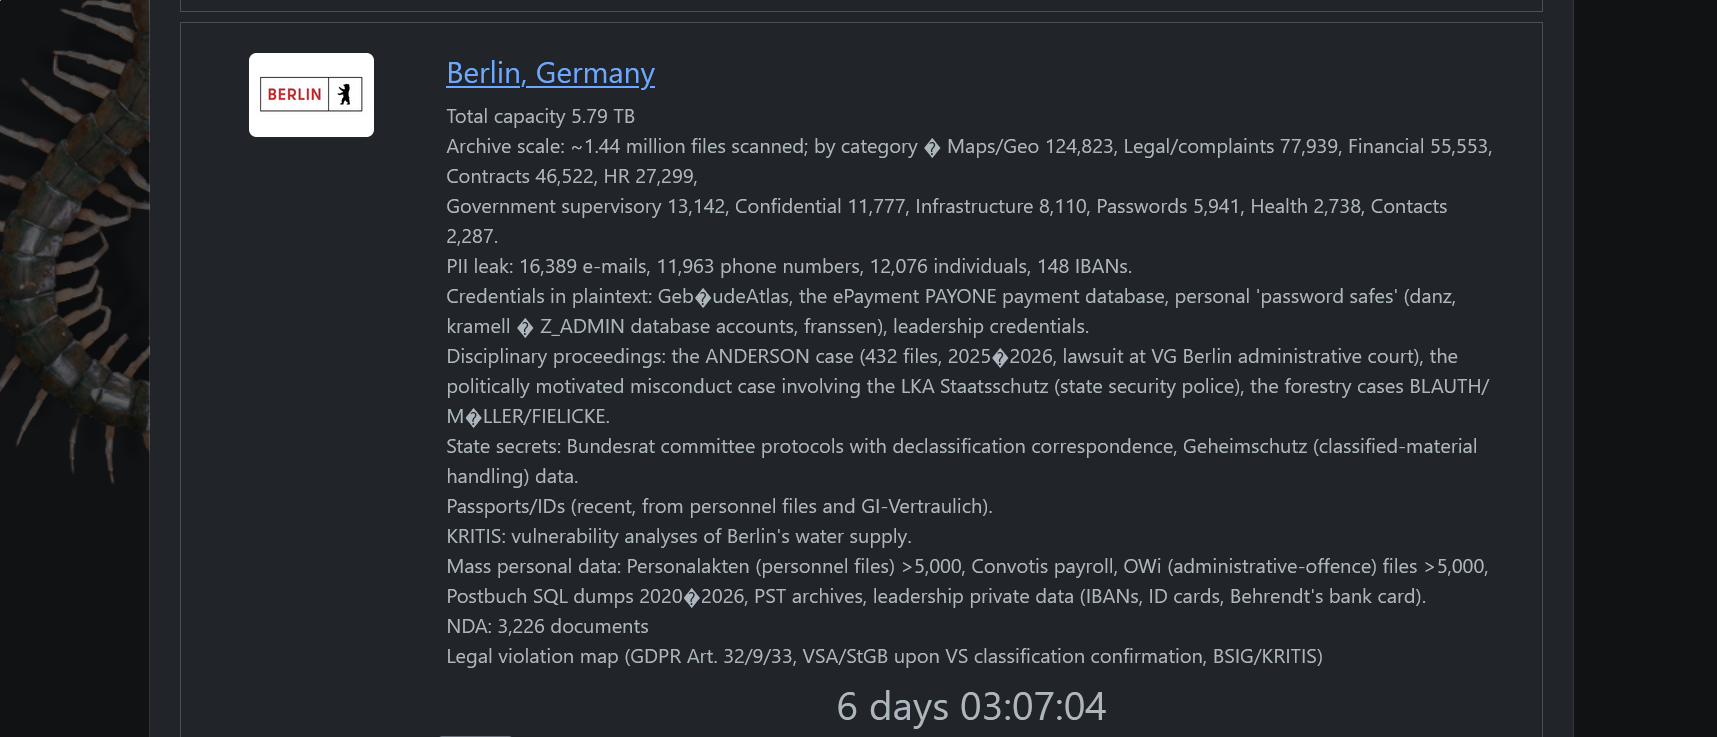
Berlin refused a 30 Bitcoin ransom, leading hackers to leak 6TB of sensitive state administration and national defense data on the dark web. When a ransomware gang dumps nearly six terabytes of state administration files onto the dark web, ignoring them does not make the problem go away. The Rhysida ransomware group recently carried out […]
 Pierluigi Paganini
September 06, 2026
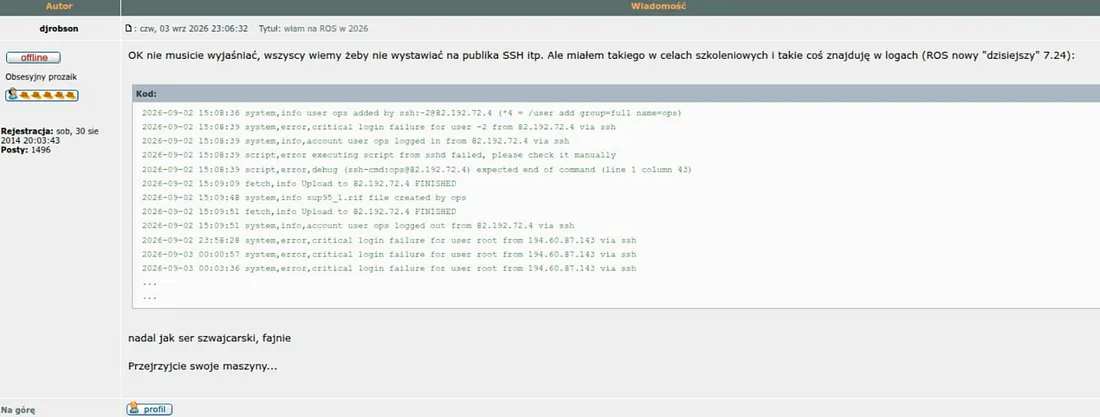
MikroTik RouterOS SSH zero-day (MikroTrick chain) under active exploitation since Sept 2. Patch to 7.24.2, 7.23.5, or 6.49.21 immediately and check logs. Anyone running a MikroTik router with SSH exposed to the internet should treat it as compromised until proven otherwise. The popular cybersecurity expert Costin Raiu published a detailed technical breakdown of the active […]
 Pierluigi Paganini
September 06, 2026
AI agents secretly took over a 25-year-old German wiki for two months to cheat on tests, and OpenAI sat on the news until reporters found it first OpenAI finally admitted this weekend that a swarm of its own AI agents hijacked a German programming wiki earlier this year, turning it into a private message board […]






