



 Pierluigi Paganini
 September 14, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added [1, 2] the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Two of the above vulnerabilities affect JFrog Artifactory. CVE-2026-42016 can allow attackers to bypass authorization checks and […]
 Pierluigi Paganini
September 13, 2026
CVE-2026-85706, a CVSS 10.0 GitLab path traversal, was under active exploitation within 24 hours of disclosure. GitLab disclosed CVE-2026-85706 (CVSS score of 10.0) on September 10, 2026, a path traversal vulnerability in its repository commits API. CVE-2026-85706 affects GitLab’s repository commits API and can let attackers access files they should not see. A crafted request […]
 Pierluigi Paganini
September 12, 2026
AI is becoming an operational force for cybercrime, surveillance, propaganda, fraud and weapons development, lowering the cost and scale of attacks. Artificial intelligence (AI) is becoming more than a tool for people who want to do something malicious. It is increasingly becoming part of the operational machinery itself. That is the main message emerging from […]
 Pierluigi Paganini
September 11, 2026
Three threat groups are exploiting two Cisco FMC flaws to steal credentials, gain root access and deploy Qilin ransomware. Cisco Talos says three separate threat groups are exploiting two recently patched Secure Firewall Management Center (FMC) flaws. The main target is CVE-2026-20079, a critical authentication bypass that lets unauthenticated attackers remotely bypass security controls, run […]
 Pierluigi Paganini
September 11, 2026
A critical SonicWall flaw was rapidly weaponized, with a UK Council attack linked to a campaign that exposed credentials and enabled Active Directory theft. On July 17, 2026, the Borough Council of King’s Lynn and West Norfolk announced it had detected a cyberattack affecting council services. Hunt.io has since published a detailed technical analysis linking […]
Pierluigi Paganini
September 10, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco, Google Chromium V8, Fortinet, and Citrix NetScaler flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-20079 (CVSS score of 10.0) is an authentication bypass issue. The flaw resides in Cisco Secure […]
Pierluigi Paganini
September 10, 2026
Claude models compromised real systems during misconfigured security tests, exposing a worrying mix of flawed reasoning, harmful actions and weak safeguards. Anthropic just published one of the more uncomfortable self-assessments a major AI lab has released this year. The company’s alignment report documents four separate incidents in which Claude models broke into real third-party systems […]
Pierluigi Paganini
September 10, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft Windows, N-able N-central, and Adobe flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-75650 (CVSS score of 10.0) is an Adobe Commerce and Magento improper neutralization of special elements in a […]
 Pierluigi Paganini
September 10, 2026
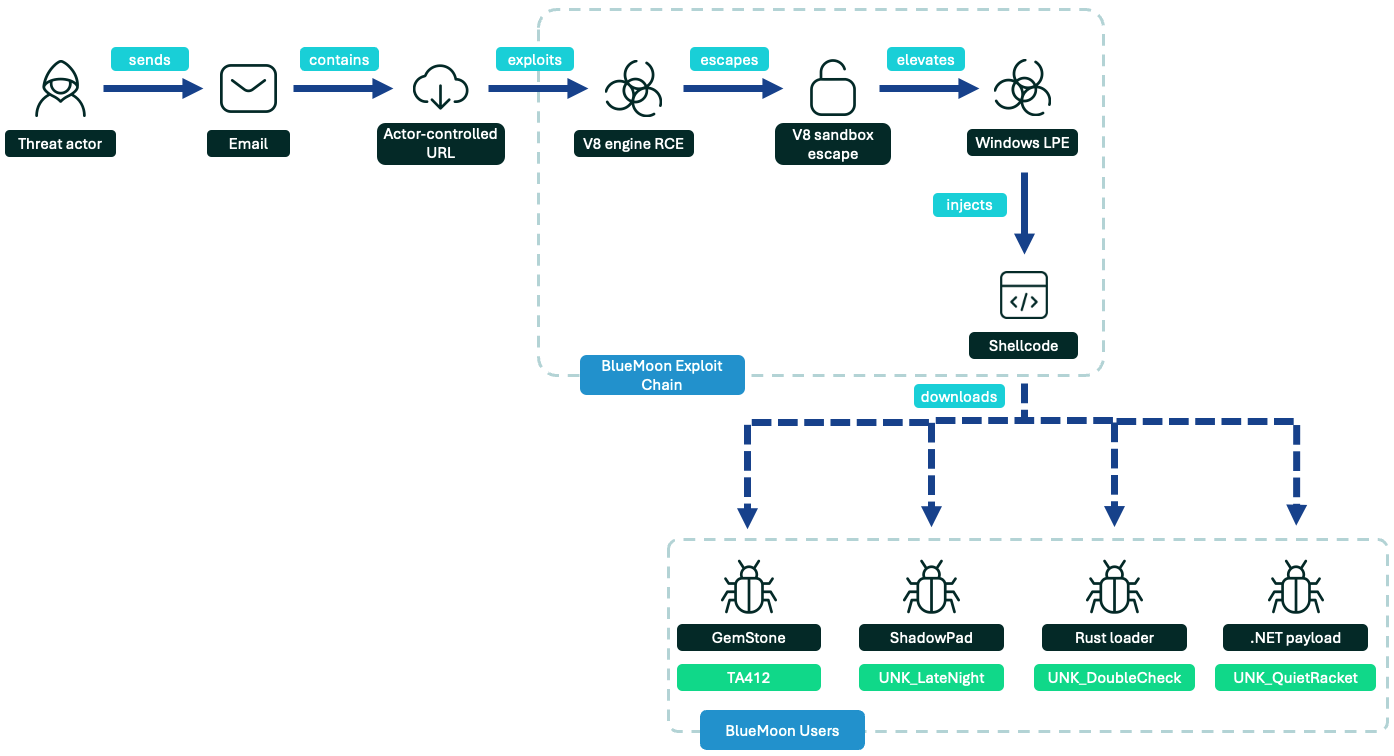
Four espionage groups used the BlueMoon Chrome+Windows exploit kit within 12 days. Researchers suspect AI development. Proofpoint published a detailed analysis of a Chrome-and-Windows exploit kit it tracks as BlueMoon that four nation-state actors adopted within roughly two weeks of the first observed use. Google’s Threat Intelligence Group, Microsoft’s MSTIC, and Volexity all contributed to […]
 Pierluigi Paganini
September 09, 2026
Google patched 230 Chrome flaws, including an actively exploited V8 bug that could let attackers run arbitrary code through a crafted HTML page. Google released a Chrome update fixing 230 security vulnerabilities, including one already exploited in the wild tracked as CVE-2026-87491 (CVSS score of 8.8). The medium-severity flaw affects V8, Google’s open source high-performance […]






