


 Pierluigi Paganini
 September 05, 2026
Attackers are exploiting two new PaperCut flaws to steal credentials and gain privileged access in education-sector attacks across the U.S. and Europe. Attackers are exploiting two recelty disclosed PaperCut flaws, CVE-2026-81578 and CVE-2026-82078, in attacks targeting schools and other education organizations in the U.S. and Europe, as reported by TheHackerNews. Arctic Wolf researchers observed threat […]
 Pierluigi Paganini
September 04, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Google Chromium V8 flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Google Chromium V8 flaw, tracked as CVE-2026-85046 (CVSS score of 8,8), to its Known Exploited Vulnerabilities (KEV) catalog. This week, Google released a Chrome security update fixing 12 […]
 Pierluigi Paganini
September 04, 2026
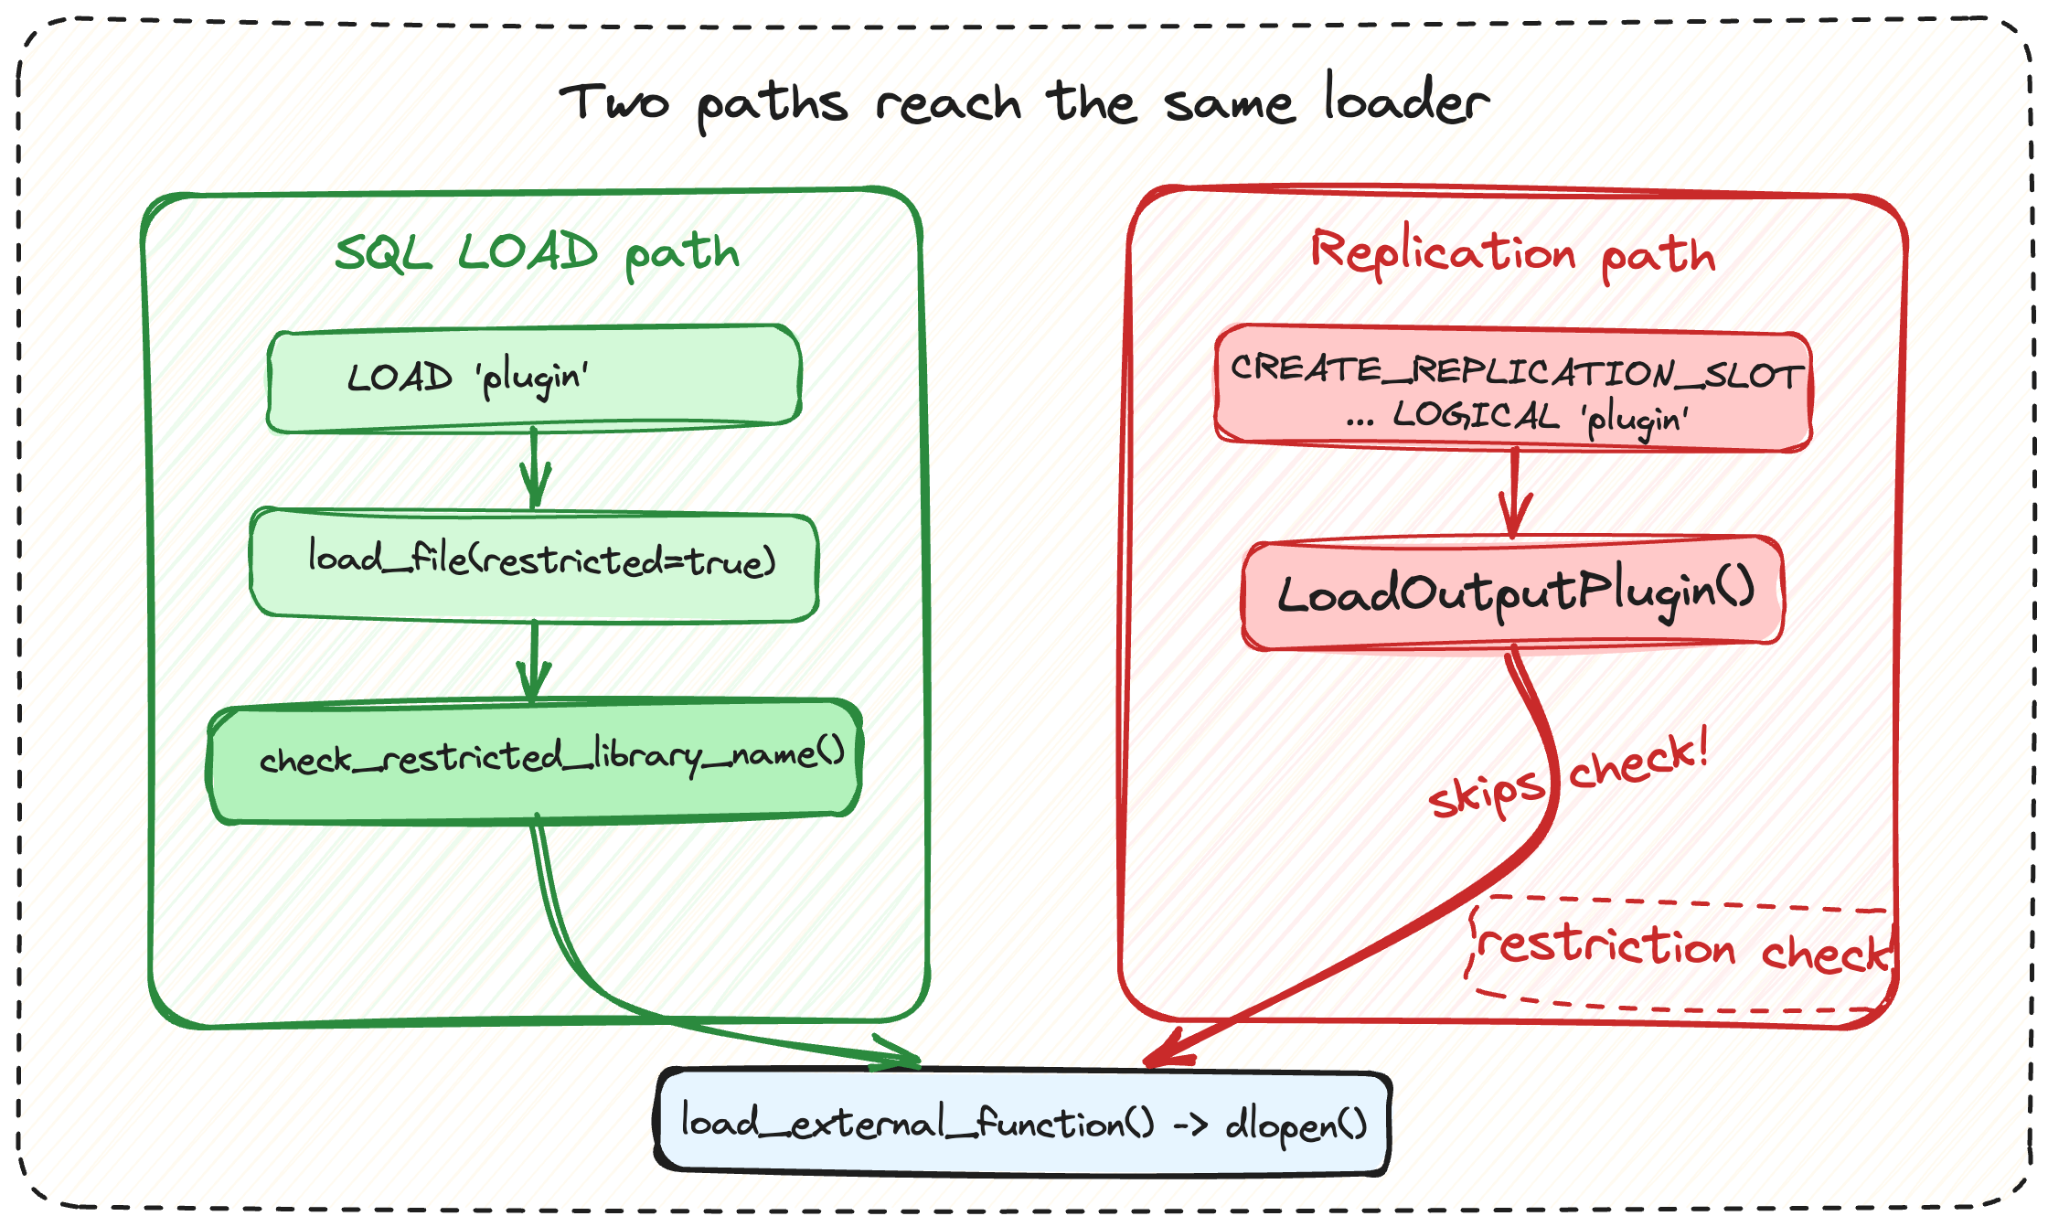
PostGREShell (CVE-2026-6471) is a 12-year-old PostgreSQL flaw that lets low-privileged attackers execute code and take over servers. Cyera researchers found a severe PostgreSQL vulnerability, dubbed PostGREShell and tracked as CVE-2026-6471 (CVSS score of 7.2). Present in releases dating back to 2014, the flaw can be exploited by attackers with low-level replication access to execute code, […]
 Pierluigi Paganini
September 04, 2026
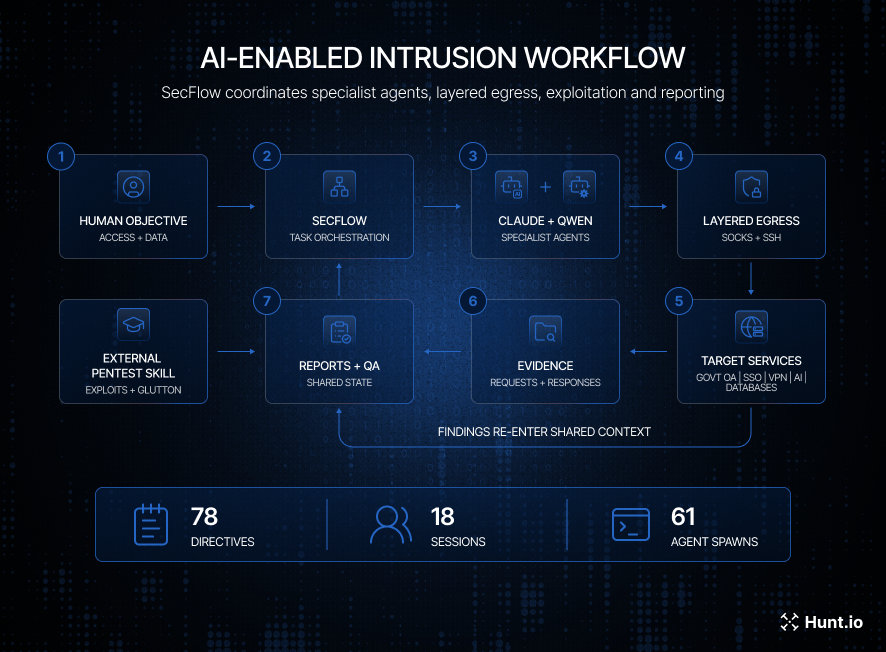
Hunt.io uncovered a Chinese-speaking campaign using AI agents to automate cyberattacks against Asian government, education and industrial targets. Threat intelligence firm Hunt.io just documented a second, separate China-linked campaign wiring commercial AI models directly into live cyberespionage operations, this time hitting Taiwan’s Kuomintang Party archives, Indonesia’s Ministry of Foreign Affairs, government and education systems in […]
 Pierluigi Paganini
September 04, 2026
Google patched 12 Chrome flaws, including an actively exploited V8 zero-day that could enable remote code execution through a crafted webpage. Google released a Chrome security update fixing 12 vulnerabilities, including CVE-2026-85046 (CVSS score of 8.8), an actively exploited V8 type confusion flaw. The bug affects Chrome’s JavaScript and WebAssembly engine and could let a […]
 Pierluigi Paganini
September 04, 2026
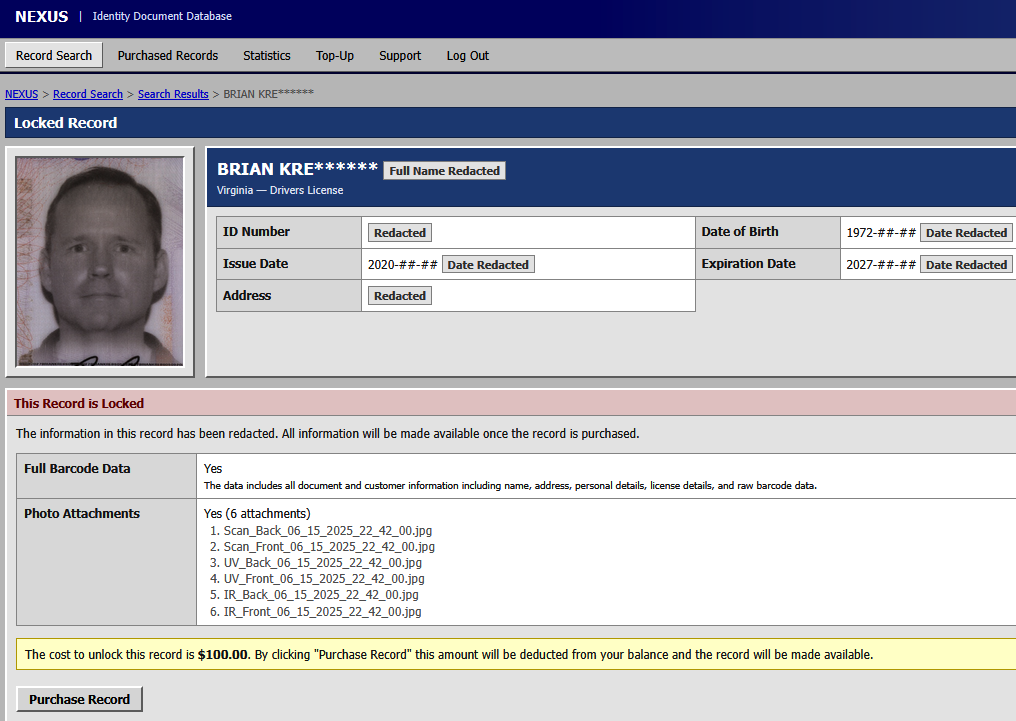
FBI probes suspected breach at IDScan.net after dark web service Nexus offered 153M+ US and Canadian driver’s license scans. A dark web identity theft service called Nexus appeared on September 1, 2026, offering searchable access to more than 153 million scanned driver’s licenses belonging to people in the United States and Canada. The FBI’s New […]
 Pierluigi Paganini
September 03, 2026
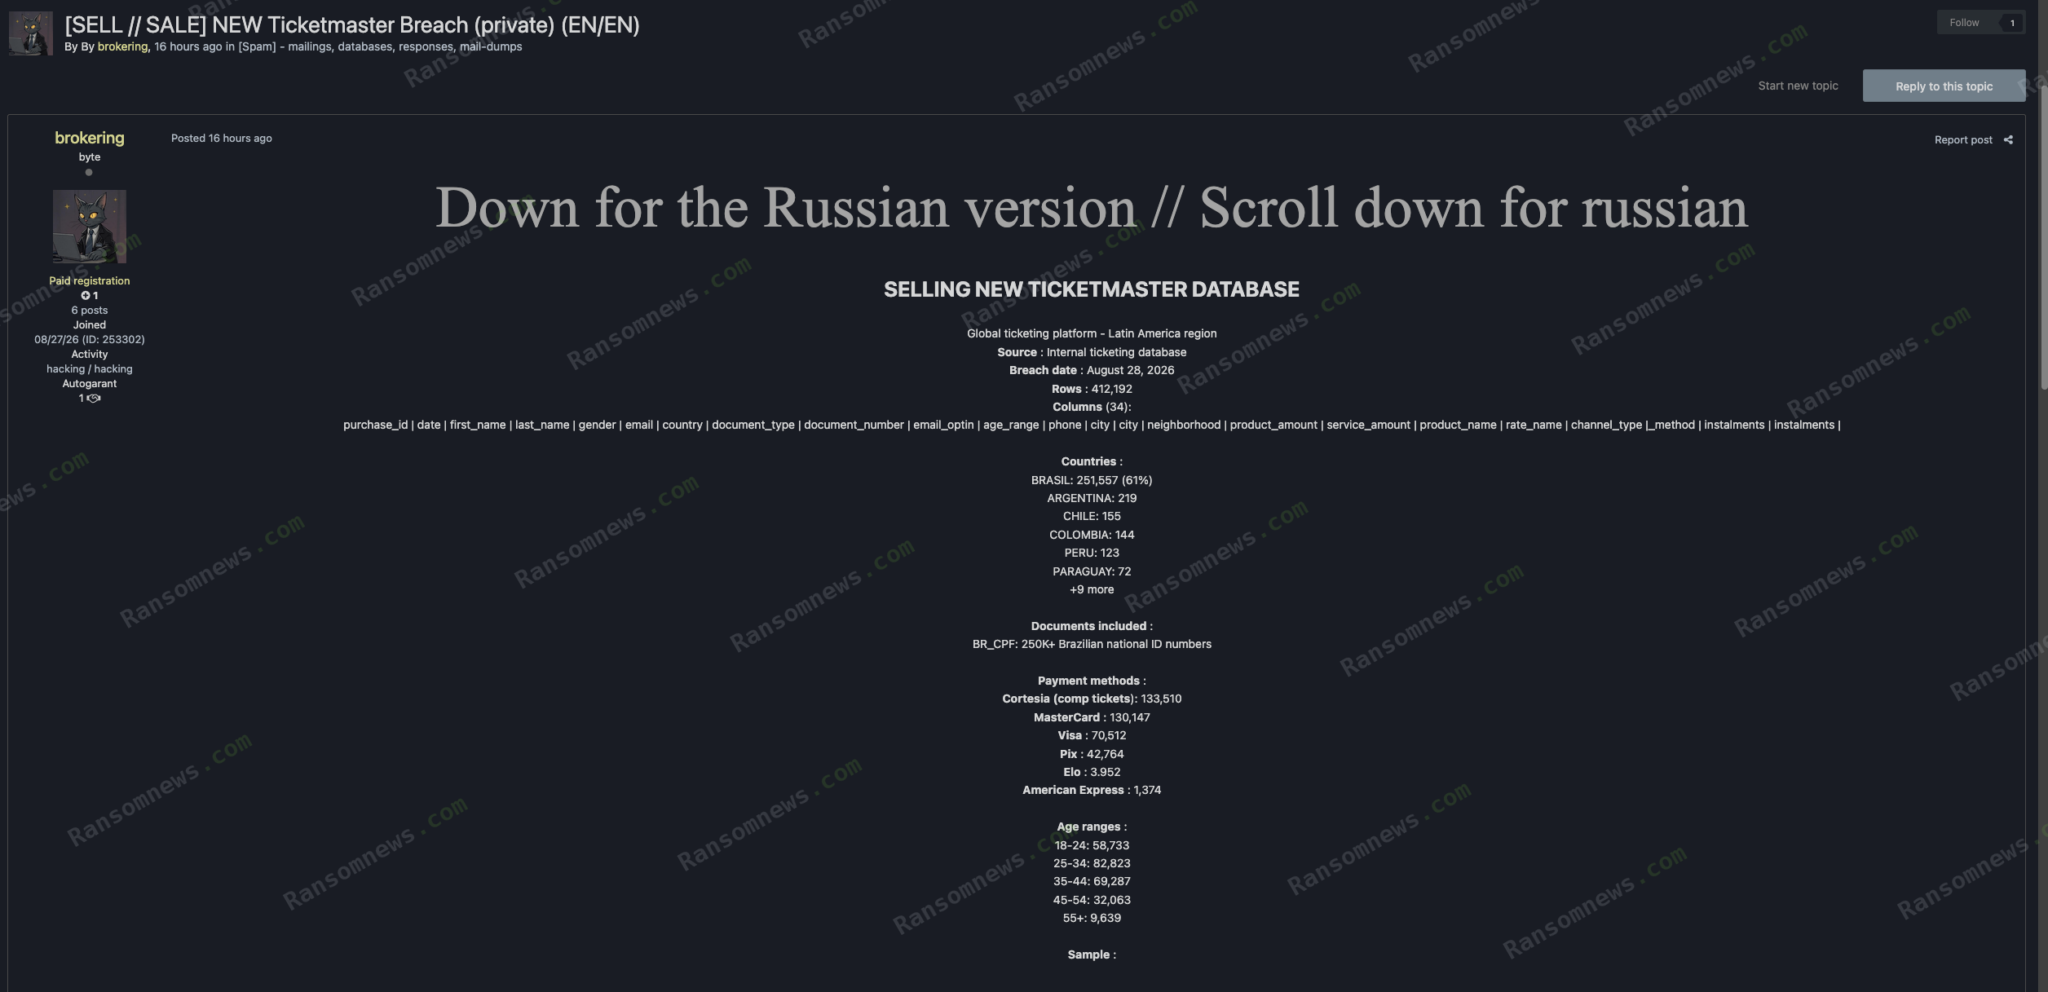
412,000 The Town 2025 festival buyer records are being sold for $10,000, with Brazil’s data openly marketed for bank fraud, loans and SIM registration. A seller on a Russian-language data-trading forum listed what they’re calling a Ticketmaster database on September 2, claiming over 412,000 Latin American purchase records with a heavy concentration of Brazilian data. […]
 Pierluigi Paganini
September 03, 2026
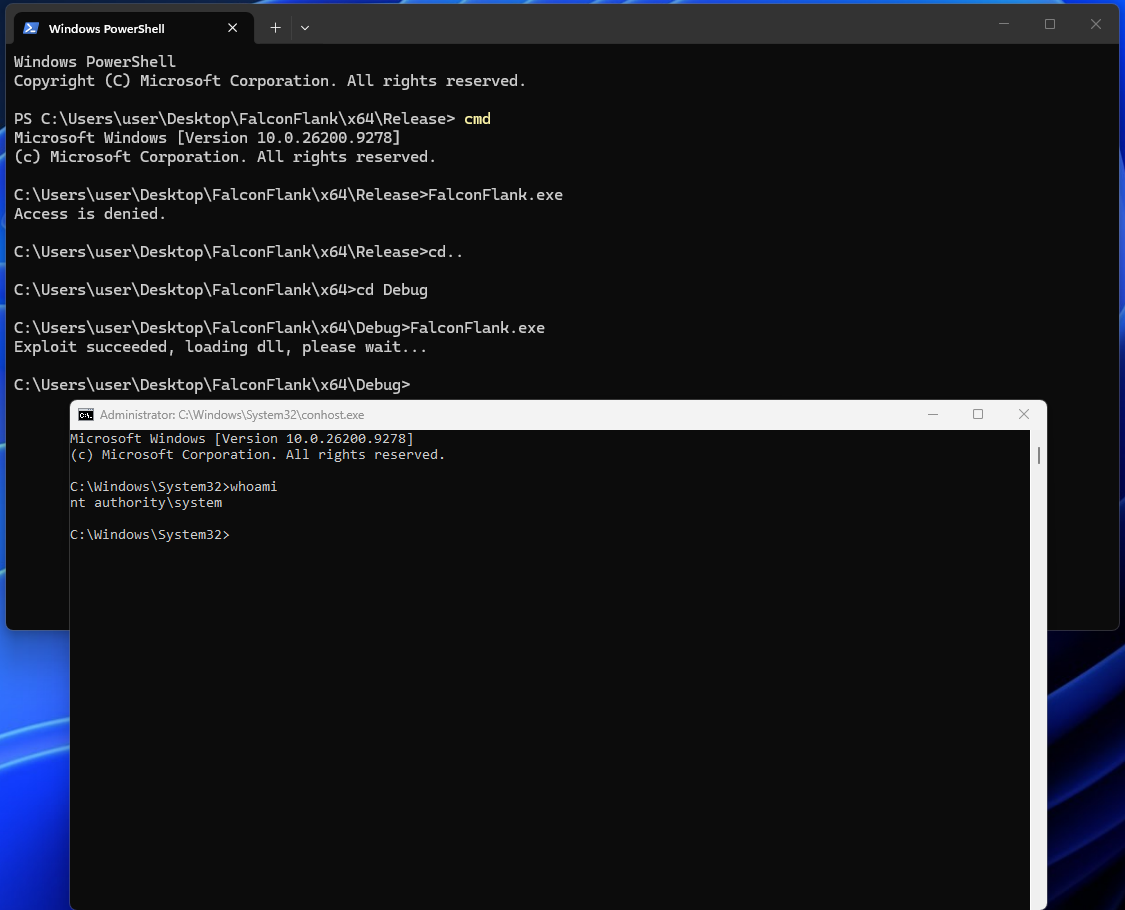
Chaotic Eclipse released FalconFlank, a PoC exploit for a Crowdstrike Falcon ZeroDay Elevation of Privileges Vulnerability Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Crowdstrike Falcon cybersecurity platform. The researcher named the exploit FalconFlank, it triggers a privilege escalation flaw. According to the researcher, FalconFlank abuses […]
 Pierluigi Paganini
September 02, 2026
OpenAI says Astra can autonomously find zero-days and build exploits, marking its first model to reach the “Critical” cyber risk level. Astra is now officially OpenAI’s highest-risk cybersecurity model. In August, OpenAI said it “couldn’t rule out” that its upcoming model had reached the highest cybersecurity risk level in its Preparedness Framework. In a new […]
 Pierluigi Paganini
September 02, 2026
SonicWall patched two zero-days in SMA 1000 VPNs, including a CVSS 10 pre-auth SSRF flaw, after confirming active exploitation. SonicWall has released security updates for two vulnerabilities in its SMA 1000 VPN appliances that are actively exploited in attacks in the wild. SonicWall’s researchers William Perry and Adam Babis discovered the vulnerabilities. SonicWall confirmed that […]






