


 Pierluigi Paganini
 August 12, 2021
The threat actor who hacked Poly Network cross-chain protocol stealing $611 million worth of cryptocurrency assets returns the stolen funds. The threat actor behind the hack of the Poly Network cross-chain protocol is now returning the stolen funds. The hackers have stolen $611 million worth of cryptocurrency assets, $273 million worth of Ethereum tokens, $253 million […]
Pierluigi Paganini
August 10, 2021
The cross-chain protocol Poly Network has been hacked, threat actors stole $611 million making this hack the largest DeFi hack to date. $611 million has reportedly been stolen in one of the largest cryptocurrency hacks. The cross-chain protocol Poly Network disclose a security breach, threat actors have stolen over $611 million in cryptocurrencies. The attackers have […]
 Pierluigi Paganini
August 10, 2021
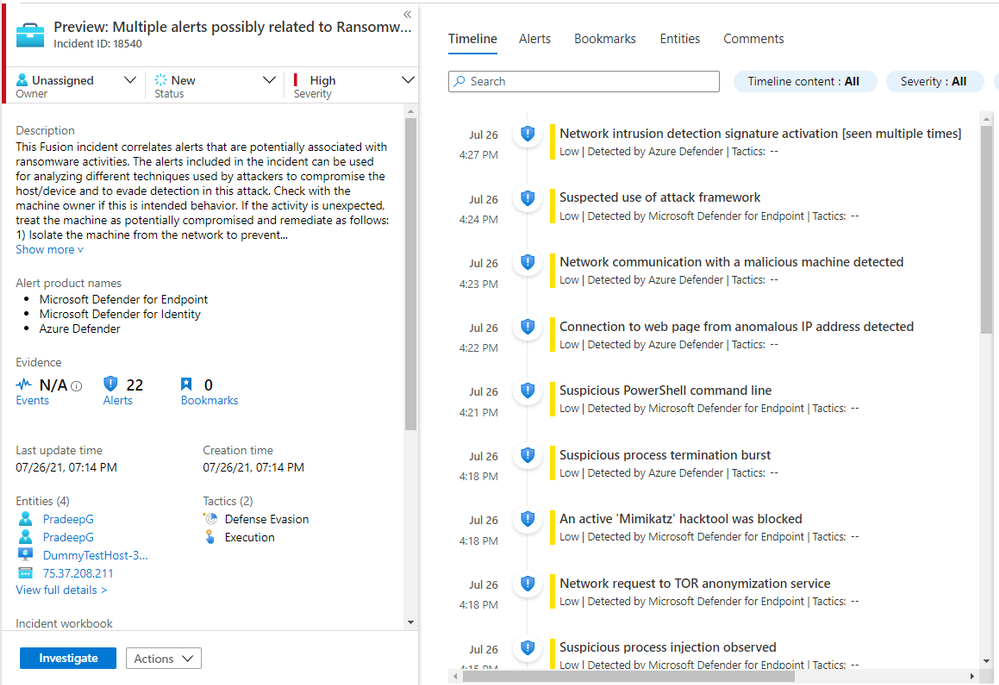
Microsoft Azure Sentinel cloud-native SIEM (Security Information and Event Management) platform used the Fusion machine learning model to detect ransomware attack. Microsoft Azure Sentinel cloud-native SIEM is using the Fusion machine learning model to analyze data across enterprise environments and detect the activity associated with potential threats, including ransomware attacks. When a potential ransomware attack […]
 Pierluigi Paganini
August 09, 2021
Threat actors are actively scanning for the Microsoft Exchange ProxyShell RCE flaws after technical details were released at the Black Hat conference. Threat actors started actively scanning for the Microsoft Exchange ProxyShell remote code execution flaws after researchers released technical details at the Black Hat hacking conference. ProxyShell is the name of three vulnerabilities that could be […]
 Pierluigi Paganini
August 07, 2021
Threat actors are actively exploiting a critical authentication bypass issue (CVE-2021-20090) affecting home routers with Arcadyan firmware. Threat actors actively exploit a critical authentication bypass vulnerability, tracked as CVE-2021-20090, impacting home routers with Arcadyan firmware to deploy a Mirai bot. “A path traversal vulnerability in the web interfaces of Buffalo WSR-2533DHPL2 firmware version <= 1.02 and […]
 Pierluigi Paganini
August 06, 2021
Security expert provided leak indicators for Conti ransomware operations that were recently disclosed by a disgruntled affiliate. An affiliate of the Conti RaaS has leaked the training material provided by the group to the customers of its RaaS, he also published the info about one of the operators. The Conti Ransomware operators offer their services to their […]
 Pierluigi Paganini
August 04, 2021
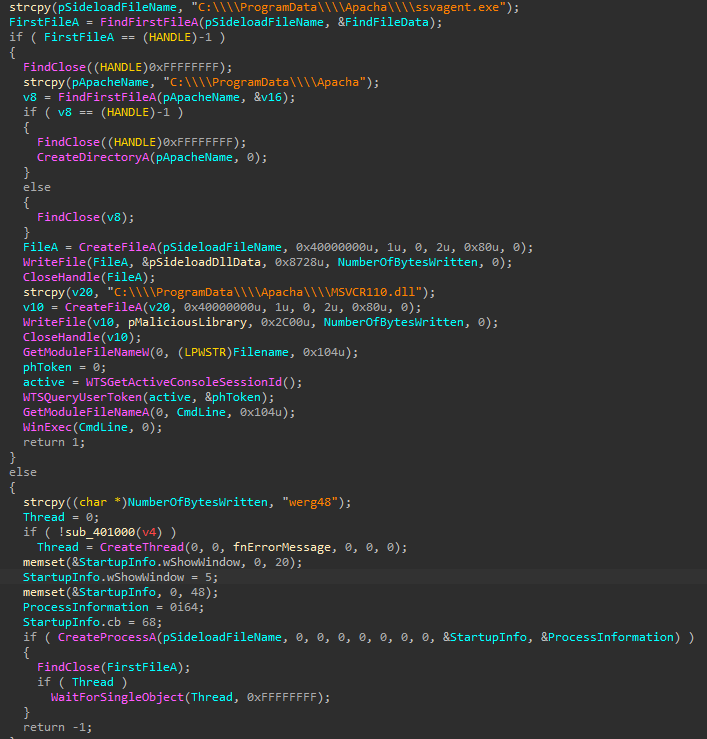
China-linked APT31 group employed a new strain of malware in attacks aimed at entities in Mongolia, Belarus, Canada, the US, and Russia. Researchers from Positive Technologies reported that China-linked APT31 group has been using a new piece of malware in a recent wave of attacks targeting Mongolia, Belarus, Canada, the United States, and Russia. Experts […]
 Pierluigi Paganini
August 04, 2021
INFRA:HALT is a set of vulnerabilities affecting a popular TCP/IP library commonly OT devices manufactured by more than 200 vendors. Security researchers from security teams at Forescout and JFrog have disclosed today 14 vulnerabilities that impact a popular TCP/IP library named NicheStack commonly used in industrial equipment and Operational Technology (OT) devices manufactured by more […]
 Pierluigi Paganini
August 03, 2021
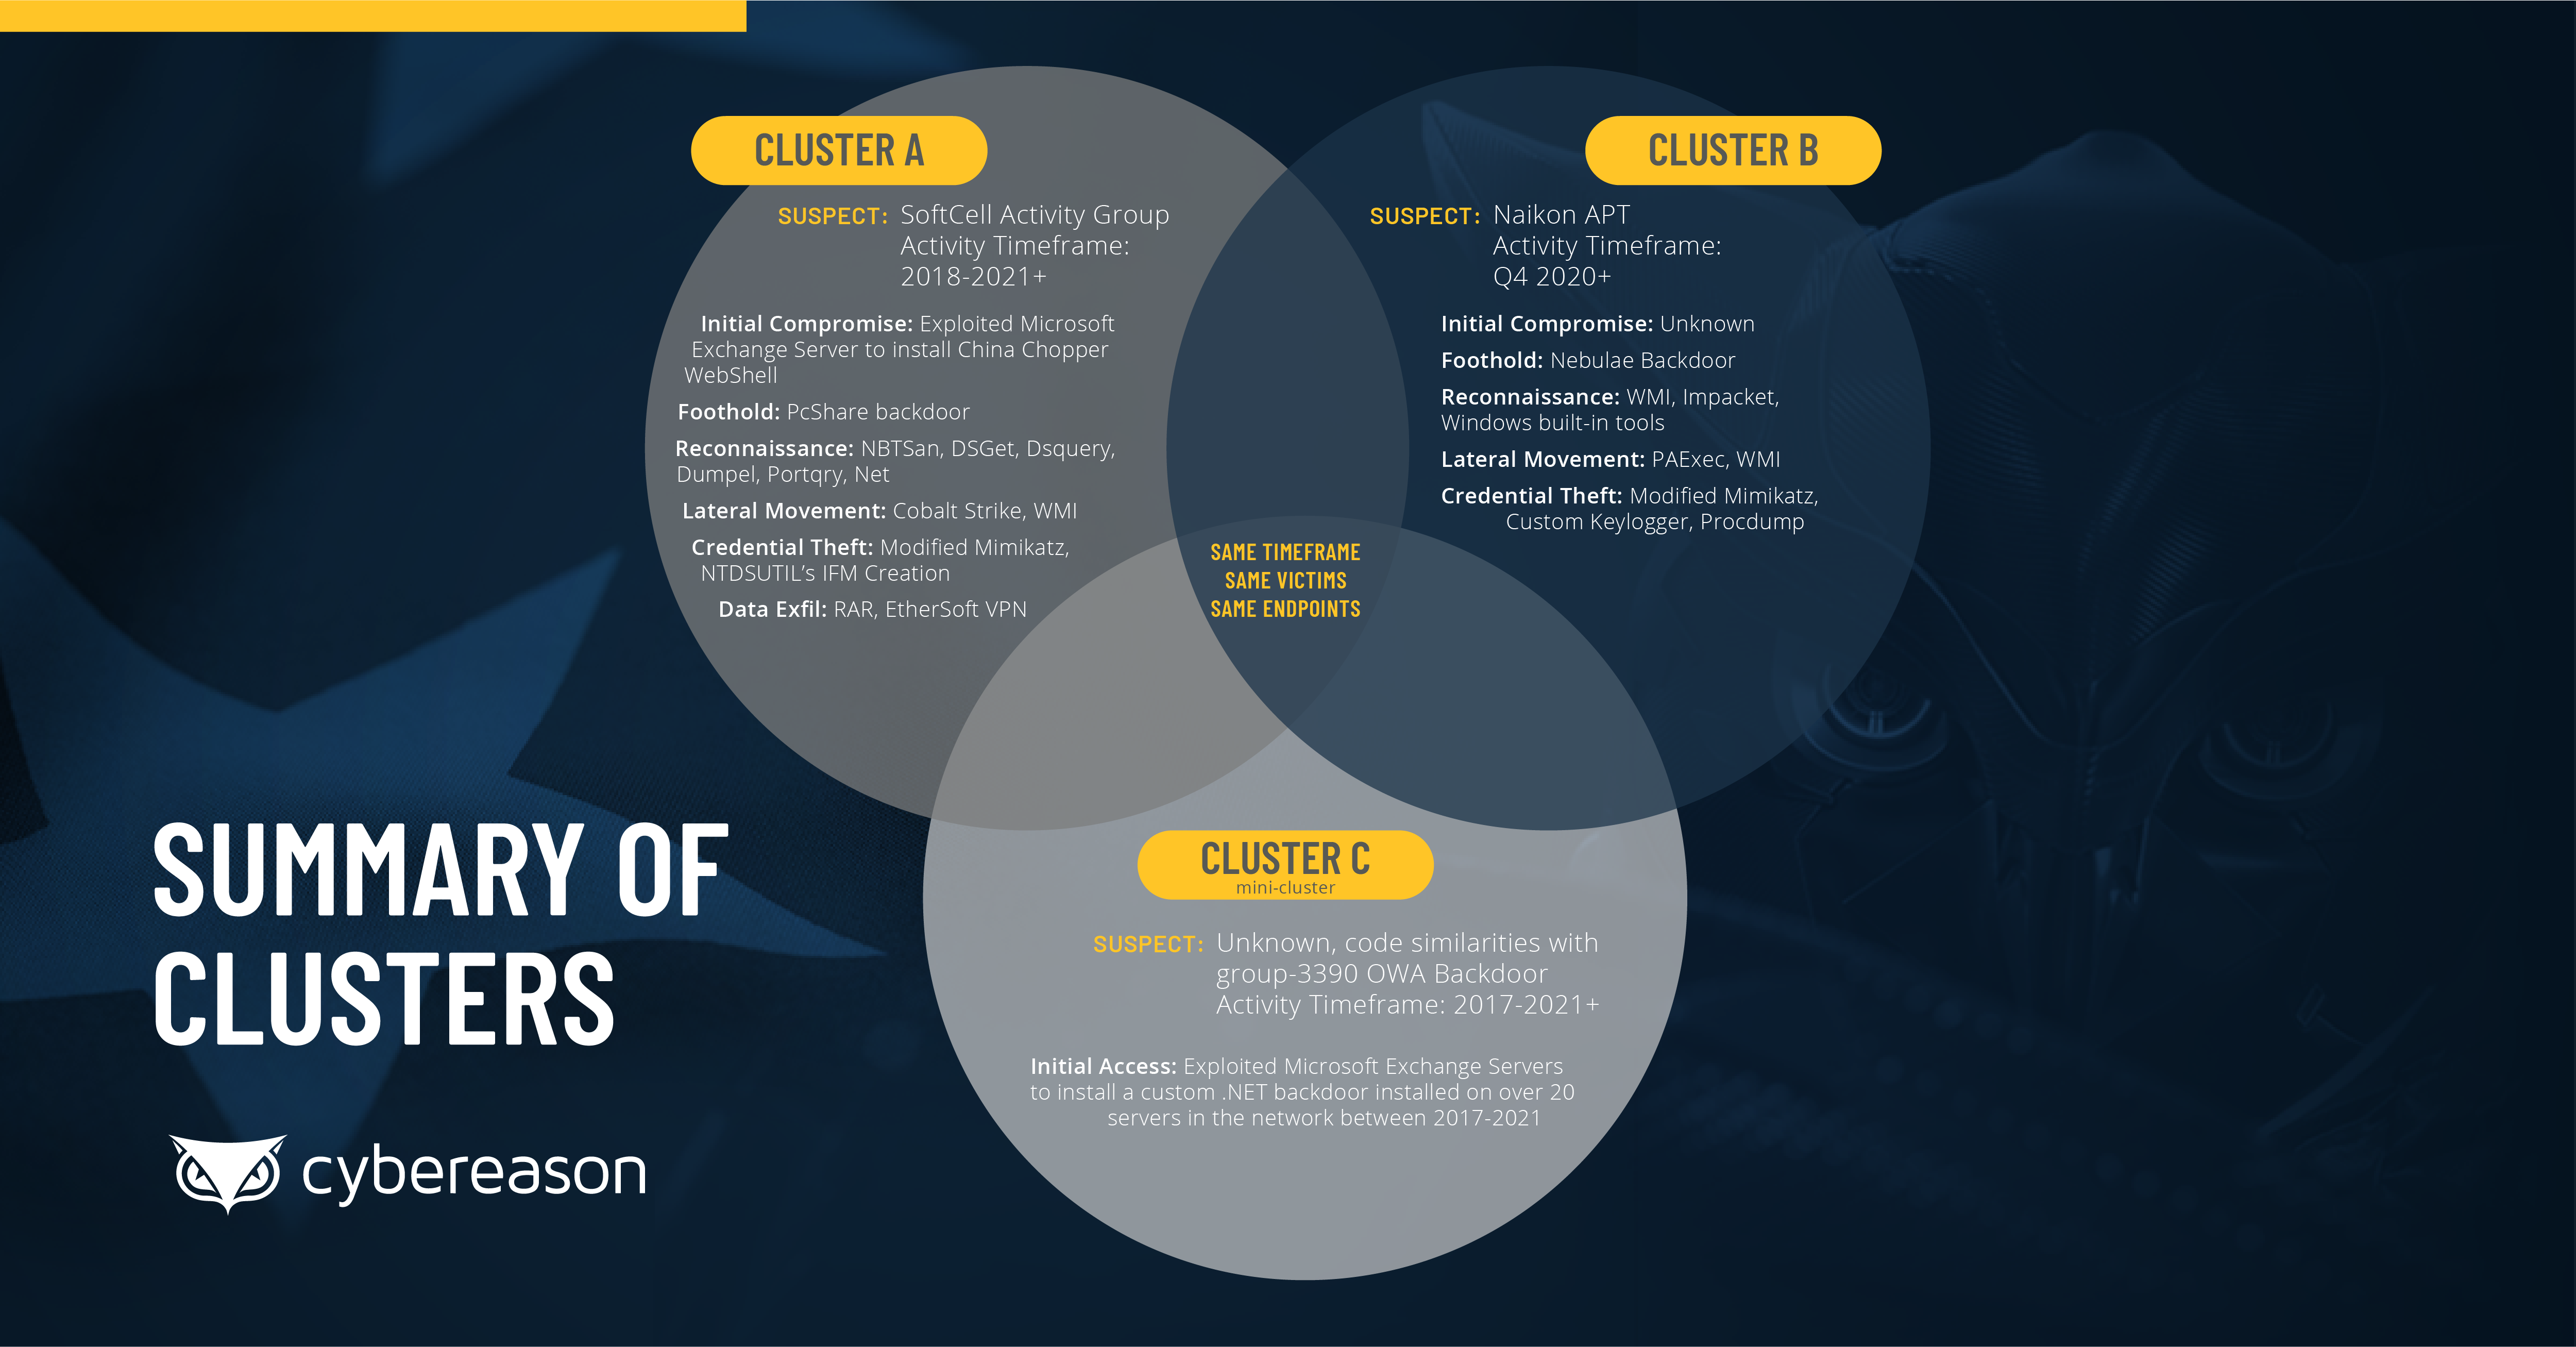
China linked APT groups have targeted networks of at least five major telecommunications companies operating in Southeast Asia since 2017. Cybereason researchers identified three clusters of activity associated with China-linked threat actors that carried out a series of attacks against networks of at least five major telecommunications companies located in South Asia since 2017. “The goal […]
 Pierluigi Paganini
August 03, 2021
A flaw in the GitHub Actions workflow for PyPI ’s source repository could be exploited to potentially execute arbitrary code on pypi.org. Security researcher RyotaK disclosed three flaws in PyPI, the most severe one could potentially lead to the compromise of the entire PyPI infrastructure. Python Package Index (PyPI) is the official third-party software repository […]






