 Pierluigi Paganini
 February 20, 2025
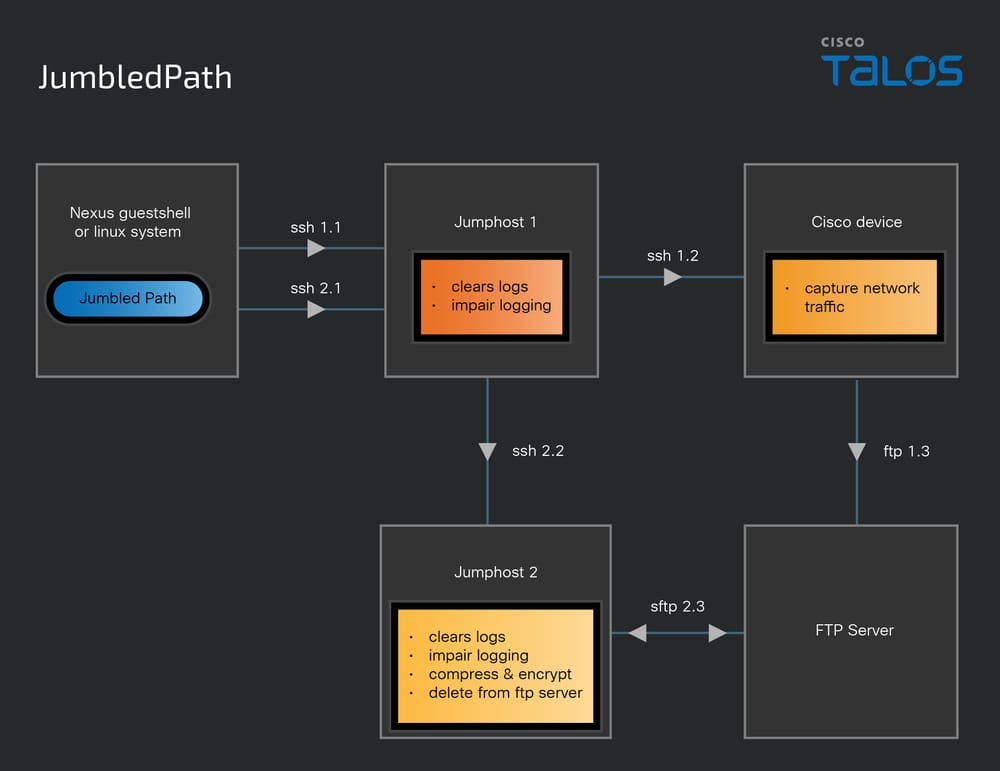
China-linked cyber espionage group Salt Typhoon uses custom malware JumbledPath to on spy U.S. telecom providers. Cisco Talos researchers reported that China-linked APT group Salt Typhoon uses a custom-built utility, dubbed JumbledPath, to spy on network traffic of U.S. telecommunication providers. China-linked APT group Salt Typhoon (also known as FamousSparrow and GhostEmperor) and has been active since at least 2019 and […]
 Pierluigi Paganini
February 18, 2025
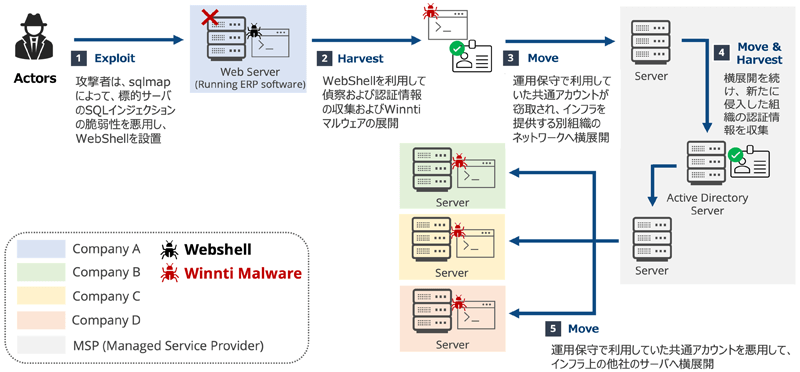
China-linked threat actor Winnti targeted Japanese companies in the manufacturing, materials, and energy sectors in March 2024 as part of a campaign dubbed RevivalStone. Researchers from cybersecurity firm LAC uncovered a new cyberespionage campaign, tracked as RevivalStone, carried out by the China-linked APT group Winnti in March 2024. Threat actors targeted Japanese companies in the manufacturing, […]
 Pierluigi Paganini
February 16, 2025
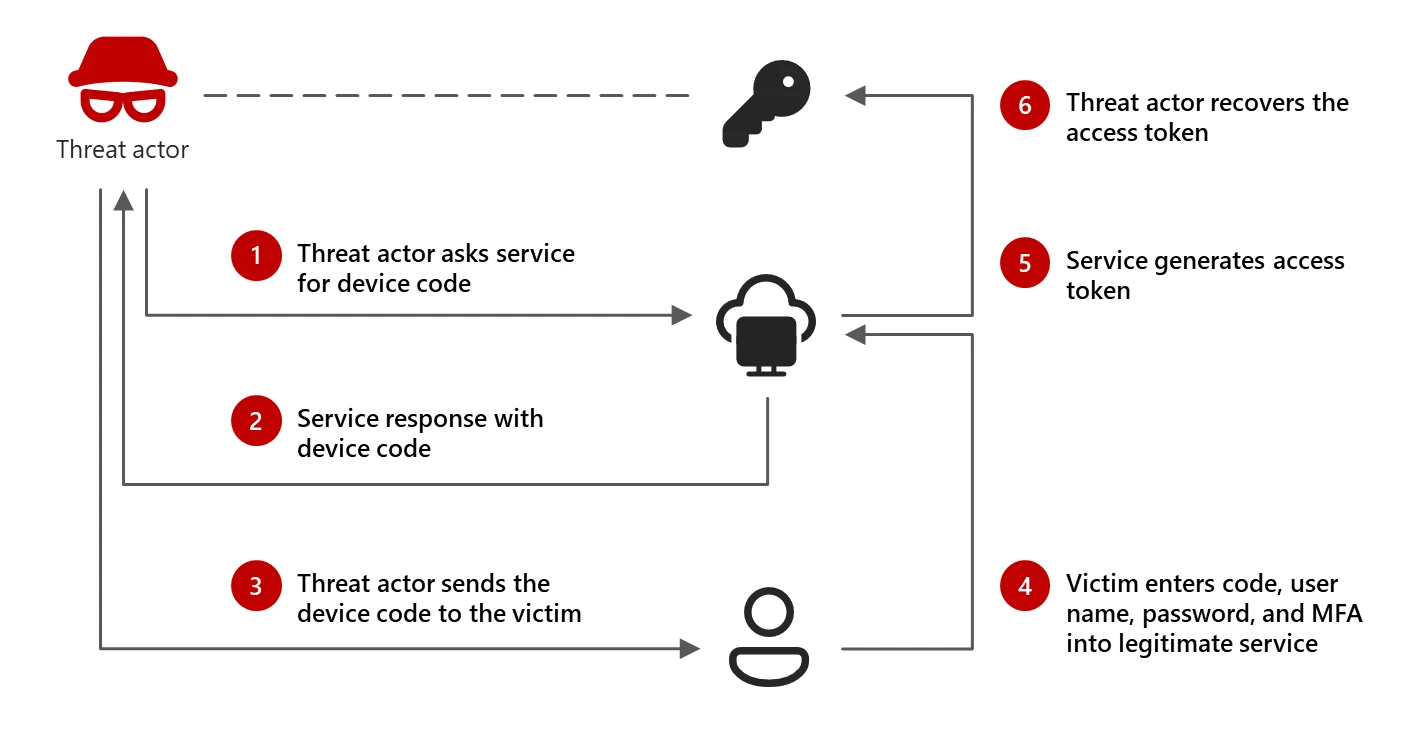
Russia-linked group Storm-2372 used the device code phishing technique since Aug 2024 to steal login tokens from governments, NGOs, and industries. Microsoft Threat Intelligence researchers warn that threat actor Storm-2372, likely linked to Russia, has been targeting governments, NGOs, and various industries across multiple regions since August 2024. The attackers employ a phishing technique called […]
 Pierluigi Paganini
February 16, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape. Mobile Indian Cyber Heist: FatBoyPanel And His Massive Data Breach Google Tag Manager Skimmer Steals Credit Card Info From Magento Site From South America to Southeast Asia: The Fragile Web of REF7707 Analyzing DEEP#DRIVE: North Korean […]
 Pierluigi Paganini
February 14, 2025
China-linked APT Salt Typhoon has breached more U.S. telecommunications providers via unpatched Cisco IOS XE network devices. China-linked APT group Salt Typhoon is still targeting telecommunications providers worldwide, and according to a new report published by Recorded Future’s Insikt Group, the threat actors has breached more U.S. telecommunications providers by exploiting unpatched Cisco IOS XE […]
 Pierluigi Paganini
February 13, 2025
Researchers at cybersecurity firm Resecurity detected a rise in cyberattacks targeting UAV and counter-UAV technologies. Resecurity identified an increase in malicious cyber activity targeting UAV and counter-UAV (C-UAV/C-UAS) technologies. That was especially notable during active periods of local conflicts, including the escalation of the Russia-Ukraine war and the Israel-Hamas confrontation. The trend of malicious targeting […]
 Pierluigi Paganini
February 12, 2025
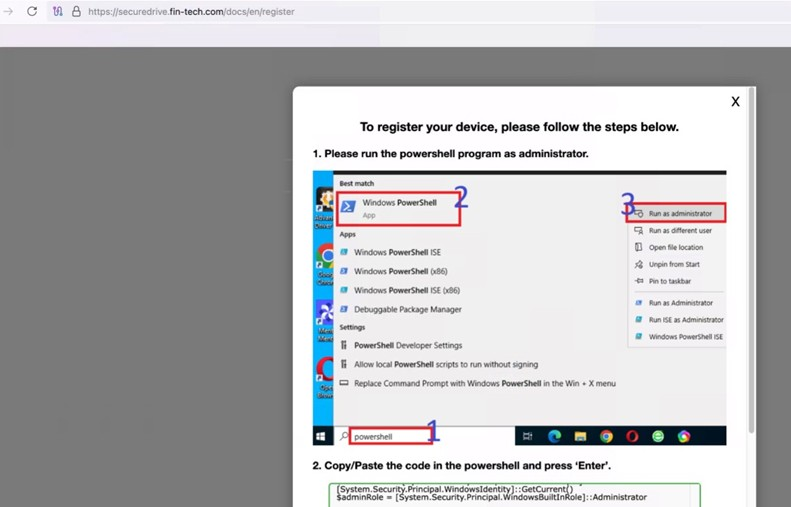
Microsoft Threat Intelligence has observed North Korea-linked APT Emerald Sleet using a new tactic, tricking targets into running PowerShell. Microsoft Threat Intelligence researchers spotted North Korea-linked threat actor Emerald Sleet (also known as Kimsuky and VELVET CHOLLIMA) using a new tactic. They are tricking targets into running PowerShell as an administrator and executing code provided […]
 Pierluigi Paganini
February 10, 2025
UK secretly demands Apple create an iCloud backdoor via a Technical Capability Notice, raising privacy concerns over end-to-end encryption. The UK demands Apple to create a backdoor to access any iCloud backups, the request raises concerns about user privacy and undermines Apple’s security commitments. “The British government’s undisclosed order, issued last month, requires blanket capability […]
 Pierluigi Paganini
February 08, 2025
Researchers spotted North Korea’s Kimsuky APT group launching spear-phishing attacks to deliver forceCopy info-stealer malware. Researchers from AhnLab Security Intelligence Center (ASEC) observed North Korea’s Kimsuky APT group conducting spear-phishing attacks to deliver forceCopy info-stealer malware. Kimsuky cyberespionage group (aka ARCHIPELAGO, Black Banshee, Thallium, Velvet Chollima, APT43) was first spotted by Kaspersky researchers in 2013. The group works under the control […]
 Pierluigi Paganini
February 08, 2025
Russia’s intelligence recruits Ukrainians for terror attacks via messaging apps and forums, offering quick pay, Ukraine’s law enforcement warns. According to Ukraine’s law enforcement, Russian intelligence is using messaging apps and forums to recruit Ukrainians for terrorist attacks, offering quick pay. Ukrainian authorities have recently seen a rise in terrorist attacks on police, military centers, […]
Data Breach / October 20, 2026