


 Pierluigi Paganini
 September 20, 2026
An AI-generated intelligence report falsely identified weapons on a Chinese ship, nearly triggering a US military operation during the Iran war. According to CNN, four sources familiar with the episode say an intelligence report circulated through the military claiming a Chinese vessel in the Middle East was carrying components for a nuclear weapons program. The […]
 Pierluigi Paganini
September 17, 2026
Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia. Hunt.io and researcher Guy Yasur have traced a tight cluster of SpiceRAT command‑and‑control servers that predate and extend Bitdefender’s August 2026 SilkParasite report. The work doesn’t dissect malware samples; it maps the network side of the […]
 Pierluigi Paganini
September 17, 2026
UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram. The UK, the US, and the Netherlands published a joint advisory warning about a Windows malware family, dubbed Chosen Brick, that Iran’s intelligence services use to track down dissidents, journalists, and activists, and the […]
 Pierluigi Paganini
September 10, 2026
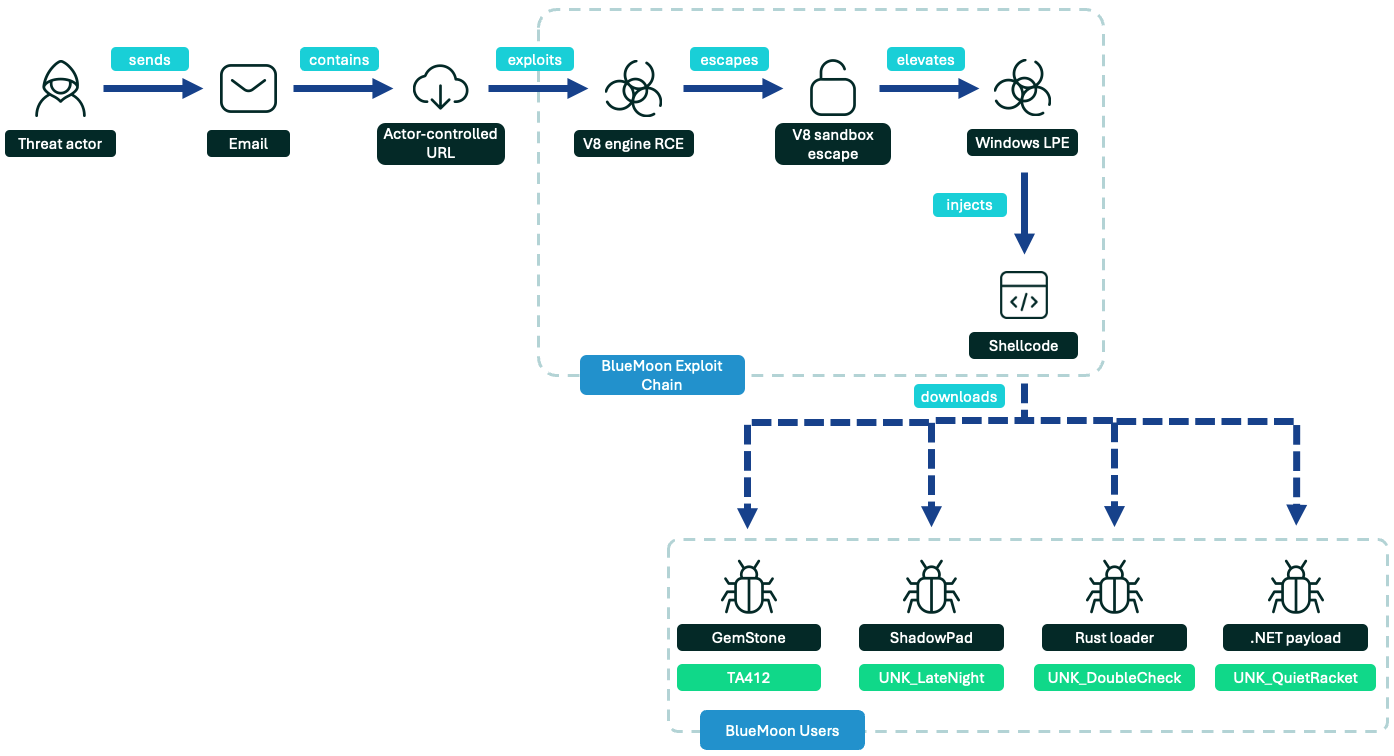
Four espionage groups used the BlueMoon Chrome+Windows exploit kit within 12 days. Researchers suspect AI development. Proofpoint published a detailed analysis of a Chrome-and-Windows exploit kit it tracks as BlueMoon that four nation-state actors adopted within roughly two weeks of the first observed use. Google’s Threat Intelligence Group, Microsoft’s MSTIC, and Volexity all contributed to […]
 Pierluigi Paganini
September 03, 2026
Serbian activists were targeted with zero-click Pegasus and NoviSpy spyware, exposing a major surveillance campaign ahead of elections. A member of Serbia’s student protest movement had their iPhone infected with NSO Group‘s Pegasus spyware without ever clicking a link or opening a file. The Citizen Lab confirmed the infection in collaboration with the SHARE Foundation, […]
 Pierluigi Paganini
September 03, 2026
2,000 leaked files expose Bauman University’s hidden Department No. 4, which trained GRU-linked hackers and propagandists linked to APT28 and Sandworm. Leaked Documents Expose Bauman University’s Hidden Department That Trained Hackers, Propagandists, and Malware Developers for the GRU More than 2,000 internal documents from Bauman Moscow State Technical University have been reviewed by an international […]
 Pierluigi Paganini
September 02, 2026
Mirage Kitten used fake LinkedIn coding tests to spread NodeRabbit and PollCat, even banning AI tools that could have spotted the malware. Iran-linked Mirage Kitten hackers just found a genuinely clever way to make their own malware harder to detect: telling job candidates not to use AI tools while reviewing the trojanized code they were […]
 Pierluigi Paganini
September 01, 2026
Huntress found five DPRK-linked workers hired in 2026 using fake identities, remote-access setups and proxy tools to infiltrate legitimate companies. Companies keep accidentally hiring North Korea-linked individuals as remote workers, and Huntress just published the receipts. The security firm’s investigation documents five confirmed cases in 2026 alone where DPRK-aligned workers, tracked under the name FAMOUS […]
 Pierluigi Paganini
August 31, 2026
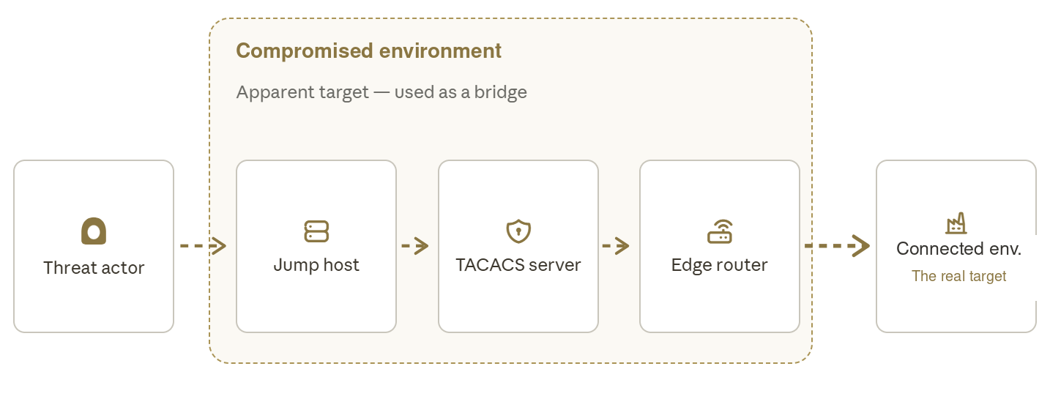
Fire Ant hijacked Cisco routers, stole credentials and altered logs to hide its tracks, using trusted infrastructure to reach high-value networks. Chinese-linked cyber espionage group Fire Ant has spent the past year quietly graduating from hacking individual computers to hacking the infrastructure that connects them. Sygnia’s new report traces how the group expanded from compromising […]
 Pierluigi Paganini
August 29, 2026
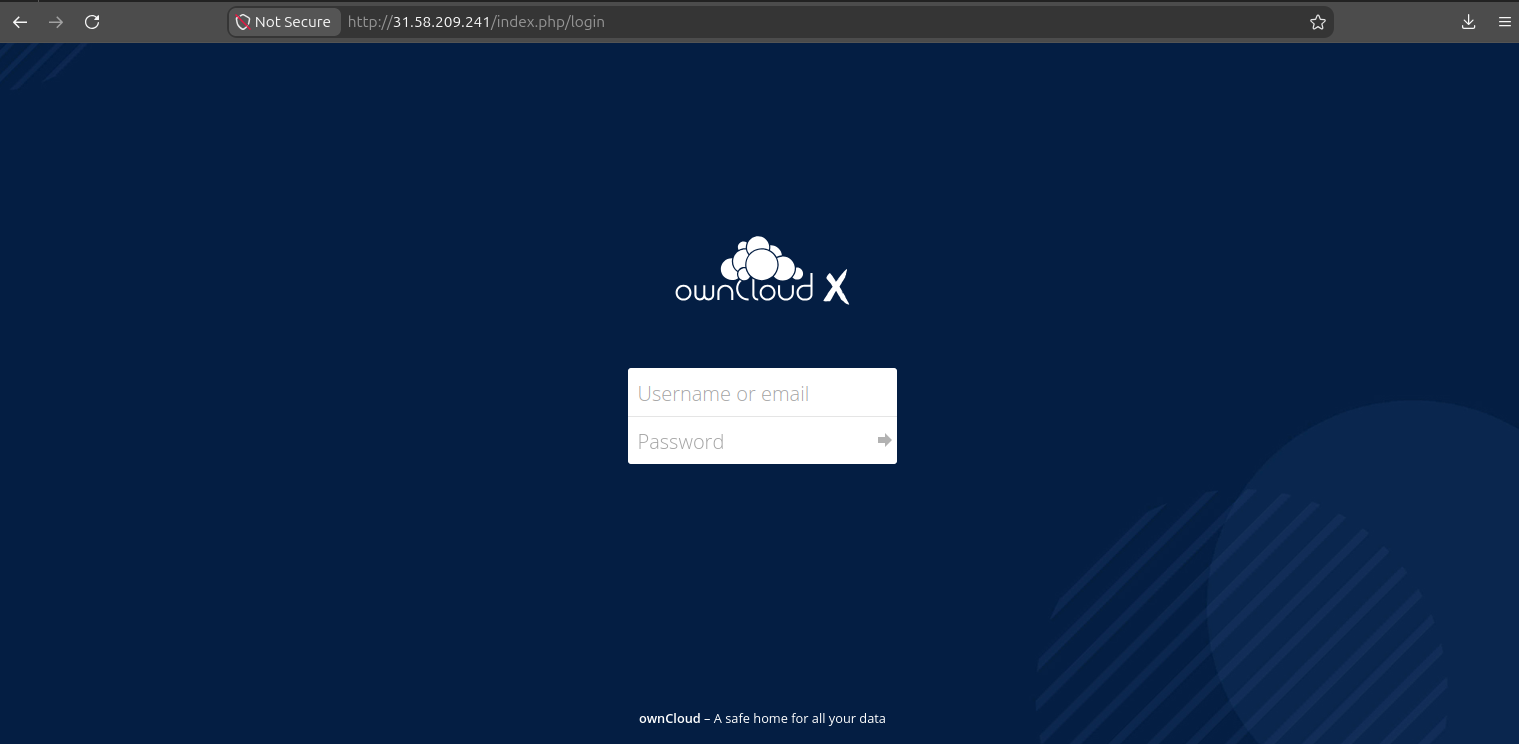
An alleged Chinese-speaking actor breached Philippine nuclear and naval targets by exploiting known flaws, stealing sensitive data. A suspected Chinese-speaking operator targeted a Philippine nuclear research body and a marine engineering company that supports the Philippine Navy, using well-known vulnerabilities in internet-facing ownCloud and WordPress systems. The activity was uncovered after Hunt.io found an exposed […]



Artificial Intelligence / September 19, 2026

