


 Pierluigi Paganini
 August 28, 2026
BlueDelta (APT28) uses webhook.site and Microsoft Edge to hide HOOKEDGE espionage traffic targeting European governments. Recorded Future’s Insikt Group documented a campaign by BlueDelta, the Russian GRU-linked group that overlaps with the group APT28, running an entire espionage operation against European government targets using webhook.site, a service built for developers to test HTTP requests, as […]
 Pierluigi Paganini
August 27, 2026
OpenAI banned Russian ChatGPT accounts backing a fake think tank, IBI, that used AI posts and a fake “sovereignty” index to push pro‑Russia narratives. OpenAI says it has banned a cluster of ChatGPT accounts that likely originated in Russia and were used to support a covert influence operation. The campaign promoted an organisation called the […]
 Pierluigi Paganini
August 21, 2026
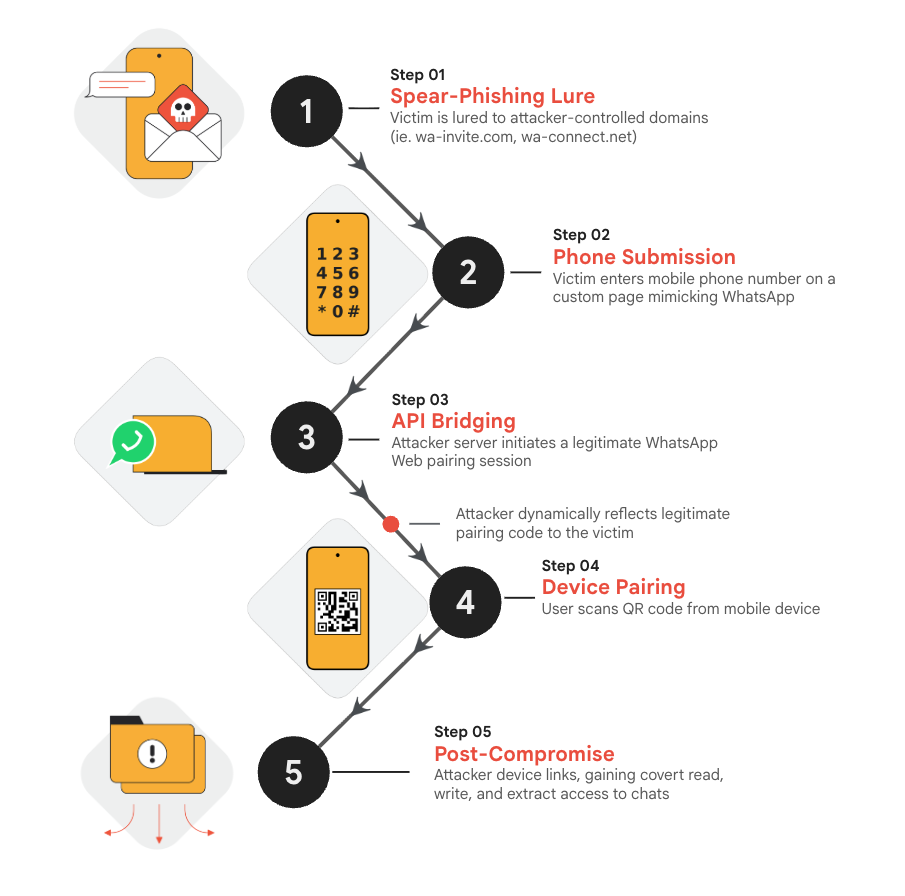
Google tracks three Russia-linked espionage clusters using phishing and legitimate authentication tools to target researchers, diplomats and defense staff. Google’s Threat Intelligence Group tracked three separate suspected Russia-linked cyber espionage clusters. All three focus on the same thing: abusing authentication features that are supposed to protect accounts to access them instead. Threat actors target researchers, […]
 Pierluigi Paganini
August 20, 2026
The US charged 17 Iranians over a years-long hacking campaign that stole 31TB from universities, companies and government agencies worldwide. Eight years after the original indictment first went public, US prosecutors just added eight more names to the list. The Justice Department unsealed a superseding indictment this week charging 17 members of the Mabna Institute, […]
 Pierluigi Paganini
August 19, 2026
An exposed operator directory reveals how one actor compromised 14,000+ Dahua cameras across Ukraine and Russia, no password needed for most. A researcher discovered an exposed directory containing the tools of an attacker who compromised more than 14,000 Dahua cameras between June 17 and July 22, 2026, mainly in Ukraine and Russia. Hunt.io reconstructed the […]
 Pierluigi Paganini
August 16, 2026
Mustang Panda upgraded CoolClient with a signed kernel driver that hides processes, files and network activity, making the backdoor harder to detect. HoneyMyte, also known as Mustang Panda, has pushed its CoolClient backdoor another step deeper into Windows. Kaspersky’s latest analysis shows a new variant that can deploy a signed kernel-mode driver as a Windows […]
 Pierluigi Paganini
August 16, 2026
Acronis uncovered PATCHCORD, a stealthy backdoor targeting Afghan telecom and South Asian infrastructure via fake VPN tools and Google Sheets C2. Researchers at Acronis just documented an espionage operation that reads like it was built by someone with genuinely good taste in disguises. Their Threat Research Unit report tracks a previously undocumented backdoor called PATCHCORD, […]
 Pierluigi Paganini
August 12, 2026
China-linked hackers reportedly used eight AI agents to breach a government network, steal data and compromise accounts with minimal human oversight. Israeli cybersecurity firm Dream documented what looks like the first fully autonomous, end-to-end AI hacking operation against a government target. Over four days at the start of July, according to the Financial Times, suspected […]
 Pierluigi Paganini
August 08, 2026
China opened a cybersecurity review of Palo Alto Networks, citing national security concerns but giving no details about the reasons behind the probe. China’s Cyberspace Administration (CAC) announced that it’s launching a cybersecurity review of products Palo Alto Networks sells in the country. The announcement itself runs to a few sentences of formal Chinese, citing […]
 Pierluigi Paganini
August 01, 2026
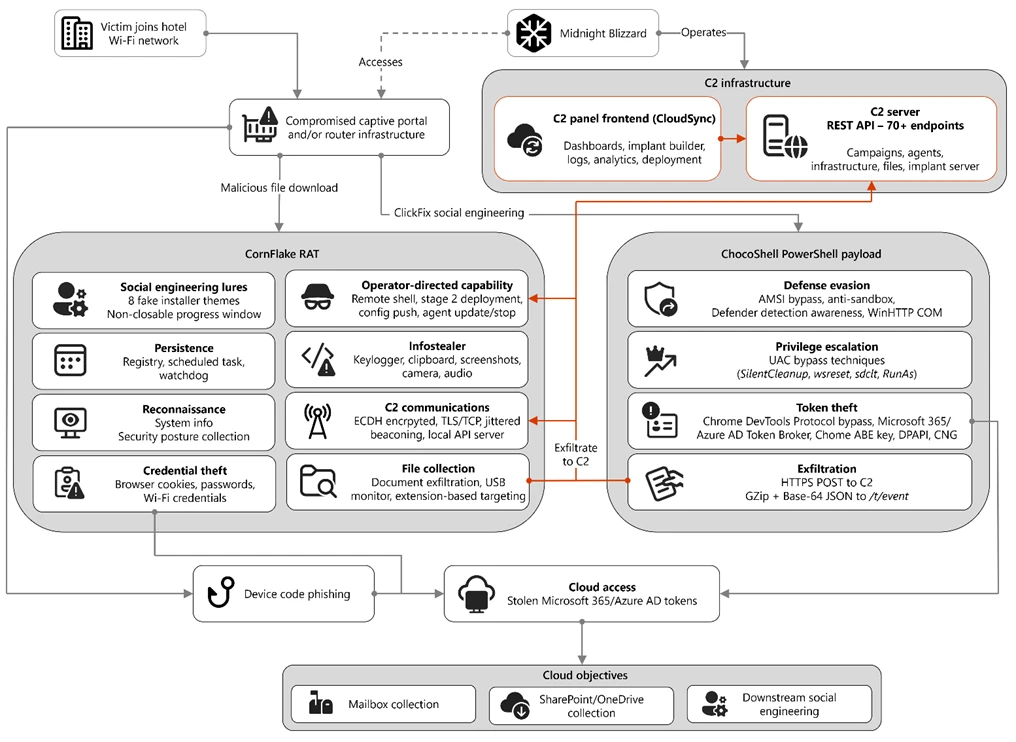
Microsoft says Russian hackers hijacked hotel Wi-Fi portals to spread malware and steal Microsoft 365 tokens from travelers. Microsoft Threat Intelligence disclosed CaptiveCrunch, a campaign it attributes to Storm-2945, an operational sub-cluster of Midnight Blizzard, the Russian SVR-linked group also known as APT29 and Cozy Bear. Since early May 2026, Storm-2945 has been manipulating DNS […]



Artificial Intelligence / September 19, 2026

