19322 results
 Pierluigi Paganini
 January 14, 2015
GE MultiLink managed switches are affected by two vulnerabilities which could be exploited to gain unauthorized access and run DoS attacks on the device. Managed Ethernet switches produced by GE include the hard-coded private SSL key in a number of network devices. The Ethernet switches that present the security hole are designed for use in industrial […]
 Pierluigi Paganini
January 14, 2015
Dell SecureWorks detected the Skeleton Key malware, which modifies authentication process on Active Directory (AD) systems protected by only passwords. The experts at Dell SecureWorks Counter Threat Unit(TM) (CTU) have recently discovered a malware dubbed Skeleton Key that bypasses single-factor authentication on Active Directory (AD) systems. The attackers can use to have total access to remote […]
 Pierluigi Paganini
January 14, 2015
Google is not able to direct control the distribution of bug patches for its devices, and 60 percent of Android phones is exposed to security risks. The security expert Todd Bearsley published an interesting blog post on Rapid7 Security Street blog explaining that the Metasploit framework currently includes 11 different exploits for WebView. “WebView is the core component […]
 Pierluigi Paganini
January 14, 2015
Google Project Zero team disclosed a new unpatched vulnerability affecting Windows 8.1 systems unleashing the wrath of Microsoft for its disclosure policy. Google’s Project Zero hacking team has disclosed the details of a new unpatched Windows 8.1 Privilege Escalation vulnerability in Microsoft Windows 8.1 OS. It is the second flaw in Windows 8.1 OS publicly disclosed by […]
 Pierluigi Paganini
January 13, 2015
Security researcher Samy Kamkar has designed a USB wall charger dubbed KeySweeper, which secretly logs keystrokes from Microsoft wireless keyboards nearby. Security researcher Samy Kamkar has designed a cheap USB wall charger that can eavesdrop on almost any Microsoft wireless keyboard. The stealthy Arduino-based device, dubbed “KeySweeper“, works like a generic USB mobile charger, but he has the capability […]
 Pierluigi Paganini
January 13, 2015
Prime Minister Cameron said that the UK would pursue banning encrypted messaging apps if the Intelligence was not given access to the communications. At this historical moment, governments are facing increasingly dangerous cyber threats, but their activities are hampered by the large diffusion of encryption mechanisms. Following the Snowden‘s revelations, several IT firms like Google and Apple are […]
 Pierluigi Paganini
January 13, 2015
New York Times have managed to lead to the declassification of a report, highlighting the participation of the FBI to a warrantless surveillance program terminated in 2012. Links to the Prism surveillance program and leaks from Edward J Snowden point at the FBI being actively present in breaches of privacy. FBI has been linked to […]
 Pierluigi Paganini
January 13, 2015
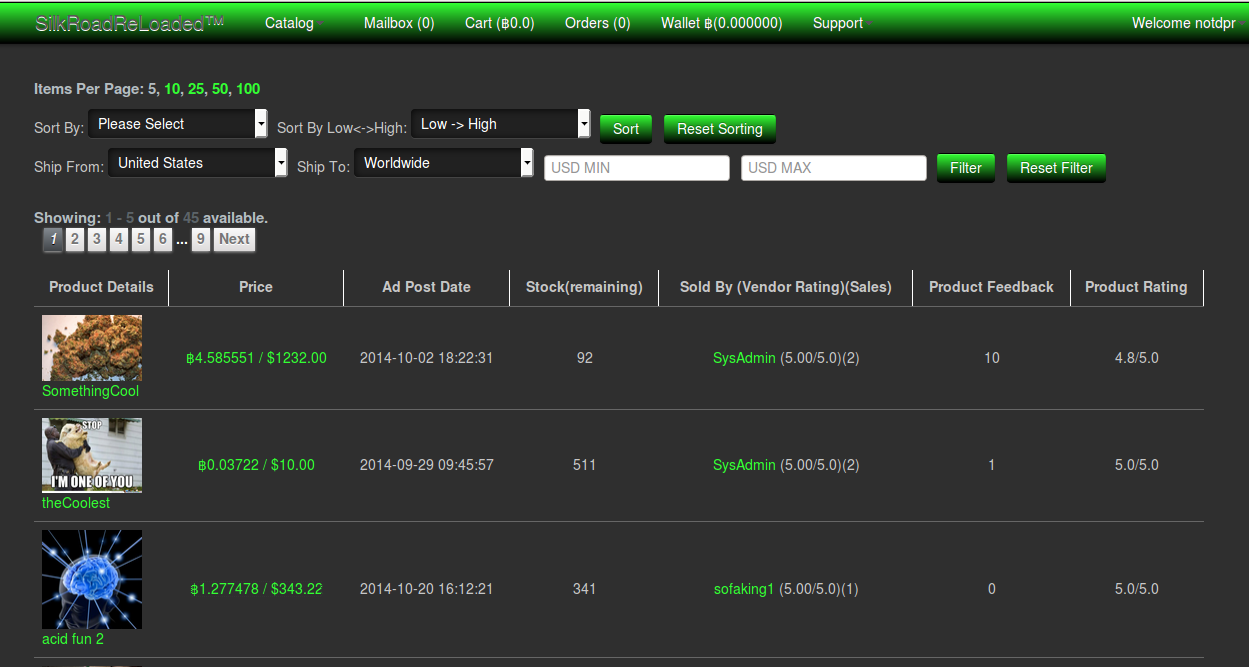
The newborn Silk Road Reloaded black marketplace adopts I2P Anonymous Network and different virtual currency scheme to protect illegal business. The Operation Onymous conducted by law enforcement allowed the seizure of dozens of black markets on Tor Networks. While all the underground marketplaces in the DeepWeb, including Silk Road 2.0, went down due to the operation of […]
 Pierluigi Paganini
January 12, 2015
ISIS supporters have hacked the YouTube and Twitter accounts belonging to the US CENTCOM leaking online internal documents stolen from mobile devices. While Anonymous started the #OpCharlieHebdo campaign against jihadist websites to avenge the attack against the Charlie Hebdo, hackers of the CyberCaliphate group, claiming to support the terrorist group ISIS, have compromised the official […]
 Pierluigi Paganini
January 12, 2015
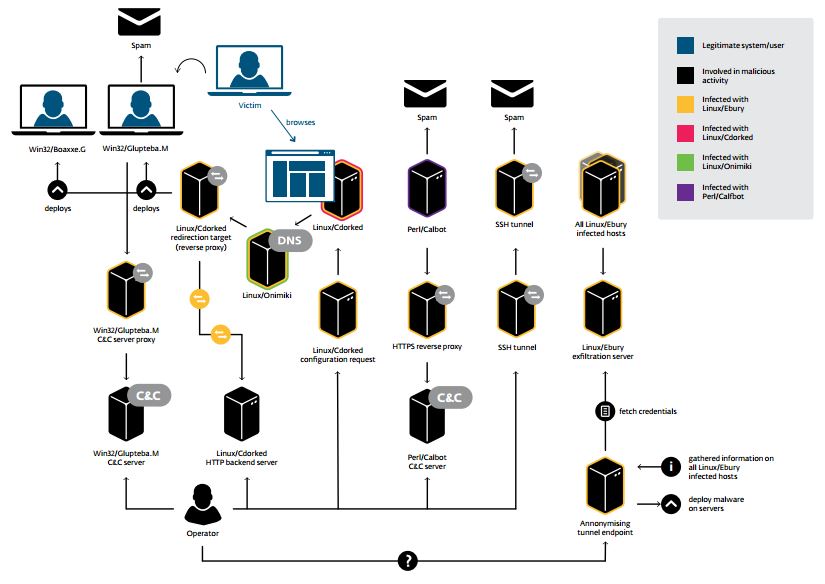
Security Experts at ESET firm discovered that Windigo campaign is still active and that bad actors are changing their tactics to remain under the radar. Windigo is a sophisticated malware-based campaign uncovered by security Experts at ESET in March 2014, hackers behind the campaign that exploited the Linux/Ebury backdoor compromising more than 500,000 computers and 25,000 dedicated servers. The […]