19313 results
 Pierluigi Paganini
 December 17, 2013
During a CBS Interview show “60 Minutes”, The NSA Director General Alexander and the Information Assurance Director Plunkett claimed a foreign government has developed a BIOS based malware that can remotely destroy any computer. Senior National Security Agency (NSA) officials have revealed to CBS American television newsmagazine “60 Minutes” that a foreign government has tried […]
 Pierluigi Paganini
December 16, 2013
KrebsOnSecurity has discovered an unusual botnet that disguises itself as a legitimate add-on for Mozilla Firefox to perform website vulnerability scanning. Krebson security blog posted an interesting article on a new concerning botnet infected more than 12,500 systems disguises itself as a legitimate add-on for Mozilla Firefox to hack websites on a large scale. The botnet, […]
 Pierluigi Paganini
December 16, 2013
Interview with the security experts Andrey Komarov and Dan Clements of IntelCrawler to analyze significant evolutions in the cyber-threat landscape. Today I desire to propose an interview with Andrey Komarov, CEO of IntelCrawler and Dan Clements, President of IntelCrawler. IntelCrawler is a multi-tier intelligence aggregator, which gathers information and cyber prints from a starting big […]
 Pierluigi Paganini
December 16, 2013
Incapula security firm published a new report on the analysis of website traffic evidencing the increment for malicious activities. Researchers at the Incapsula security firm have published a new study on the nature of website traffic, early 2013 the company revealed that 51% of the overall traffic was generated by non-human entities and 60% of […]
 Pierluigi Paganini
December 15, 2013
Researchers at Kaspersky Lab discovered Apple Safari browser stores previous secure session data unencrypted in a hidden folder. Apple’s Safari browser stores session information including authentication credentials used in previous HTTPS sessions to implement the feature “Reopen All Windows from Last Session”. Safari stores in a plain text XML file called Property list, or plist, […]
 Pierluigi Paganini
December 15, 2013
Do users know that Facebook analyzes everything they type and not publish (self-censorship content)? Why Facebook does not consider it a privacy violation? Recent revelations on the NSA surveillance programs have raised many questions in user’s mind on the real roles of companies such as Facebook and Google, how do they manage users’ data and […]
 Pierluigi Paganini
December 14, 2013
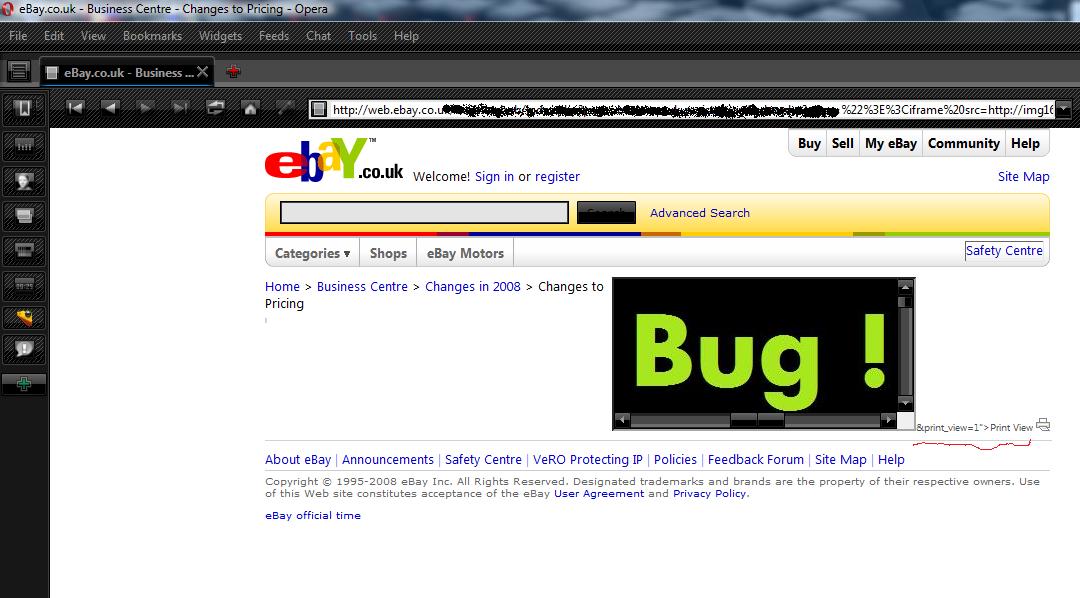
The German security researcher David Vieira-Kurz discovered a critical vulnerability in the Ebay website that allows an attacker a remote code execution. The German security researcher David Vieira-Kurz discovered a critical vulnerability in the official Ebay website in particular in its sub domain http://sea.ebay.com that allows an attacker a remote code execution. It’s not the first time […]
 Pierluigi Paganini
December 14, 2013
Experts at Hacker Online Club published a post on Google vulnerabilities that are currently not under bug bounty program of the company. Today I desire to propose the information on Un-patched Google Vulnerabilities published on the web site Hackers Online Club trying to understand a hacker how could exploit them. The first Google Vulnerability is a […]
 Pierluigi Paganini
December 13, 2013
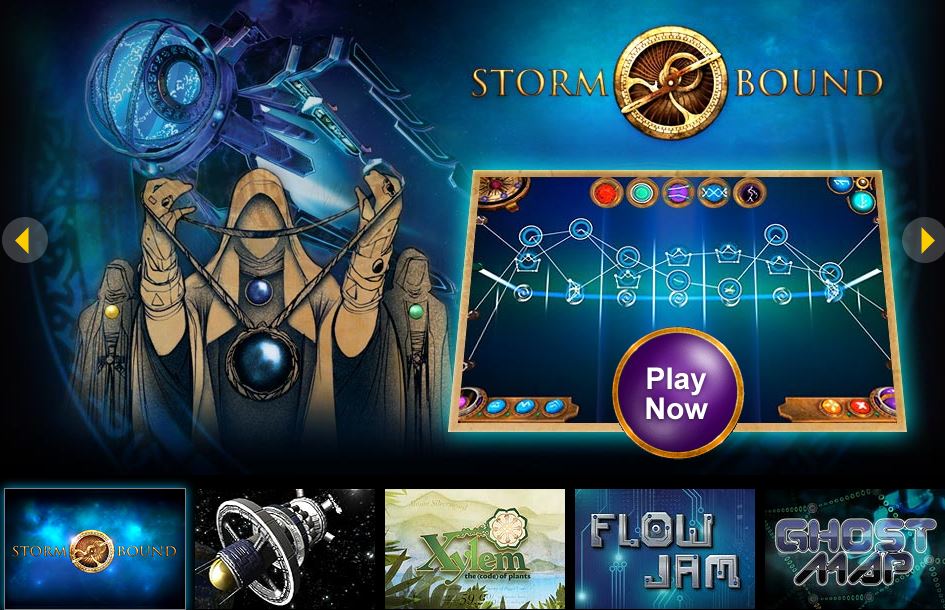
DARPA has launched the Crowd Sourced Formal Verification, it creates a set of games that search for software vulnerabilities involving volunteer gamers. The US Department of Defense Is evaluating the use of video games for finding software vulnerabilities with the collaboration of a network of volunteers. The idea is revolutionary, the support offered to DoD […]
 Pierluigi Paganini
December 12, 2013
ENISA releases the ENISA Threat Landscape 2013, it a collection of information on top cyber-threats that have been assessed in the reporting period. The European Network and Information Security Agency (ENISA) published the ENISA Threat Landscape 2013 report, a document that was annually issued to analyze significant evolutions in the cyber-threat landscape. The ENISA has […]