19313 results

 Pierluigi Paganini
 June 23, 2013
Operation Tempora, is the name of GCHQ program to tap fibre-optic cables for secret access to communications. Operation Tempora, this is the name of last massive tapping program conducted by Britain’s Government Communications Headquarters (GCHQ) and revealed by The Guardian. Operation Tempora has been going on for at least 18 months, British intelligence adopted “intercept probes” […]
 Pierluigi Paganini
June 22, 2013
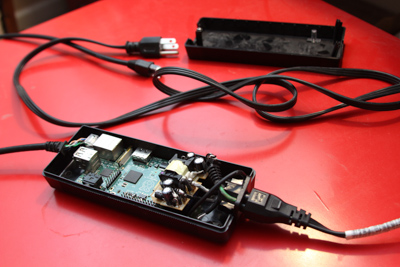
Network security engineer “Richee” explained how to use a Raspberry Pi to realize a physical backdoor to gain remote access to an office network. Network security engineer “Richee” published an interesting post on how to use a tiny Raspberry Pi computer to obtain physical access into a corporate network. I decided to publish this post because […]
 Pierluigi Paganini
June 21, 2013
US law enforcers suggest a kill switch for mobile devices to principal manufactures and Apple adapts. The idea of US law enforcers is the realization of a kill switch on mobile devices that would be used in case of theft. New York’s top prosecutor, State Attorney General Eric Schneiderman, and San Francisco District Attorney George Gascón promoted […]
 Pierluigi Paganini
June 20, 2013
Megaupload files have been deleted by Dutch hosting provider LeaseWeb, in the post a resume of the facts and fantastic hypothesis (maybe) on a strange case. Megaupload files have been deleted by LeaseWeb, a Dutch hosting provider, without notice, the news is shocking if we consider the wealth of information contained in the files. LeaseWeb is based […]
 Pierluigi Paganini
June 20, 2013
Researcher Egor Homakov demonstrated the possibility of Webcam hacking exploiting Chrome Inbuilt Flash player, a flaw that represents a serious threat to privacy. Webcam hacking, hackers are increasing their interest on millions of cams that surround us. These prying eyes are everywhere, in the street as in our home, gaming consoles, smartTV and PC are all equipped […]
 Pierluigi Paganini
June 19, 2013
Security firm Group-IB has discovered on an forum in the underground the sale for Carberp banking Trojan source code at $5K. Carberp banking Trojan is experiencing a new youth in the underground, in the last months investigation at security firm Group-IB have identified in an underground forum the resumption of sale for the malware. The version proposed […]
 Pierluigi Paganini
June 18, 2013
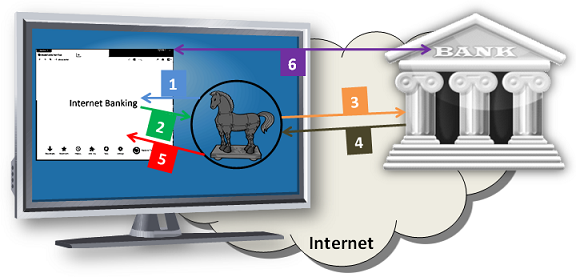
Security firm Trusteer detected a new variant of Zeus Trojan that steals funds and recruits Money Mules proposing jobs ads to the victims using Man-in-the-Browser (MitB) techniques. Zeus Trojan is becoming even more complex, its evolution is unpredictable due to the intense activity in the underground on its source code. Various forums in the underground offer customization […]
 Pierluigi Paganini
June 17, 2013
Palantir Technologies is considered the principal company behind the design of software used for PRISM program, think of it as the work of a single company is truly an understatement. Palantir Technologies, this is the most popular company name referred when discussing those who have supported the U.S. Government in the development of massive surveillance […]
 Pierluigi Paganini
June 16, 2013
RARSTONE is the name of the RAT (REMOTE ACCESS TOOL) used in a cyber espionage campaign dubbed “Naikon” uncovered by security experts at TrendMicro. Security experts at TrendMicro revealed to have detected the RARSTONE RAT studying targeted attacks across Asia (e.g. India, Malaysia, Singapore, and Vietnam) conducted against various companies belonging to different sectors such […]
 Pierluigi Paganini
June 15, 2013
Google revealed that tens of thousands of Gmail accounts belonging to Iranian users have been targeted by state-sponsored attacks. The Google company announced that tens of thousands of Gmail accounts of Iranian users have been targeted hacked. The attacks seem to be organized by a group of state sponsored hackers few days before presidential elections. The […]