


19312 results
 Pierluigi Paganini
 April 04, 2013
FireEye is one of most interesting security companies, thanks to its investigations many cases have been discovered in the last months, such as the attack to Bit9 companies and the abuse of its certificate to sign malicious code. The security firm has just published a new interesting report titled “2H 2012 Advanced Threat Report” reporting […]
 Pierluigi Paganini
April 03, 2013
It’s not a surprise South Korean security experts suggest that the North Korea military is training an elite force of “cyber warriors” to involve in cyber attacks against South institutions and companies. The South intelligence revelations follow continuous menaces of North Korea against U.S. Forces located in the Far East, the dictator Kim Jong-UN enhances […]
 Pierluigi Paganini
April 02, 2013
Researchers at Hacktive Security, an independent security consulting company, have demonstrated how much insidious could be a so a simple and crimeless large scale application. We are in the digital era, everything is connected to the large networks and applications benefit of even more complex devices that deeply interact with the owner, in this scenario […]
 Pierluigi Paganini
April 01, 2013
Webroot has recently published an interesting study, available here (registration required), on latest Web-borne threats and their economic impact providing also useful suggestions on how to implement an effective defense. The survey revealed a direct correlation between free access to web resources by employees of the companies and the level of exposure to cyber threats such as malware and phishing attacks. […]
 Pierluigi Paganini
March 31, 2013
Botnet author are increasing complexity of the malicious code they use and at the same time security firms are adopting more sophisticated detection methods. Between principal concerns of botmaster the need to improve the capabilities of bot agents to operate silently and necessity to masquerade traffic from bots and Command & Control servers. Focusing on this […]
 Pierluigi Paganini
March 29, 2013
The principal reports proposed by various security firm demonstrate a sustained growth of cyber criminal activities fueled by increased offer of underground. In the underground it is practically possible to acquire/sell any kind of product and services to realize illegal activities. The offer is complete and include programming and hacking services, bulletproof-hosting services, cyber attacks on […]
 Pierluigi Paganini
March 29, 2013
Not a day goes by that we’re talking about powerful cyber attacks and the sensational cyber espionage campaigns, the dangerous trend is also sustained by the increased offer of tools and services in the underground. Unfortunately the underground market is very dynamic and very difficult to monitor and to aggravate the situation is the leak […]
 Pierluigi Paganini
March 28, 2013
The news is circulating and this morning many colleagues called me to have more details on the event … what’s happening to the internet? All seems to be originated from a single DDoS attack against a unique company, but the event has reached unimaginable proportions with implications for the global network, in particular dragging down Internet […]
 Pierluigi Paganini
March 28, 2013
New age of POS malware – cash points are in the hackers’ interest, major US banks are compromised. UPDATE January 17th, 2014 I desire to reveal the identity of the person that has conducted the analysis on the BlackPos agent, giving me a significant support for the realization of the post. Andrey Komarov, IntelCrawler’s CEO, has arranged […]
 Pierluigi Paganini
March 27, 2013
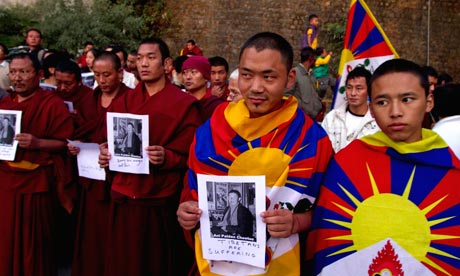
Read about APT attacks has become customary, even easier to hear of attacks against political dissidents or minorities as Tibetan and Uyghur activists, but never before has been exploited the Android platform for this type of offensive. In the past Tibetan minorities have been already targeted with malware able to infect Windows and Mac OSs, […]



Data Breach / November 17, 2026


