



 Pierluigi Paganini
 September 15, 2026
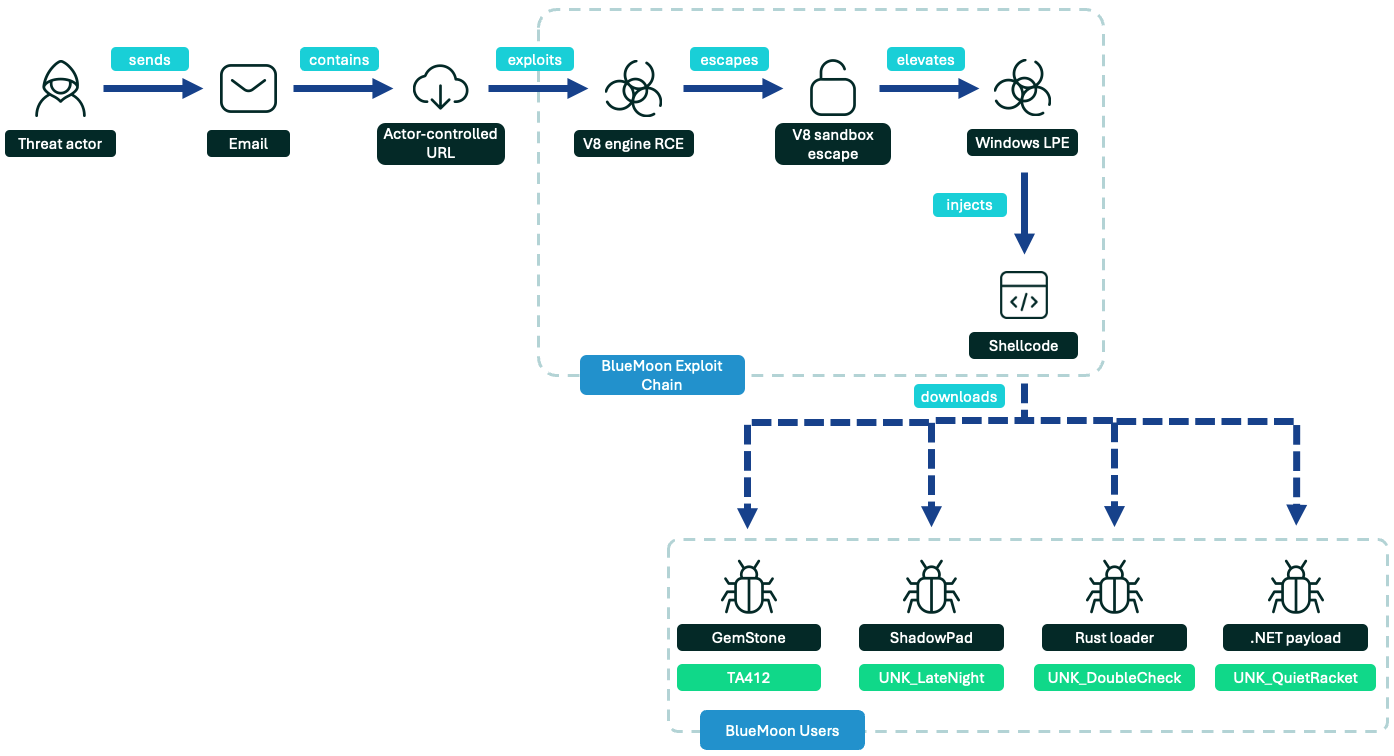
Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each. Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail. On September 1, Volexity detected a spear-phishing campaign by UTA0560 targeting several […]
 Pierluigi Paganini
September 10, 2026
Four espionage groups used the BlueMoon Chrome+Windows exploit kit within 12 days. Researchers suspect AI development. Proofpoint published a detailed analysis of a Chrome-and-Windows exploit kit it tracks as BlueMoon that four nation-state actors adopted within roughly two weeks of the first observed use. Google’s Threat Intelligence Group, Microsoft’s MSTIC, and Volexity all contributed to […]
 Pierluigi Paganini
September 09, 2026
Google patched 230 Chrome flaws, including an actively exploited V8 bug that could let attackers run arbitrary code through a crafted HTML page. Google released a Chrome update fixing 230 security vulnerabilities, including one already exploited in the wild tracked as CVE-2026-87491 (CVSS score of 8.8). The medium-severity flaw affects V8, Google’s open source high-performance […]
 Pierluigi Paganini
September 04, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Google Chromium V8 flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Google Chromium V8 flaw, tracked as CVE-2026-85046 (CVSS score of 8,8), to its Known Exploited Vulnerabilities (KEV) catalog. This week, Google released a Chrome security update fixing 12 […]
Pierluigi Paganini
September 04, 2026
Google patched 12 Chrome flaws, including an actively exploited V8 zero-day that could enable remote code execution through a crafted webpage. Google released a Chrome security update fixing 12 vulnerabilities, including CVE-2026-85046 (CVSS score of 8.8), an actively exploited V8 type confusion flaw. The bug affects Chrome’s JavaScript and WebAssembly engine and could let a […]
Pierluigi Paganini
July 31, 2026
Google says AI found and helped fix 1,072 Chrome security bugs in two releases, dramatically accelerating vulnerability detection and patching Google’s Chrome Security team published a detailed account of how AI models have transformed their vulnerability management pipeline, and the headline figure is difficult to dismiss: in the last two Chrome releases alone, the team […]
 Pierluigi Paganini
July 22, 2026
Adobe patched CVE-2026-48294, a flaw in Adobe Acrobat Chrome extension that could let attackers steal WhatsApp Web chats by luring users to a webpage. Guardio Labs researcher Shaked Biner disclosed HermeticReader, a vulnerability chain in the Adobe Acrobat Chrome extension that allowed any attacker-controlled webpage to silently steal a visitor’s WhatsApp chats, contacts, profile name, […]
Pierluigi Paganini
June 09, 2026
Google fixed a new Chrome zero-day, tracked as CVE-2026-11645, in the V8 JavaScript engine, which is already being exploited in the wild. Google released emergency updates to address a new Chrome zero-day vulnerability, tracked as CVE-2026-11645, that has been exploited in the wild. This flaw is the fifth Chrome zero-day that is being exploited in […]
Pierluigi Paganini
April 01, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in Google Dawn to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a flaw in Google Dawn, tracked as CVE-2026-5281 (CVSS score of 8.8), to its Known Exploited Vulnerabilities (KEV) catalog. The flaw is a use after free in the Dawn […]
Pierluigi Paganini
April 01, 2026
Google fixed a new Chrome zero-day, tracked as CVE-2026-5281, in the WebGPU Dawn component that is already exploited in the wild. Google released Chrome updates fixing 21 vulnerabilities, including a new actively exploited zero-day tracked as CVE-2026-5281. The flaw is a use-after-free bug in Dawn, the WebGPU component used for graphics processing. Due to ongoing […]
Hacking / September 17, 2026





