 Pierluigi Paganini
 July 04, 2016
The researcher Dmytro Oleksiuk published details of ThinkPwn flaw, a UEFI zero-day that could be exploited by hackers to disable security features. Once again the IT giant Lenovo is in the headlines, some products of the company and some others from other PC vendors, are affected by a UEFI vulnerability, dubbed ThinkPwn, that can be exploited […]
 Pierluigi Paganini
July 04, 2016
For the cyber security experts, Karsten Nohl doesn’t need to be introduced, he is volcanic, a shining professional. Karsten Nohl is one of the most famous hackers in the world, laymen know him as the hacker that revealed to the world how to spy on anyone through the vulnerability in the SS7 protocol. Karsten Nohl […]
 Pierluigi Paganini
July 03, 2016
Two security experts have conducted a study that allowed them to spot over 100 snooping Tor HSDir Nodes spying on Dark Web Sites. The attempts of snooping traffic from Tor nodes are not a novelty, in the past, we have reported the activity of threat actors that set up malicious exit nodes to de-anonymize users. Early 2014, […]
 Pierluigi Paganini
July 02, 2016
Security experts from Kaspersky monitored a phishing campaign launched to spread a Facebook malware that infected more than 10,000 users in just two days. Security experts from Kaspersky monitored a phishing campaign that hit Israeli media since June 26th. Thousands of Facebook users reported that they had been infected by a malware spread through the […]
 Pierluigi Paganini
July 02, 2016
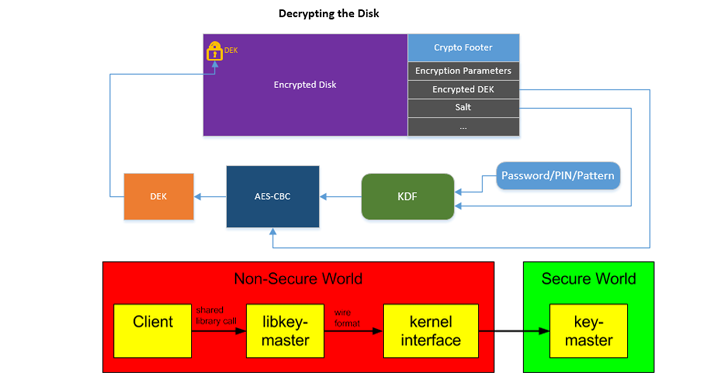
The Android full-disk encryption can be easily cracked with a brute force attack, hundreds of millions of Android mobile are at risk. Bad news for Android users that want to protect their data by enabling full-disk encryption (FDE) on their mobile devices. The Android full-disk encryption can be easily cracked with a brute force attack, […]
 Pierluigi Paganini
July 01, 2016
The Lizardsquad’s botnet known as LizardStresser is now leveraging on Internet of Things devices, latest waves of DDoS attack reached 400Gbps. The Lizardstresser DDoS botnet has been increasing in popularity throughout 2016 and is being used increasingly to target the Internet of Things. Arbor Networks reported in their blog, a marked increase since the start […]
 Pierluigi Paganini
July 01, 2016
Researchers discovered two flaws in the Siemens SICAM PAS widely used in the energy industry. One of the vulnerabilities is still unpatched. Security experts from Positive Technologies that have reviewed the Siemens SICAM PAS (Power Automation System) solution have discovered two information disclosure vulnerabilities (CVE-2016-5848 and CVE-2016-5849) that can be exploited by a local attacker. The experts […]
 Pierluigi Paganini
July 01, 2016
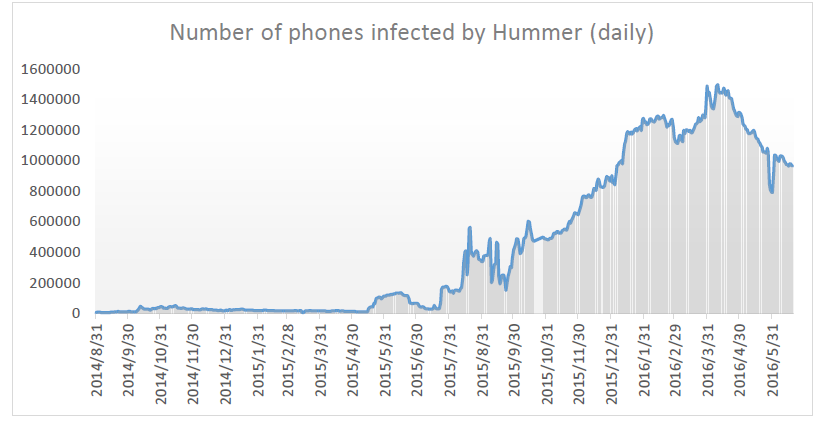
Experts from Cheetah Mobile firm revealed that the Hummer Android malware has already infected millions of smartphones worldwide. Security experts from the Cheetah Mobile firm are monitoring an Android malware dubbed Hummer since August 2014. The researchers noticed a significant increase in the number of infections in 2016, with a daily average of 1.4 million […]
 Pierluigi Paganini
June 30, 2016
Cisco released security patches for some of its products that fix critical and high severity flaw that could be remotely exploited by hackers. Cisco has released security patches for a number of high-severity vulnerabilities in the CISCO Management and other security products. One of the flaws, a critical vulnerability in the Cisco Prime Collaboration Provisioning (CVE-2016-1416), […]
 Pierluigi Paganini
June 30, 2016
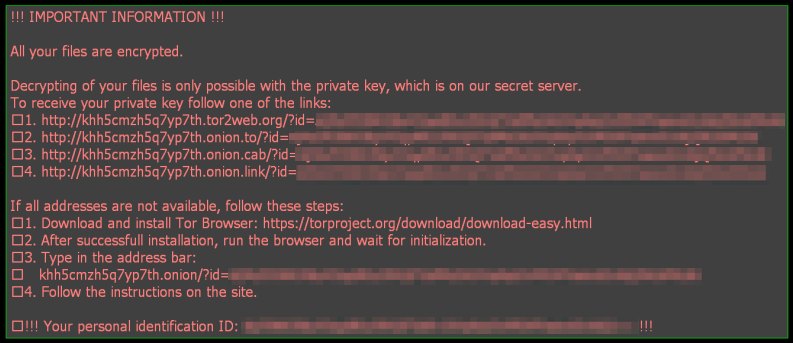
The authors responsible for Dridex and Locky malware have recently made another appearance, this time with their latest release – Bart malware. Similar to other ransomware, infected users are notified of the compromise with their desktop backgrounds changed with a warning, confirming that their files have been encrypted and offering a number of URLs accessible […]