


 Pierluigi Paganini
 June 01, 2014
Security researchers at Sucuri firm have discovered multiple serious vulnerabilities in the popular ‘All In One SEO Pack’ plugin for WordPress. WordPress in one of most targeted CMS platforms due its large diffusion, attackers are able to compromise victim instance exploiting flaws in outdated version or in vulnerable plugins . The Netcraft internet services company, in […]
 Pierluigi Paganini
May 29, 2014
Security experts at Kaspersky Lab have discovered a new banking trojan, dubbed Banker.AndroidOS.Basti.a, hidden in a fake WeChat application. Cyber criminals are abusing of the brand WeChat, the popular mobile application designed by Chinese company Tencent, to arrange a malware campaign which hit Chinese users. Experts at Kaspersky Lab have discovered that cybercriminals are using an […]
 Pierluigi Paganini
May 28, 2014
Spotify company is investigating unauthorized access to its systems and internal company data. Android users urge to update the app and change the password. The popular Music streaming service Spotify is the last illustrious victim of hackers. The Swedish company today has issued an advisory to inform its the users of its Android app that it has suffered a […]
 Pierluigi Paganini
May 27, 2014
Disclosed on Internet a curious news, hacking the Windows OS registry it is possible to get Windows XP Security Updates until 2019. On April 8th 2014 Microsoft officially ended the support for Windows XP, but there is still a wide audience of users that are using the oldest Microsoft OS. This portion of users is no more receiving security updates […]
 Pierluigi Paganini
May 27, 2014
Unencrypted cookies leave WordPress accounts exposed to hijacking on insecure networks, even if the two-factor authentication is enabled. WordPress administrators must be aware that it is quite easy for hackers to hijack their web site if they login from the same WI-Fi connection (e.g. From a public place) even if it is protected by two-factor authentication, . […]
 Pierluigi Paganini
May 26, 2014
Prosecutors filed a document which reveals ex LulzSec hacker Sabu helped US authorities stop more that 300 cyber attacks against US targets. The time of sentencing the former LulzSec hacker is arrived, next week the turned-FBI informant Hector “Sabu” Monsegur will be judged for the numerous cyber attacks he organized when he was a member of Anonymous group. […]
 Pierluigi Paganini
May 26, 2014
Cyber attacks could pose a potentially huge risk to US critical infrastructure, state-sponsored hackers and cyber criminals are increasing their activity. Governments are even more alarmed by the possibility of cyber attacks against critical infrastructure, hackers could pose a potentially huge risk to the helpless population. In a recent US Government exercise, a team of hackers […]
 Pierluigi Paganini
May 26, 2014
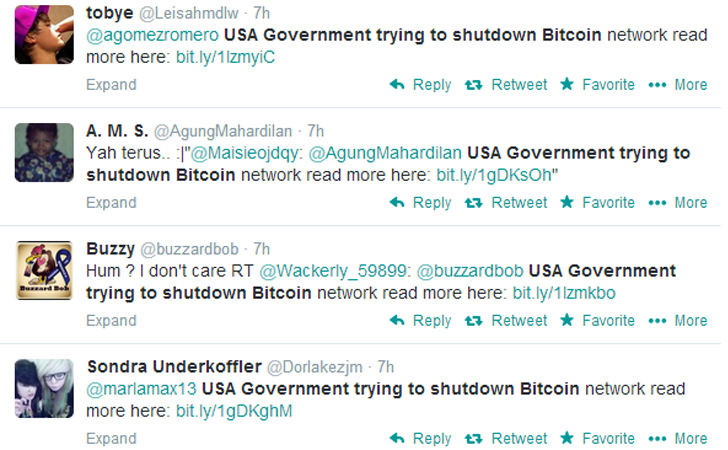
US Government was working on taking down Bitcoin, this is the theme of a new spam campaign via Twitter to spread malicious links. Security Experts at Malwarebytes have discovered a malicious scam spreading malicious links via Twitter. The cyber criminals behind the spam campaign are spreading malware through rogue tweets by a number of bogus Twitter accounts, they […]
 Pierluigi Paganini
May 25, 2014
Experts at Mandiant have corroborated the DOJ’s data by releasing additional evidence not included in the original APT1 report. One of the news most important shared on the internet this week it the one related to the indictment announced by US Department of Justice (DOJ) on five members of PLA Unit 61398. One year ago Mandiant experts deeply analyzed […]
 Pierluigi Paganini
May 25, 2014
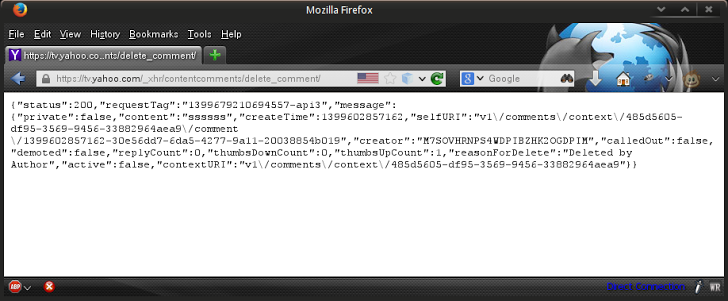
The Egyptian security researcher Ahmed Aboul-Ela has discovered a vulnerability which allowed deleting comments of any user in all Yahoo sites. A couple of days ago I was contacted by the Egyptian security researcher Ahmed Aboul-Ela which informed me to have disclosed a vulnerability in Yahoo websites which allow attackers to delete any comment from all Yahoo Services, […]







