 Pierluigi Paganini
 November 07, 2018
Security expert disclosed the details of a zero-day flaw affecting Oracle’s VirtualBox virtualization software without waiting for a patch from Oracle The security expert Sergey Zelenyuk has disclosed the details of a zero-day vulnerability affecting Oracle’s VirtualBox virtualization software that could be exploited by an attacker to make a guest-to-host escape. Zelenyuk publicly disclosed the vulnerability […]
 Pierluigi Paganini
November 07, 2018
HSBC Bank USA notified customers of a data breach that has happened between Oct 4 and Oct 14, unknown attackers were able to access their online accounts. HSBC Bank USA notified customers of a data breach that has happened between October 4 and October 14, unknown attackers were able to access online accounts of the financial institution. Exposed info […]
 Pierluigi Paganini
November 07, 2018
Apache Struts Users have to update the Commons FileUpload library in Struts 2 that is affected by two vulnerabilities. Apache Struts developers have addressed two vulnerabilities in the Commons FileUpload library in Struts 2, the flaws can be exploited for remote code execution and denial-of-service (DoS) attacks. “Apache today released an advisory, urging users who run Apache Struts 2.3.x to […]
 Pierluigi Paganini
November 06, 2018
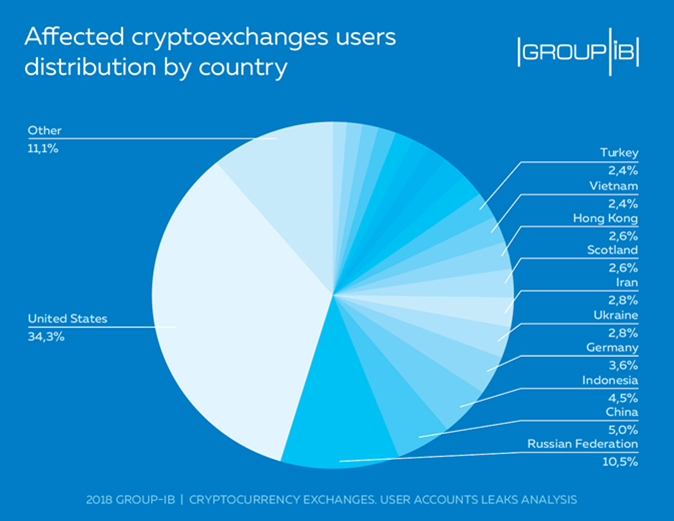
Group-IB and Swiss insurance broker ASPIS that owns CryptoIns project, have developed the world’s first scoring model for assessing cryptocurrency exchanges Group-IB, an international company that specializes in preventing cyber attacks, and a Swiss insurance broker ASPIS SA that owns CryptoIns project, have developed the world’s first scoring model for assessing cryptocurrency exchanges cybersecurity, allowing the exchanges’ clients to ensure their assets. According to CryptoIns analysts, […]
 Pierluigi Paganini
November 06, 2018
The encryption system implemented by popular solid-state drives (SSDs) is affected by critical vulnerabilities that could be exploited by a local attacker to decrypt data. The flaws were discovered by researchers Carlo Meijer and Bernard van Gastel at Radboud University in the Netherlands, the duo discovered that it is possible to bypass password-based authentication to access to […]
 Pierluigi Paganini
November 06, 2018
Security experts at Trend Micro have spotted an IRC bot dubbed Shellbot that was built using Perl Shellbot. The malware was distributed by a threat group called Outlaw, it was able to target Linux and Android devices, and also Windows systems. “We uncovered an operation of a hacking group, which we’re naming “Outlaw” (translation derived from the Romanian word haiduc, […]
 Pierluigi Paganini
November 05, 2018
Google queries allowed Iran Government to dismantle the CIA communication network used by its agents and kill dozens of tens of spies The alleged hack of the communications network used by CIA agents allowed Iranian intelligence to identify and kill at least 30 spies. According to Yahoo! News the security breach has happened in 2009, the Iranian […]
 Pierluigi Paganini
November 05, 2018
Icecast streaming media server is affected by a flaw that could be exploited by an attacker to take off the broadcast of online radio stations. Icecast streaming media server is affected by a vulnerability, tracked as CVE-2018-18820, that could be exploited by an attacker to take off the broadcast of online radio stations. Icecast supports both audio and video data […]
 Pierluigi Paganini
November 05, 2018
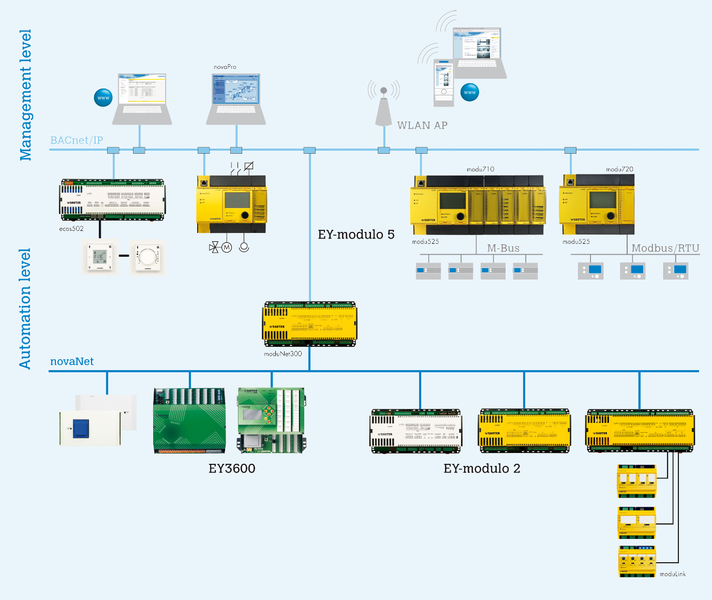
A security researcher has found a serious vulnerability in a building automation product from Sauter AG that could be exploited to steal files from an affected system. Sauter AG CASE Suit is a building automation product used worldwide that is affected by a high severity XML external entity (XXE) vulnerability that could be exploited to steal files from an affected […]
 Pierluigi Paganini
November 05, 2018
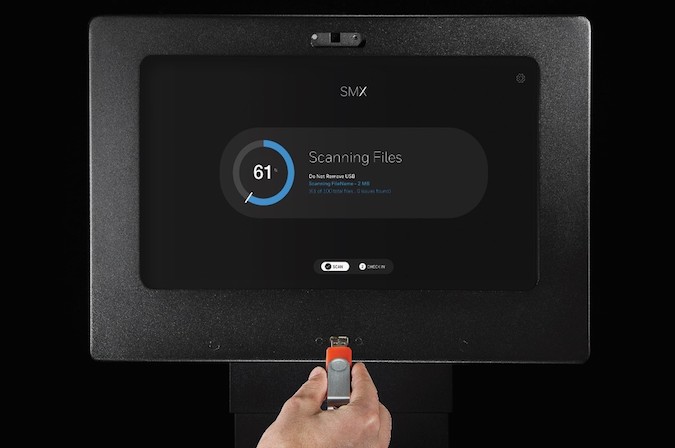
USB removable storage devices are the main vector for malware attacks against industrial facilities, states Honeywell report. According to a report published on by Honeywell, malware-based attacks against industrial facilities mostly leverage USB removable storage devices Experts from Honeywell analyzed data collected with the Secure Media Exchange (SMX), a product it has launched in 2017 and that was designed […]