 Pierluigi Paganini
 April 05, 2020
A new round of the weekly newsletter arrived! The best news of the week with Security Affairs Coronavirus-themed attacks March 22 – March 28, 2020 FIN7 hackers target enterprises with weaponized USB drives via USPS Source code of Dharma ransomware now surfacing on public hacking forums Crooks leverage Zooms popularity in Coronavirus outbreak to serve […]
 Pierluigi Paganini
April 04, 2020
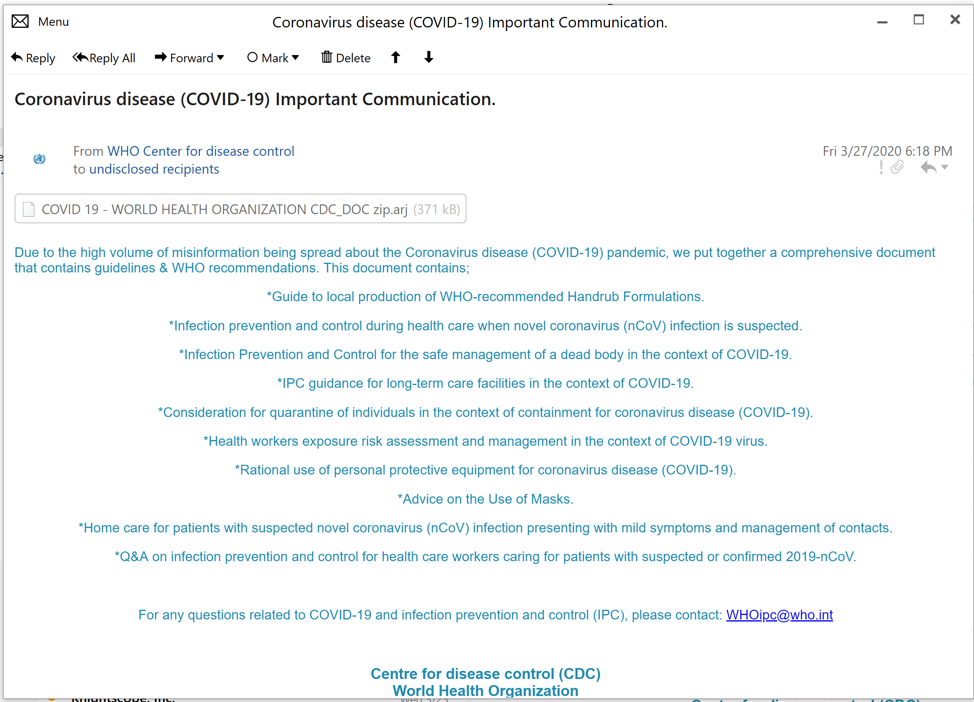
Researchers spotted a new Coronavirus-themed attack, the messages pretend to be sent from the World Health Organization to deliver Lokibot infostealer. Security experts at FortiGuard Labs discovered a new Coronavirus-themed campaign using alleged messages from the World Health Organization (WHO) to deliver the LokiBot trojan. The campaign was uncovered on March 27 when the researchers […]
 Pierluigi Paganini
April 04, 2020
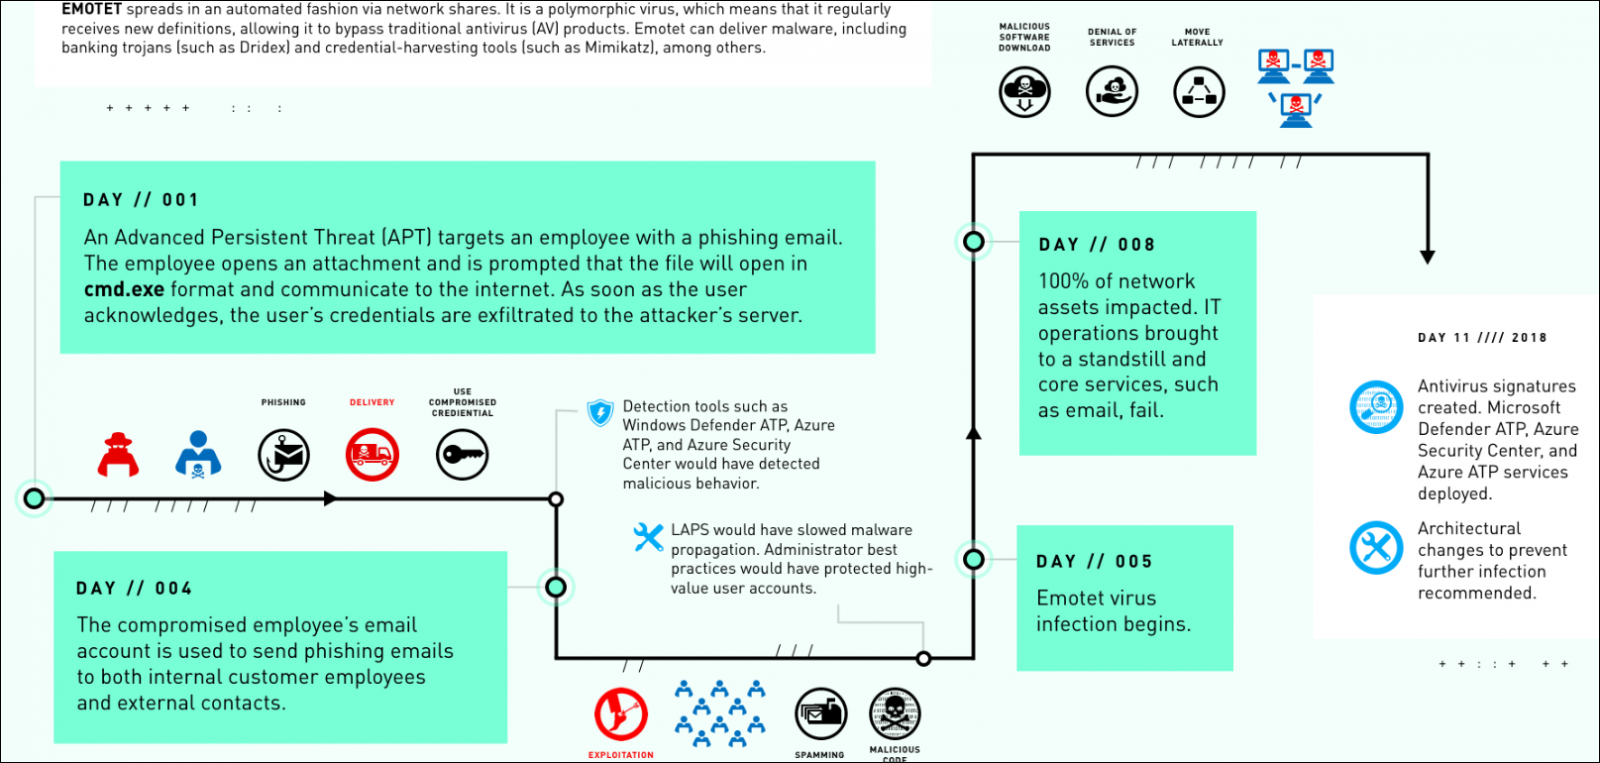
Microsoft declared that an Emotet attack took down an organization’s network by overheating all the computers and bringing its Internet access down. Microsoft shared details of the Emotet attack suffered by an organization named Fabrikam in the Microsoft’s Detection and Response Team (DART) Case Report 002, where Fabrikam is a fake name the IT giant […]
 Pierluigi Paganini
April 03, 2020
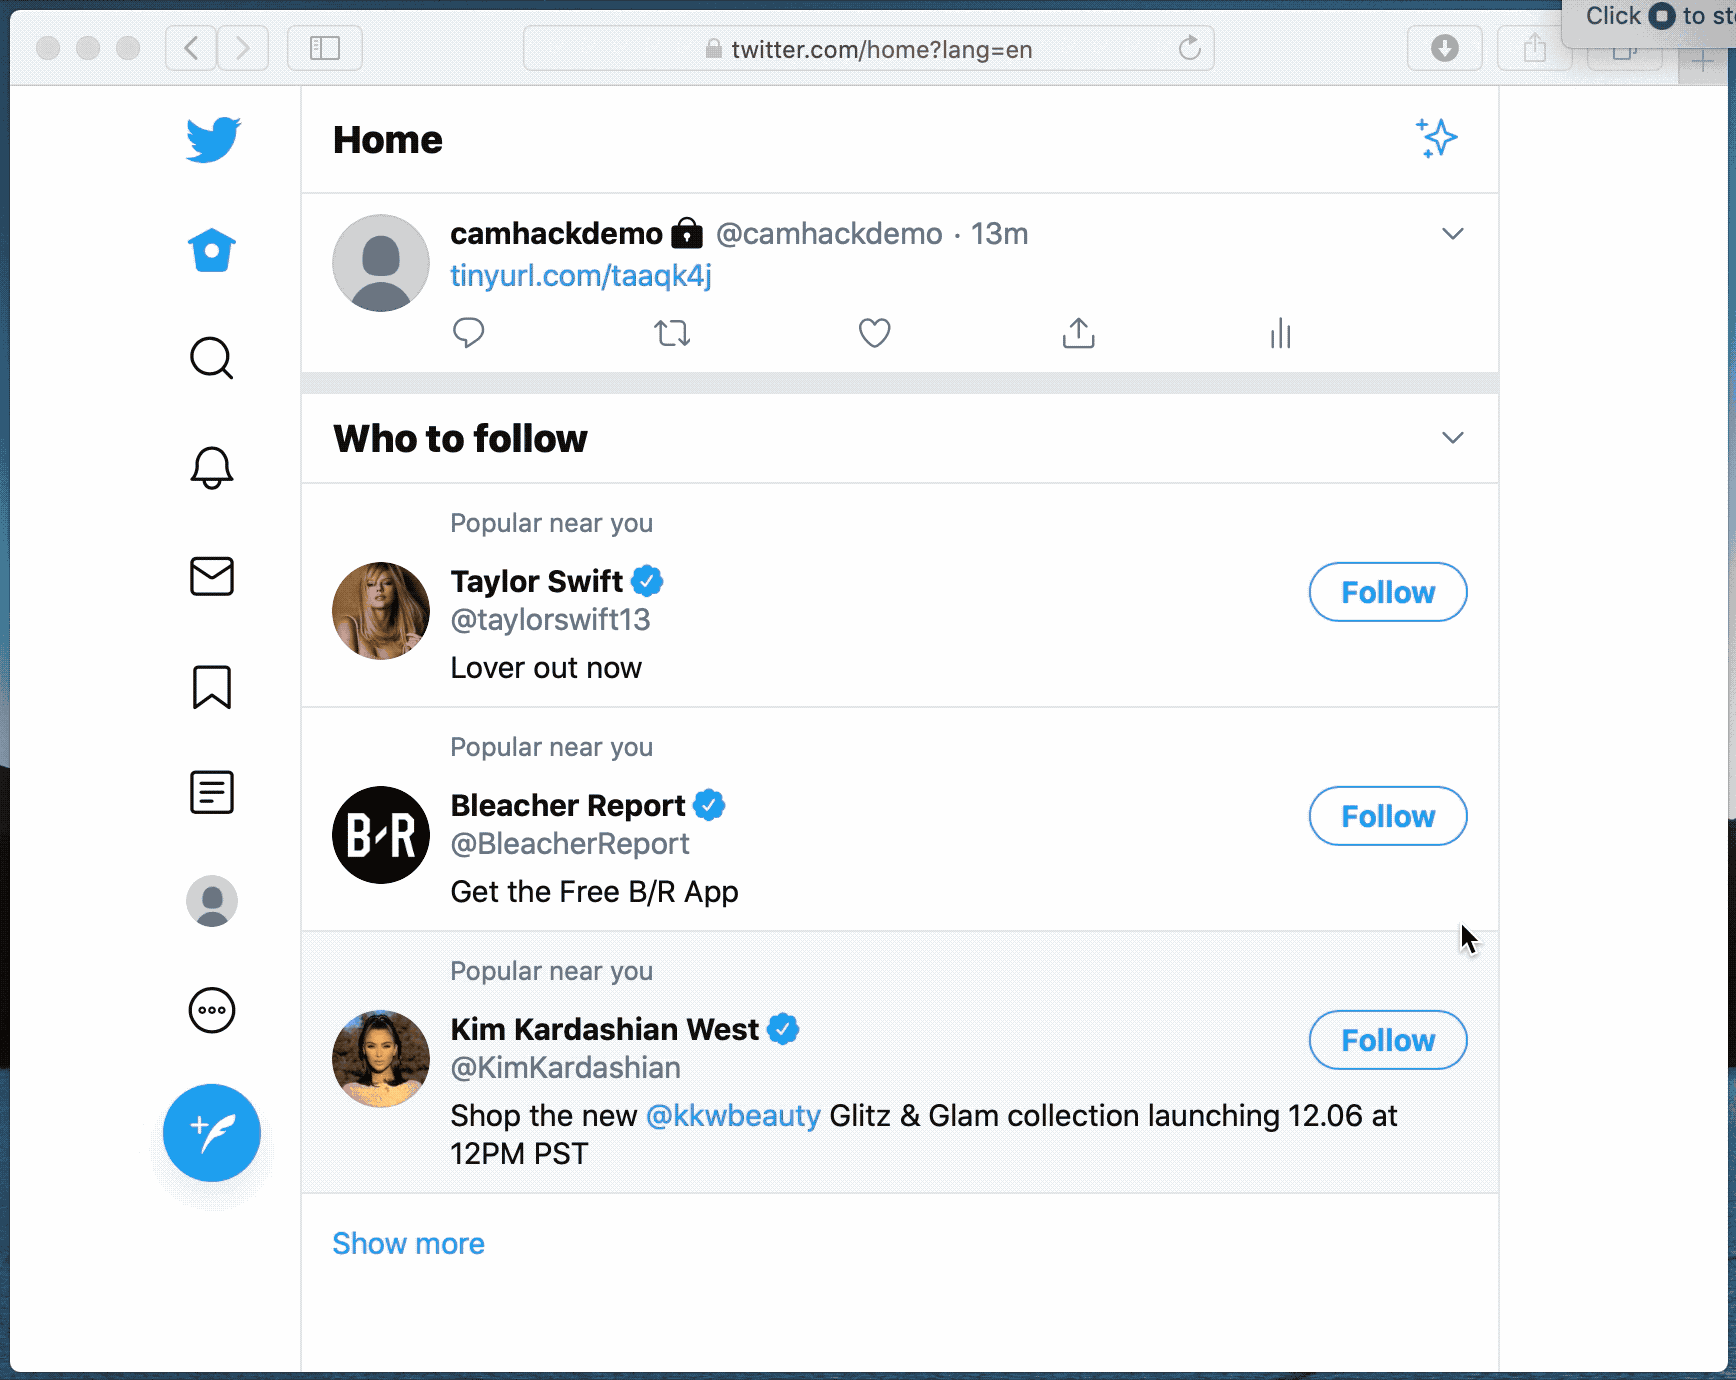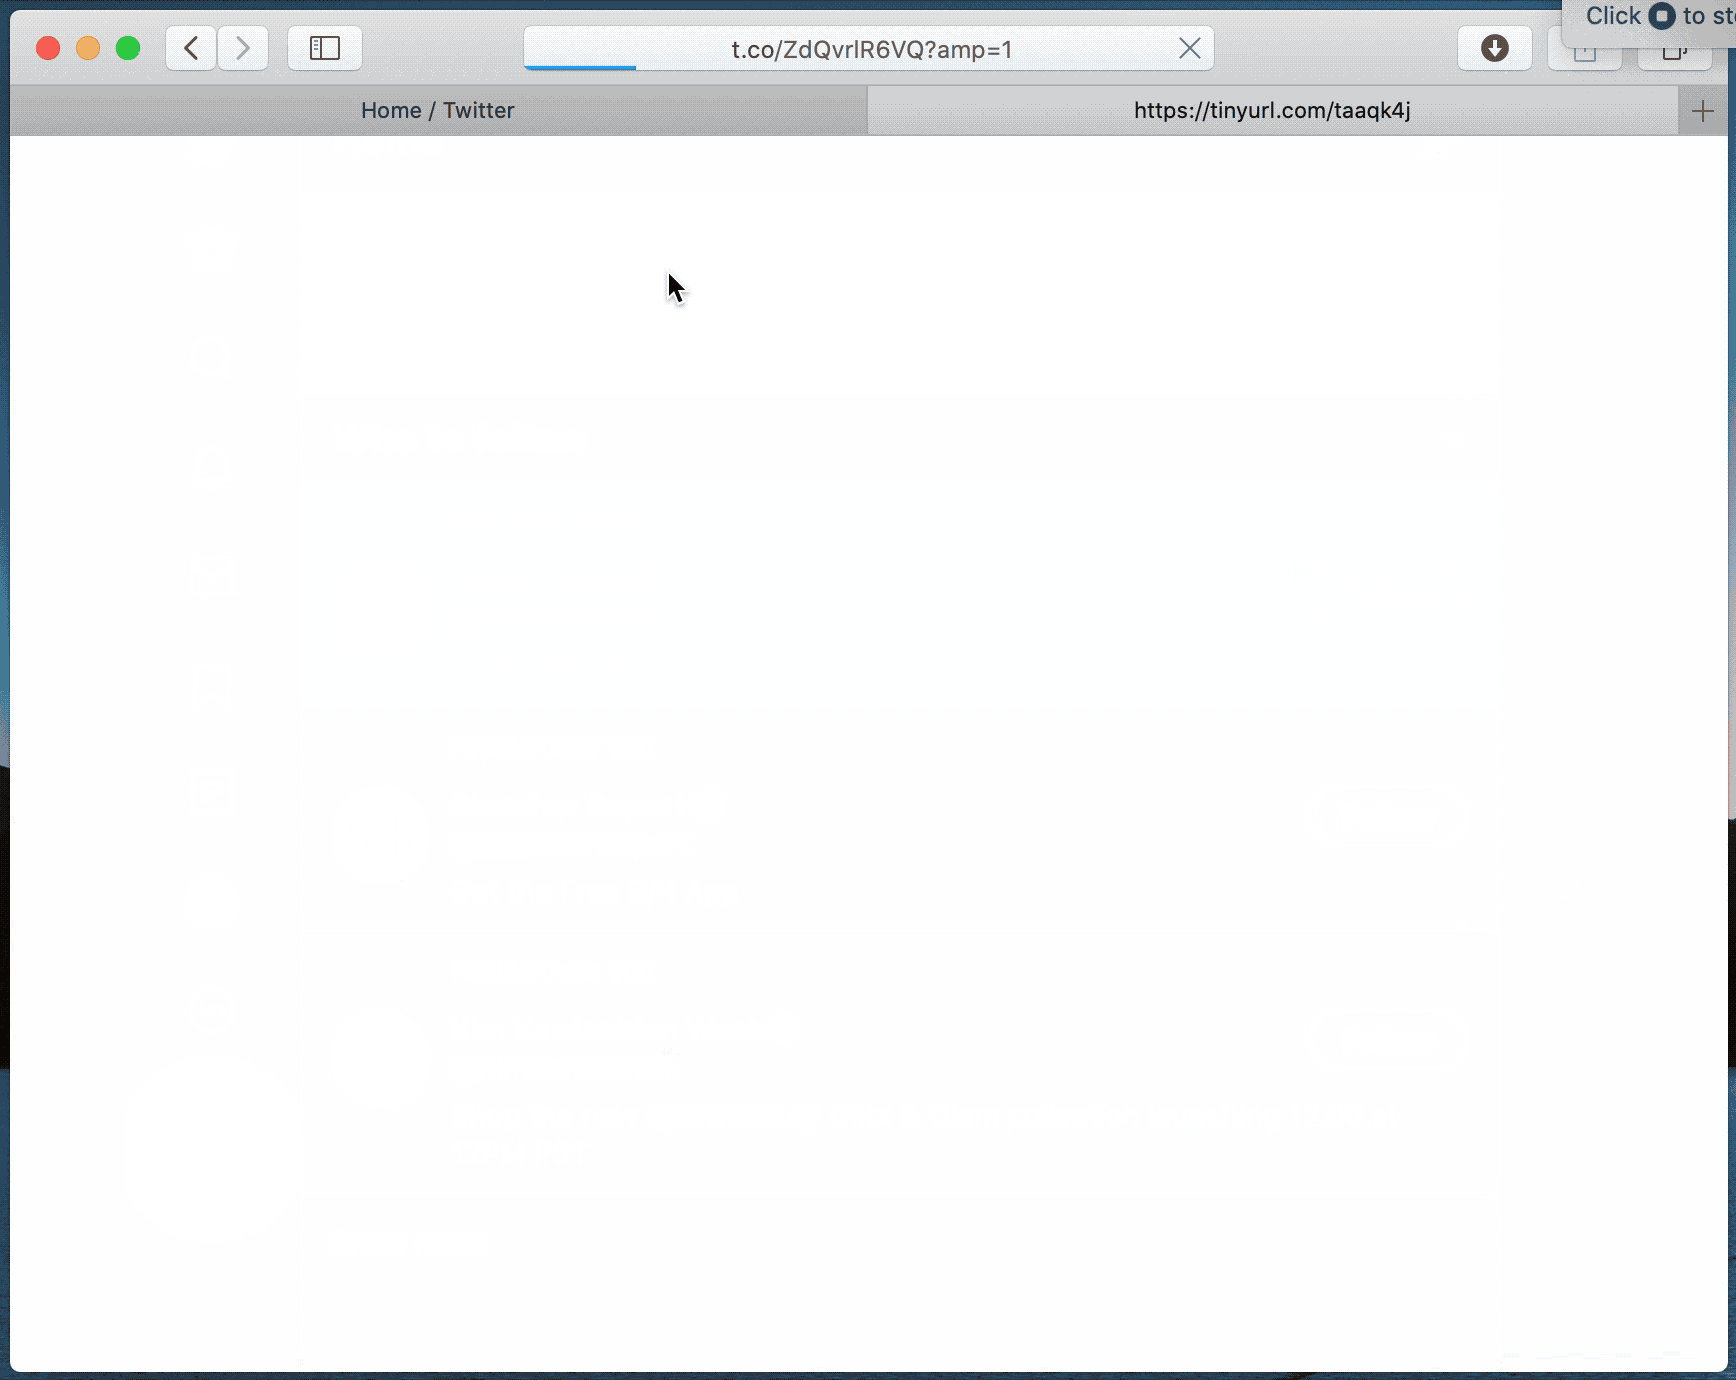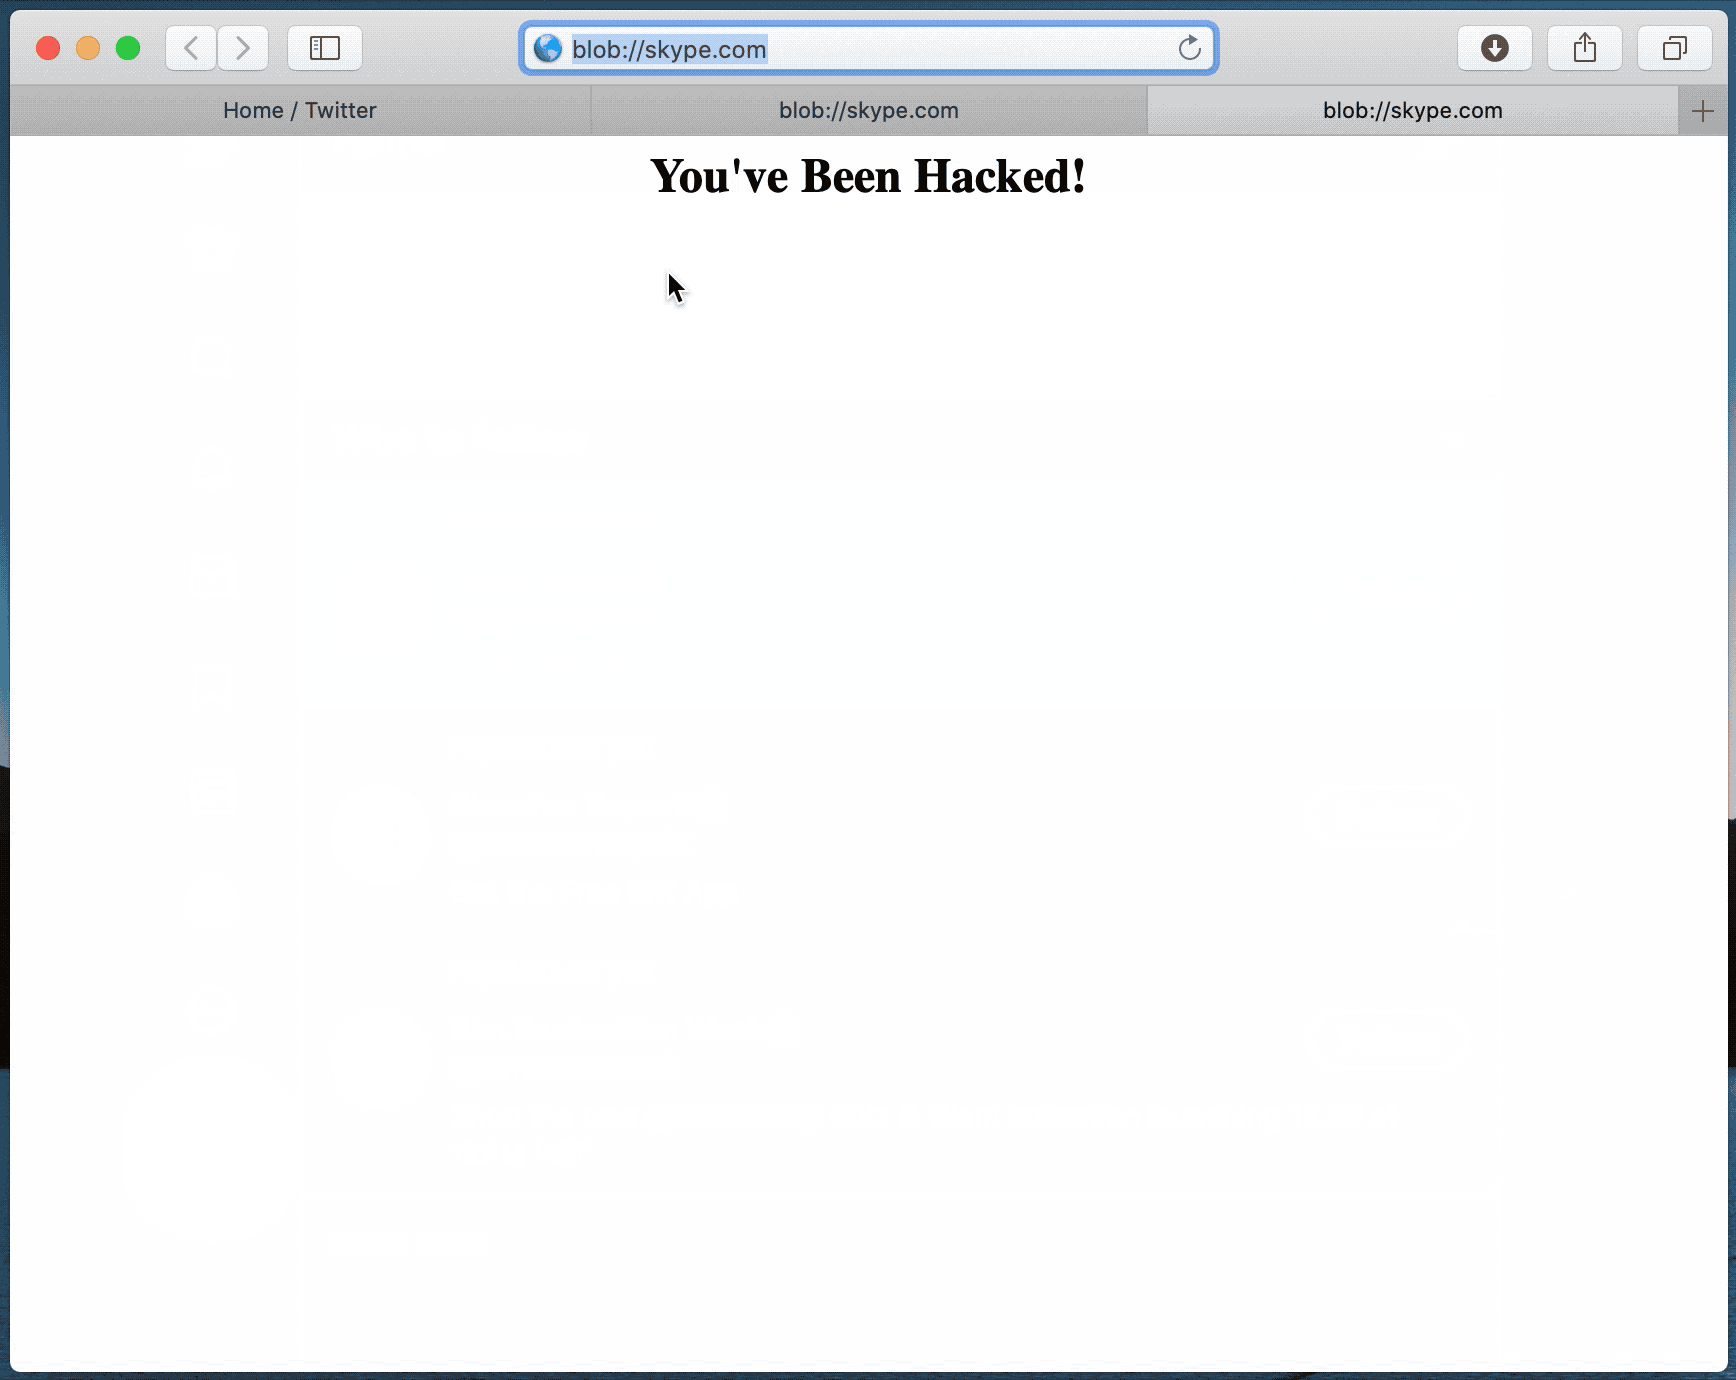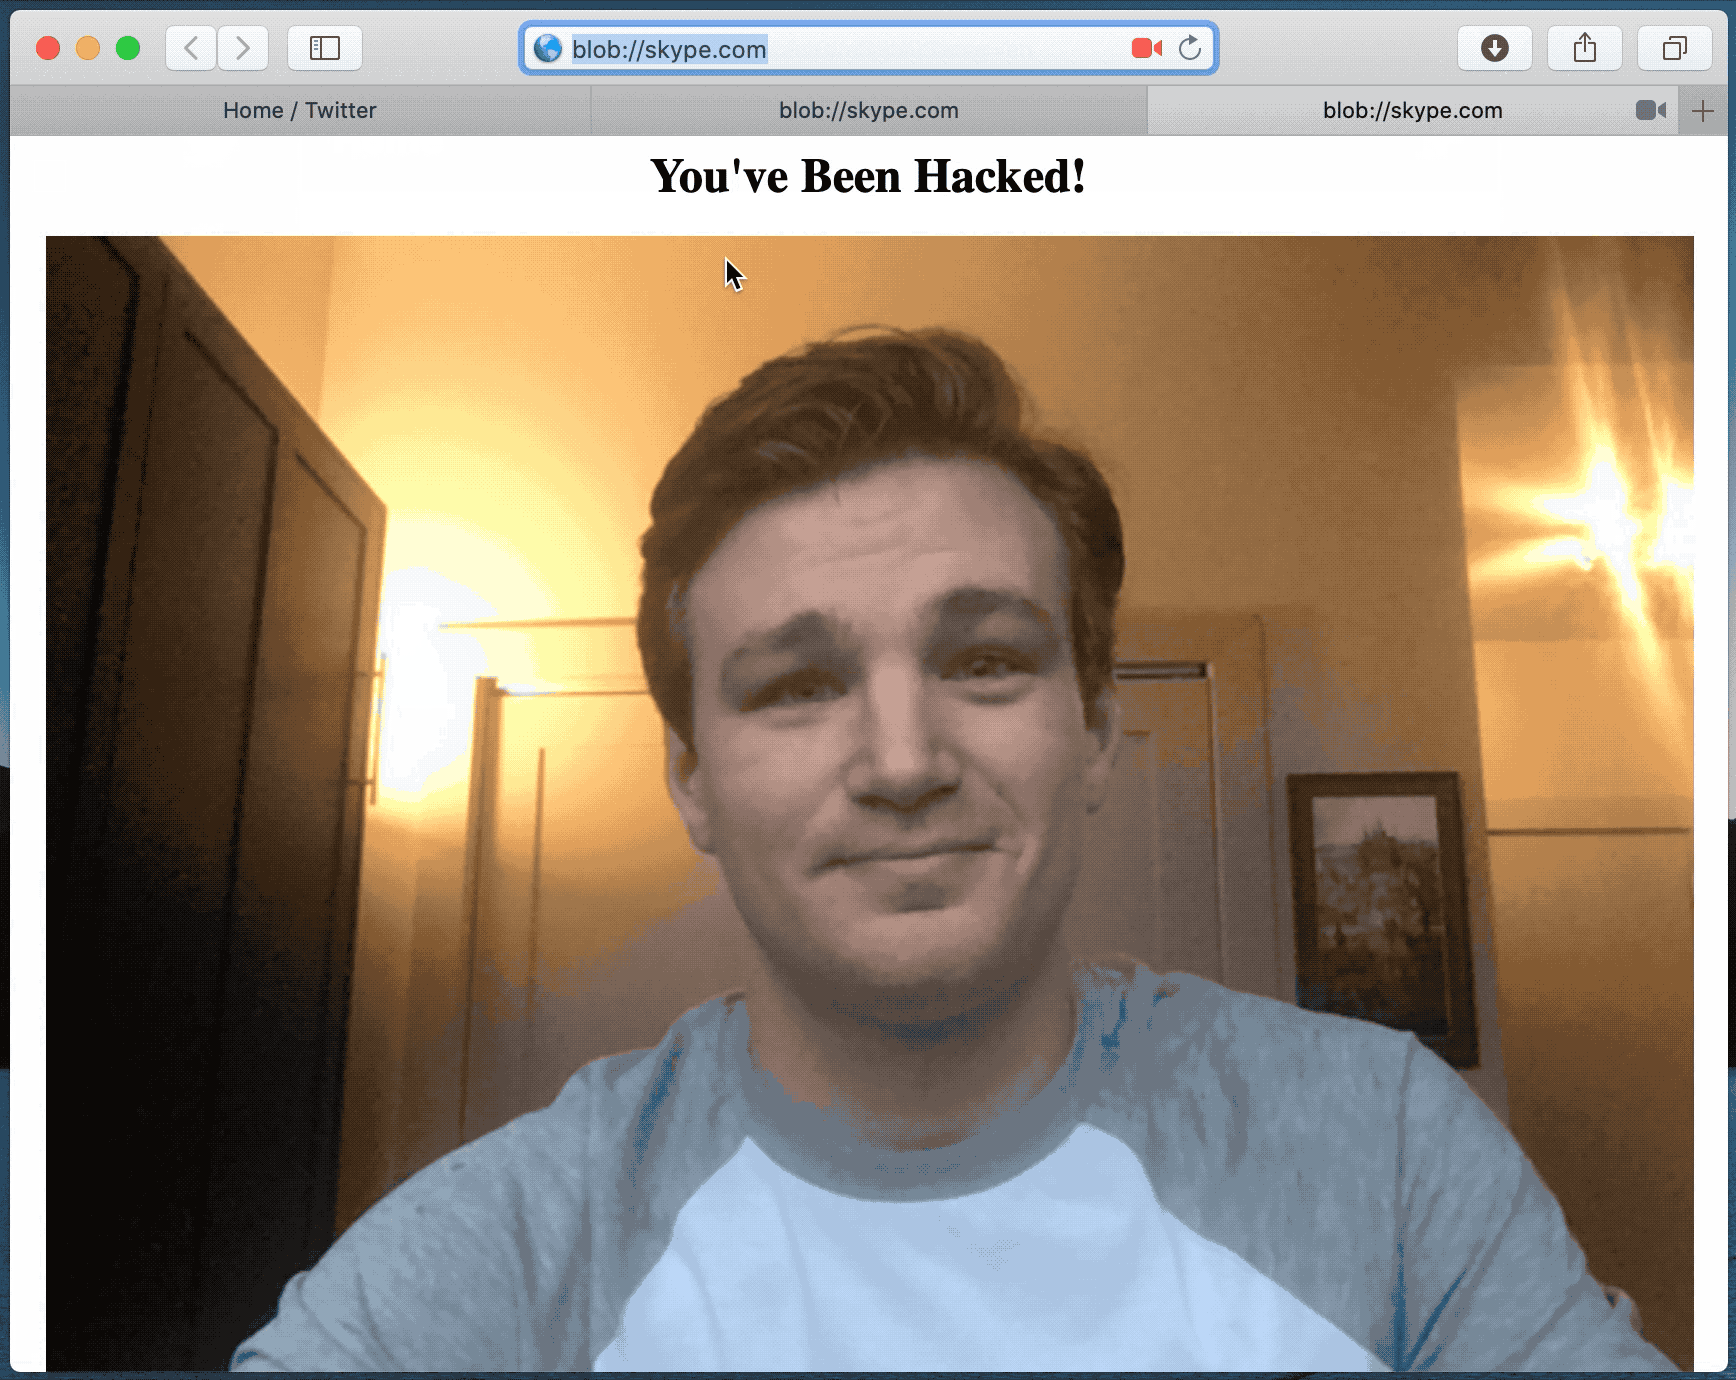
Bad news for Apple iPhone or MacBook users, attackers could hack their device’s camera by tricking them into visiting a website. The ethical hacker Ryan Pickren demonstrated that it is possible to hack Apple iPhone or MacBook users by simply tricking them into visiting a website with the Safari browser. Pickren reported seven vulnerabilities to Apple […]
 Pierluigi Paganini
April 03, 2020
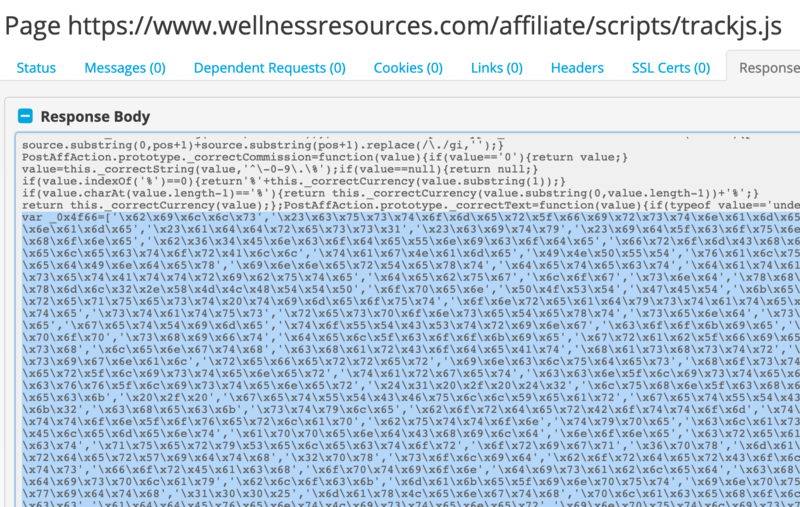
RiskIQ researchers spotted a new ongoing Magecart campaign that already compromised at least 19 different e-commerce websites. Researchers from security firm RiskIQ have uncovered a new ongoing Magecart campaign that already compromised at least 19 different e-commerce websites to steal customers’ payment card data. The experts discovered a new software skimmer, dubbed “MakeFrame,” that injects […]
 Pierluigi Paganini
April 03, 2020
Twitter discloses a privacy issue in the way the Mozilla Firefox cached private files sent or received via DM for up to 7 days. Twitter admitted that the private files sent via Twitter DMs were cached inside the users’ Firefox browsers for up to seven days, even if users have logged off. The problem is […]
 Pierluigi Paganini
April 03, 2020
An authenticated stored cross-site scripting (XSS) vulnerability could allow attackers to create rogue admins on WordPress sites using Contact Form 7 Datepicker plugin. Administrators of WordPress sites using the Contact Form 7 Datepicker plugin are recommended to remove or deactivate it to prevent attackers from exploiting a stored cross-site scripting (XSS) vulnerability to create rogue […]
 Pierluigi Paganini
April 02, 2020
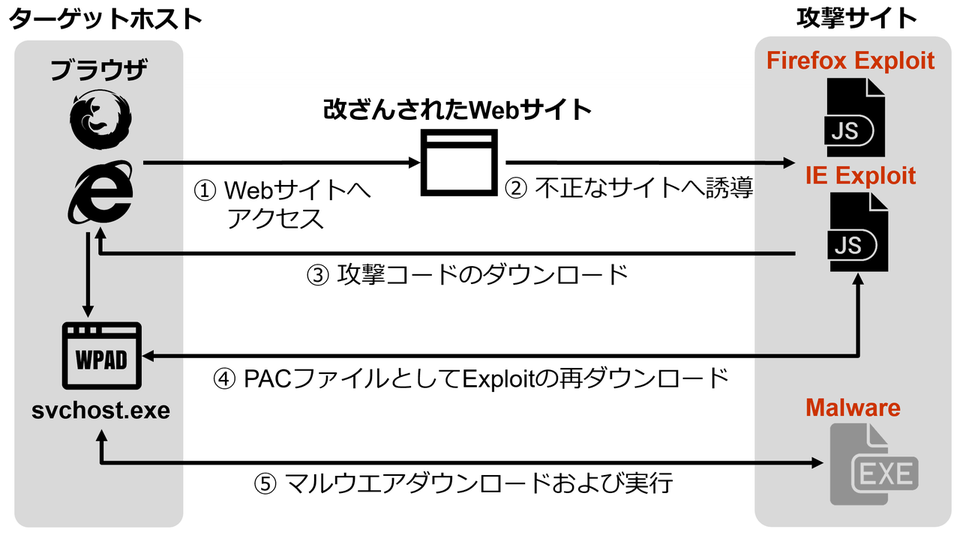
An APT group is exploiting the flaws patched earlier this year in Firefox and Internet Explorer in attacks aimed at China and Japan. An APT group is exploiting two vulnerabilities patched earlier this year in Firefox and Internet Explorer in attacks aimed at China and Japan. The first issue, tracked as CVE-2019-17026, affects the Firefox […]
 Pierluigi Paganini
April 02, 2020
Microsoft is sending notifications to dozens of hospitals about vulnerable VPN devices and gateways exposed online in their network. Microsoft is warning dozens of hospitals of the risks of ransomware attacks due to insecure VPN devices and gateways exposed online. Recently Microsoft has published details about human-operated ransomware attacks that targeted organizations in various industries. […]
 Pierluigi Paganini
April 01, 2020
The popular Zoom app is under scrutiny, experts have discovered a vulnerability that could be exploited to steal users’ Windows passwords. Experts warn of a ‘UNC path injection’ flaw that could be exploited by remote attackers to steal login credentials from Windows systems. Security experts and privacy advocates believe that the Zoom is an efficient […]