 Pierluigi Paganini
 March 15, 2023
Russia-linked APT29 group abused the legitimate information exchange systems used by European countries to target government entities. Russia-linked APT29 (aka SVR group, Cozy Bear, Nobelium, and The Dukes) was spotted abusing the legitimate information exchange systems used by European countries in attacks aimed at governments. In early March, BlackBerry researchers uncovered a new cyber espionage campaign aimed at EU […]
 Pierluigi Paganini
March 15, 2023
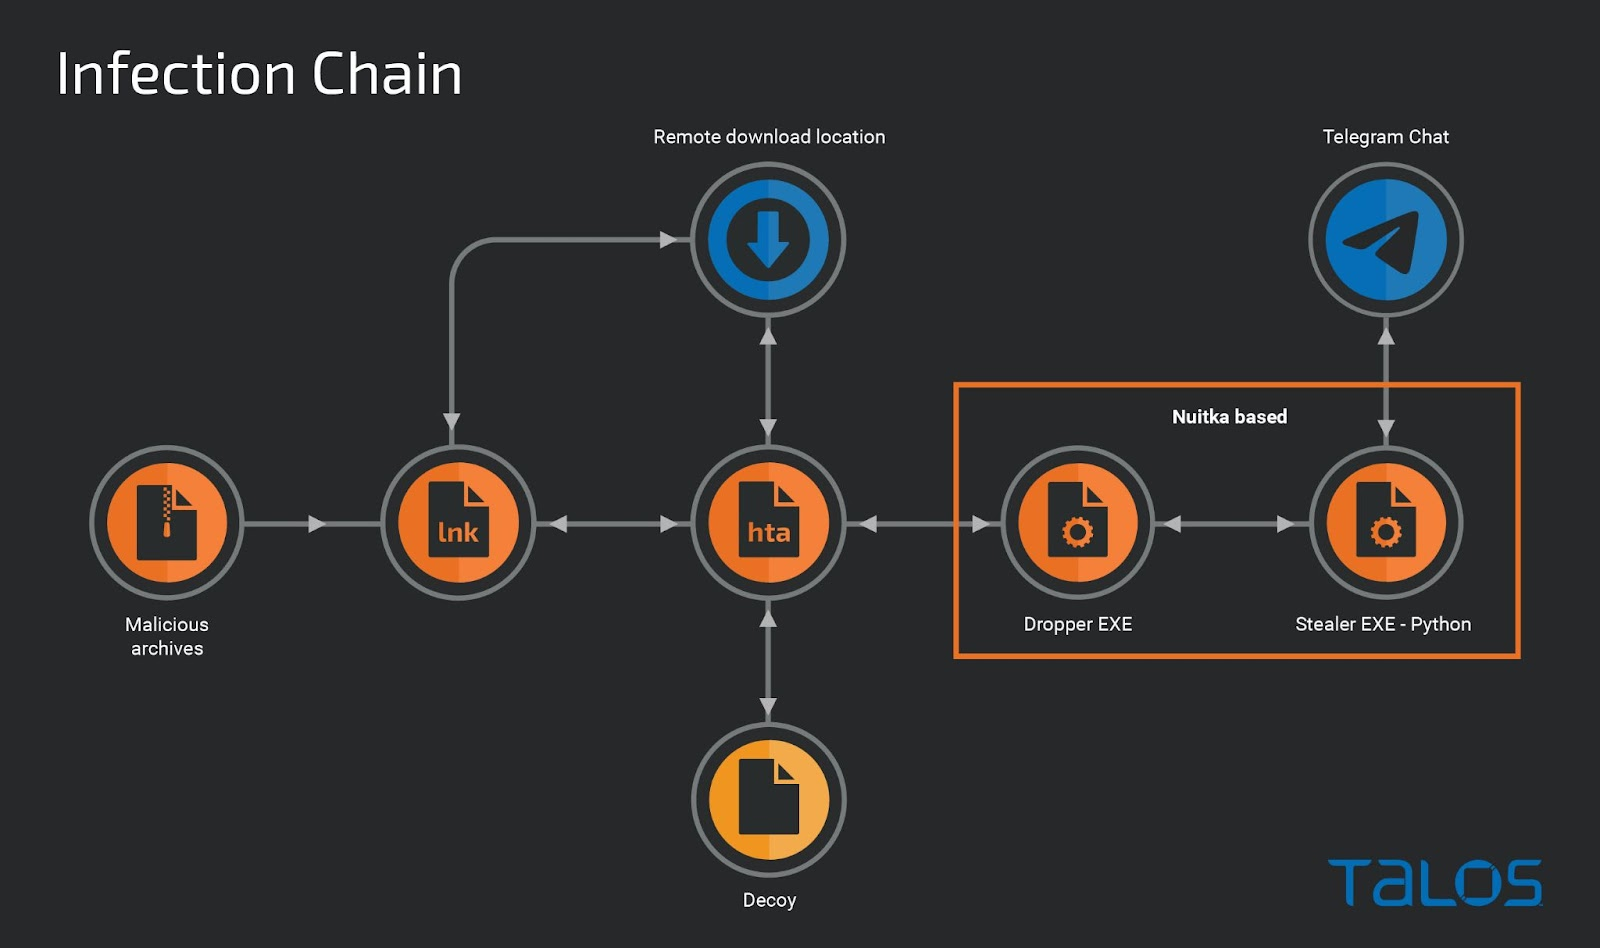
A new APT group, dubbed YoroTrooper, has been targeting government and energy organizations across Europe, experts warn. Cisco Talos researchers uncovered a new cyber espionage group targeting CIS countries, embassies and EU health care agency since at least June 2022. The APT group focuses on government or energy organizations in Azerbaijan, Tajikistan, Kyrgyzstan and other Commonwealth […]
 Pierluigi Paganini
March 14, 2023
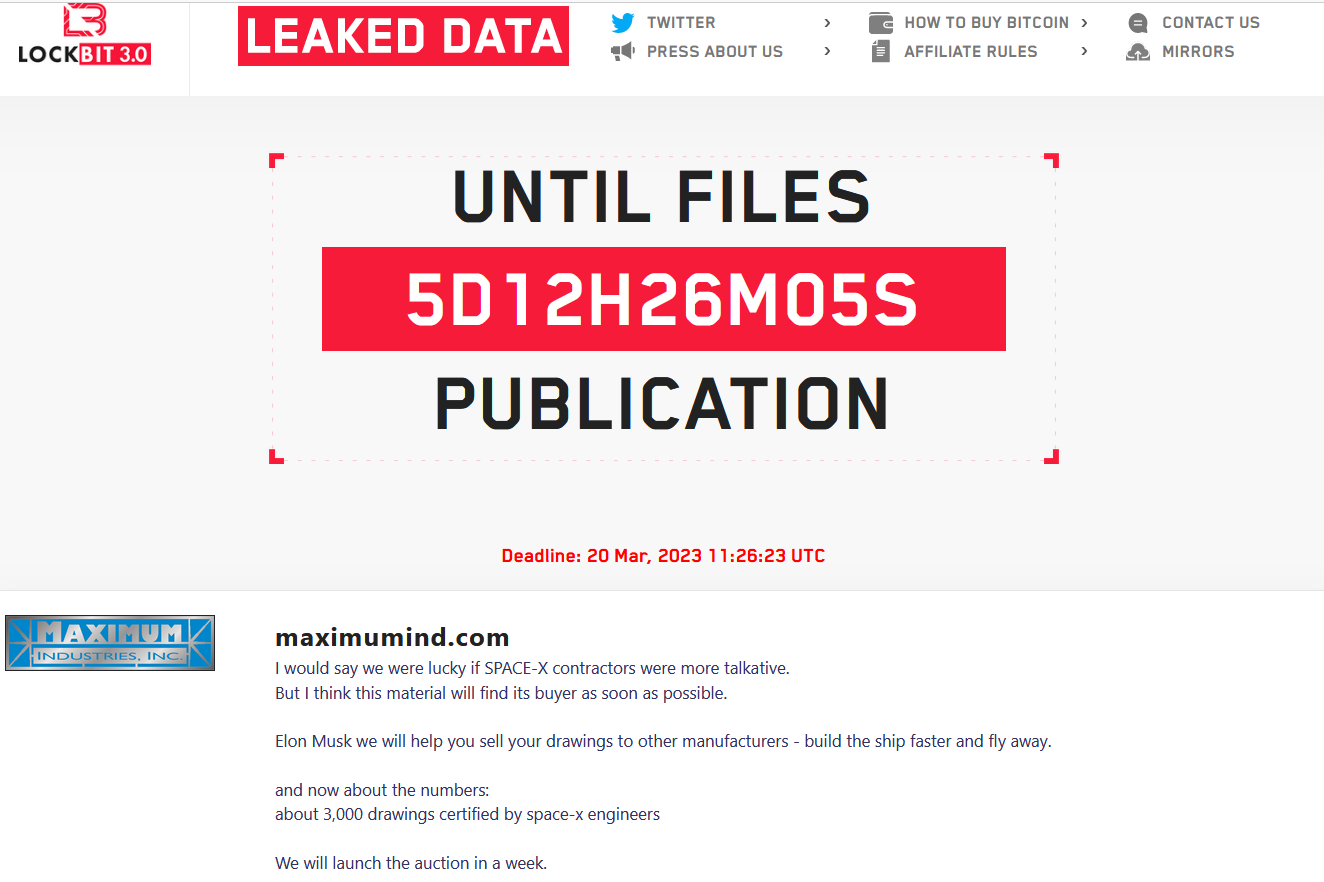
The LockBit ransomware group claims to have stolen confidential data belonging to SpaceX from the systems of Maximum Industries. The LockBit ransomware gang claims to have stolen confidential data of SpaceX after they hacked the systems of production company Maximum Industries. Maximum Industries is a full-service, piece-part production, and contract manufacturing facility. The ransomware gang […]
 Pierluigi Paganini
March 14, 2023
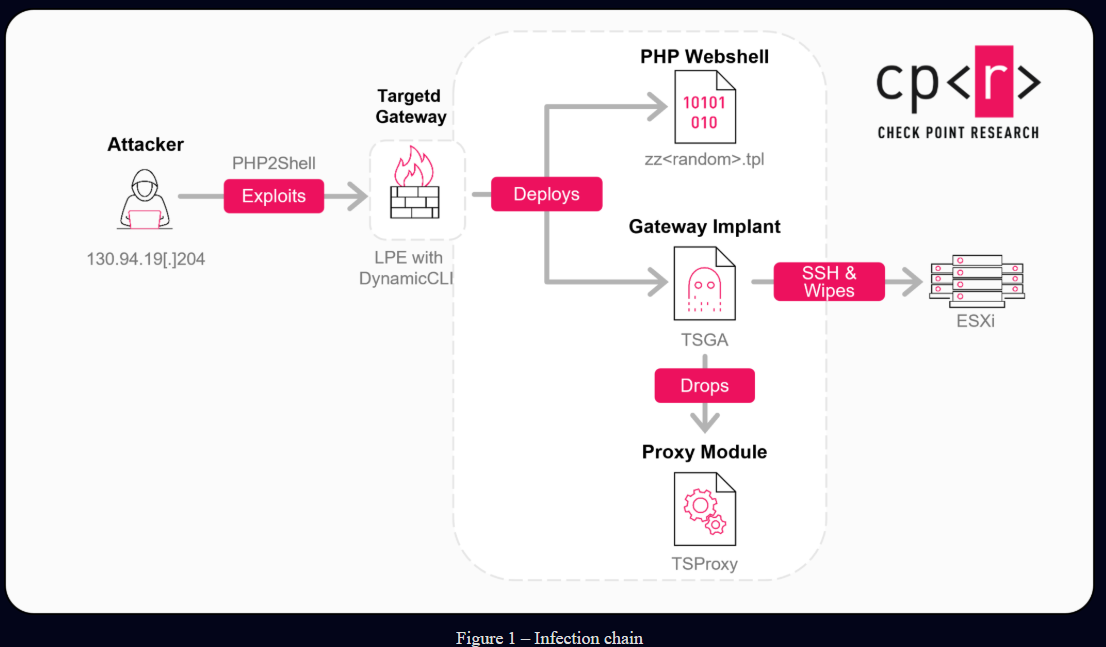
An unknown threat actor is targeting Government entities and large organizations by exploiting a security flaw in Fortinet FortiOS. Fortinet researchers are warning of an advanced threat actor that is targeting governmental or government-related entities. The unknown threat actor is exploiting a vulnerability in Fortinet FortiOS software, tracked as CVE-2022-41328, that may allow a privileged […]
 Pierluigi Paganini
March 14, 2023
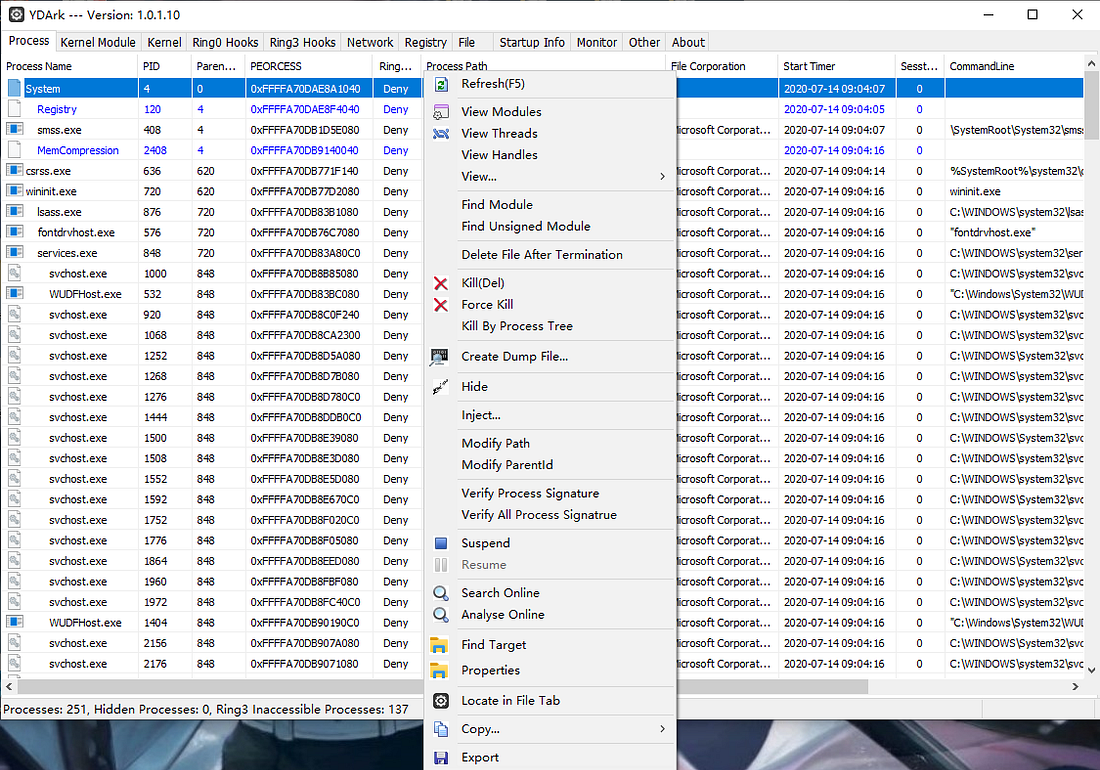
Cyber security researcher Luca Mella analyzed the Makop ransomware employed in a recent intrusion. Executive summary Introduction The Makop ransomware operators started their infamous criminal business in 2020 leveraging a new variant of the notorious Phobos ransomware. During the last years, the gang maintained a solid presence in the criminal underground even if they did […]
 Pierluigi Paganini
March 13, 2023
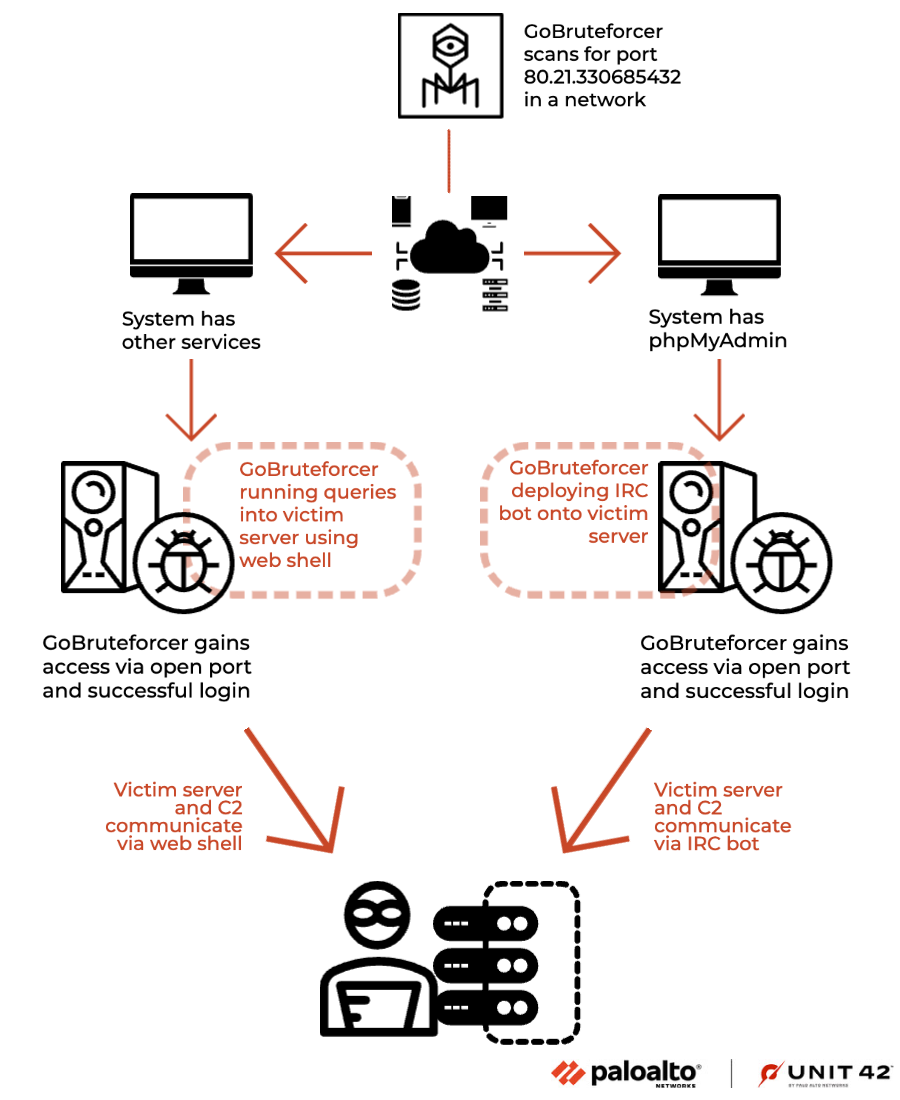
A recently discovered Golang-based botnet, dubbed GoBruteforcer, is targeting web servers running FTP, MySQL, phpMyAdmin, and Postgres services Researchers from Palo Alto Networks Unit 42 recently discovered a Golang-based botnet, tracked as GoBruteforcer, which is targeting web servers running FTP, MySQL, phpMyAdmin, and Postgres services. In order to compromise a target system, the samples require […]
 Pierluigi Paganini
March 13, 2023
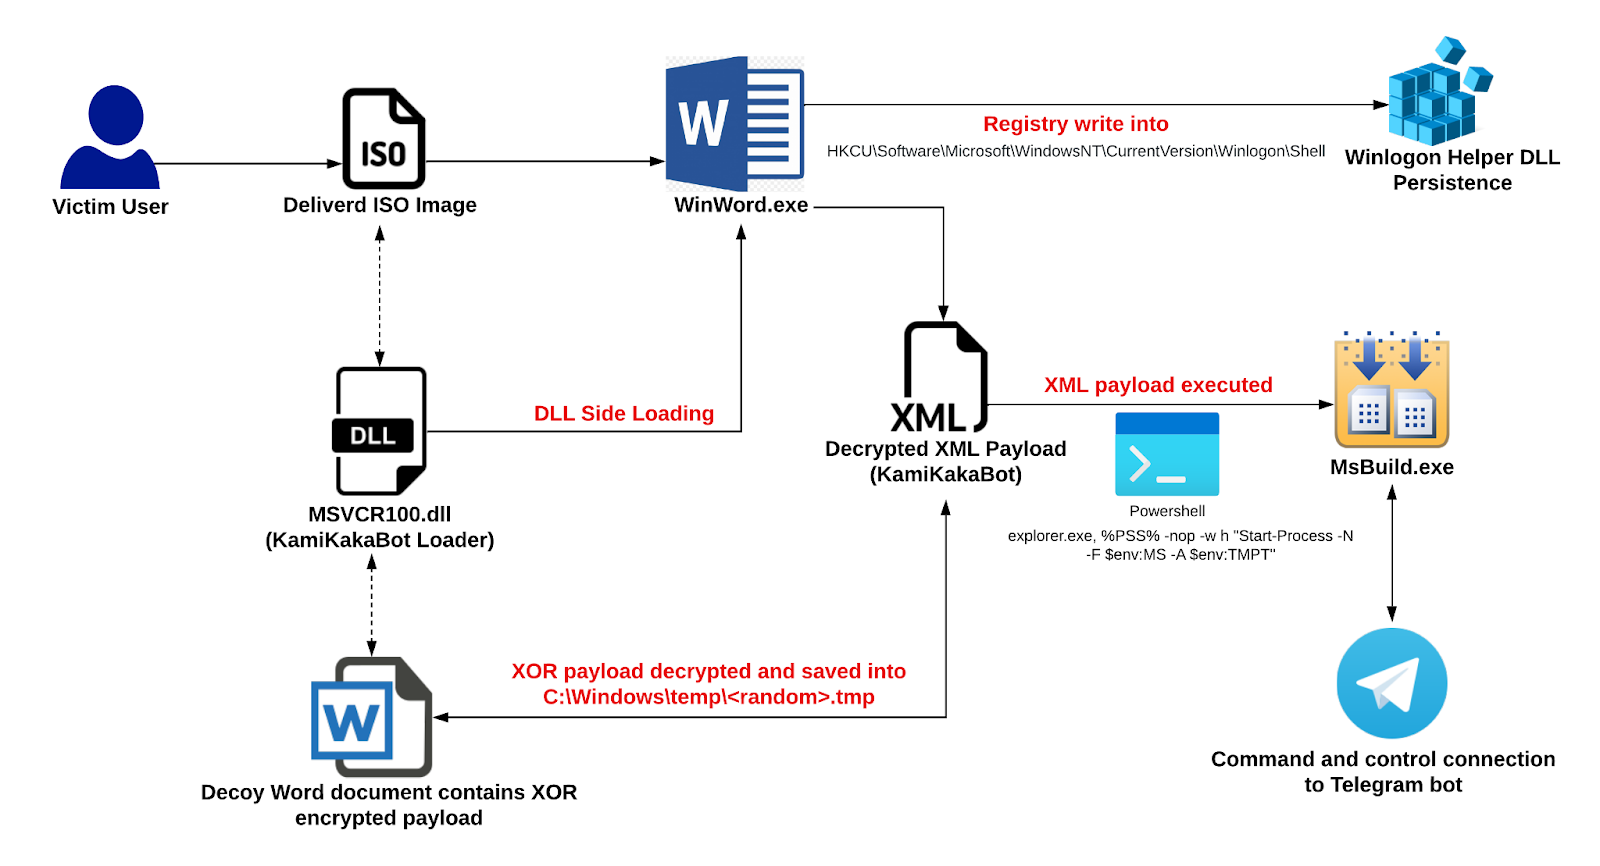
Researchers reported that Dark Pink APT employed a malware dubbed KamiKakaBot against Southeast Asian targets. In February 2023, EclecticIQ researchers spotted multiple KamiKakaBot malware samples that were employed by the Dark Pink APT group (aka Saaiwc) in attacks against government entities in Southeast Asia countries. The activity of the group was first detailed by Group-IB […]
 Pierluigi Paganini
March 12, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. PlugX malware delivered by exploiting flaws in Chinese programs Prometei botnet evolves and infected +10,000 […]
 Pierluigi Paganini
March 11, 2023
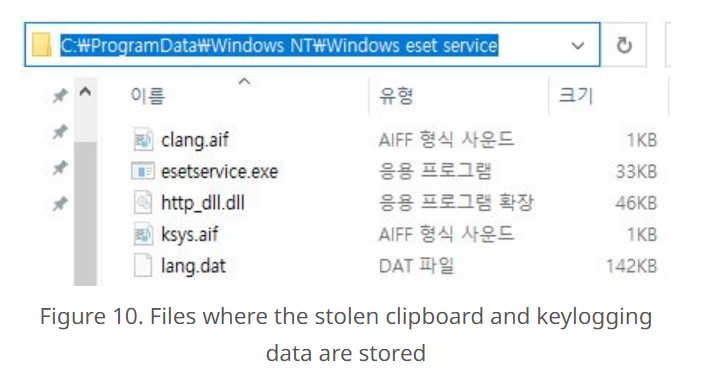
Researchers observed threat actors deploying PlugX malware by exploiting flaws in Chinese remote control programs Sunlogin and Awesun. Researchers at ASEC (AhnLab Security Emergency response Center) observed threat actors deploying the PlugX malware by exploiting vulnerabilities in the Chinese remote control software Sunlogin and Awesun. Sunlogin RCE vulnerability (CNVD-2022-10270 / CNVD-2022-03672) is known to be […]
 Pierluigi Paganini
March 11, 2023
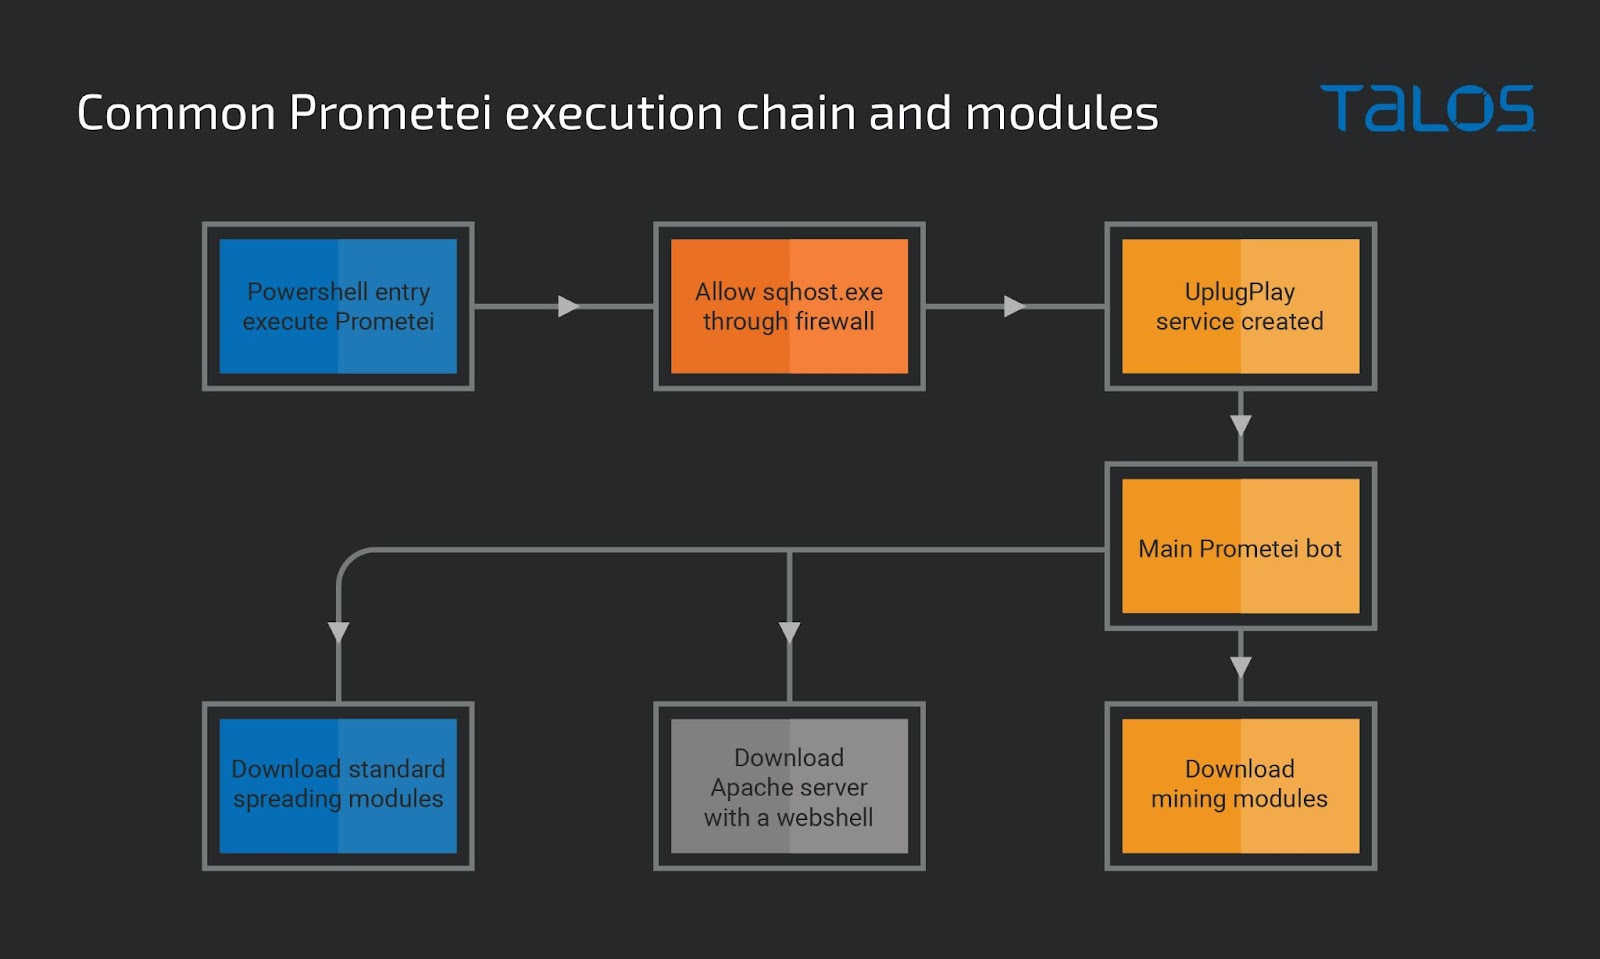
A new version of the Prometei botnet has infected more than 10,000 systems worldwide since November 2022, experts warn. Cisco Talos researchers reported that the Prometei botnet has infected more than 10,000 systems worldwide since November 2022. The crypto-mining botnet has a modular structure and employs multiple techniques to infect systems and evade detection. The Prometei botnet […]