 Pierluigi Paganini
 October 11, 2016
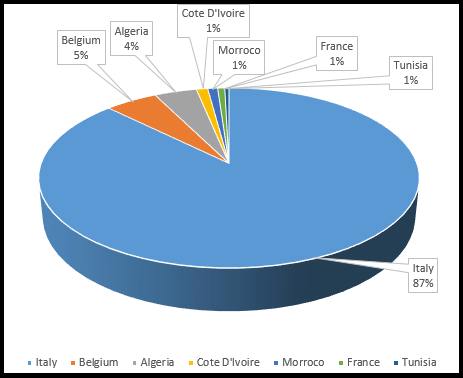
Kaspersky published a report on cyber espionage activities conducted by StrongPity APT that most targeted Italians and Belgians with watering holes attacks. Experts from Kaspersky Lab have published a detailed report on the cyber espionage activities conducted by the StrongPity APT. The group is very sophisticated, its operations leverage on watering holes attacks and malware to target users […]
 Pierluigi Paganini
October 10, 2016
A German nuclear plant suffered a disruptive cyber attack, the news was publicly confirmed by the IAEA Director Yukiya Amano. According to the head of the United Nations nuclear watchdog, the International Atomic Energy Agency (IAEA) Director Yukiya Amano, a nuclear power plant in Germany was hit by a “disruptive” cyber attack two to three […]
 Pierluigi Paganini
October 09, 2016
The users of the free version of the popular Spotify online music service have been served malicious advertisements. Spotify users have been targeted by a malvertising campaign, the malicious advertising served to the victims could automatically open a web browser and redirect victims websites hosting malware. Spotify is a popular online music service that allows its […]
 Pierluigi Paganini
October 07, 2016
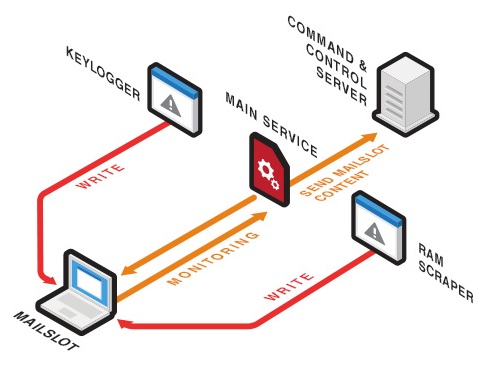
The author of the FastPoS PoS malware issued an update that profoundly changes its behavior, preferring a quick exfiltration activity even if is noisier. Christmas is approaching, and the experts are already at work, including the authors of PoS malware that at that time maximize their profits. The criminal group behind the FastPoS PoS malware have updated […]
 Pierluigi Paganini
October 06, 2016
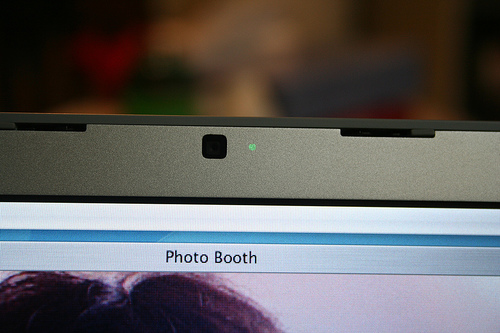
Mac malware could spy on users by piggybacking on webcam sessions started by legitimate applications such as FaceTime, Skype and Google Hangouts. Security experts are worried about the presence of a new Mac malware in the wild that attempt to record video via the built-in webcam. The principal problem for this family of spyware is […]
 Pierluigi Paganini
October 06, 2016
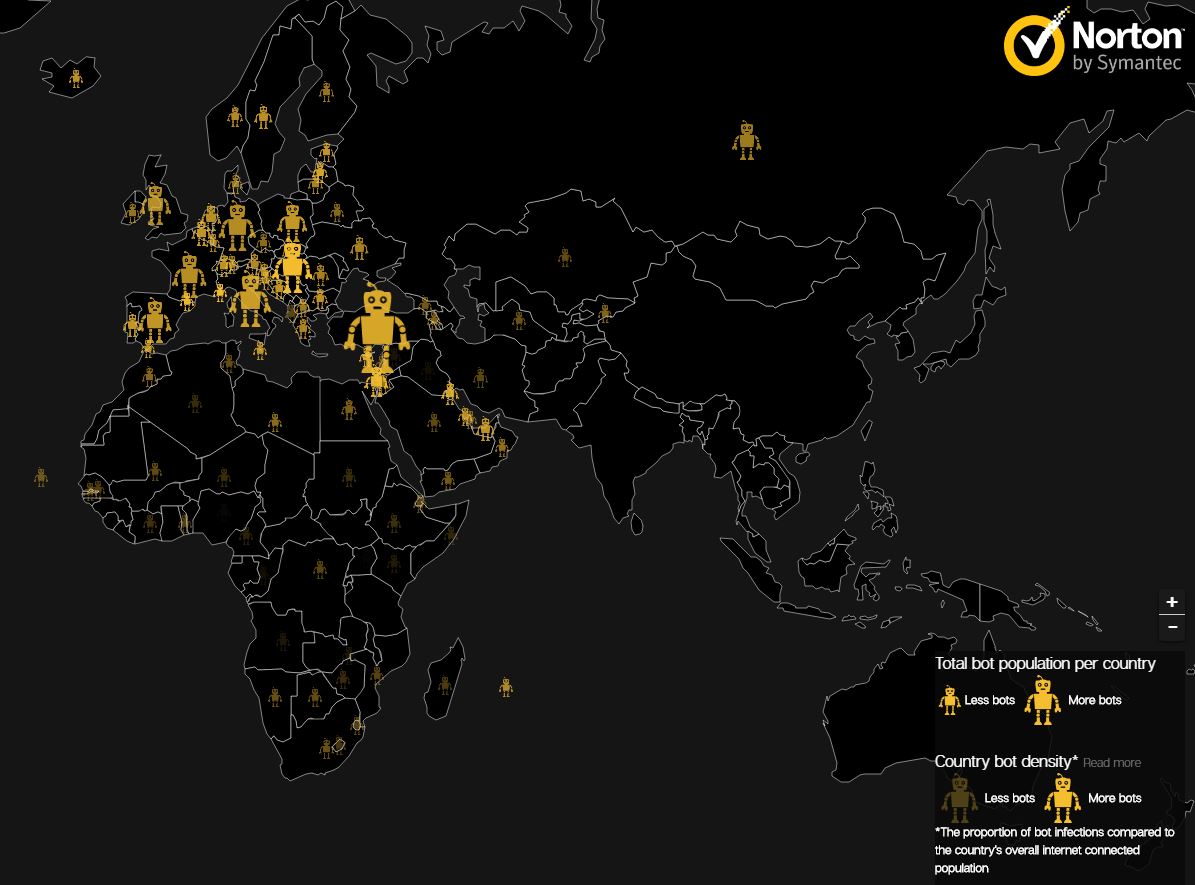
Which are principal cities hostages of malicious botnets? Symantec has tried to reply the difficult questions with an interesting study. It is not a mystery, there is a strict link between cybercrime and Geography. Cyber criminal organization used different tactics and offer different products depending on the country where they operate. Russian criminal communities specialize in […]
 Pierluigi Paganini
October 03, 2016
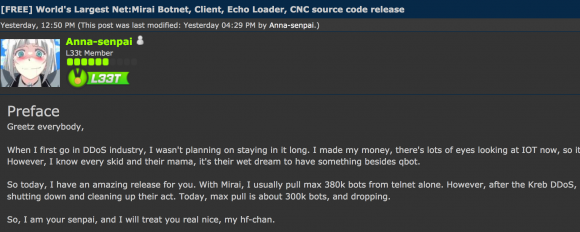
A hacker released the source code of the Mirai malware that powered the record-breaking DDoS attack against the Brian Krebs Website, but … A couple of weeks ago the unknown hackers launched a massive Distributed Denial of Service (DDoS) attack against the website of the popular cyber security investigator Brian Krebs. Further investigation revealed the involvement of […]
 Pierluigi Paganini
October 01, 2016
Malware researcher discovered a Reddit user which is warning of the existence of hacked Steam accounts used to spread a Remote Access Trojan (RAT). This week the popular malware researcher Lawrence Abrams from Bleepingcomputer.com has found a worrisome message on Reddit. The Reddit user with the moniker Haydaddict was warning of the existence of compromised Steam accounts spreading […]
 Pierluigi Paganini
September 29, 2016
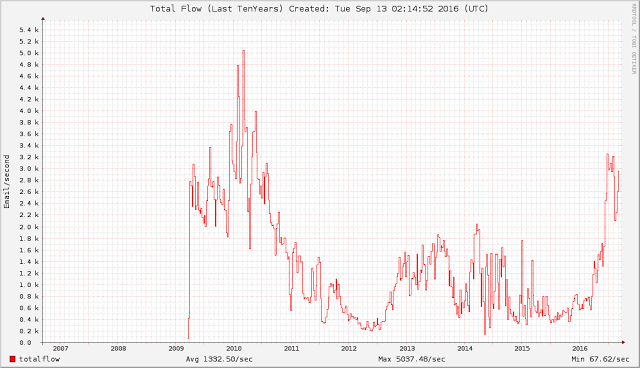
Necurs botnet, the monster is resurrected. Banking Trojans and Ransomware propagated via spam is bring backing the high-volume spam campaign Botnets are like monsters that surface back after some period of inactivity, this time, the monster it the dreaded Necurs botnet. The Necurs Botnet is one of the world’s largest malicious architectures, used to spread the dreaded […]
 Pierluigi Paganini
September 28, 2016
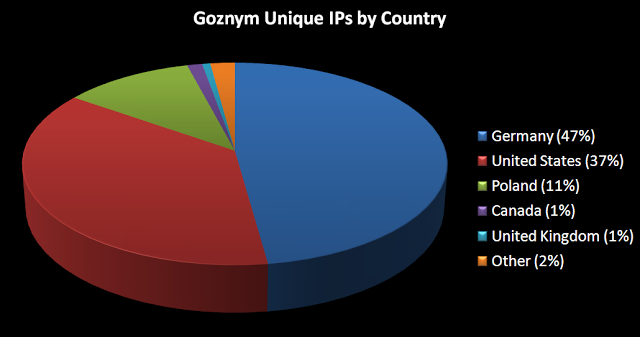
The Talos team published a detailed analysis of the GozNym botnet, it was possible because the experts cracked the DGA algorithm used by the malware. In April 2015, the researchers from the IBM X-Force Research discovered a new banking Trojan dubbed GozNym Trojan that combines best features of Gozi ISFB and Nymaim malware. The GozNym has been seen targeting […]