 Pierluigi Paganini
 January 16, 2016
Once again, the security expert Patrick Wardle has demonstrated how to bypass the Apple Gatekeeper security feature. Once again, a security expert demonstrated how to bypass OS X’s Gatekeeper security feature, and the worst news is that the patch distributed by Apple fixes the problem only temporarily. Apple tried to mitigate the attack method (CVE-2015-7024) with the […]
 Pierluigi Paganini
January 15, 2016
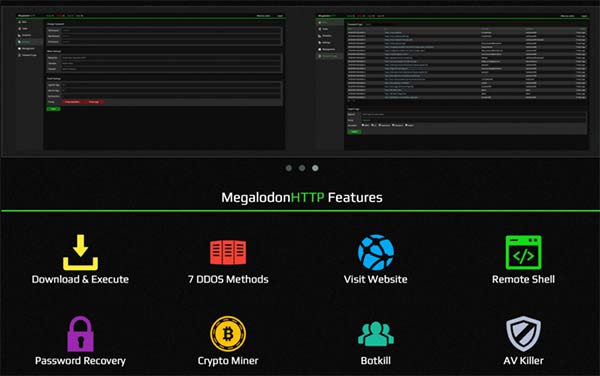
The operators behind the MegalodonHTTP botnet have been arrested in an international joint effort of law enforcement and a private security firm. In December, Norway law enforcement arrested five people accused of running the MegalodonHTTP Remote Access Trojan (RAT) as part of a joint operation between Norway’s Kripos National Criminal Investigation Service and Europol, codenamed “OP […]
 Pierluigi Paganini
January 15, 2016
The Hyatt Hotels Corporation announced a total of 250 of its resorts were compromised last year in a malware-based attack that stole customer payment card information. Hyatt Hotels revealed that 250 of its resorts have been involved in the data breach suffered last year. In December the Hyatt Hotels Corporation issued an official announcement to inform its users that unknown hackers […]
 Pierluigi Paganini
January 14, 2016
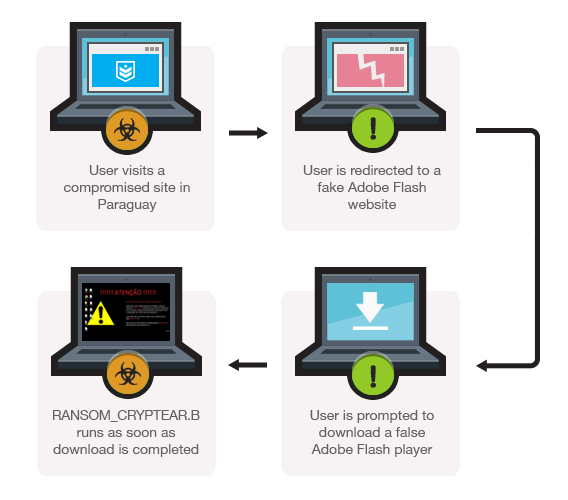
Faulty ransomware derived from an open source ransomware project makes files unrecoverable due to a serious coding error. The story I’m gong to tell you is incredible, a cyber criminal gang has developed a very singular ransomware called RANSOM_CRYPTEAR.B and now I’ll tell you why? According to the experts at TrendMicro, the Ransomware has built starting from […]
 Pierluigi Paganini
January 11, 2016
According to security experts the BlackEnergy malware was a key element of the attack against Ukrainian power grid that caused the power outage. On December 23, the entire Ivano-Frankivsk region in Ukraine suffered a major power outage, according to security experts and the Ukrainian Government the attackers used a destructive varian of the popular BlackEnergy […]
 Pierluigi Paganini
January 08, 2016
The Rovnix Banking Trojan is an aggressive malware that has been used in a new campaign targeting the customers of more than a dozen Japanese banks. Malware experts at IBM’s X-Force have spotted a new strain of the Rovnix malware targeting the Japanese bank customers. The new threat comes from Russia and it is very […]
 Pierluigi Paganini
January 07, 2016
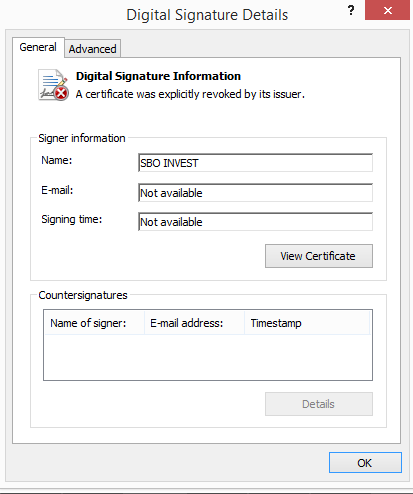
Zscaler ThreatLabZ detected a new infostealer malware family dubbed Spymel that uses stolen certificates to evade detection. In late December, security experts at Zscaler ThreatLabZ detected a new infostealer malware family dubbed Spymel that uses stolen certificates to evade detection. “ThreatLabZ came across yet another malware family where the authors are using compromised digital certificates to evade detection. The malware family in […]
 Pierluigi Paganini
January 07, 2016
Bitdefender has discovered for the third time a flaw in Linux Encryption Ransomware Linux Encoder that exposes the decryption Key used to lock the files. In November 2015, the Russian antivirus firm Doctor Web reported the discovery of a new Linux ransomware dubbed Linux Encoder that was specifically designed to infect Linux systems. The Linux.Encoder1 ransomware encrypts files present […]
 Pierluigi Paganini
January 05, 2016
Hackers cause power outage with the BlackEnergy malware in Ukraine. Is it an Information warfare act? Cyber security of ICS e SCADA systems in the critical infrastructure is essential, these components are a privileged target of cyber criminals and state sponsor hackers. The most popular SCADA attack in the history is the one conducted against control systems […]
 Pierluigi Paganini
January 03, 2016
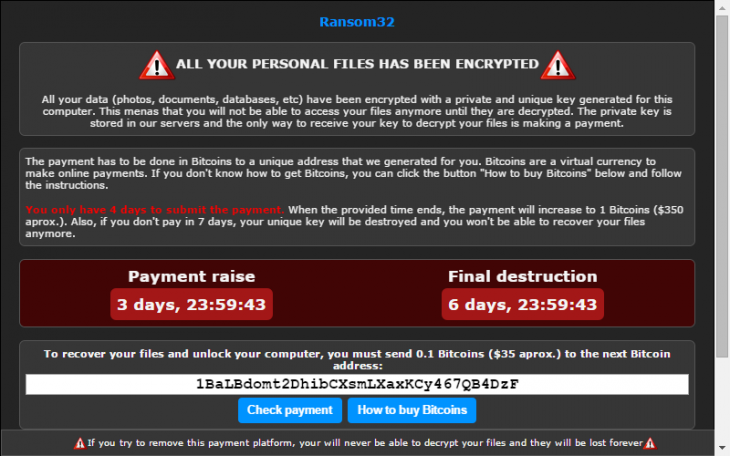
Ransom32 is a new crypto-ransomware variant recently reported, it is the first ransomware variant that has been developed in the JavaScript. Ransom32 is a new crypto-ransomware variant that was first reported on December 29th, 2015, by an infected user on the Bleeping Computer forums. It is the first ransomware variant that has been developed in the […]