 Pierluigi Paganini
 November 23, 2015
According to Kaspersky Lab, bad actors in the Russian underground have stolen more than $790 Million over 3 years, from 2012 to 2015. According to the experts at Kaspersky Lab, Russian criminal rings have stole roughly $790 Million over 3 years (from 2012 to 2015), more than $500 million of that is from victims located outside the […]
 Pierluigi Paganini
November 22, 2015
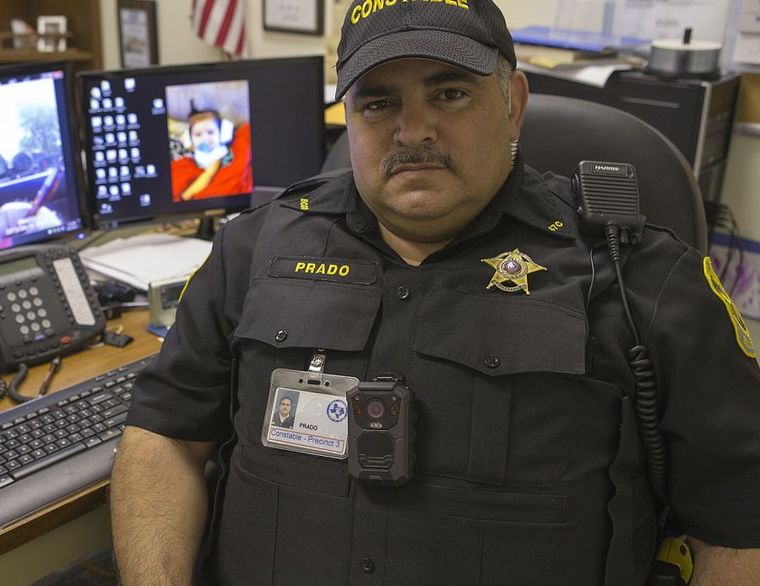
Police body cameras sold by Martel Electronics have been found to be infected with the notorious Conficker worm. Security experts at iPower Technologies while analyzing the body cam designed for police departments manufactured by Martel Electronics, discovered that the cameras were infected. Martel Electronics is US company that design video systems used by law enforcement, including […]
 Pierluigi Paganini
November 20, 2015
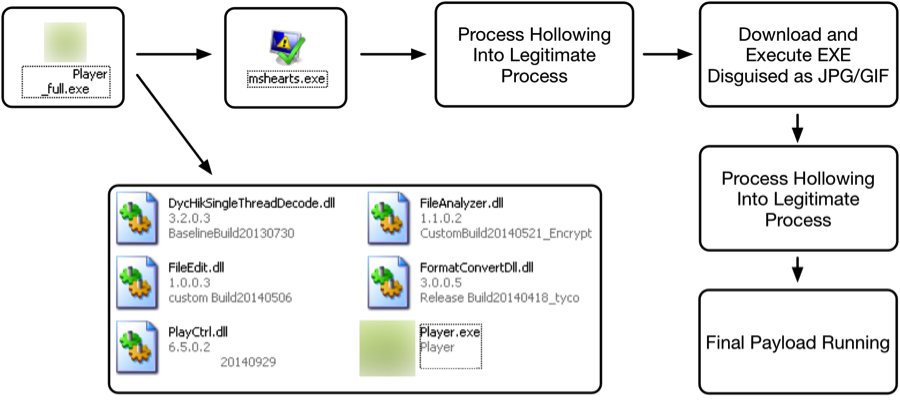
The hacking group that behind the Dark Seoul Operation that hit entities in South Korea in 2013 may be back with new targets. According to the experts at Palo Alto Networks, the hacking group behind the attacks that targeted banks, financial institutions, government websites and news agencies in South Korea is still active. The attacks […]
 Pierluigi Paganini
November 19, 2015
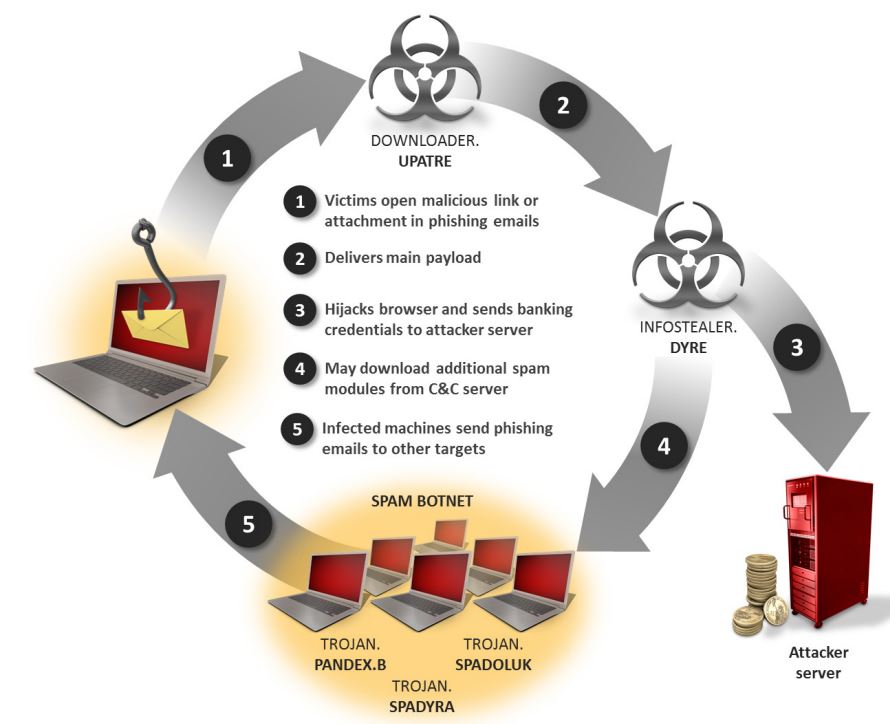
The developers of the Dyre banking Trojan have released a new version of the malware that includes support for Windows 10 and Microsoft Edge. The security firms Heimdal Security and F5 Networks have uncovered a new version of the Dyre (Dyreza) banking Trojan that includes support for Windows 10 and Microsoft Edge. The new variant of Dyre now also […]
 Pierluigi Paganini
November 13, 2015
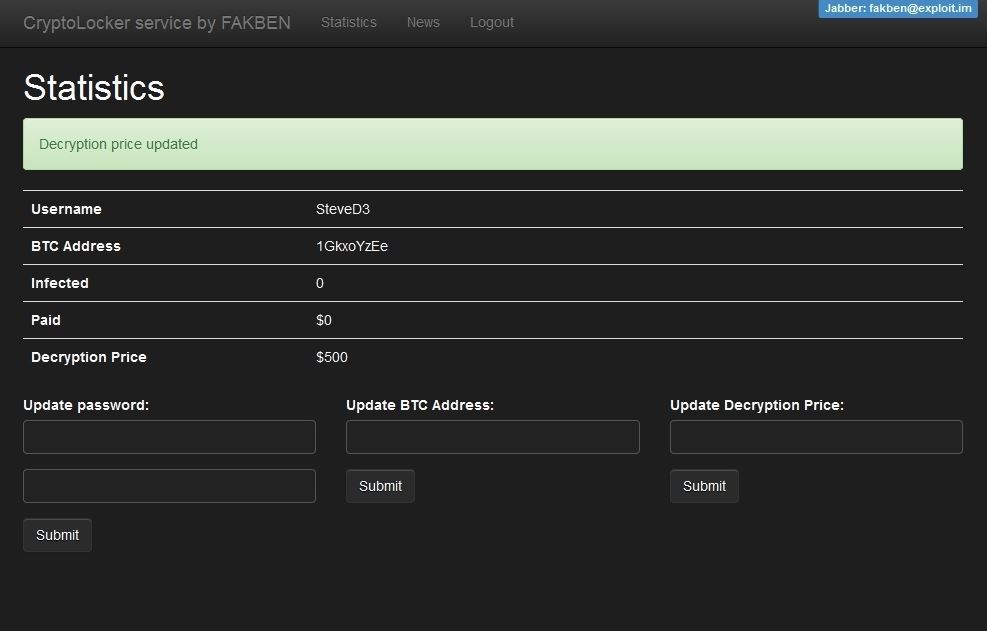
FAKBEN is offering a professional Ransomware-as-a-service that relies on a new CryptoLocker ransomware which can be downloaded through the executable file. Ransomware is probably the most popular category of malicious code in this period, this week we have discussed a malicious code that infected the UK Parliament, an off-line ransomware and a Linux.Encoder1 ransomware revealing the decryption key. News of the […]
 Pierluigi Paganini
November 13, 2015
Researchers at Trustwave have published the analysis of the Cherry Picker threat, a point-of-sale (PoS) malware that went undetected over the years. A point-of-sale (PoS) malware that went largely undetected for the past several years has been analyzed by researchers at Trustwave. Security experts at Trustwave have analyzed an insidious point-of-sale (PoS) malware dubbed Cherry Picker that threat has […]
 Pierluigi Paganini
November 12, 2015
Experts at Cheetah Mobile are warning about Android Tablet pre-loaded with Cloudsota Trojan sold on Amazon and other online stores. Once again electronics equipment from China was offered for sale with pre-installed Trojan. This time, several models of Android tablets sold on Amazon and other online stores are sold with pre-loaded the Cloudsota malware. Cheetah Mobile has […]
 Pierluigi Paganini
November 11, 2015
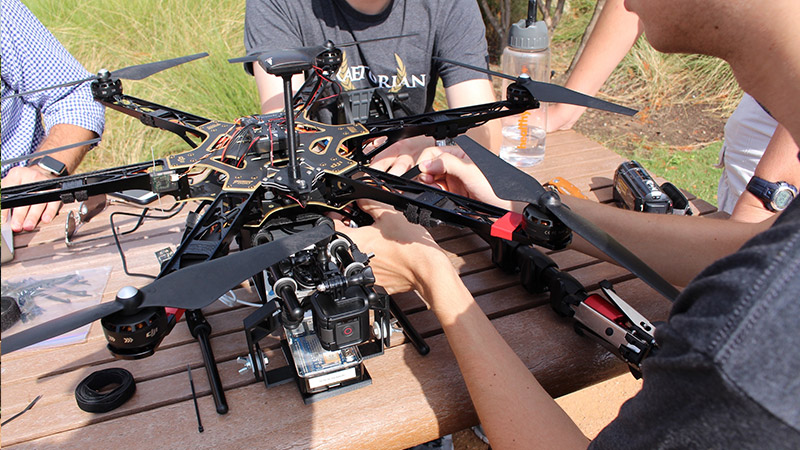
My participation at the World Insight on CCTV discussing the Federal Aviation Administration regulation for the commercial drones. Q1 First of all, the Federal Aviation Administration gave a very compressed timeline. They’re asking a expert panel task force to make registration guideline recommendations by November 20 and these recommendations implemented by mid-December, so that 1 […]
 Pierluigi Paganini
November 09, 2015
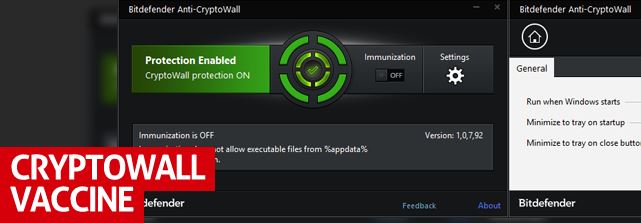
Security experts at Bitdefender speculate that the newborn Cryptowall 4.0 has a Russian origin. The company released a vaccine software. Security experts at Bitdefender seem to have no doubt, the authors of the last variant of the popular Cryptowall ransomware, Cryptowall 4.0 are Russians. The experts came to this conclusion through evidence collected during their investigations, for example, the servers used […]
 Pierluigi Paganini
November 07, 2015
Researchers at Russian antivirus company Doctor Web have discovered a Linux ransomware that has already infected tens of users. Ransomware is a profitable instrument in the criminal ecosystem, security experts discover new variant on a weekly basis. This week the new variant of Cryptowall, the Cryptowall 4.0, appeared in the wild, meanwhile an offline ransomware is targeting […]