


 Pierluigi Paganini
 April 27, 2014
Verizon Data Breach Investigation Report 2014, to better understand how attackers can affect company business, and learn the proper countermeasures. Verizon firm provided the first data related to its annual report titled Verizon’s 2014 Data Breach Investigations Report (DBIR). The document reports specific sections around common incident patterns covering the bad actors, the techniques used, targets hit, timelines […]
 Pierluigi Paganini
April 25, 2014
A user raised an alert on Reddit, on the presence of a malicious Chrome browser extension, on the official store, that is able to steal digital coins. Security experts have recently observed a significant increase for the number of malicious browser extensions, malware authors are exploiting the usage of browser addons to conduct illicit activities. Today […]
 Pierluigi Paganini
April 23, 2014
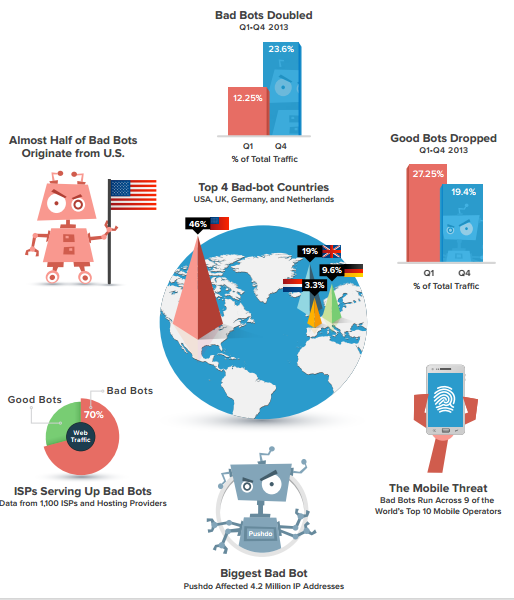
Distil Networks security firm has published an interesting report on the Bad Bot Landscape, it is full of data on the evolution of malicious architecture. Surfing on the Internet I have found The Bad Bot Landscape Report Q1 2014 and interesting study issued by the Distil Networks security firm which provides an interesting analysis of botnet evolution detected by the […]
 Pierluigi Paganini
April 21, 2014
Which are the security improvements in the critical update proposed by criminal ecosystem for P2P Zeus Botnet? Fortinet experts detected and analyzed it. Security experts at Fortinet have uncovered a critical update proposed by criminal ecosystem for P2P Zeus Botnet. The first P2P Zeus variant was uncovered by Trusteer firm a couple of years ago, it was used […]
 Pierluigi Paganini
April 10, 2014
According principal security firms, extortion, ransom and blackmail are pillars of illicit activities, cyber criminals are adapting them to the cyber context. Extrotion is becoming a worrying inclination in the cyber criminal ecosystem, the number of targeted attacks that request money in change of a suspension of the hostilities and to give back to the victims […]
 Pierluigi Paganini
April 08, 2014
Security experts at Symantec observed a new phishing campaign based on a fake voting application used to steal victim’s credentials. Phishing is a very dangerous threat for Internet users, nearby classic techniques new forms of phishing are exploiting new platforms like mobile and social networks. Phishers continuously improve their techniques to be able to harvest […]
 Pierluigi Paganini
April 07, 2014
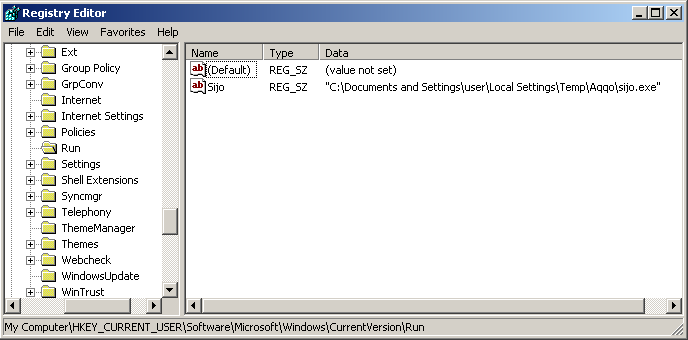
Security researchers at Comodo have detected a new Zeus trojan variant enhanced with digital signature of its source code to avoid detection. The security community is once again menaced by Zeus banking trojan, a new variant of the malicious ZeuS Trojan has been identified by researchers at Comodo AV labs. This instance presents an interesting feature, it is […]
 Pierluigi Paganini
April 04, 2014
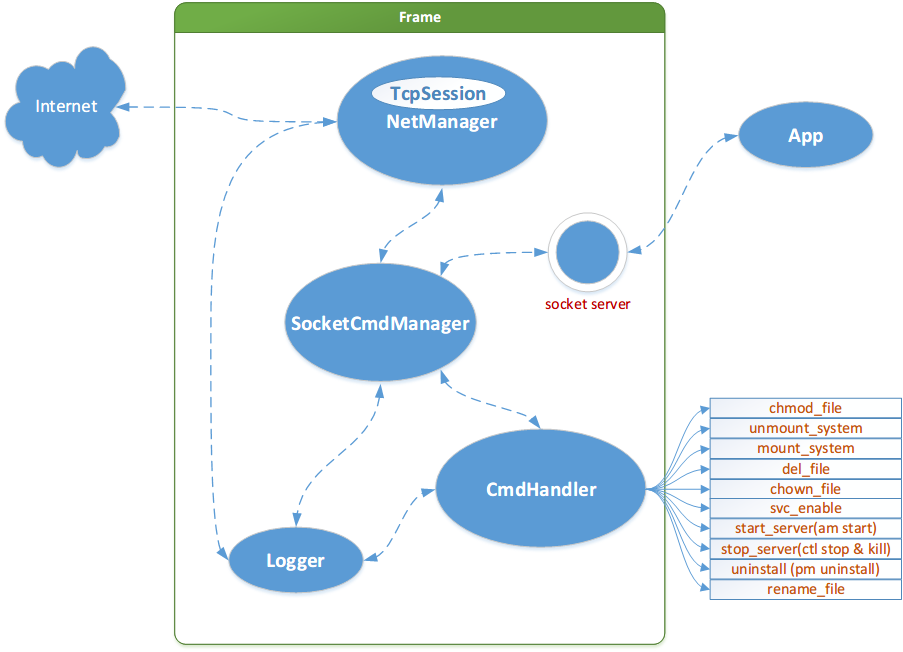
Chinese researchers from “360 Mobile Security” detected Android Oldboot.B malware, until today the most complex bootkit which infected millions of devices. A new sophisticated Android Bootkit has been detected by Chinese Security Researchers from “360 Mobile Security“, its name is Oldboot.B and appears as an evolution of its predecessor Oldboot.A. According the researchers Oldboot.B could be considerable as […]
 Pierluigi Paganini
April 03, 2014
Security Experts at F-Secure discovered a collection of pdf documents, that had references to Ukraine, containing MiniDuke malware samples. MiniDuke is the name of a sophisticated cyber espionage campaign discovered more than one year ago by experts at Kaspersky Lab and Hungary’s Laboratory of Cryptography and System Security (CrySyS). The malicious code was used by unknown hackers to […]
 Pierluigi Paganini
April 02, 2014
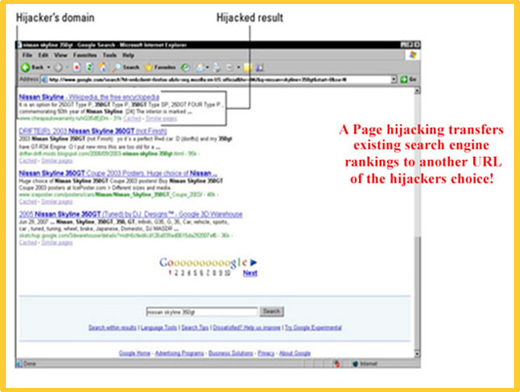
F-Secure has identified a malware dubbed Coremex that takes advantage of plugin functionality provided by browsers to hijack search engine results. Search engine are a strategic component in the successful execution of any attacks, we saw in the past Black SEO campaigns conducted with the primary intent to provide results that help the attackers to […]







