


 Pierluigi Paganini
 February 18, 2014
Security expert Dancho Danchev profiled hacking for hire services offered in the underground, providing an indication of their prices. In the past we have already analyzed the diffusion in the underground of hacking for hire services, a term coined to define the sale of hacking services made by cyber criminals for a limited period of time. Surfing […]
 Pierluigi Paganini
February 16, 2014
Hold Security reported it has discovered a list of credentials for close to 7,800 FTP servers being circulated in cybercrime forums in the Deep Web. FTP servers are considered a privileged target for cyber criminals, hackers can exploit them for example to spread malware infecting webservers that rely on FTP applications for updates. The Hold Security firm […]
 Pierluigi Paganini
February 16, 2014
PandaLabs has found at least four free apps in the official Google Play store that are packaged with a premium SMS scam. Already 300000 mobile infected. PandaLabs security firm has identified malicious Android apps available on Google Play that can sign up users for premium SMS subscription services without user knowledge. The malware has infected at least 300,000 Android devices, although the number of […]
 Pierluigi Paganini
February 09, 2014
Two security researchers have designed a kit to hack a car made up of a tiny device, smaller than your Smartphone, they called it CAN Hacking Tools (CHT) Imagine that a hacker wants to hijack your car hack remotely, the thought is scaring but it’s reality! The high level of technological penetration into the objects that surround […]
 Pierluigi Paganini
February 08, 2014
Security experts at AppRiver detected a traffic spam spike linked to a new malware Campaign Targeting customers of Bank of America. Bank of America is being targeted by a new malicious campaign, cybercriminals are spreading a stealthy malicious financial malware to hit the clients of the financial institution. Security experts at AppRiver recently detected and blocked a set of […]
 Pierluigi Paganini
February 08, 2014
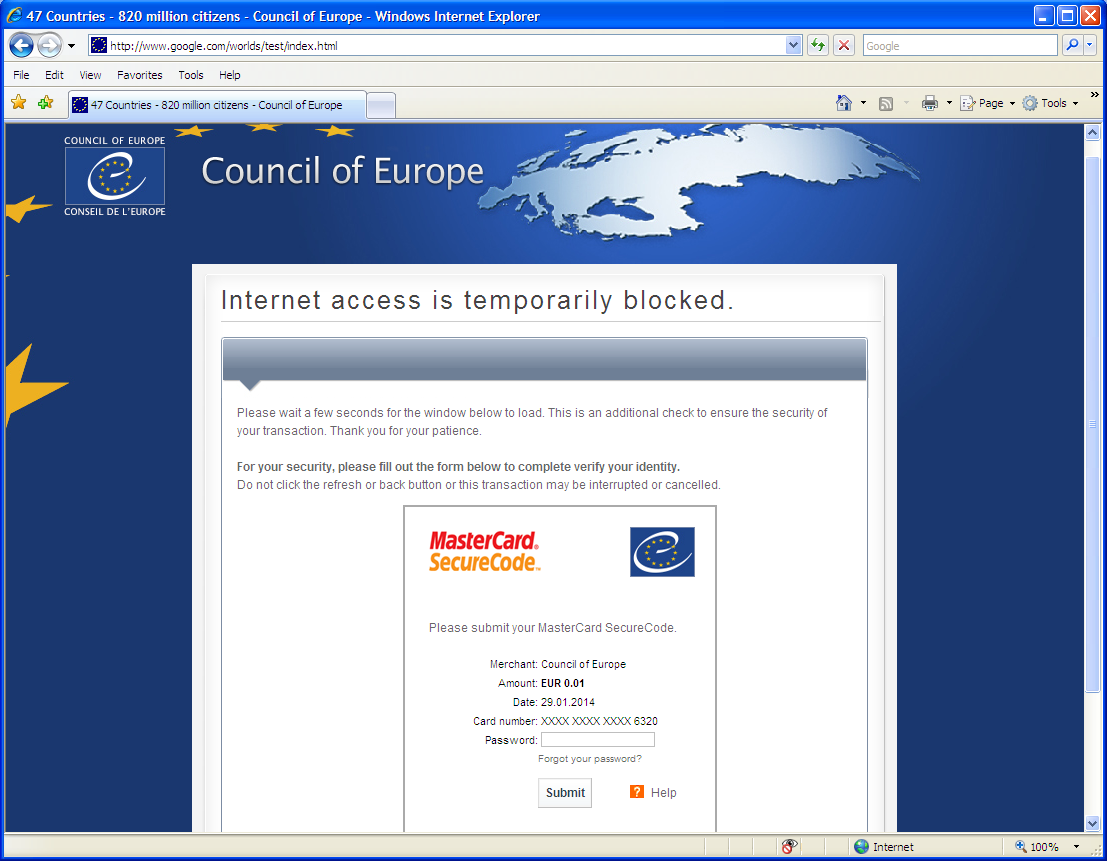
Emsisoft has detected a new variant of malware dubbed Linkup (Trojan-Ransom.Win32.Linkup), it is ransomware that blocks Internet access and mines Bitcoin. Emsisoft has detected a new variant of malware dubbed Linkup (Trojan-Ransom.Win32.Linkup), it is ransomware presenting a singular behavior. Usually a ransomware locks victim’s computer or encrypts files requesting the payment of a ransom to unlock it, but […]
 Pierluigi Paganini
February 04, 2014
Adobe has released security updates for Adobe Flash Player to fix a critical vulnerability exploited in a sophisticated cyber espionage campaign. Adobe has released today a new patch for the Flash Player product to fix a vulnerability which is currently being exploited. The vulnerability (CVE-2014-0497), allows an attacker to remotely take control of the targeted system […]
 Pierluigi Paganini
February 04, 2014
Security experts at Malcovery firm have detected a new Zeus variant bypassing the security traditional defenses with the usage of encryption. Zeus malware is hard to die, the availability of its source code in the wild caused periodically the born of a new variant, even more resistant and sophisticated. Over the years, we saw variants […]
 Pierluigi Paganini
January 30, 2014
Russian company Doctor Web detected Android.Oldboot, an Android Trojan that resides in the memory of infected devices and starts on OS bootstrapping. The Russian security firm Doctor Web has detected the first mass distributed Android bootkit malware dubbed Android.Oldboot, its principal capability is to re-infect the Smartphone after reboot, even if all its components are […]
 Pierluigi Paganini
January 25, 2014
Symantec experts recently came across a Windows malicious code that attempts to infect connected Android devices serving an Android malware. Researchers at Symantec antivirus firm have discovered a malicious code that is able to infect Android mobile device with a banking malware during synchronization. The Android malware that was designed to hit Windows user could compromise user’s Smartphone during file […]







