 Pierluigi Paganini
 April 27, 2017
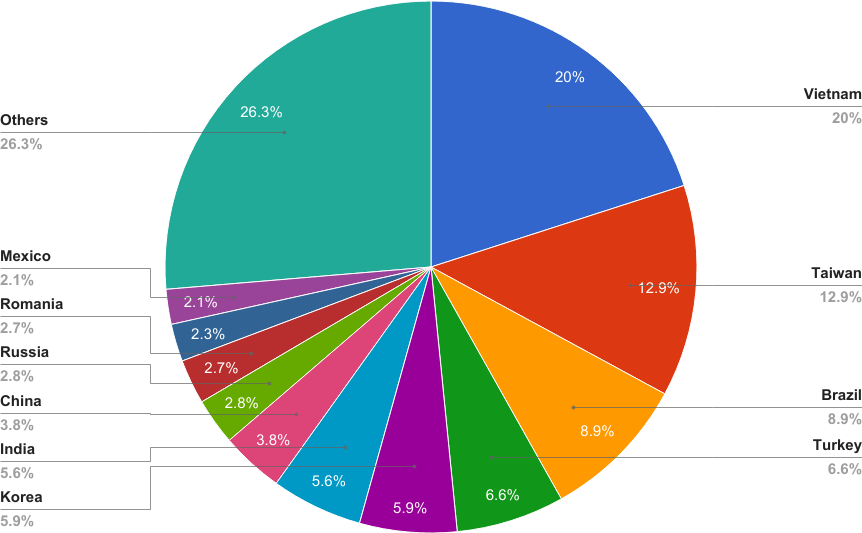
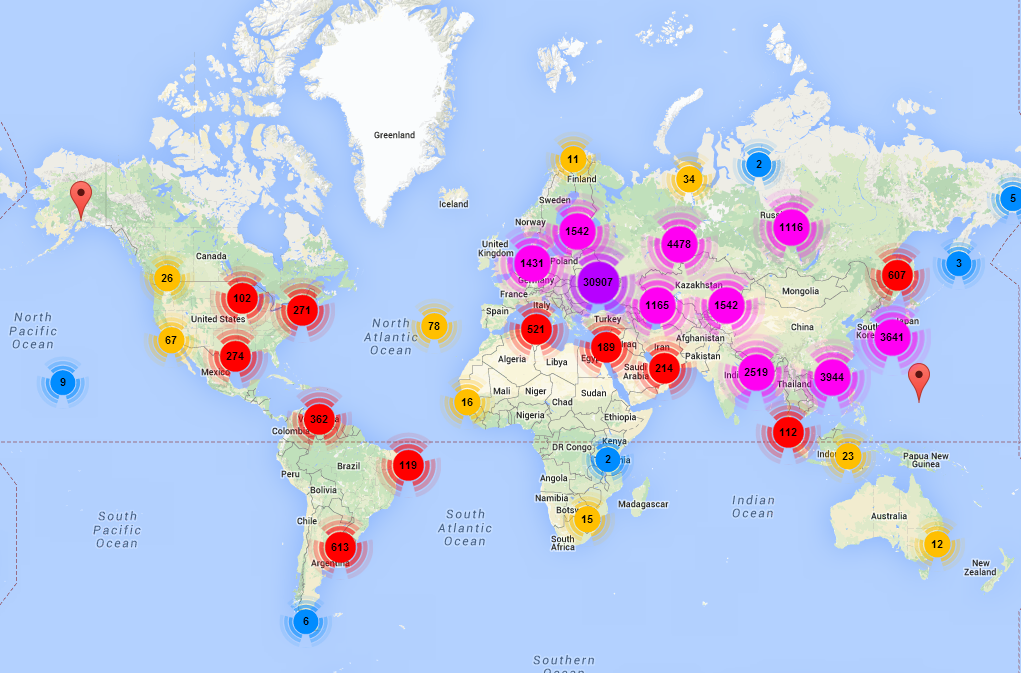
The mysterious Hajime Botnet continues to grow and reached 300,000 IoT Devices, the author also implemented a new attack method. Recently experts from Symantec spotted a new IoT botnet dubbed Hajime that is spreading quickly in the last months, mostly in Brazil and Iran. The Hajime malware was first spotted in October 2016, it implements the same mechanism […]
 Pierluigi Paganini
April 26, 2017
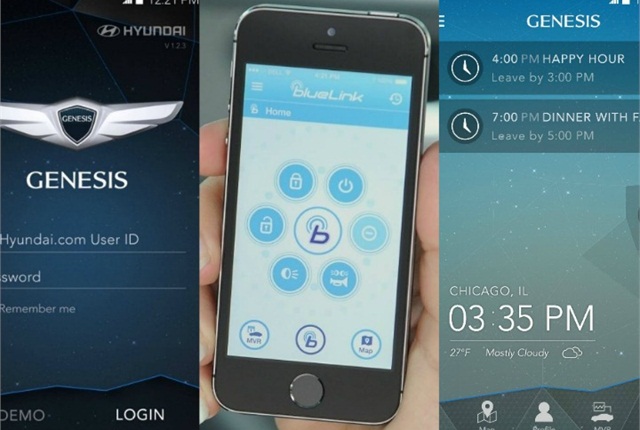
Security vulnerabilities in the Hyundai Blue Link mobile apps allowed hackers to steal vehicles, the car maker fixed them. Security vulnerabilities in the Hyundai Blue Link mobile apps could be exploited by hackers to locate, unlock and start vehicles of the carmaker. The Blue Link application is available for both iOS and Android mobile OSs, it was […]
 Pierluigi Paganini
April 24, 2017
The Russian hacker Petr Levashov has been indicted in connection with the infamous Kelihos Botnet that was recently dismantled. It isn’t a good period for Russian cyber criminals, last week Roman Valeryevich Seleznev, aka “Track2”, was sentenced to 27 years in prison, he was convicted of causing $170 million in damage by hacking into point-of-sale systems. Today the […]
 Pierluigi Paganini
April 24, 2017
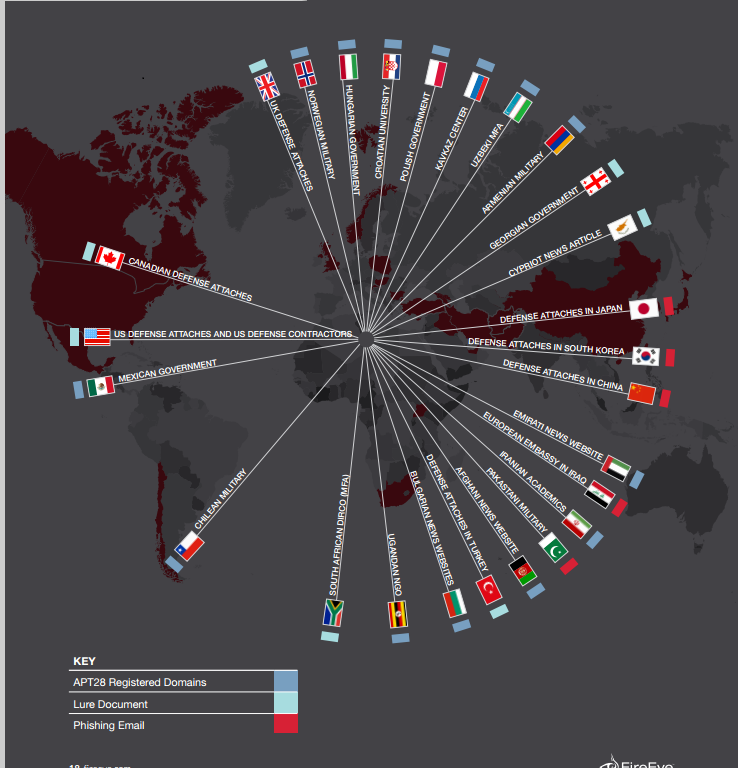
Denmark on Monday denounced Russia after the publication of a report that accused Russian APT28 of hacking the defense ministry’s email accounts. Today the Danish Government officially blamed Russia for cyber attacks against its Defense Ministry. Denmark denounced a cyber intrusion in several Defense Ministry’s email accounts. The accusation comes after the publishing by the Centre for Cyber […]
 Pierluigi Paganini
April 23, 2017
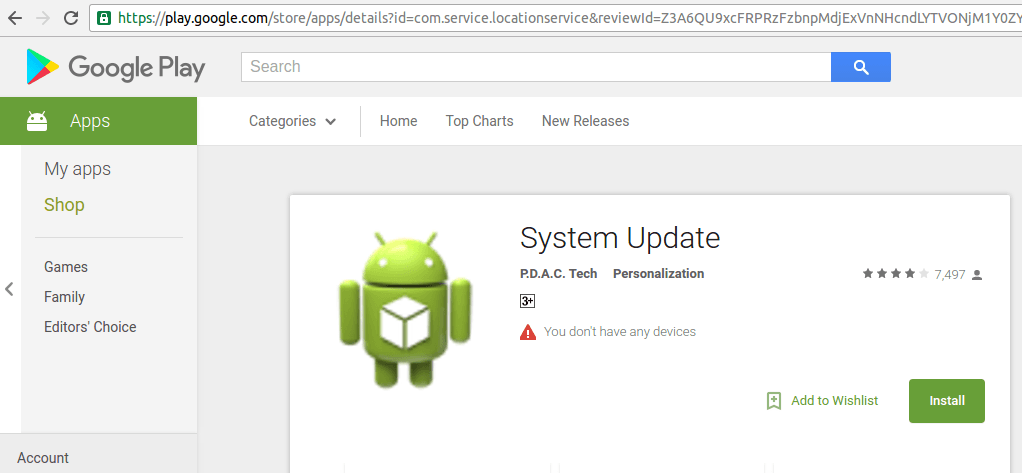
Millions of users looking to get software updates have downloaded an app hiding a spyware called SMSVova through the official Google Play store. Bad news for millions of Android users looking to get software updates, they have been tricked into downloading a spyware called SMSVova through the official Google Play store. Experts at Zscaler discovered […]
 Pierluigi Paganini
April 16, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. First of all, let me inform you that at the #infosec16 SecurityAffairs was awarded as The Best European Personal Security Blog http://securityaffairs.co/wordpress/48202/breaking-news/securityaffairs-best-european-personal-security-blog.html · Millions of mobile phones and laptops potentially exposed to attack leveraging baseband zero-days · ATMitch – […]
 Pierluigi Paganini
April 15, 2017
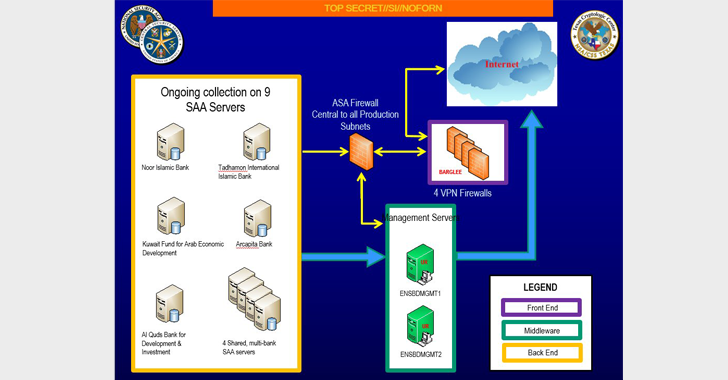
Microsoft determined that most of the flaws exploited by the tools in the dump released by Shadow Brokers yesterday were patched in March. Yesterday the Shadow Brokers hacker group has released a new portion of the alleged archive of the NSA containing hacking tools and exploits. The group released a 117.9 MB encrypted dump containing […]
 Pierluigi Paganini
April 13, 2017
A group of researchers has demonstrated that attackers can steal PINs and Passwords capturing data from smartphone sensors. Modern mobile devices are full of sensors (i.e. GPS, Camera, microphone, accelerometer, magnetometer, proximity, gyroscope, pedometer, and NFC) that could be exploited by hackers to gather data about owner’s activities? A group of researchers from Newcastle University demonstrated that […]
 Pierluigi Paganini
April 12, 2017
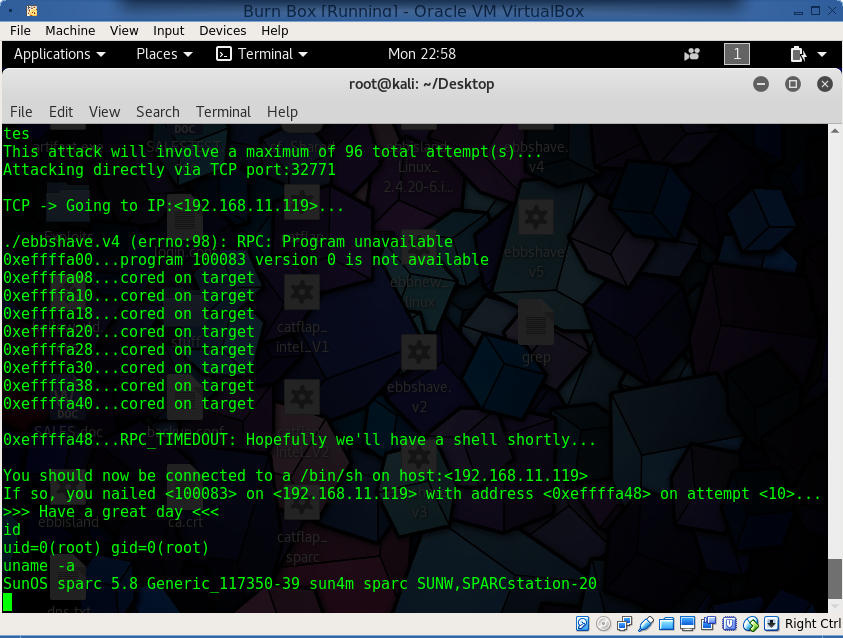
The security expert Matthew Hickey has discovered two tools dubbed EXTREMEPARR and EBBISLAND which were specifically designed to target Solaris systems. After the mysterious Shadow Brokers group has leaked the archive containing the stolen NSA hacking tools and exploits, security experts started analyzing the huge trove of data. Experts discovered that NSA operators developed an attack […]
Pierluigi Paganini
April 09, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. First of all, let me inform you that at the #infosec16 SecurityAffairs was awarded as The Best European Personal Security Blog http://securityaffairs.co/wordpress/48202/breaking-news/securityaffairs-best-european-personal-security-blog.html · Android Chrysaor spyware went undetected for years · UEFI Vulnerabilities allow to fully compromise Gigabyte Mini […]

Security / September 15, 2026