 Pierluigi Paganini
 July 24, 2025
A new stealth backdoor has been discovered in the WordPress mu-plugins folder, granting attackers persistent access and control over compromised sites. Sucuri researchers found a stealthy backdoor hidden in WordPress’s “mu-plugins” folder. These plugins auto-run and allow attackers to stay hidden in admin, and maintain persistence. “must-use plugins” are special WordPress plugins that cannot be […]
 Pierluigi Paganini
April 01, 2025
Sucuri researchers spotted threat actors deploying WordPress malware in the mu-plugins directory to evade security checks. In February, Sucuri warned of threat actors exploiting WordPress mu-plugins, which auto-load without activation, to maintain persistence and evade detection by hiding backdoors in the plugin directory. “Unlike regular plugins, must-use plugins are automatically loaded on every page load, […]
 Pierluigi Paganini
January 13, 2025
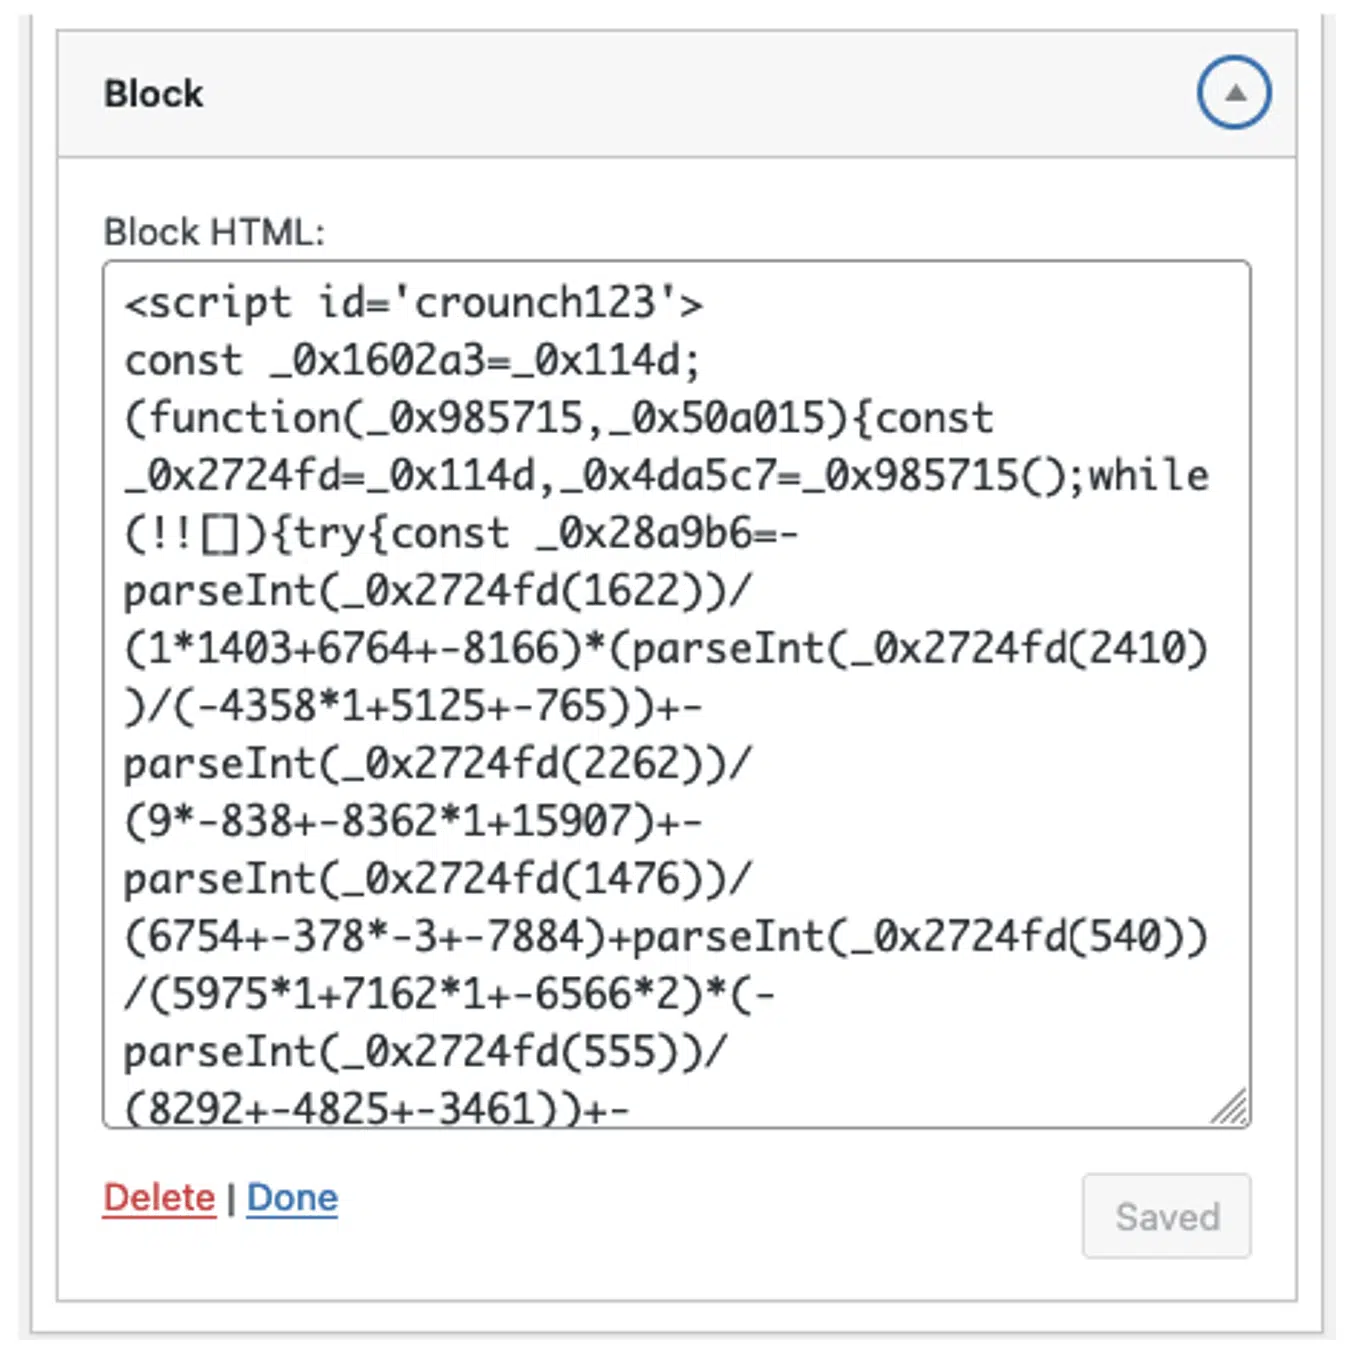
Stealthy credit card skimmer targets WordPress e-commerce sites, injecting malicious JavaScript into CMS database tables to evade detection. Sucuri researchers warn of a stealthy credit card skimmer campaign targeting WordPress e-commerce sites by injecting malicious JavaScript into CMS database tables. The attackers hide the malicious code in the WordPress wp_options table, injecting obfuscated JavaScript into […]
Pierluigi Paganini
November 18, 2024
A Really Simple Security plugin flaw affects 4M+ sites, allowing attackers full admin access. It’s one of the most critical WordPress vulnerabilities ever. Wordfence researchers warn of a vulnerability, tracked as CVE-2024-10924 (CVSS Score of 9.8), in the Really Simple Security plugin that affects 4M+ sites. The Really Simple Security plugin, formerly Really Simple SSL, is […]
Pierluigi Paganini
October 05, 2024
A high-severity flaw in the WordPress LiteSpeed Cache plugin could allow attackers to execute arbitrary JavaScript code under certain conditions. A high-severity security flaw, tracked as CVE-2024-47374 (CVSS score 7.2), in the LiteSpeed Cache plugin for WordPress could allow attackers to execute arbitrary JavaScript. The vulnerability is a stored cross-site scripting (XSS) issue impacting versions […]
Pierluigi Paganini
September 07, 2024
A critical flaw in the LiteSpeed Cache plugin for WordPress could allow unauthenticated users to take control of arbitrary accounts. The LiteSpeed Cache plugin is a popular caching plugin for WordPress that accounts for over 5 million active installations. The plugin offers site acceleration through server-level caching and various optimization features. The LiteSpeed Cache plugin […]
Pierluigi Paganini
August 27, 2024
A critical flaw in the WPML WordPress plugin, which is installed on 1 million websites, could allow potential compromise of affected sites. The WPML Multilingual CMS Plugin for WordPress is installed on over 1 million sites. An authenticated (Contributor+) Remote Code Execution (RCE) vulnerability, tracked CVE-2024-6386 (CVSS score of 9.9), in WPML Plugin potentially allows […]
Pierluigi Paganini
May 08, 2024
Threat actors are exploiting a high-severity vulnerability in the LiteSpeed Cache plugin for WordPress to take over web sites. WPScan researchers reported that threat actors are exploiting a high-severity vulnerability in LiteSpeed Cache plugin for WordPress. LiteSpeed Cache for WordPress (LSCWP) is an all-in-one site acceleration plugin, featuring an exclusive server-level cache and a collection […]
Pierluigi Paganini
April 26, 2024
A critical vulnerability in the WordPress Automatic plugin is being exploited to inject backdoors and web shells into websites WordPress security scanner WPScan warns that threat actors are exploiting a critical SQL injection vulnerability in the plugin WordPress Automatic to inject malware into websites. The premium plugin “Automatic” developed by ValvePress enables users to automatically […]
 Pierluigi Paganini
April 02, 2024
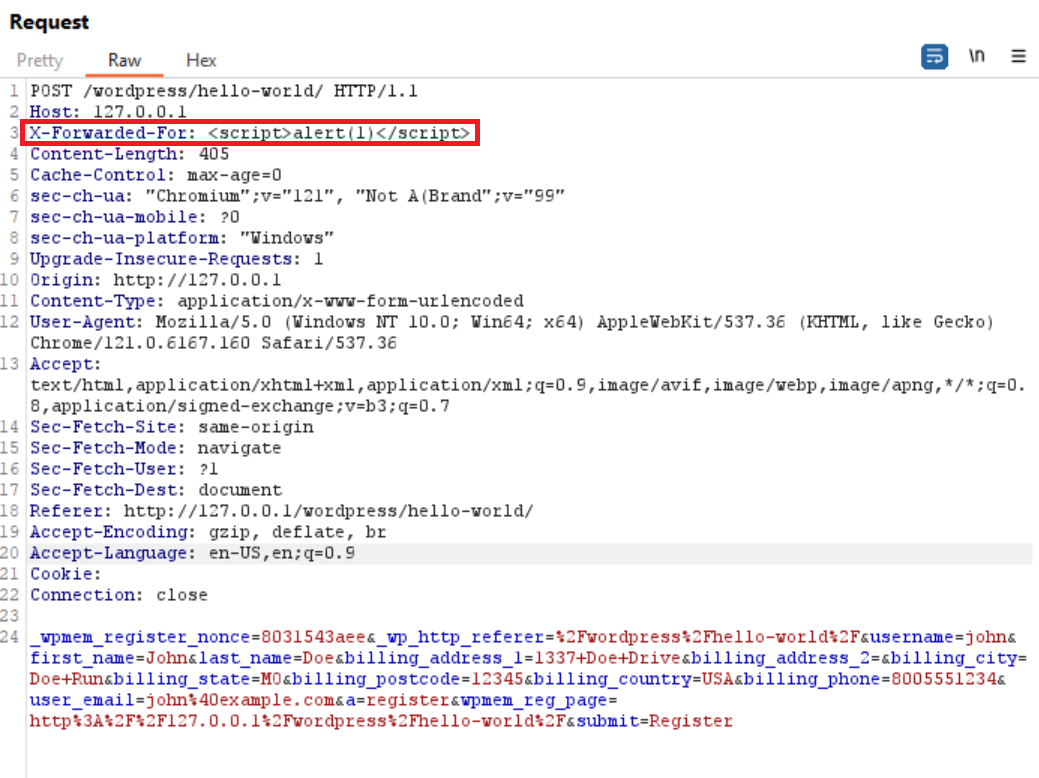
A cross-site scripting vulnerability (XXS) in the WordPress WP-Members Membership plugin can lead to malicious script injection. Researchers from Defiant’s Wordfence research team disclosed a cross-site scripting vulnerability (XXS) in the WordPress WP-Members Membership plugin that can lead to malicious script injection. The Unauthenticated Stored Cross-Site Scripting vulnerability was reported to Wordfence by the WordPress […]