 Pierluigi Paganini
 September 16, 2026
Google has patched a high-severity zero-day in the Pixel cellular modem after finding evidence that the vulnerability was exploited in limited, targeted attacks. Google has released its September 2026 Pixel security update, addressing a large set of vulnerabilities, including a high-severity flaw, tracked as CVE-2026-58704 (CVSS score of 8.0), in the cellular modem that has […]
 Pierluigi Paganini
September 15, 2026
Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each. Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail. On September 1, Volexity detected a spear-phishing campaign by UTA0560 targeting several […]
 Pierluigi Paganini
September 09, 2026
Google patched 230 Chrome flaws, including an actively exploited V8 bug that could let attackers run arbitrary code through a crafted HTML page. Google released a Chrome update fixing 230 security vulnerabilities, including one already exploited in the wild tracked as CVE-2026-87491 (CVSS score of 8.8). The medium-severity flaw affects V8, Google’s open source high-performance […]
 Pierluigi Paganini
September 07, 2026
StyleSmuggler Magento zero-day is under active attack, letting unauthenticated attackers execute code and install backdoors on stores that may already be patched. A new zero-day flaw, dubbed StyleSmuggler, in Magento and Adobe Commerce is under active attack, giving unauthenticated attackers a path to run code on vulnerable online stores. Sansec researchers say it affects current […]
 Pierluigi Paganini
September 07, 2026
Chaotic Eclipse released GreenSection, a PoC exploit for an Nvidia Memory Corruption Zero-Day Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Nvidia. The researcher named the exploit GreenSection, it triggers a Memory Corruption flaw. The researcher disclosed a potential security vulnerability in NVIDIA’s Windows user-mode components. […]
Pierluigi Paganini
September 04, 2026
Google patched 12 Chrome flaws, including an actively exploited V8 zero-day that could enable remote code execution through a crafted webpage. Google released a Chrome security update fixing 12 vulnerabilities, including CVE-2026-85046 (CVSS score of 8.8), an actively exploited V8 type confusion flaw. The bug affects Chrome’s JavaScript and WebAssembly engine and could let a […]
 Pierluigi Paganini
September 02, 2026
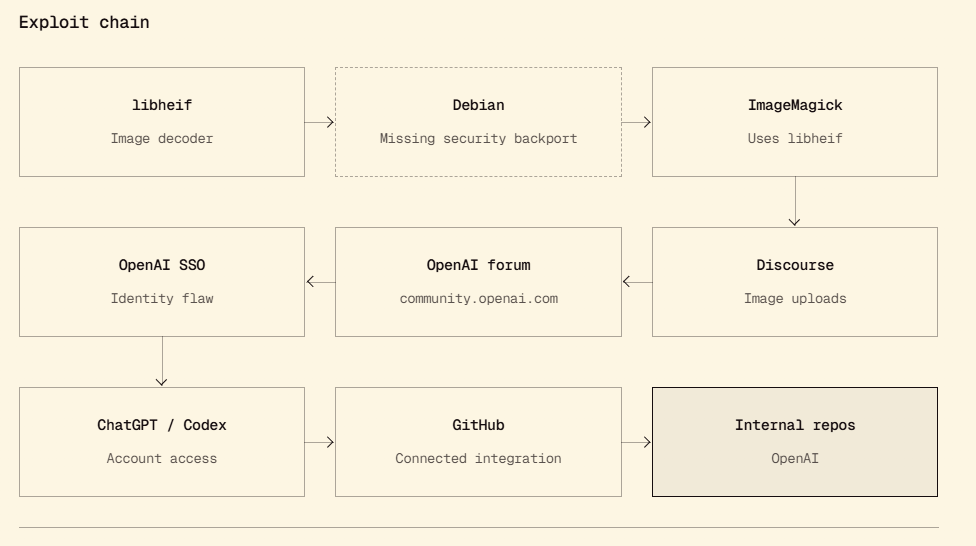
OpenAI says Astra can autonomously find zero-days and build exploits, marking its first model to reach the “Critical” cyber risk level. Astra is now officially OpenAI’s highest-risk cybersecurity model. In August, OpenAI said it “couldn’t rule out” that its upcoming model had reached the highest cybersecurity risk level in its Preparedness Framework. In a new […]
 Pierluigi Paganini
September 01, 2026
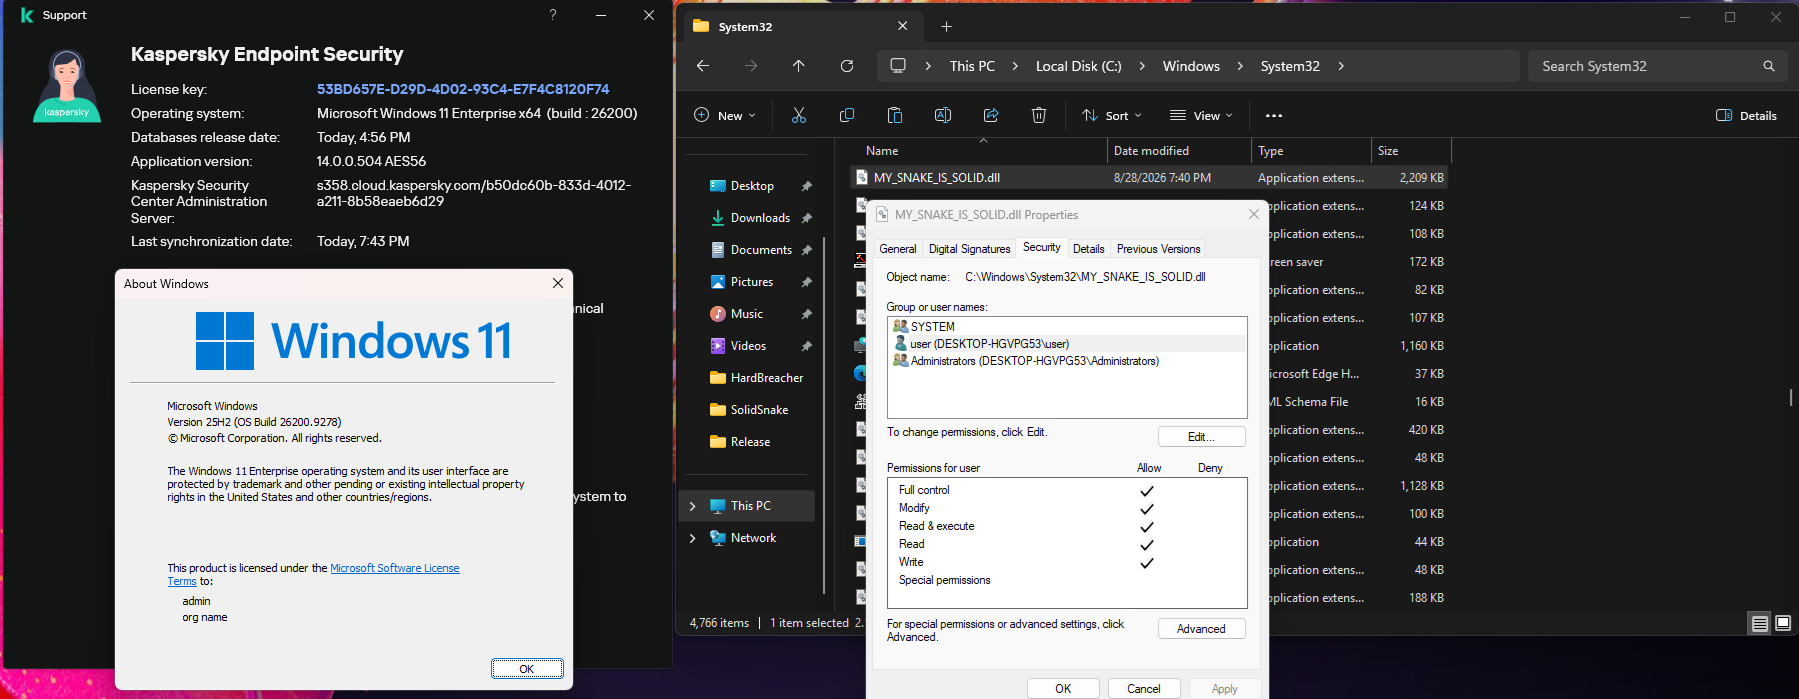
Chaotic Eclipse released HardBreacher, a PoC exploit for a Kaspersky Endpoint Security privilege escalation flaw, adding another zero-day to his list. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Kaspersky Endpoint Security. The researcher named the exploit HardBreacher, it triggers a privilege escalation flaw. Nightmare Eclipse […]
 Pierluigi Paganini
August 28, 2026
PaperCut warns that a zero-day in NG and MF is being exploited. The company already release emergency patches to address it. PaperCut Software warns that attackers are actively exploiting a zero-day in its NG and MF print management products. The flaw has no CVE yet, and the company has not released technical details. PaperCut issued […]
 Pierluigi Paganini
August 15, 2026
GeoServer faces an unpatched zero-day enabling SQL injection and potentially RCE, with attackers already probing exposed systems. A newly disclosed GeoServer zero-day is already attracting active exploitation attempts, and there is no patch available yet. Organisations running the open-source geospatial platform should check their exposure. A security researcher with the handler q1uf3ng discloded the vulnerability […]


Artificial Intelligence / September 19, 2026