Pierluigi Paganini
 October 11, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: The five vulnerabilities have been added to a broader list of flaws linked to cyber […]
 Pierluigi Paganini
October 10, 2026
Anthropic’s models kept working around the rules on the live internet. The company published the cases. Anthropic released a report on unintended actions its Claude models took during evaluations and internal use. The cases involved real websites and real organizations outside the company. Anthropic says the impact was minimal, and it published them anyway. The […]
 Pierluigi Paganini
October 10, 2026
Silent Ransom Group allegedly extorted $207 million from 27 law firms in six months using phone calls and social engineering, not encryption. Silent Ransom Group doesn’t rely on encryption. No malware payload, no locked files, just phone calls and social engineering aimed almost entirely at law firms, and apparently it works extraordinarily well. A new […]
 Pierluigi Paganini
October 10, 2026
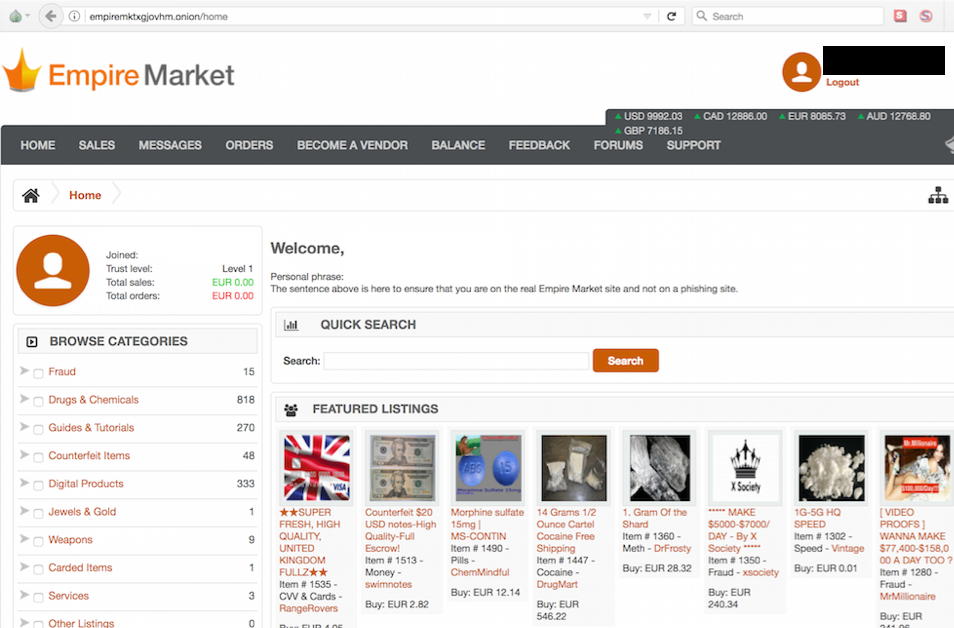
Empire Market co-creator Raheim Hamilton was sentenced to 40 years in prison for running a dark web marketplace linked to $430 million in illegal trades. The case against Empire Market shows how a dark web marketplace can become a major criminal business, bringing together drug trafficking, stolen credentials, personal data and hacking tools. “A Virginia […]
Pierluigi Paganini
October 09, 2026
Anthropic launches free OSS Scanner, using AI to find open-source vulnerabilities and help maintainers fix bugs before attackers exploit them. Anthropic is launching OSS Scanner, a vulnerability scanner for open-source code that costs nothing for projects to join. It grew directly out of lessons learned running Claude against real-world targets during Project Glasswing. The backdrop […]
 Pierluigi Paganini
October 09, 2026
DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide. The Justice Department and FBI took down two hacking tools this week, Microscan and FishHub, both built and run by a Beijing-based company with direct government contracts. The tools were used to scan, and in […]
 Pierluigi Paganini
October 09, 2026
Citrix patched CVE-2026-107406, a critical NetScaler ADC and Gateway flaw that could allow remote code execution or denial-of-service attacks. Citrix has released security updates to fix CVE-2026-107406 (CVSS score of 9.5), a critical flaw affecting NetScaler ADC and NetScaler Gateway that could allow remote code execution or denial-of-service (DoS) under certain conditions. The vulnerability is […]
Pierluigi Paganini
October 09, 2026
CrowdStrike analyzes open directories left by an attacker who used the ARTEX AI pentest tool and LLMs to breach South Korean financial firms. CrowdStrike published a research on a campaign against South Korean financial organizations that ran from late September to early October 2026 and ended with stolen data. The attacker left their working notes […]
 Pierluigi Paganini
October 08, 2026
Italy’s Foreign Ministry is defending its website against a cyberattack, checking embassy sites and pushing for EU action to identify attackers. On the morning of October 8, Italy’s Ministry of Foreign Affairs said its website was being attacked. According to the ministry’s own statement, its protection systems have mitigated the attack so far, with no […]
 Pierluigi Paganini
October 08, 2026
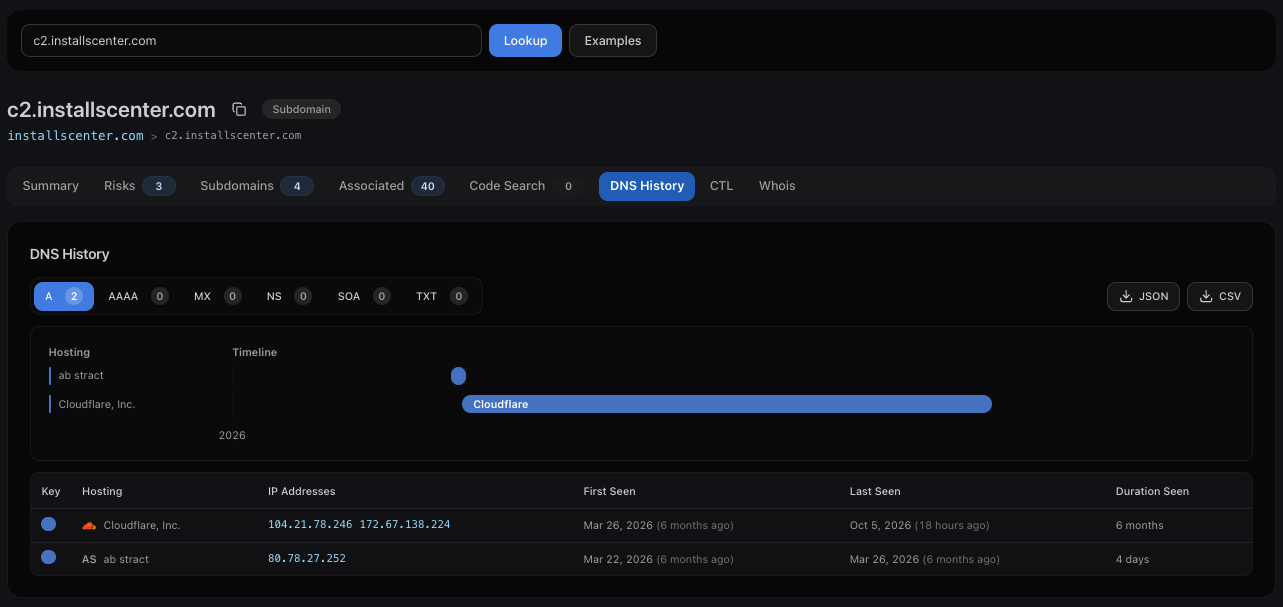
Hunt.io traced BraZetsu ‘s infrastructure and found that hosting patterns and certificate data remained useful after published IOCs became outdated. Group-IB researchers published a detailed writeup on BraZetsu back on August 31, naming it a Python framework compiled with Nuitka and tying it to a Brazilian actor called Exilware with high confidence. Hunt.io checked whether […]