 Pierluigi Paganini
 May 14, 2026
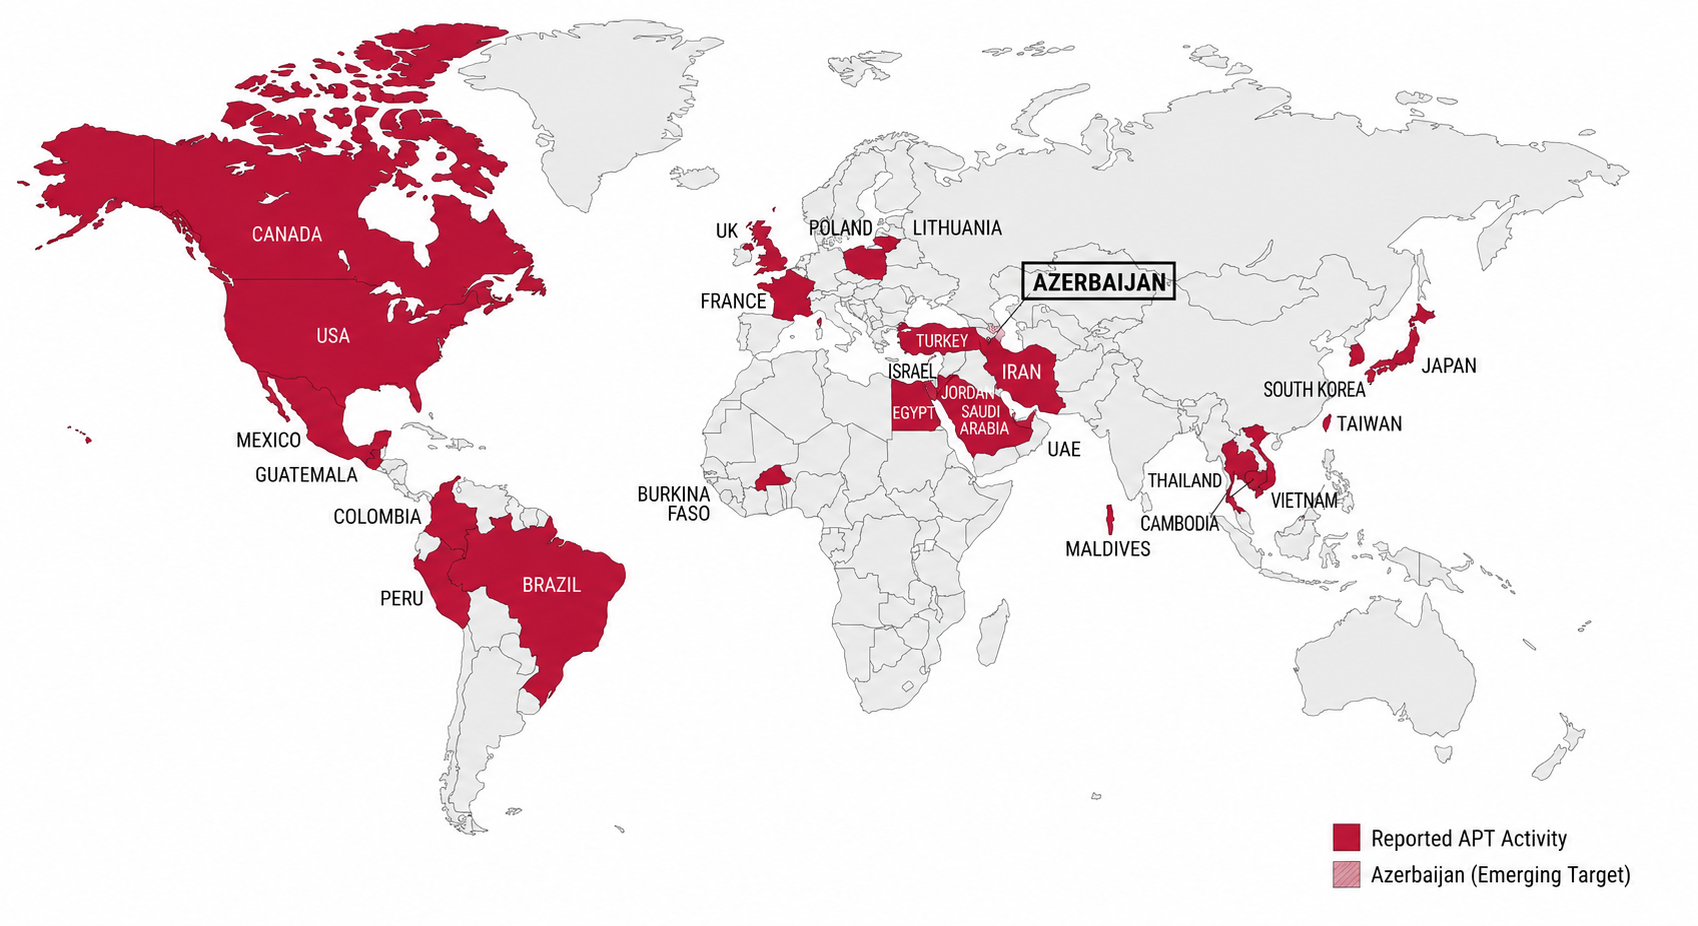
Chinese-linked FamousSparrow repeatedly targeted an Azerbaijani oil and gas company, reusing the same entry point in three intrusions from Dec 2025 to Feb 2026. Chinese-linked threat actor FamousSparrow has conducted a sustained intrusion campaign against an Azerbaijani oil and gas company, returning to the same compromised entry point three separate times between late December 2025 […]
 Pierluigi Paganini
May 06, 2026
Iran-linked APT MuddyWater used ransomware-style tactics to mask espionage, combining phishing, credential theft, data exfiltration, and extortion without encryption. A newly discovered cyber intrusion attributed to the Iran-linked APT MuddyWater (aka SeedWorm, TEMP.Zagros, Mango Sandstorm, TA450, and Static Kitten) reveals how state-sponsored attackers are increasingly leveraging ransomware tactics to disguise espionage operations. The campaign, uncovered by security researchers at Rapid7, blended […]
 Pierluigi Paganini
May 03, 2026
April 2026 breach at Sistemi Informativi (IBM Italy) raises concerns over Chinese-linked cyber ops in Europe, including Salt Typhoon. In late April 2026, the Italian cybersecurity landscape was shaken by a significant breach targeting Sistemi Informativi, a company wholly owned by IBM Italy that provides IT infrastructure management for key public and private institutions. The […]
 Pierluigi Paganini
April 28, 2026
Suspected Russian phishing via Signal targeted German officials, exploiting trust to access accounts and sensitive political communications. A new wave of cyber operations targeting European political leadership is once again highlighting how modern espionage increasingly relies on deception rather than technical exploits. Recent investigations by German authorities point to a large-scale phishing campaign conducted via […]
 Pierluigi Paganini
April 27, 2026
A Chinese national posed as a U.S. researcher, tricking NASA staff in a phishing campaign to steal sensitive data tied to defense software and exports. A Chinese national ran a spear-phishing campaign by posing as a U.S. researcher and tricked NASA employees into sharing sensitive information. The NASA Office of Inspector General (OIG) and federal […]
 Pierluigi Paganini
April 27, 2026
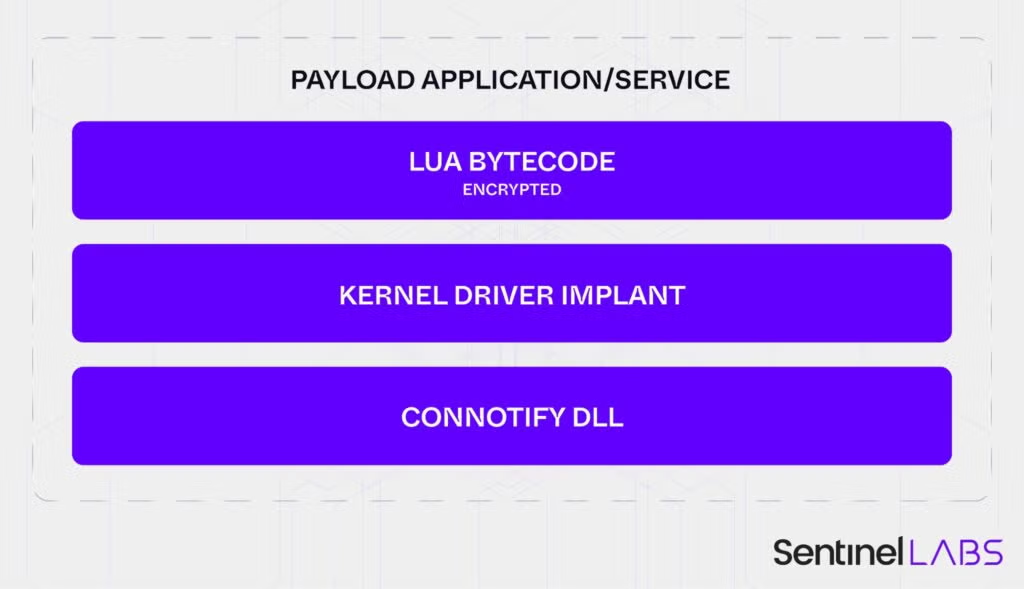
Fast16 is a pre-Stuxnet malware that tampered with precision software and spread itself. Evidence suggests links to U.S. operations during early cyber tensions. SentinelOne uncovered Fast16, a sabotage malware used in 2005, years before Stuxnet. The malicious code is written in Lua and targeted high-precision calculation software, altering results and spreading across systems. The malware […]
Pierluigi Paganini
April 27, 2026
Italy plans to extradite Xu Zewei to the U.S. over alleged hacks on COVID-19 research tied to state-backed operations. Italy is moving to extradite Xu Zewei, the Chinese national arrested in 2025 at the request of U.S. authorities on cyber-espionage charges, Bloomberg reported. The case stands out because it ties a single suspect, Xu, to […]
Pierluigi Paganini
April 26, 2026
ESET found a new China-linked APT, tracked as GopherWhisper, targeting Mongolia using Go-based malware, loaders, and backdoors. ESET researchers uncovered a new China-aligned APT group called GopherWhisper, targeting government institutions in Mongolia. The group’s arsenal includes a range of tools mainly written in Go, such as loaders and injectors, which are used to deploy multiple […]
 Pierluigi Paganini
April 24, 2026
Germany’s Bundestag President Klöckner was targeted in a Signal phishing attack via a fake CDU group chat. Germany’s Bundestag President Julia Klöckner has reportedly become the latest European political figure targeted through a Signal-based phishing attack, reported Der Spiegel. The incident is another reminder that even trusted messaging apps can become entry points when attackers […]
 Pierluigi Paganini
April 22, 2026
Mastodon suffered a major DDoS attack shortly after a similar incident hit Bluesky. The outage was significant but resolved within a few hours. Mastodon was hit by a major DDoS attack just days after a similar disruption affected Bluesky. Mastodon is a free and open-source software platform for decentralized social networking with microblogging features similar […]
Data Breach / October 20, 2026