 Pierluigi Paganini
 March 27, 2026
China-linked Red Menshen APT group used stealthy BPFDoor implants in telecom networks to spy on government targets. Rapid7 Labs uncovered a China-linked threat group known as Red Menshen has been running a long-term espionage campaign by infiltrating telecom networks, mainly in the Middle East and Asia. Active since at least 2021, the group uses highly […]
 Pierluigi Paganini
March 23, 2026
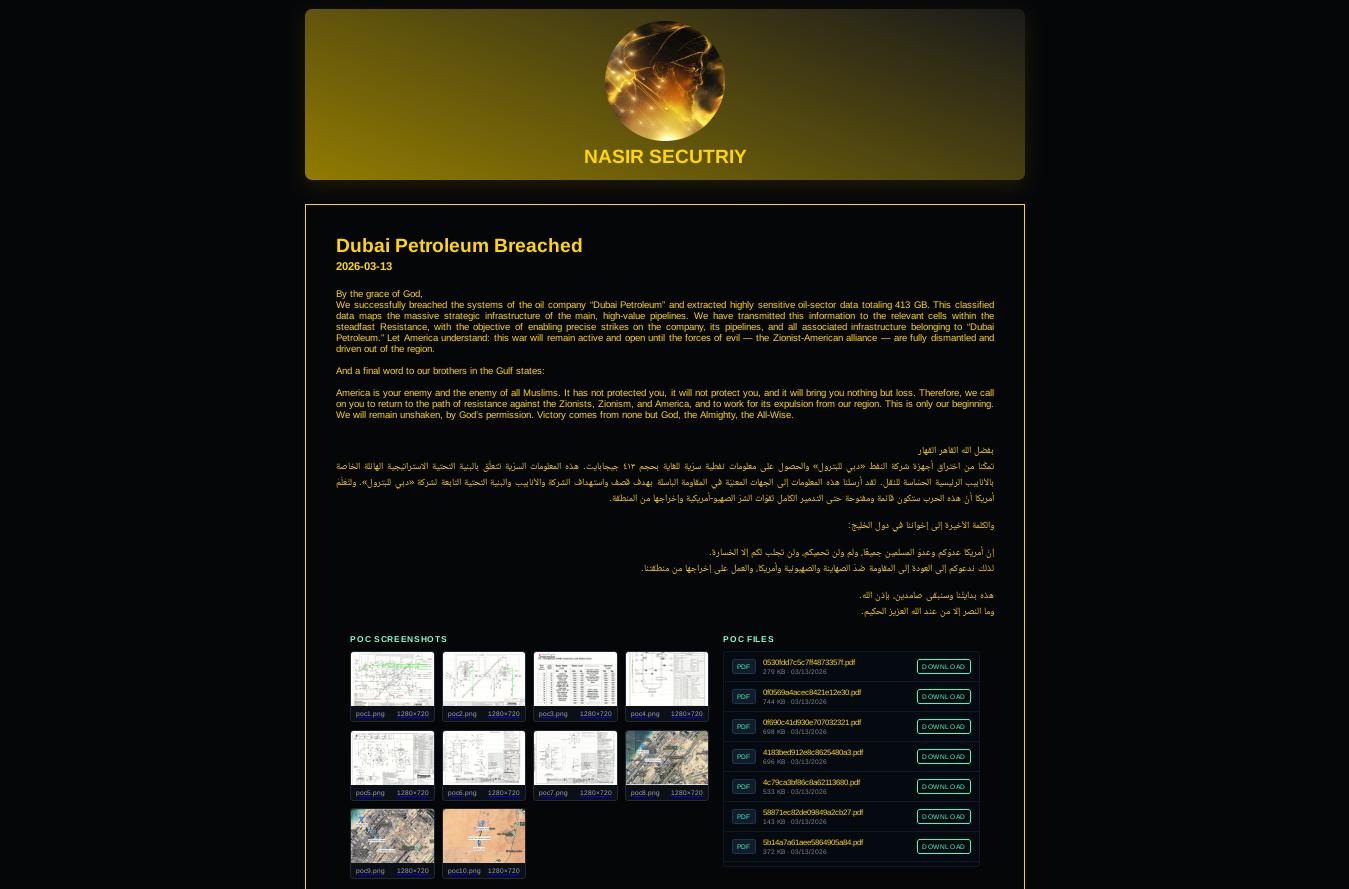
Resecurity tracks Iran-linked Nasir Security targeting Middle East energy firms amid ongoing regional cyber and military threats. Resecurity (USA) is tracking a relatively new cybercriminal group called Nasir Security, presumably associated with Iran, that is targeting energy organizations in the Middle East. The energy sector is one of the most impacted areas because of the […]
 Pierluigi Paganini
March 23, 2026
Iran-linked actors use Telegram as C2 to spread malware targeting dissidents and journalists, enabling surveillance and data theft. The FBI warns that Iran’s Ministry of Intelligence and Security (MOIS) runs cyber campaigns using Telegram as a command-and-control infrastructure to deliver malware. Threat actors target Iranian dissidents, journalists, and opposition groups worldwide. Once deployed, the malware […]
 Pierluigi Paganini
March 22, 2026
Russia-linked actors target WhatsApp and Signal accounts of officials and journalists via phishing, gaining access to messages and contacts. Threat actors linked to Russian Intelligence Services are running phishing campaigns to hijack high-value accounts on messaging apps like WhatsApp and Signal, the FBI warns. “The FBI has identified cyber actors associated with Russian Intelligence Services targeting […]
 Pierluigi Paganini
March 20, 2026
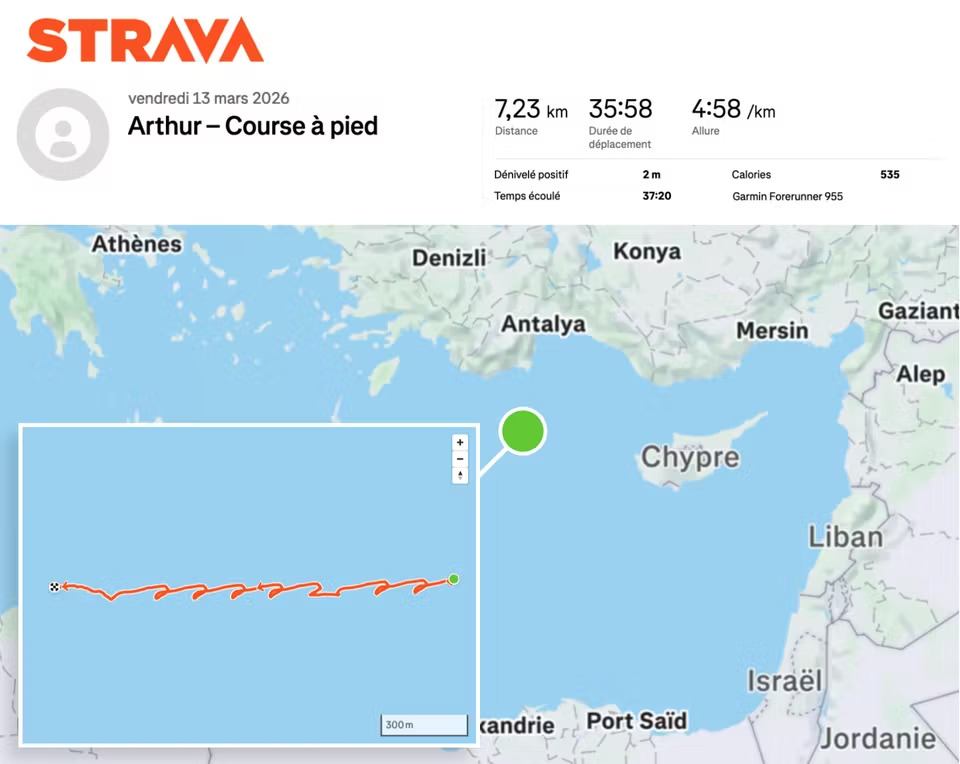
A French aircraft carrier was tracked in real time via a sailor’s Strava activity, exposing a persistent operational security flaw. Le Monde revealed that France’s aircraft carrier Charles de Gaulle was tracked in real time through an officer’s activity on the Strava app. A sailor unknowingly shared running data from the ship, exposing its location […]
 Pierluigi Paganini
March 19, 2026
Russia uses Vienna as its largest Western spy hub, monitoring NATO and other sensitive communications via diplomatic sites and satellite dishes. Western intelligence reports that Russia has transformed Vienna into its largest Western spy hub, steadily expanding surveillance over the past two years. Using diplomatic compounds and rooftop satellite clusters, Russia monitors sensitive communications across […]
 Pierluigi Paganini
March 17, 2026
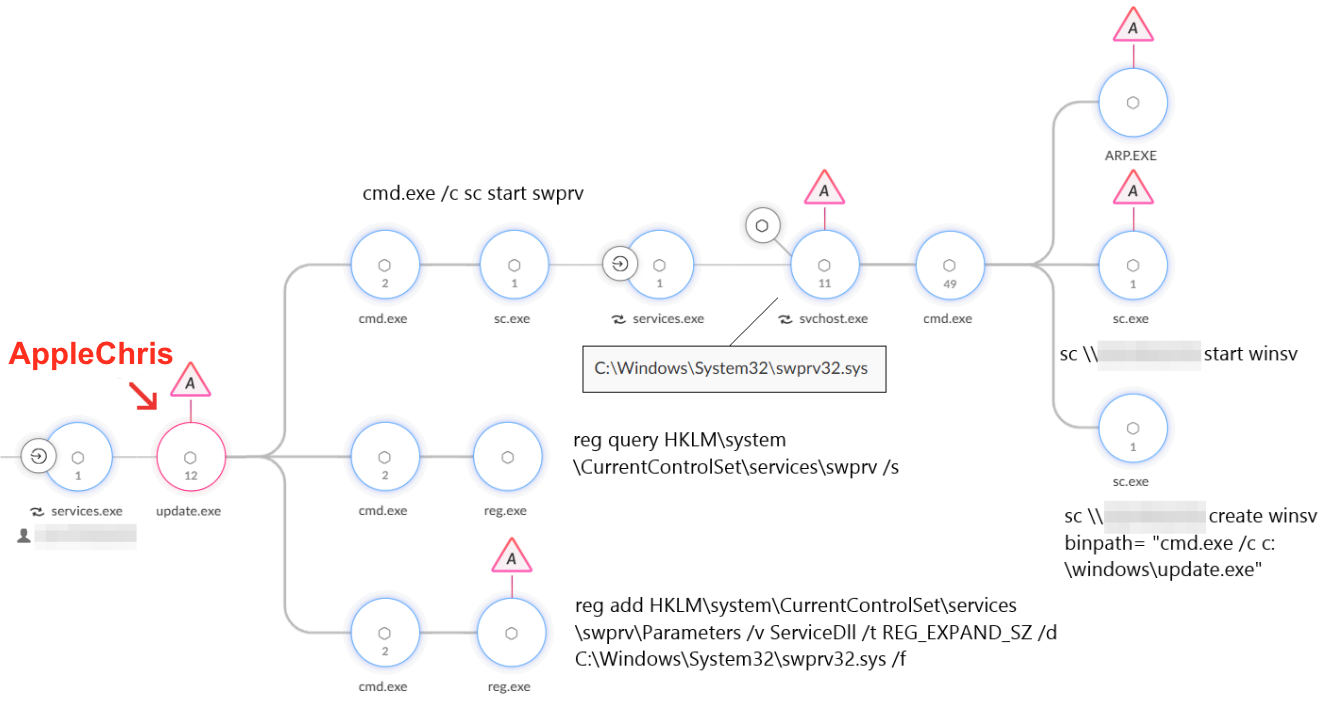
China-linked APT group CL-STA-1087 has targeted Southeast Asian militaries since 2020 using AppleChris and MemFun. A suspected China-linked espionage campaign, tracked as CL-STA-1087, has targeted Southeast Asian military organizations since at least 2020, using AppleChris and MemFun malware. “The activity demonstrated strategic operational patience and a focus on highly targeted intelligence collection, rather than bulk […]
 Pierluigi Paganini
March 16, 2026
Russia-linked threat actors target Ukrainian entities with DRILLAPP backdoor and use Edge debugging for stealth. A new DRILLAPP backdoor campaign targets Ukrainian organizations, abusing Microsoft Edge debugging to evade detection. Observed in February 2026, it shows links to previous Russian-aligned operations by Laundry Bear APT group (aka UAC-0190, Void Blizzard) using the PLUGGYAPE malware family […]
Pierluigi Paganini
March 16, 2026
Former BND VP Arndt Freytag von Loringhoven was targeted in a Signal cyberattack, part of a wave hitting officials and politicians in Germany. A cyberattack targeting Signal and WhatsApp users has hit high-ranking German officials, including former BND Vice President Arndt Freytag von Loringhoven. The official reported being contacted by someone posing as Signal support […]
 Pierluigi Paganini
March 10, 2026
APT28 used BEARDSHELL and COVENANT malware to spy on Ukrainian military personnel, enabling long-term surveillance since April 2024. The Russia-linked group APT28 (aka UAC-0001, aka Fancy Bear, Pawn Storm, Sofacy Group, Sednit, BlueDelta, and STRONTIUM) has used BEARDSHELL and COVENANT malware to conduct long-term surveillance of Ukrainian military personnel. According to ESET, the campaign began in April 2024 and relies on […]
Data Breach / October 20, 2026