19319 results
 Pierluigi Paganini
 August 11, 2014
Researchers at FireEye have uncovered a new campaign dubbed Poisoned Hurricane characterized by the use of some clever techniques to avoid being detected. Security experts at FireEye revealed that several Internet infrastructure service providers in the United States and Asia, a financial institution, a government organization located in Asia and a US-based media company suffered […]
 Pierluigi Paganini
August 10, 2014
Security Experts at Cheetah Mobile have uncovered a new scam based on a fake Facebook Color Changer App which infected 10000 users worldwide. Facebook is a privileged target for cyber criminals, in many cases old fraud schema are proposed again by bad actors, it is the case of the bogus Facebook “Color Changer” app. Researchers at China-based Internet company […]
 Pierluigi Paganini
August 10, 2014
Researchers at Dell SecureWorks Counter Threat Unit discovered a theft of Bitcoin made hijacking networks of at least 19 Internet service providers. With the rise of Bitcon value has increased the interest of cybercrime, since now we have read of botnet able to mine virtual currency with victim’s resources and malicious codes able to steal Bitcoin […]
 Pierluigi Paganini
August 09, 2014
One million Android devices in China were infected with an Xshqi SMS worm on August 2, the day the country celebrated Valentine’s Day. Experts at Kaspersky Lab revealed that a malware, dubbed Trojan.AndroidOS.Xshqi.a, infected neatly 500,000 Android devices in just six hours last week in China, but Chinese media provided a more pessimistic estimate declaring that the […]
 Pierluigi Paganini
August 08, 2014
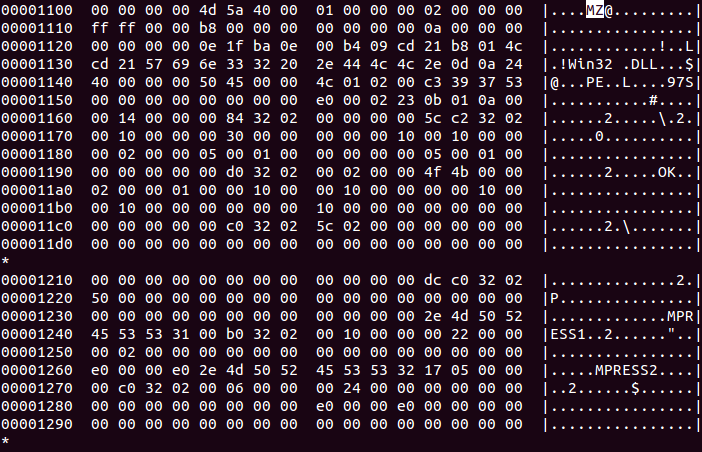
Experts at GData discovered Poweliks, a persistent malware able to infect machines without installing any files on the targeted machine. Researchers at GData software have discovered a new surprising strain of malware named Poweliks which is able to infect systems and steals data without installing any file onto the victim’s machine. This malware maintains persistence storing its components […]
 Pierluigi Paganini
August 08, 2014
A Hacker claims to have hacked the network of Gamma International firm and he has leaked docs related to the malware-for-government FinFisher. Earlier this week the British company Gamma International appears to have been hacked and a collection of files from its systems have been leaked on the Internet. The security firm is popular because it […]
 Pierluigi Paganini
August 07, 2014
The popular expert Nir Goldshlager has discovered an XMLRPC vulnerability which affects millions WordPress and Drupal websites exposing them to DoS Attack. If your website is based a WordPress or Drupal CMS you need to urgently update it to the last version released due to the presence of a critical vulnerability in the implementation of […]
 Pierluigi Paganini
August 07, 2014
A report disclosed by Wired suggests that the FBI is using a malware to identify Tor users by infecting machines on a large scale. It’s not a mystery that usage of the Tor network represents a problem for investigators of law enforcement agencies and for government entities that need to track users on the popular anonymizing network. […]
 Pierluigi Paganini
August 06, 2014
Experts at Hold Security firm discovered a Russian group of hackers that collected 1.2B stolen credentials obtained in different data breaches worldwide. Experts at Hold Security revealed to have discovered the biggest database of stolen user names and passwords and email addresses, the news is reported by The New York Times that hired an independent security expert who verified […]
 Pierluigi Paganini
August 06, 2014
A Security researcher has discovered a new flaw in the two-factor authentication process implemented by PayPal to protect its users. Security researcher Joshua Rogers has discovered a simple way of bypassing the two-factor authentication mechanism implemented by PayPal to protect accounts that are linked to eBay accounts. The flaw resides in the login process when a user is prompted […]