19319 results
 Pierluigi Paganini
 July 19, 2014
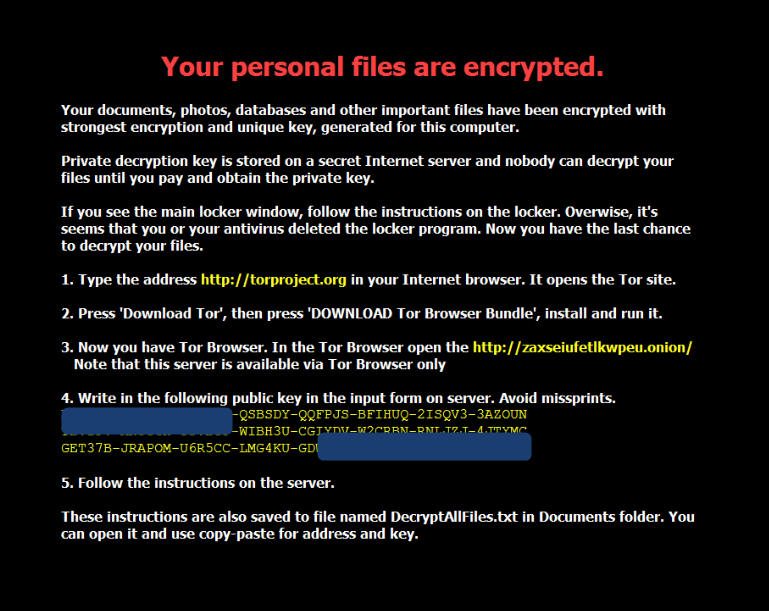
A security researcher has detailed Critroni ransomware, a new sophisticated malware which is being sold in different underground forums. In 2013 ransomware were among the menaces that monopolized the threat landscape, malware such as Cryptolocker infected hundreds of thousand machines worldwide. Critroni (aka CTB-Locker) is the name of the last ransomware which captured the attention of security experts, the malware […]
 Pierluigi Paganini
July 18, 2014
Hackers pro Hamas claim to have hacked programming on Israeli TV Channel 10 and inserted an unscheduled transmission calling for an end to Israeli airstrikes. The effects of the conflict between Israel and Palestin are evident also in the cyberspace, group of hacktivists, including Anonymous, are targeting Israeli Government websites to protest against recent strikes that […]
 Pierluigi Paganini
July 18, 2014
Russian hackers hit Nasdaq critical systems with with a malware-based attack with the primary intent to sabotage the U.S. financial world. It was October 2010 when the FBI started an investigation on alleged malware-based cyber attacks against on Nasdaq, probably related to the operation of a state-sponsored group of hackers. After more than 12 months in which […]
 Pierluigi Paganini
July 17, 2014
Multiple Cisco Wireless Residential Gateway products are affected by a critical flaw that could allow a remote attacker to hijack the devices. A security vulnerability affects multiple Cisco wireless residential Gateway products, the flaw resides on the web server an could be exploited by a remote attacker to hijack the network appliance. The flaw, ranked […]
 Pierluigi Paganini
July 17, 2014
Experts at Aorato have discovered a flaw in MS Active Directory that could allow an attacker to conduct a pass-the-hash attack to change a victim’s password. The Israel-based security firm Aorato has recently discovered a flaw in Microsoft’s Active Directory (AD) that could allow an attacker (via “pass-the-hash” attack) to change a victim’s password and access a […]
 Pierluigi Paganini
July 16, 2014
Researchers at SEC Consult have discovered a CSRF vulnerability in the OpenVPN Desktop Client that can allow remote code execution. Security researchers at SEC Consult have discovered a CSRF flaw in the OpenVPN Desktop client and promptly reported it to the company in May. OpenVPN Desktop Client for its Access Server is an SSL VPN for a variety […]
 Pierluigi Paganini
July 16, 2014
A Security Researcher at Abuse.ch has started SSL blacklist project to create an archive of all the digital certificates used for illicit activities. In recent years security experts have discovered many cases in which bad actors have abused of digital certificates for illicit activities, from malware distribution to Internet surveillance. Botmasters are exploiting new techniques to avoid detection by security experts and […]
 Pierluigi Paganini
July 16, 2014
Project Zero is the new initiative announced by Google. The company is hiring the top security experts to make the Internet a more secure place. Google has publicly announced a new program called “Project Zero,” an ambitious project which involves a team of Star Hackers and Bug Hunters with the purpose to improve security of the […]
 Pierluigi Paganini
July 15, 2014
Experts at Trusteer have recently discovered an adv on the Russian underground market regarding a new financial Trojan dubbed Kronos. Russian underground is probably the most prolific market for sale of banking malware, malicious code like Citadel, Zeus, Gozi have infected millions computers worldwide dominating the malware threat landscape. The huge demand for banking trojan is creating the conditions […]
 Pierluigi Paganini
July 15, 2014
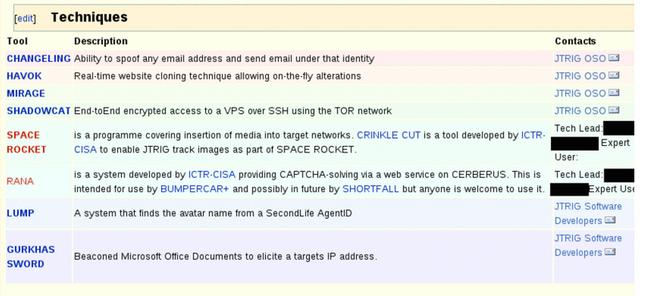
Edward Snowden leaked a top-secret GCHQ document which details the operations and the techniques used by JTRIG unit for propaganda and internet deception. The JTRIG unit of the British GCHQ intelligence agency has designed a collection of applications that were used to manipulate for internet deception and surveillance, including the modification of the results of the […]