19319 results

 Pierluigi Paganini
 June 06, 2014
The OpenSSL Foundation has fixed a series of new vulnerabilities, two of them considered critical. Organizations are invited to apply patches asap. The Open SSL has provided a collection of updates for its libraries to fix a series of new vulnerabilities recently reported. The exact number of vulnerabilities affecting OpenSSL is 6 and two of them are […]
 Pierluigi Paganini
June 05, 2014
Malware analysts at Trendmicro have discovered a new Ransomware malware using feature of Windows PowerShell which targeted English language users. Ransomware is one of the cyber threats that has created major problems last year, with increasing frequency cyber criminals gangs have opted for an extortion scheme to immediately monetize their efforts. Security expert have observed a surge […]
 Pierluigi Paganini
June 05, 2014
Experts at security firm Codenomicon discovered a critical buffer overflow vulnerability in the implementation of the GnuTLS software. GnuTLS, a free software implementation of SSL/TLS/DTLS protocols, it offers a set of application programming interface (API) to enable secure communication over their network transport layer. News of the day is that the widely used cryptographic library is vulnerable […]
 Pierluigi Paganini
June 05, 2014
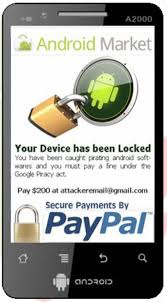
Security experts at ESET discovered and analyzed the first Android File-Encrypting ransomware dubbed Simplocker with C&C hosted on TOR. Ransomware is not a prerogative of desktop computers, cyber criminals are targeting also mobile platforms, recently it has been discovered the first mobile trojan able to encrypt victim’s data on Android by ESET security firm. Cyber criminals […]
 Pierluigi Paganini
June 04, 2014
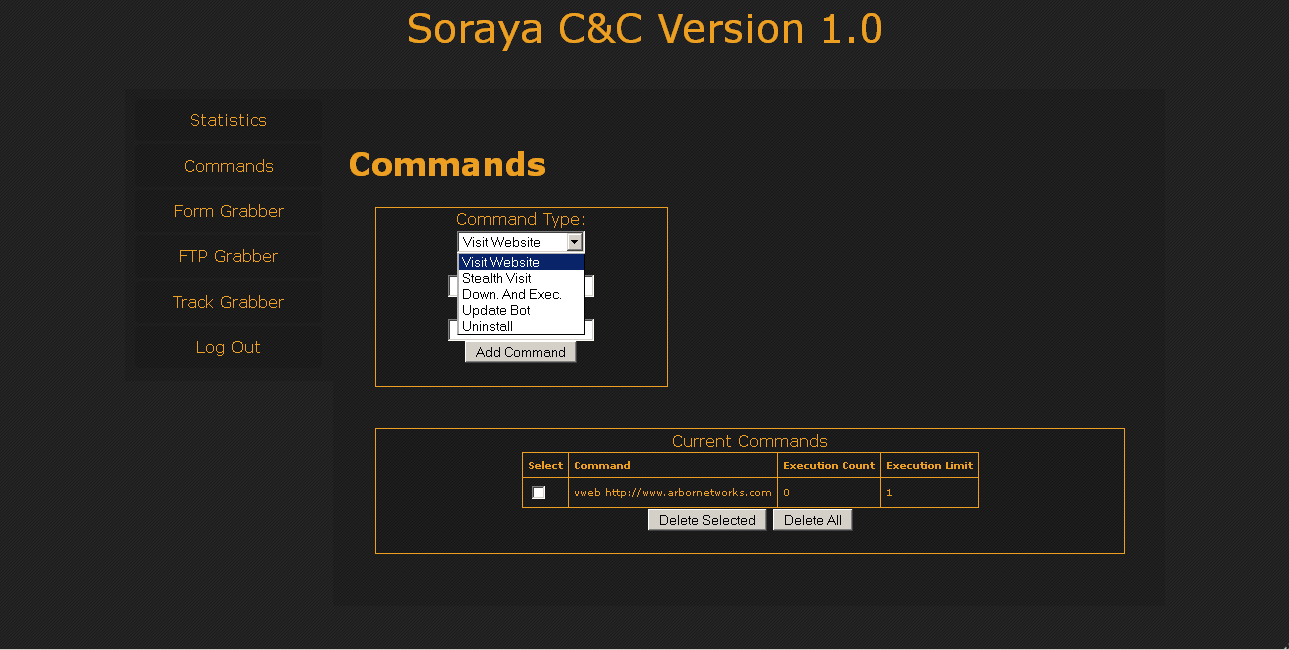
Security experts at Arbor Networks have discovered a new type of PoS malware called Soraya that implements memory scraping and Web forms grabbing. During 2013 security experts have discovered numerous malware targeting point-of-sale systems, BlackPOS, Dexter and vSkymmer are just some example of malicious code detected in the last 12 months. Researchers at Arbor Networks have discovered a […]
 Pierluigi Paganini
June 04, 2014
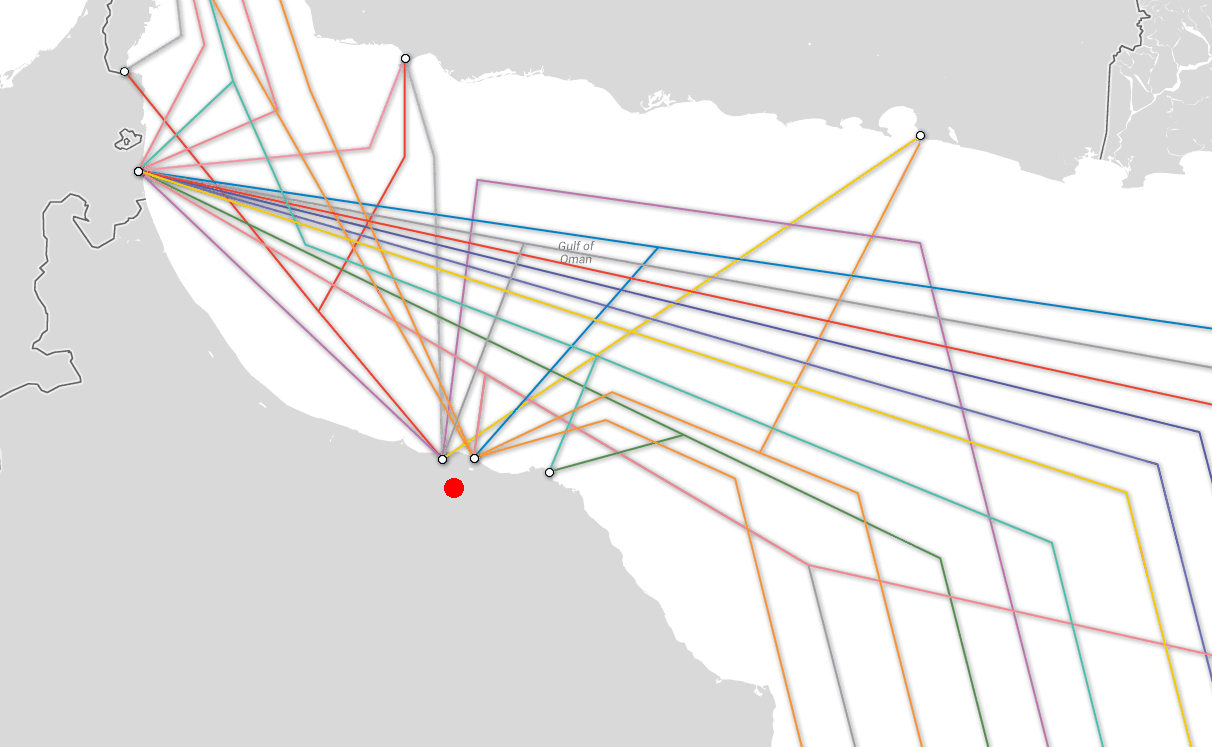
A last revelation on the surveillance activities of British intelligence GCHQ confirms the existence of spy base tapping undersea cables in the Middle East. In the last year Edward Snowden has leaked many disconcerting documents for the surveillance activity conducted by the NSA and GCHQ intelligence agencies, the last revelation is related Britain covert spying programme, in particular the information on clandestine British base […]
 Pierluigi Paganini
June 03, 2014
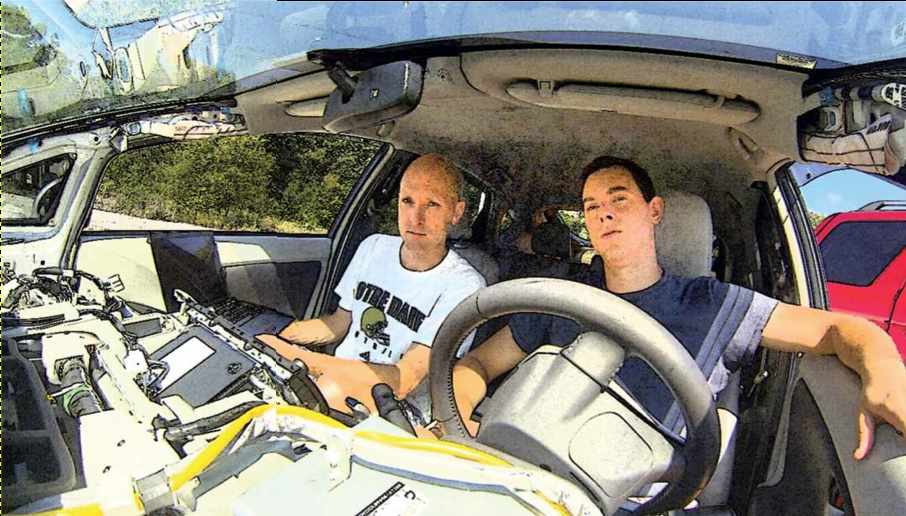
A new alarm on car hacking issued by the security community, the white hat Jonathan Brossard warns cars can be hacked on the road remotely. Car hacking is possible, I have proposed different works presented by security experts that demonstrate how to compromise modern vehicles with cheap environment. Modern cars have a huge quantity of components connected […]
 Pierluigi Paganini
June 03, 2014
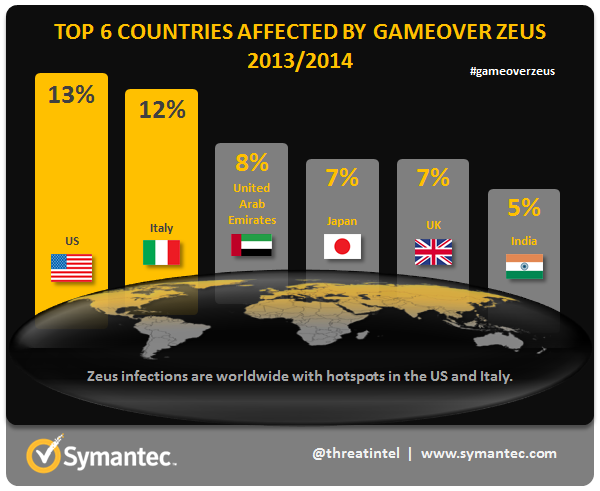
The DoJ and the FBI announced a multinational effort to disrupt the GameOver Zeus botnet responsible for the theft of millions of dollars worldwide. The U.S. DoJ in collaboration with FBI and foreign law enforcement agencies revealed early this week a joint effort to disrupt Gameover Zeus, one of the most long-lived and dangerous botnet composed by a number […]
 Pierluigi Paganini
June 02, 2014
A Portuguese security expert has uncovered the Cupid attack, a new Heartbleed attack vector which can impact Android devices, enterprise wireless networks and other connected devices. Cupid is the name of the new Heartbleed attack method recently proposed by Portuguese security researcher Luis Grangeia, unlike the original version of the attack, which took place on TLS connections over TCP, […]
 Pierluigi Paganini
June 02, 2014
Security Experts discovered a new attack method to defeat Secure Boot security mechanism of the UEFI (Unified Extensible Firmware Interface). The Secure Boot security mechanism of the UEFI (Unified Extensible Firmware Interface) can be circumvented on around half of PCs that use it, security researcher Corey Kallenberg from nonprofit research organization Mitre has demonstrated it at […]