19303 results
 Pierluigi Paganini
 January 23, 2026
Fortinet confirmed attacks are bypassing FortiCloud SSO authentication, affecting even fully patched devices, similar to recent SSO flaws. Fortinet confirmed attacks bypass FortiCloud SSO on fully patched devices. Threat actors automate firewall changes, add users, enable VPNs, and steal configs, in campaigns resembling December 2025 exploits of critical FortiCloud SSO flaws. Arctic Wolf researchers reported […]
 Pierluigi Paganini
January 23, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Prettier eslint-config-prettier, Vite Vitejs, Versa Concerto SD-WAN orchestration platform, and Synacor Zimbra Collaboration Suite flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Prettier eslint-config-prettier, Vite Vitejs, Versa Concerto SD-WAN orchestration platform and Synacor Zimbra Collaboration Suite flaws to its Known Exploited Vulnerabilities […]
 Pierluigi Paganini
January 23, 2026
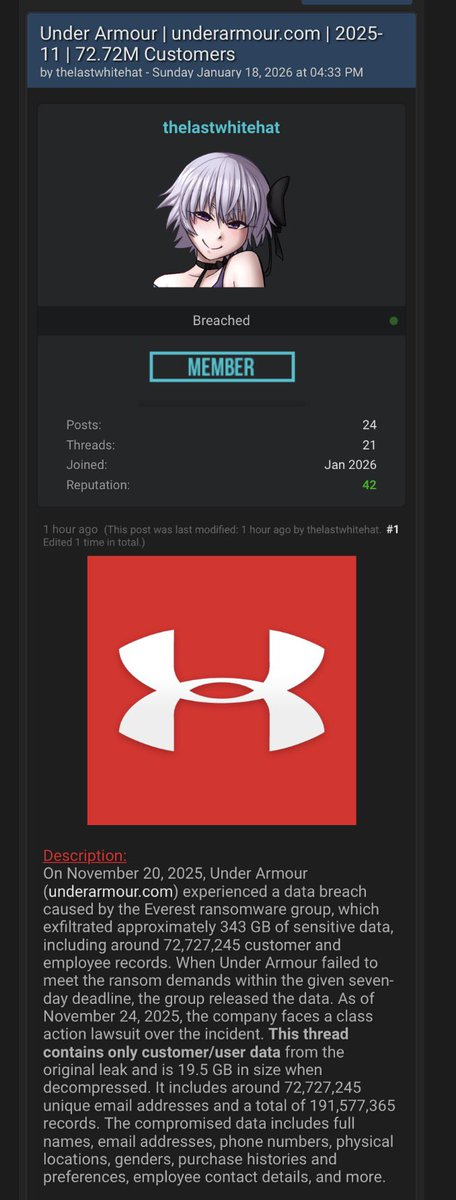
Under Armour is investigating a data breach after 72M customer records were posted online by a cybercriminal. Under Armour is an American company that designs, manufactures, and sells sportswear, athletic shoes, and fitness-related accessories. TechCrunch reported that Under Armour is investigating a data breach after 72M customer records were posted online. The stolen data, linked […]
 Pierluigi Paganini
January 22, 2026
A new Android click-fraud trojan family uses TensorFlow ML to visually detect and tap ads, bypassing traditional script-based click techniques. Researchers at cybersecurity firm Dr.Web discovered a new Android click-fraud trojan family that uses TensorFlow.js ML models to visually detect and tap ads, avoiding traditional script-based methods. The malware is distributed via Xiaomi’s GetApps, it […]
 Pierluigi Paganini
January 22, 2026
A SmarterMail flaw (WT-2026-0001) is under active attack just days after its January 15 patch, with no CVE assigned yet. A newly disclosed flaw in SmarterTools SmarterMail is being actively exploited just two days after a patch was released. The issue, tracked as WT-2026-0001 and lacking a CVE, was fixed on January 15, 2026, with […]
Pierluigi Paganini
January 22, 2026
Arctic Wolf warned of a new wave of automated attacks making unauthorized firewall configuration changes on Fortinet FortiGate devices. Arctic Wolf researchers reported a new automated attack cluster observed since January 15, 2026, targeting FortiGate devices. Attackers created generic accounts for persistence, enabled VPN access, and exfiltrated firewall configurations. The activity resembles a December 2025 […]
 Pierluigi Paganini
January 22, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw impacting Cisco Unified Communications products to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Cisco Unified Communications products vulnerability, tracked as CVE-2026-20045 (CVSS score of 8.2), to its Known Exploited Vulnerabilities (KEV) catalog. This week, Cisco patched a critical zero-day […]
Pierluigi Paganini
January 21, 2026
Cisco patched a critical zero-day RCE flaw (CVE-2026-20045) in Unified Communications and Webex Calling that is actively exploited in the wild. Cisco patched a critical zero-day remote code execution flaw, tracked as CVE-2026-20045 (CVSS score of 8.2), actively exploited in attacks. An unauthenticated, remote attacker can exploit the flaw to execute arbitrary commands on the […]
 Pierluigi Paganini
January 21, 2026
Zoom addressed a critical security vulnerability, tracked as CVE-2026-22844, that could result in remote code execution. Cloud-based video conferencing and online collaboration platform Zoom released security updates to address multiple vulnerabilities, including command injection, tracked as CVE-2026-22844 (CVSS score of 9.9), in Zoom Node Multimedia Routers (MMRs) that could result in remote code execution. “A […]
 Pierluigi Paganini
January 21, 2026
Cloudflare fixed a flaw in its ACME validation logic that could let attackers bypass security checks and access protected origin servers. Cloudflare fixed a flaw in its ACME HTTP-01 validation logic that could let attackers bypass security checks and reach origin servers. The issue stemmed from how Cloudflare’s edge handled requests to the /.well-known/acme-challenge/ path. […]