 Pierluigi Paganini
 July 22, 2016
18 out of 276 vulnerabilities fixed by Oracle with the last Patch Update resides in the OIT libraries that are used by products of numerous major vendors. The last critical Patch Update released by Oracle this week is in the headlines for the number of patches it includes. It includes the fixes for 276 vulnerabilities, 19 of […]
 Pierluigi Paganini
July 21, 2016
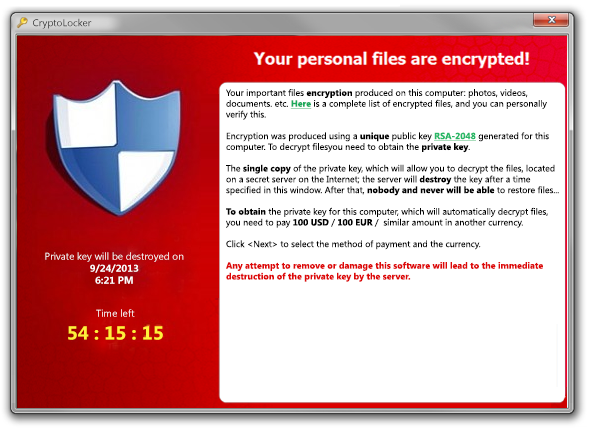
Recently, Reuters reported that the FBI sent an urgent confidential ‘Flash’ message to businesses and organizations to warn them about ransomware. Sponsored Content It is that dangerous. This is a new version of the ransom note, a form of malware that interferes with access to user files and data by encrypting it. Those running the […]
 Pierluigi Paganini
July 21, 2016
One of the most popular hacktivists, Phineas Fisher claimed responsibility for the hack of the Turkish Government that lead the disclosure of Erdogan Emails. A few hours ago I reported the news of the ban on Wikileaks decide by the Turkish Government in response to the publishing of the Erdogan Emails, now the popular Phineas Phisher […]
 Pierluigi Paganini
July 21, 2016
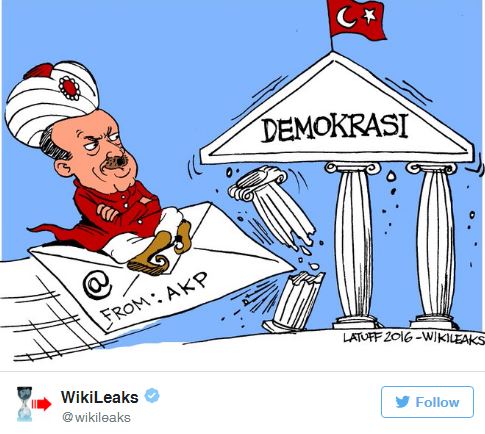
The Turkish Government blocked the access to WikiLeaks after release of the Erdogan emails, 300,000 government emails date 2010 to July this year. Cyberspace and the real world are even more interdependent, the observation of the events in both environments is an essential activity for the analysts to predict evolutionary scenarios. The world is attending events […]
 Pierluigi Paganini
July 20, 2016
Today, it is a pleasure for me to interview an Italian colleague, Matteo Meucci, a great professional, a perfect mix of talent and discipline. Enjoy the interview. Hi Matteo, you are one of the most respected Italian experts on cyber security. Could you tell me which his your technical background and when you started hacking? […]
 Pierluigi Paganini
July 20, 2016
This critical flaw CVE-2016-4631 resides in the ImageIO and could be exploited by a remote attacker to steal sensitive information from Apple devices. Apple fans, I have a bad news for you, just one specially-crafted message can expose your personal information, including your authentication credentials stored in the memory of your Apple device. This means […]
 Pierluigi Paganini
July 20, 2016
Delilah is the first extortion trojan that spies on victims and collects information to force them in doing malicious activities from inside. Delilah is a strain of malware developed to extort victims into stealing insider data, it was first discovered on crime forums by the Israeli intelligence firm Diskin Advanced Technologies. Deliah is not distributed in […]
 Pierluigi Paganini
July 20, 2016
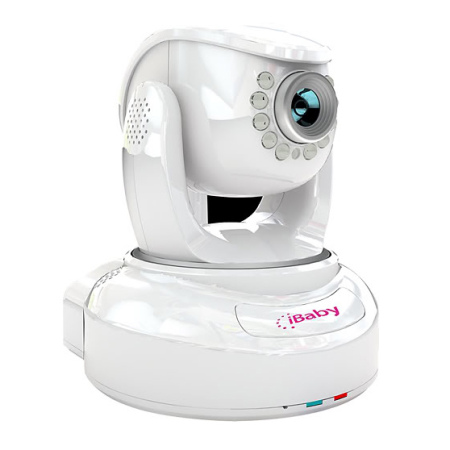
According to the ICO Baby monitors are still open to hackers across the UK, the ICO issued a list of recommendations to avoid privacy breaches. Early this year, the Shodan search engine launched a feature that lets users easily access vulnerable webcams. In September 2015, researchers from the Rapid7 security firm discovered a number of security vulnerabilities affecting several Video […]
 Pierluigi Paganini
July 19, 2016
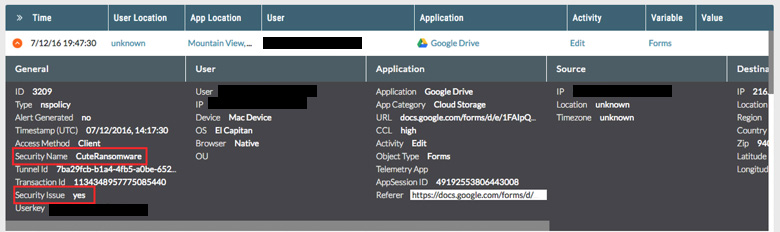
A newly strain of ransomware dubbed cuteRansomware leverages on a Google Doc to host the decryption key and command-and-control features. A recently discovered strain of ransomware, dubbed cuteRansomware, shows that your enterprise isn’t the only one thinking about cloud transition. Modern day hackers are loving the Cloud too. The cuteRansomware was discovered by Netskope security firm which observes an increase […]
 Pierluigi Paganini
July 19, 2016
A security expert revealed a number of flaws in the big player’s two-factor authentication methods that could allow crooks to steal money. Social media bug bounty hunter, Arne Swinnen, has revealed a number of flaws in the big player’s 2 factor authentication (2FA) methods that could enable a malicious user to illicit large sums of […]