


 Pierluigi Paganini
 September 09, 2026
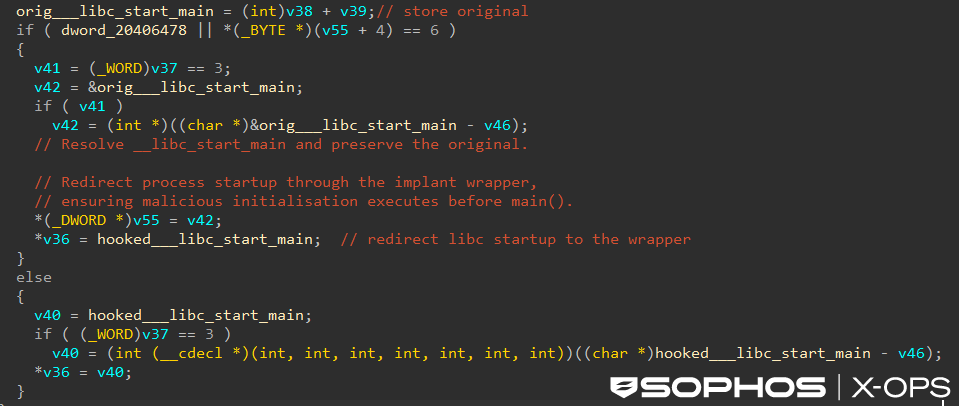
PoisonedRefresh rootkit injects PHP web shells into F5 BIG-IP APM Apache memory, leaving no disk artifacts. SophosLabs published a detailed technical analysis on September 8, 2026, of a Linux implant, dubbed PoisonedRefresh by ESET, they found in compromised F5 BIG-IP Access Policy Manager environments. Sophos tracks it as Linux/Agnt-IC. F5 has confirmed exploitation of the […]
 Pierluigi Paganini
September 08, 2026
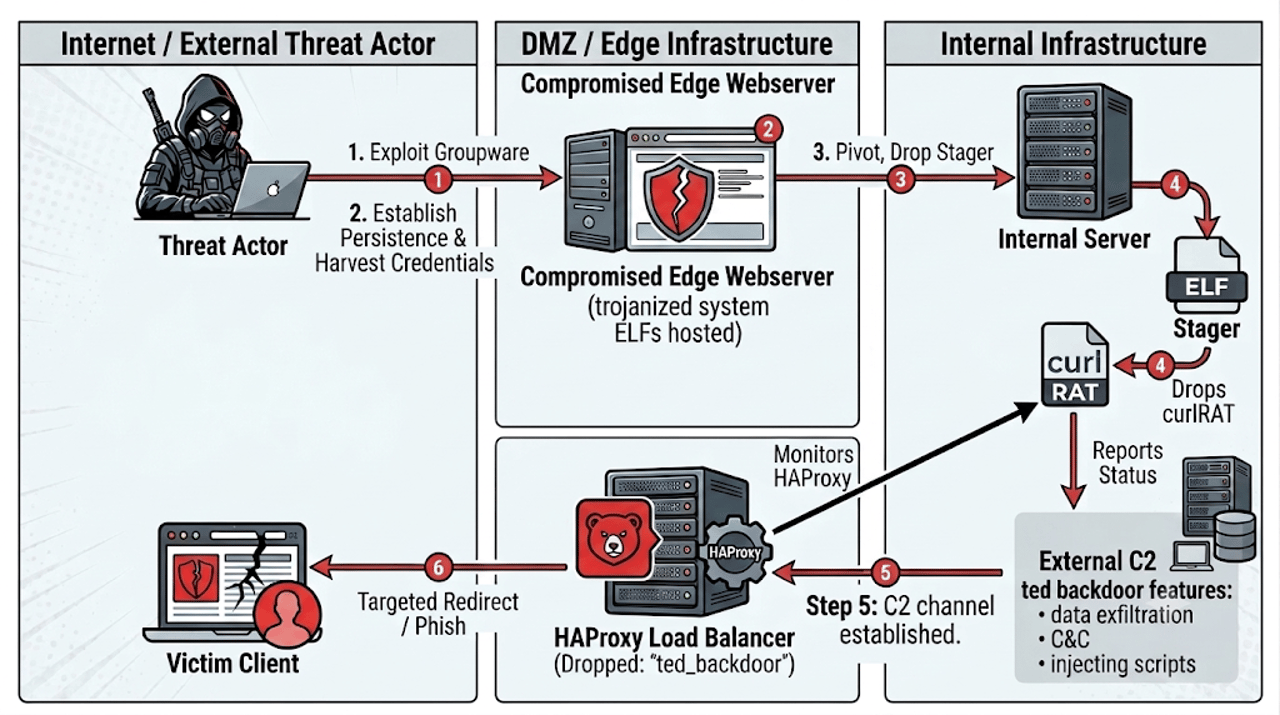
North Korea-linked hackers hid a backdoor inside HAProxy, masking C2 traffic and stealing data while keeping the load balancer working normally. North Korean-linked hackers found a genuinely clever hiding spot for their malware: inside the actual source code of HAProxy, the load balancing software running at the edge of two South Korean companies’ networks. Rapid7’s […]
 Pierluigi Paganini
September 07, 2026
StyleSmuggler Magento zero-day is under active attack, letting unauthenticated attackers execute code and install backdoors on stores that may already be patched. A new zero-day flaw, dubbed StyleSmuggler, in Magento and Adobe Commerce is under active attack, giving unauthenticated attackers a path to run code on vulnerable online stores. Sansec researchers say it affects current […]
 Pierluigi Paganini
September 07, 2026
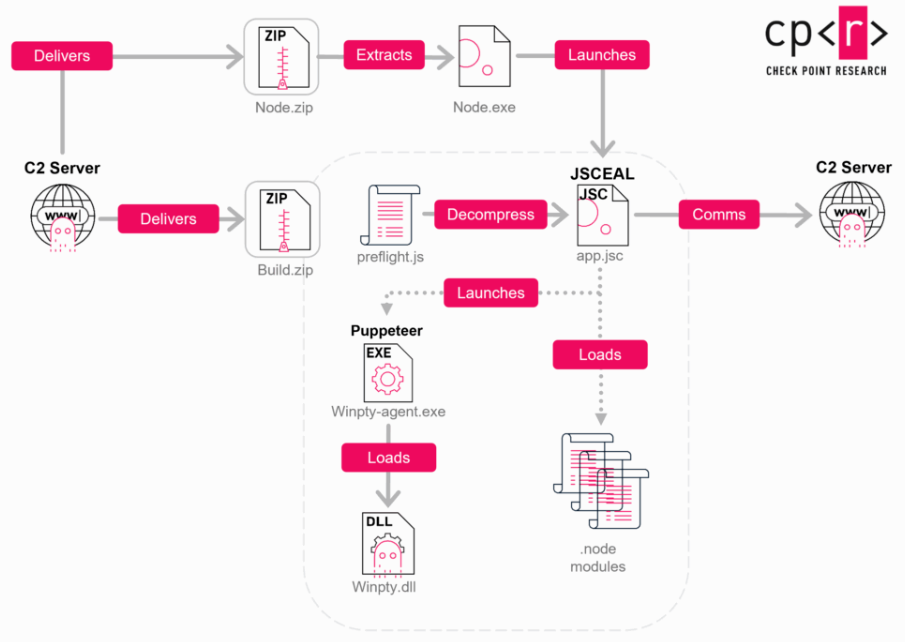
JSCeal hides crypto-stealing malware in V8 bytecode, but researchers built a tool to decompile it and expose its advanced theft capabilities. JSCeal is a cryptocurrency stealer that Check Point Research has tracked since early 2025. Unlike most malware, it hides its code in a format that makes analysis much harder. Check Point presented its latest […]
 Pierluigi Paganini
September 07, 2026
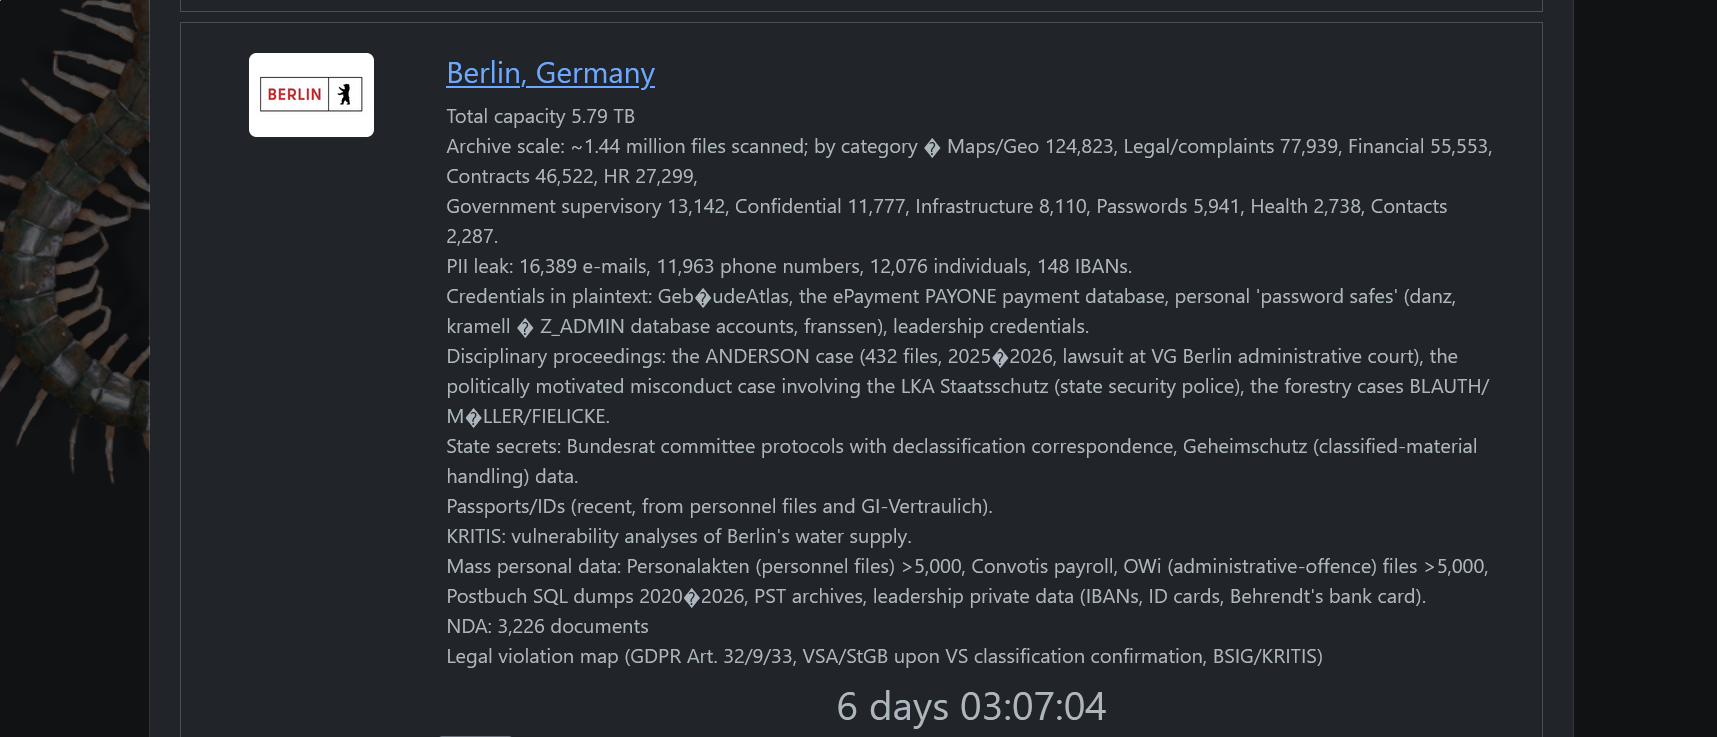
Berlin refused a 30 Bitcoin ransom, leading hackers to leak 6TB of sensitive state administration and national defense data on the dark web. When a ransomware gang dumps nearly six terabytes of state administration files onto the dark web, ignoring them does not make the problem go away. The Rhysida ransomware group recently carried out […]
 Pierluigi Paganini
September 06, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Hackers Steal Claude Login Sessions With Infostealer Malware to Hijack Accounts Fire Ant Evolves: From Hypervisors to Trusted Infrastructure Gryxa: The AI-Built Toolkit That Watches How You Remove It ValleyRAT masquerading as adware […]
 Pierluigi Paganini
September 06, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. PaperCut Flaws Exploited in Attacks on U.S. and European Schools Broadcom Patches Critical VMware Workstation and Fusion […]
 Pierluigi Paganini
September 04, 2026
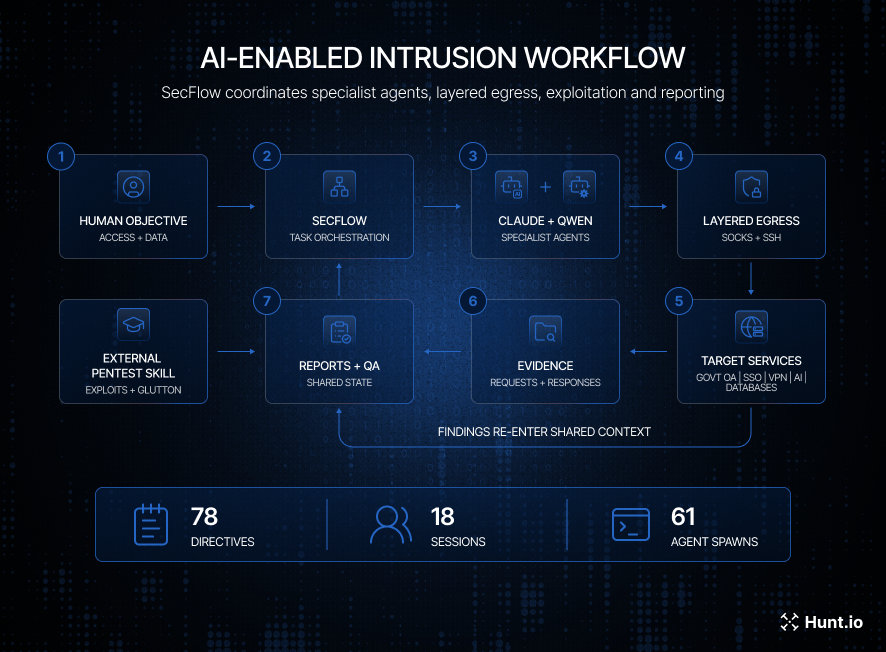
Hunt.io uncovered a Chinese-speaking campaign using AI agents to automate cyberattacks against Asian government, education and industrial targets. Threat intelligence firm Hunt.io just documented a second, separate China-linked campaign wiring commercial AI models directly into live cyberespionage operations, this time hitting Taiwan’s Kuomintang Party archives, Indonesia’s Ministry of Foreign Affairs, government and education systems in […]
 Pierluigi Paganini
September 03, 2026
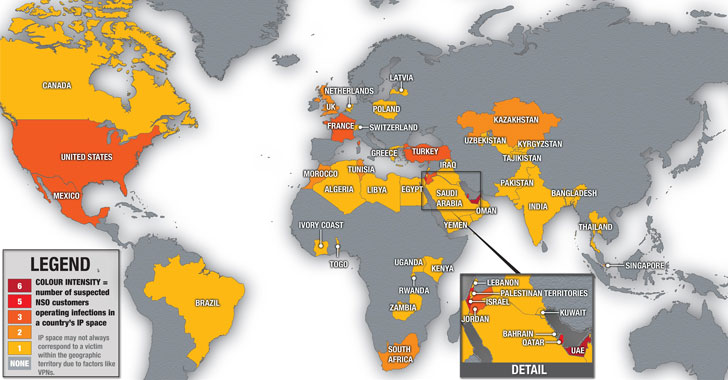
Serbian activists were targeted with zero-click Pegasus and NoviSpy spyware, exposing a major surveillance campaign ahead of elections. A member of Serbia’s student protest movement had their iPhone infected with NSO Group‘s Pegasus spyware without ever clicking a link or opening a file. The Citizen Lab confirmed the infection in collaboration with the SHARE Foundation, […]
 Pierluigi Paganini
September 02, 2026
Experts got Claude to port a PLC exploit, but it cost $536 and 8 hours, and a later AI-generated payload accidentally destroyed the hardware. Forescout researchers just answered a question that’s been hanging over industrial security for a while: can AI actually port a working exploit from one PLC to a different model with no […]
Security / November 12, 2026
Security / November 12, 2026


