


 Pierluigi Paganini
 January 21, 2015
Hacks in Taiwan security conference has uncovered a malware-based attack involving several online games to spread the PlugX RAT. Experts at Trend Micro have spotted a new malicious campaign based on the popular PlugX RAT, the threat actor behind the attack has bundled the malware with League of Legends (LoL) and Path of Exile (PoE) […]
 Pierluigi Paganini
January 17, 2015
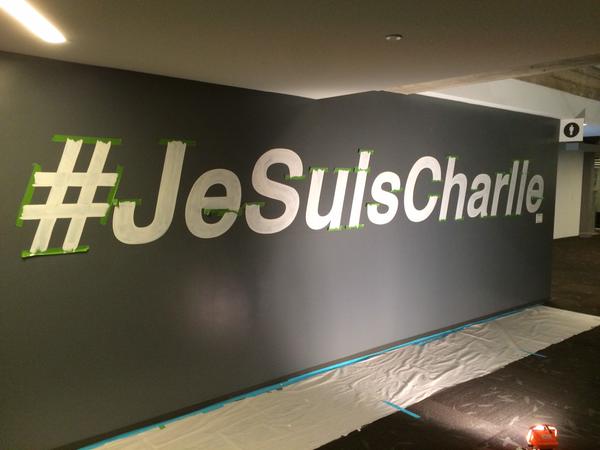
Security experts at Blue Coat have discovered that criminal criminals exploited the hashtag #JeSuisCharlie in order to spread the popular DarkComet RAT. Every time there is a clamorous event cyber criminals try to take advantage of the people’s interest to run illegal activities, it is happened recently with the incident to the Air Asia Flight and is […]
 Pierluigi Paganini
December 21, 2014
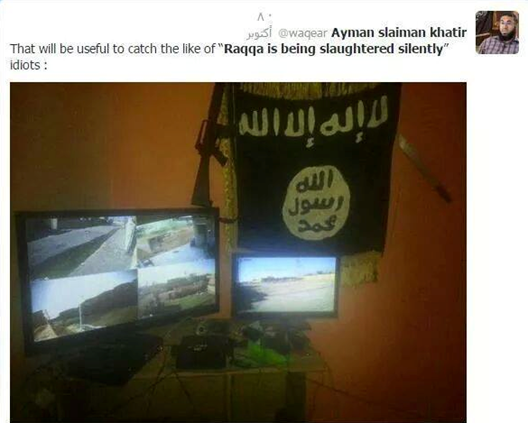
A Syrian citizen media group critical of ISIS was recently targeted in a spear phishing campaign which aim to de-anonymize its members. The Islamic State in Iraq and Syria (ISIS) is accused to have run cyber attacks against the Syrian citizen media group known as Raqqah is being Slaughtered Silently (RSS), the news was reported by […]
 Pierluigi Paganini
December 21, 2014
Experts at Dell Secure Works Counter Threat Unit (CTU) published a new report on the evolution of the hacking underground marketplaces. The monitoring of black hat markets is one the principal activities of security experts and intelligence agencies, it allows information gathering on evolution of cyber threats and emerging trends in the criminal ecosystem. In […]
 Pierluigi Paganini
November 13, 2014
Trend Micro issued a research paper on operations behind Predator Pain and Limitless keyloggers, both of which are easily obtainable from underground. Cybercriminals ordinary use malicious code to steal money from victims, the number of malware available in the criminal ecosystem is continuously growing, their level of sophistication and cost are extremely variable. Thinking of banking […]
 Pierluigi Paganini
November 01, 2014
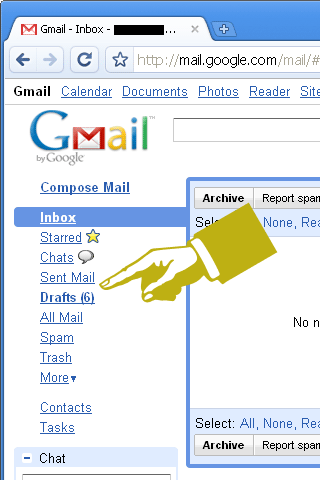
Security company Shape Security discovered a new strain of malware which is exploiting Gmail service as a communication channel with control server. Security experts at Shape Security announced to have found a new strain of malware that implements a smart technique to communicate with command and control servers, the commands are hidden in unassuming Gmail drafts that are never even […]
 Pierluigi Paganini
September 06, 2014
Expert at TrendMicro published a new chapter of the Cybercriminal Underground Economy Series in which analyzed the Chinese underground. Chinese cybercrime underground activity is rapidly increasing, according to a new interesting report published by Trend Micro the Chinese it is doubled between 2012 and 2013. The findings confirm that amount of underground activity in China doubled both with […]
 Pierluigi Paganini
August 20, 2014
Security Experts at Kaspersky Global Research & Analysis Team have discovered several malware based attacks targeting opponents of the Regime in Syria. Malware is the most diffused cyber threat used by governments to track opponents and foreign governments, in the past security experts have already detected malicious codes targeting individuals oppose to the regime of Bashar al […]
 Pierluigi Paganini
August 05, 2014
Experts at the German security firm G-Data discovered a RAT dubbed IcoScript which receives commands from C&C via email services including Yahoo and Gmail. Security experts have detected a new Remote Administration Trojan dubbed IcoScript which is controlled by bad actors through Yahoo Mail and is able to elude detection systems by using seemingly benign domains for […]
 Pierluigi Paganini
August 02, 2014
The Kaspersky Lab Team has issued a report which includes details of the investigation related to the Energetic Bear – Crouching Yeti APT campaign. Energetic Bear, aka Crouching Yeti, is the recently discovered APT campaign that targeted energy companies, manufacturers, industrial, pharmaceutical, construction, and many IT companies. Security experts have analyzed the Energetic Bear APT campaign, which appears […]

Security / October 08, 2026



