



 Pierluigi Paganini
 July 10, 2026
A former ransomware negotiator was sentenced to nearly six years for secretly helping BlackCat extort victims while betraying his clients. A U.S. court sentenced former ransomware negotiator Angelo Martino, 41, to 70 months in prison for conspiring with the BlackCat ransomware gang. While negotiating on behalf of five victims, he secretly shared confidential information about […]
 Pierluigi Paganini
July 10, 2026
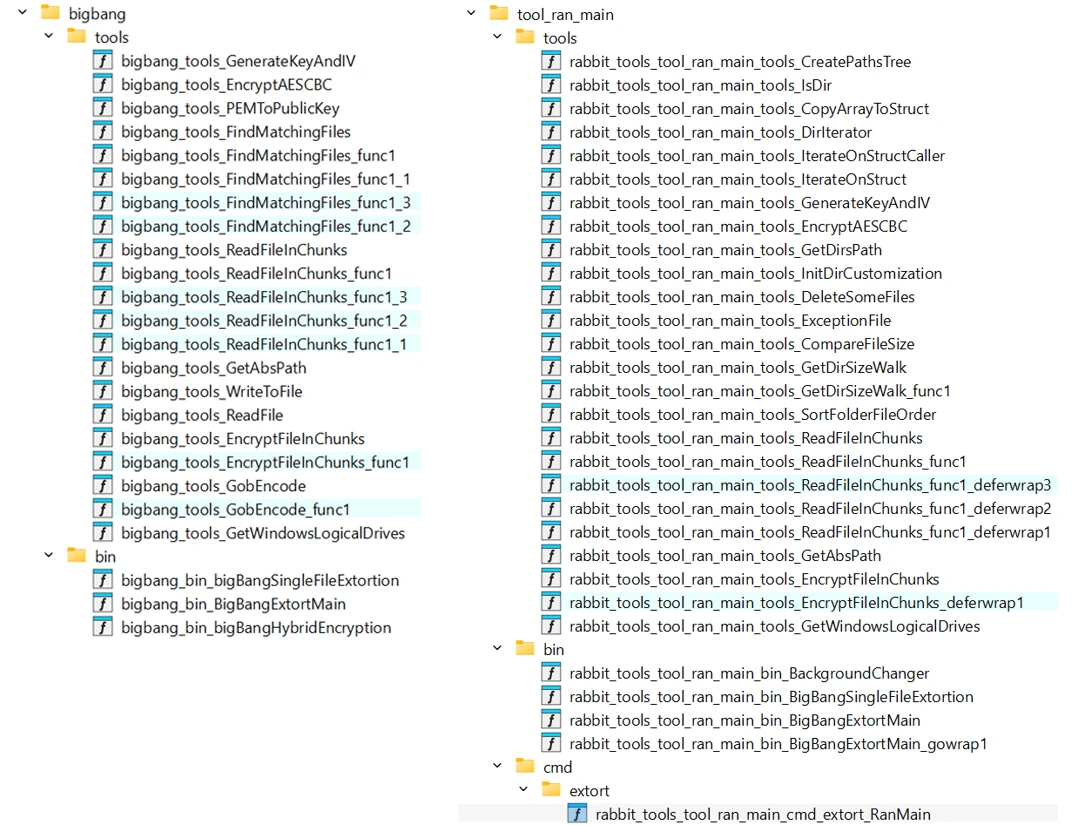
Microsoft uncovered GigaWiper, a modular Go backdoor combining three malware families with espionage, remote control, and destructive wiping features. In October 2025, Microsoft’s threat intelligence team identified destructive wiping activity inside compromised environments and traced it to a previously unknown piece of malware they’re now calling GigaWiper. The malicious code is written in Go, it […]
 Pierluigi Paganini
July 09, 2026
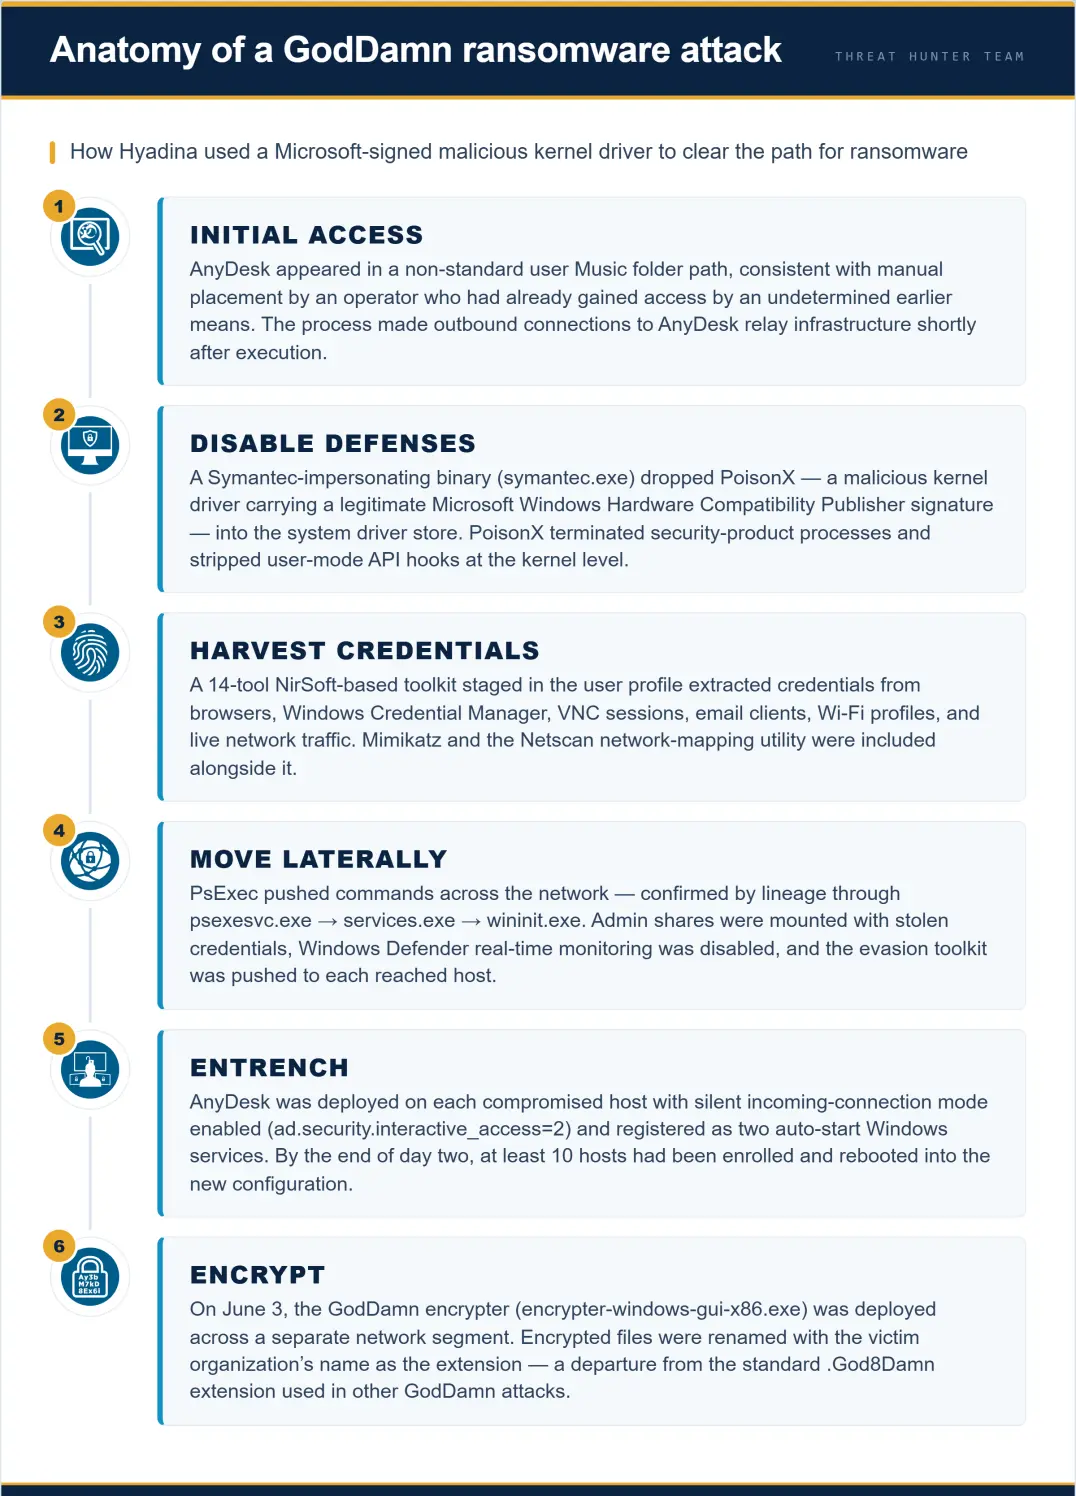
GodDamn ransomware uses the signed PoisonX driver to disable security tools, marking a more advanced version of the Beast ransomware family. Symantec’s Threat Hunter Team found a new ransomware family called GodDamn that first appeared in the wild on May 21, 2026, and analyzed an attack that took place in early June. The group behind […]
 Pierluigi Paganini
July 09, 2026
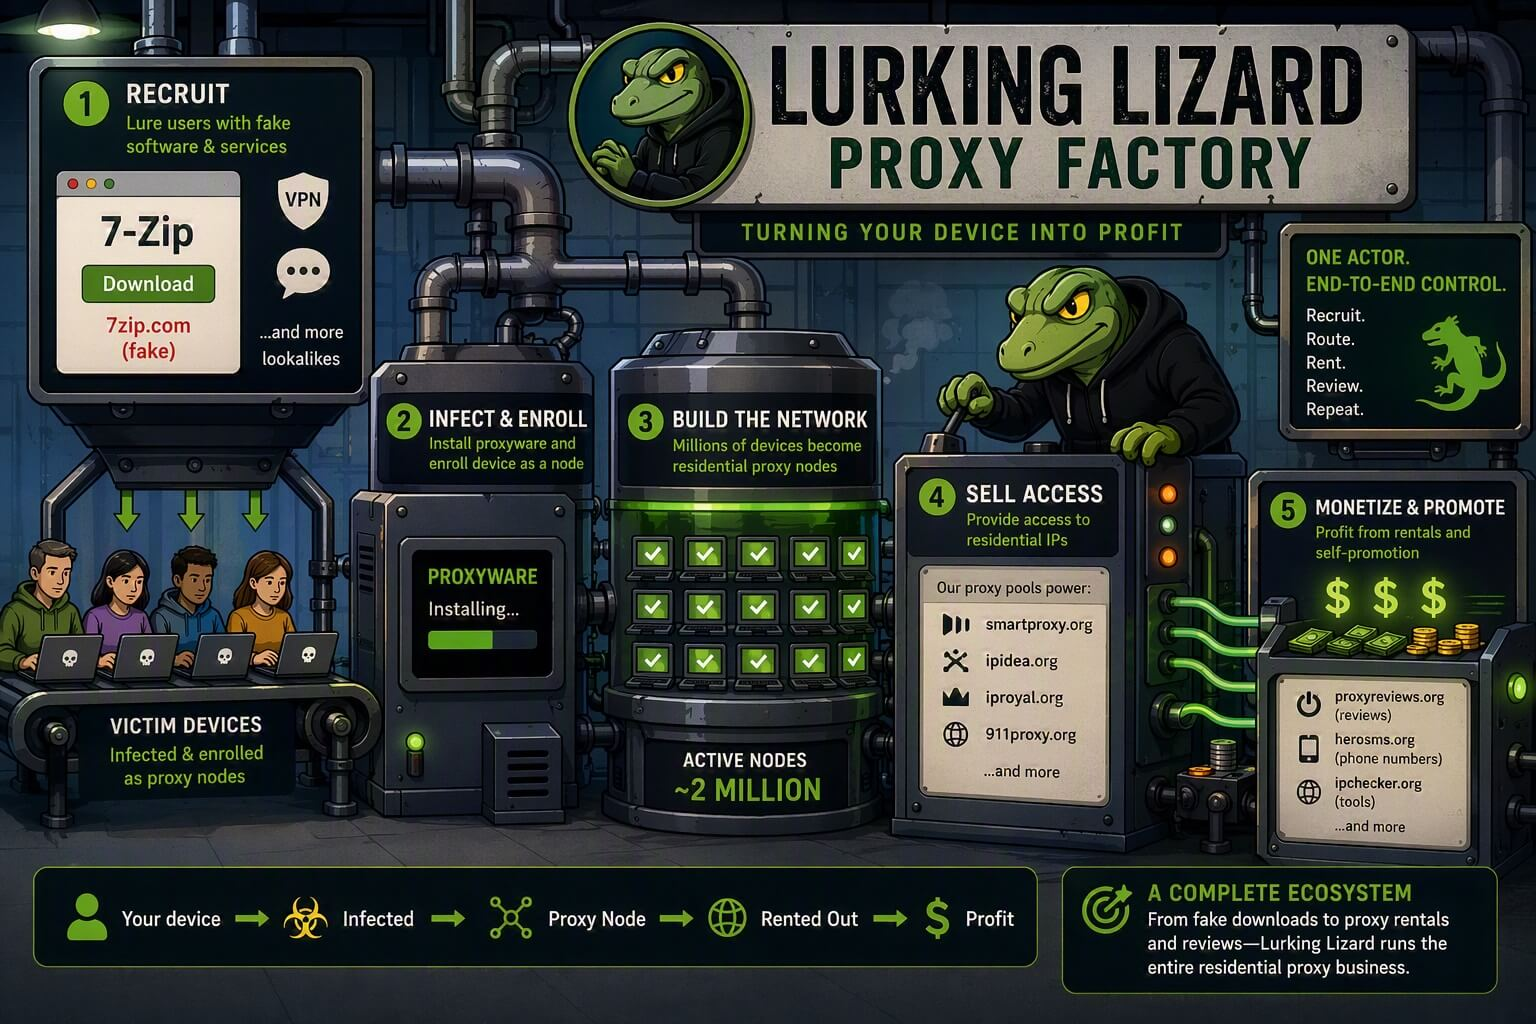
Fake apps like WireVPN and a trojanized 7-Zip turn victims’ devices into residential proxies, letting criminals route traffic through their IPs. Infoblox’s threat research team started pulling on a single thread in early 2026: a fake version of the 7-Zip archive utility hosted at 7zip[.]com instead of the real site, 7-zip[.]org. The researchers uncovered a […]
 Pierluigi Paganini
July 08, 2026
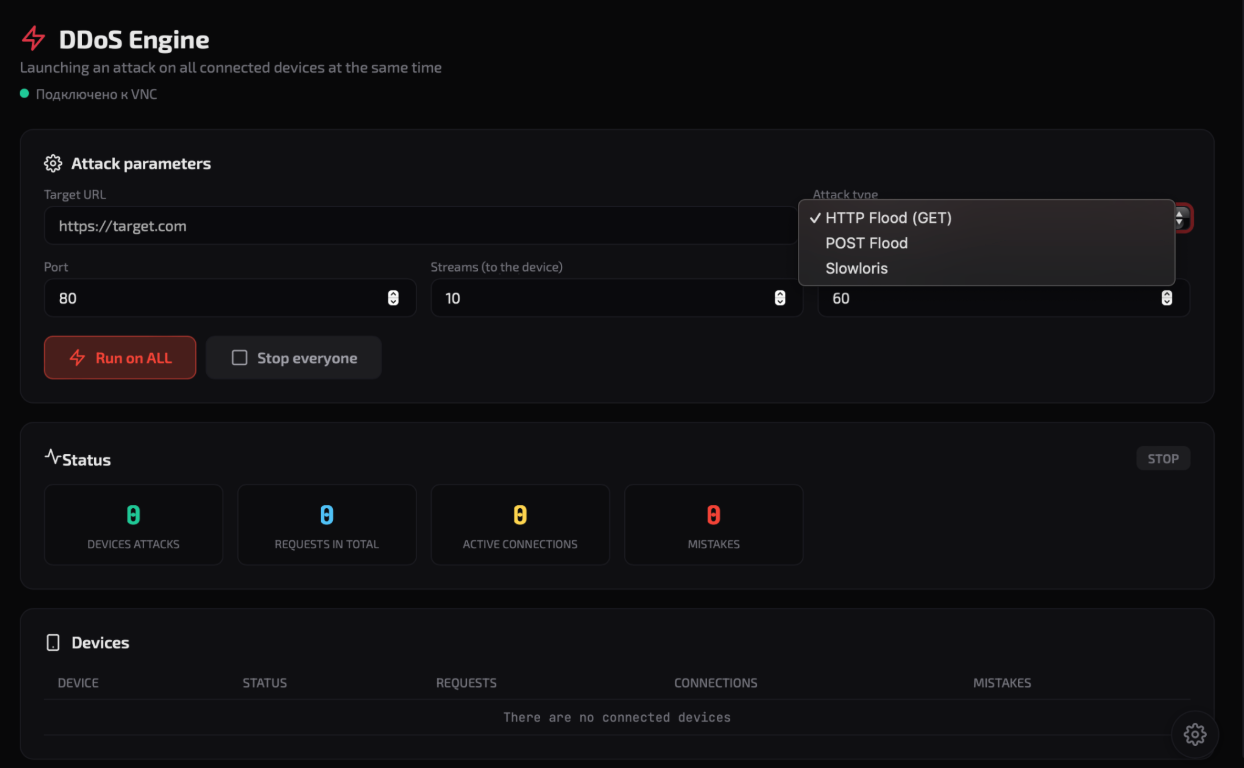
RedWing: The Android Banking Trojan You Can Rent on Telegram for Less Than a Coffee Subscription Zimperium’s zLabs team has uncovered RedWing, an Android spyware operation sold as a subscription service through Telegram, with links to Russian threat actors and apparent roots in the Oblivion malware family. It comes with documentation, tutorial videos, a referral […]
 Pierluigi Paganini
July 07, 2026
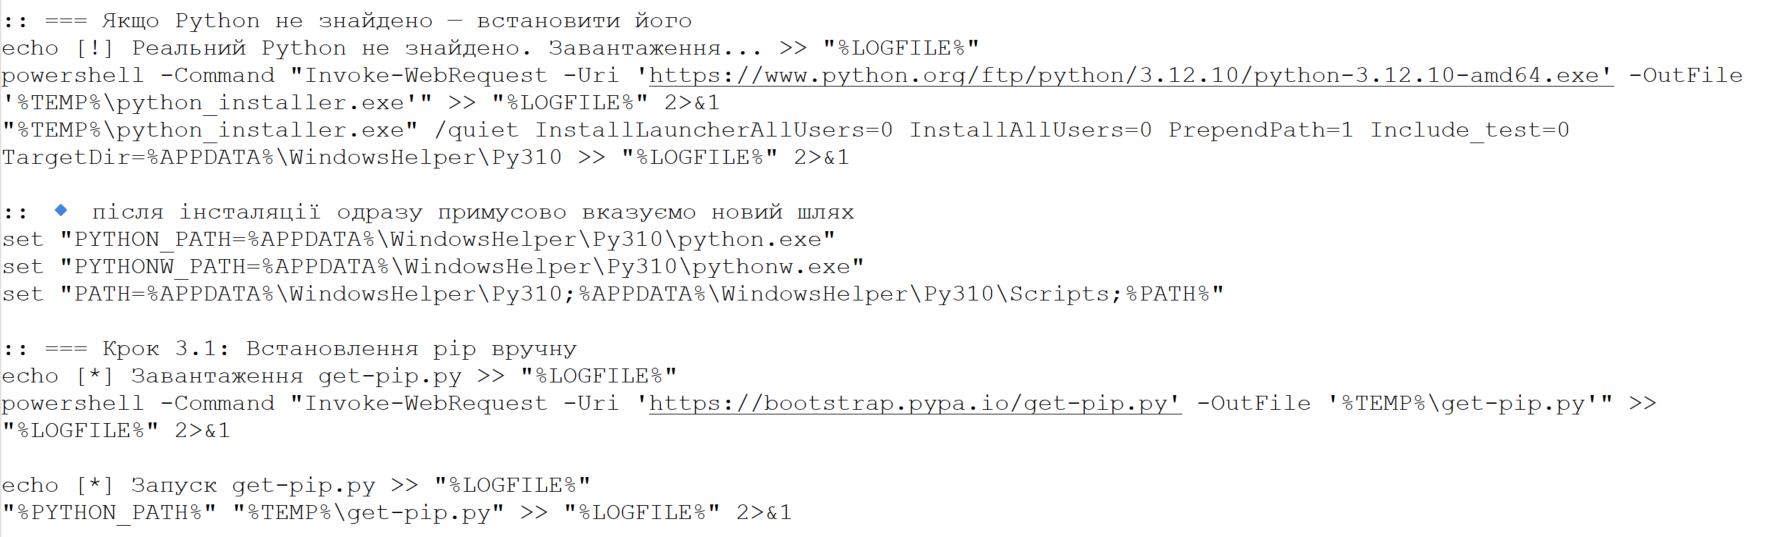
Armored Likho APT uses AI-generated malware, phishing, and BusySnake Stealer to target governments and power grids in Russia, Kazakhstan, and Brazil. Kaspersky’s threat research team has documented a previously unknown APT group they’re calling Armored Likho, also tracked under the name Eagle Werewolf. The group runs two parallel tracks: financially motivated attacks against private individuals […]
 Pierluigi Paganini
July 03, 2026
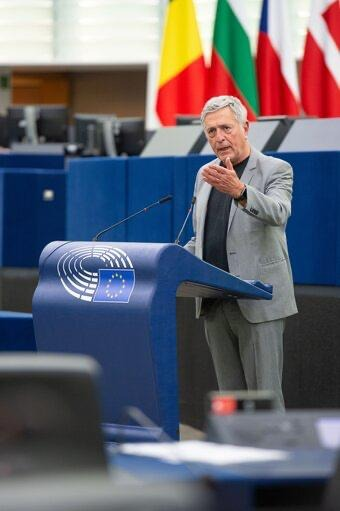
A former EU lawmaker was hacked with Pegasus spyware while investigating its use, according to Citizen Lab. The Citizen Lab published a report documenting one of the more darkly ironic findings in recent surveillance research: former Member of the European Parliament Stelios Kouloglou was repeatedly infected with NSO Group‘s Pegasus spyware while serving on the […]
 Pierluigi Paganini
July 03, 2026
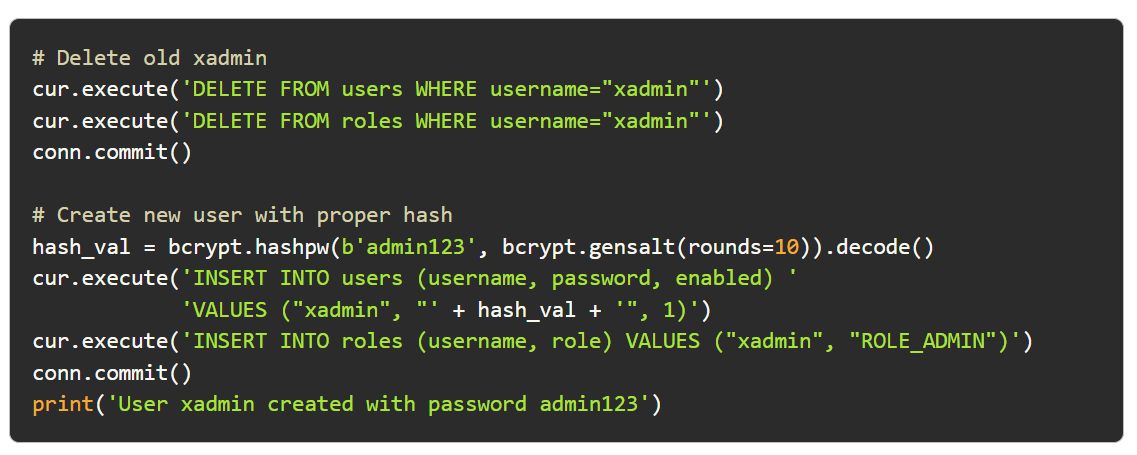
Sysdig reports an AI agent ran a full ransomware attack end-to-end, exploiting flaws, stealing creds, moving laterally, and encrypting data without humans. Sysdig’s Threat Research Team has documented what it assesses to be the first ransomware operation driven end-to-end by a large language model. The operator, which Sysdig calls JADEPUFFER, broke into a server, harvested […]
 Pierluigi Paganini
July 03, 2026
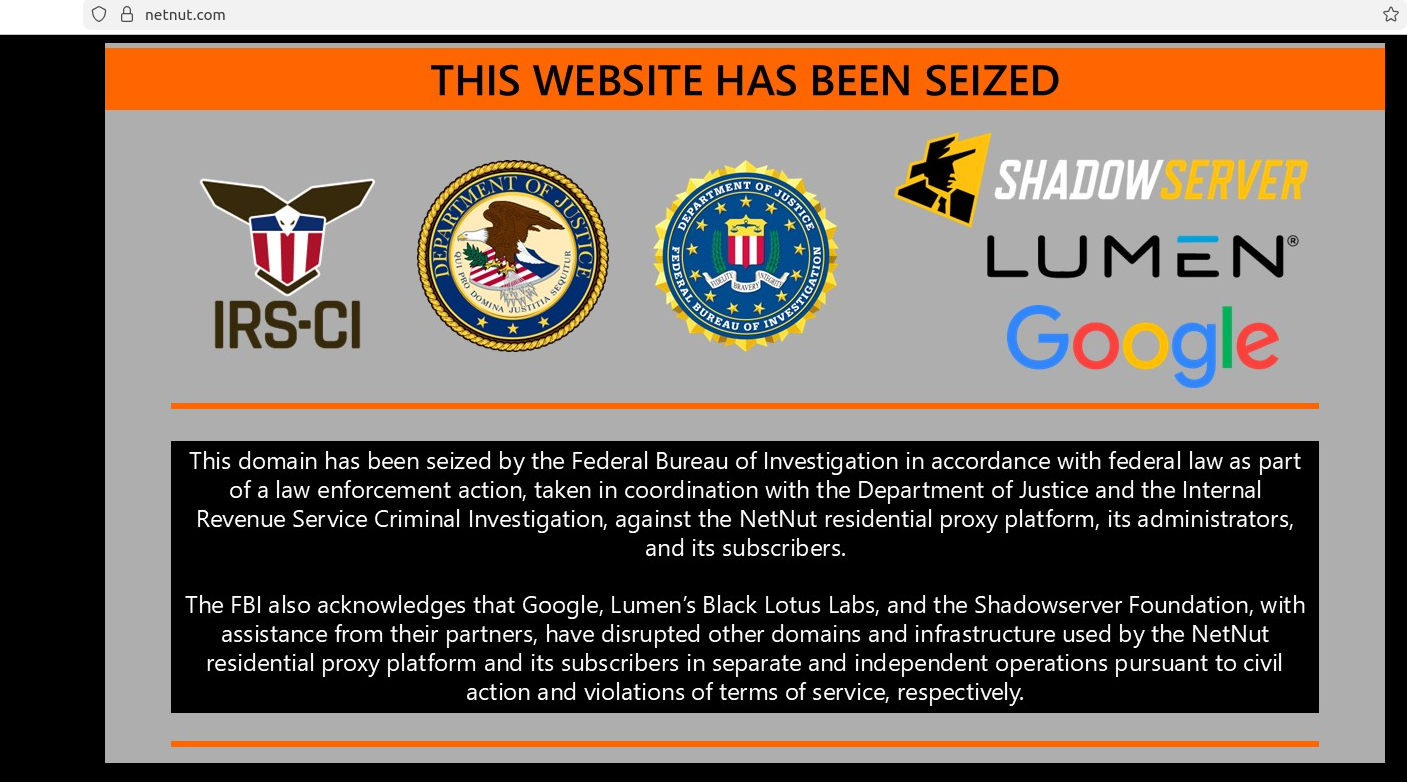
Google disrupted NetNut, a major proxy network that routed internet traffic through compromised home devices used by cybercriminals. Google has disrupted NetNut, one of the world’s largest residential proxy networks. The service routed internet traffic through home devices, allowing customers to hide their real location and identity. “Today, in coordination with the FBI, Lumen, and […]
 Pierluigi Paganini
July 02, 2026
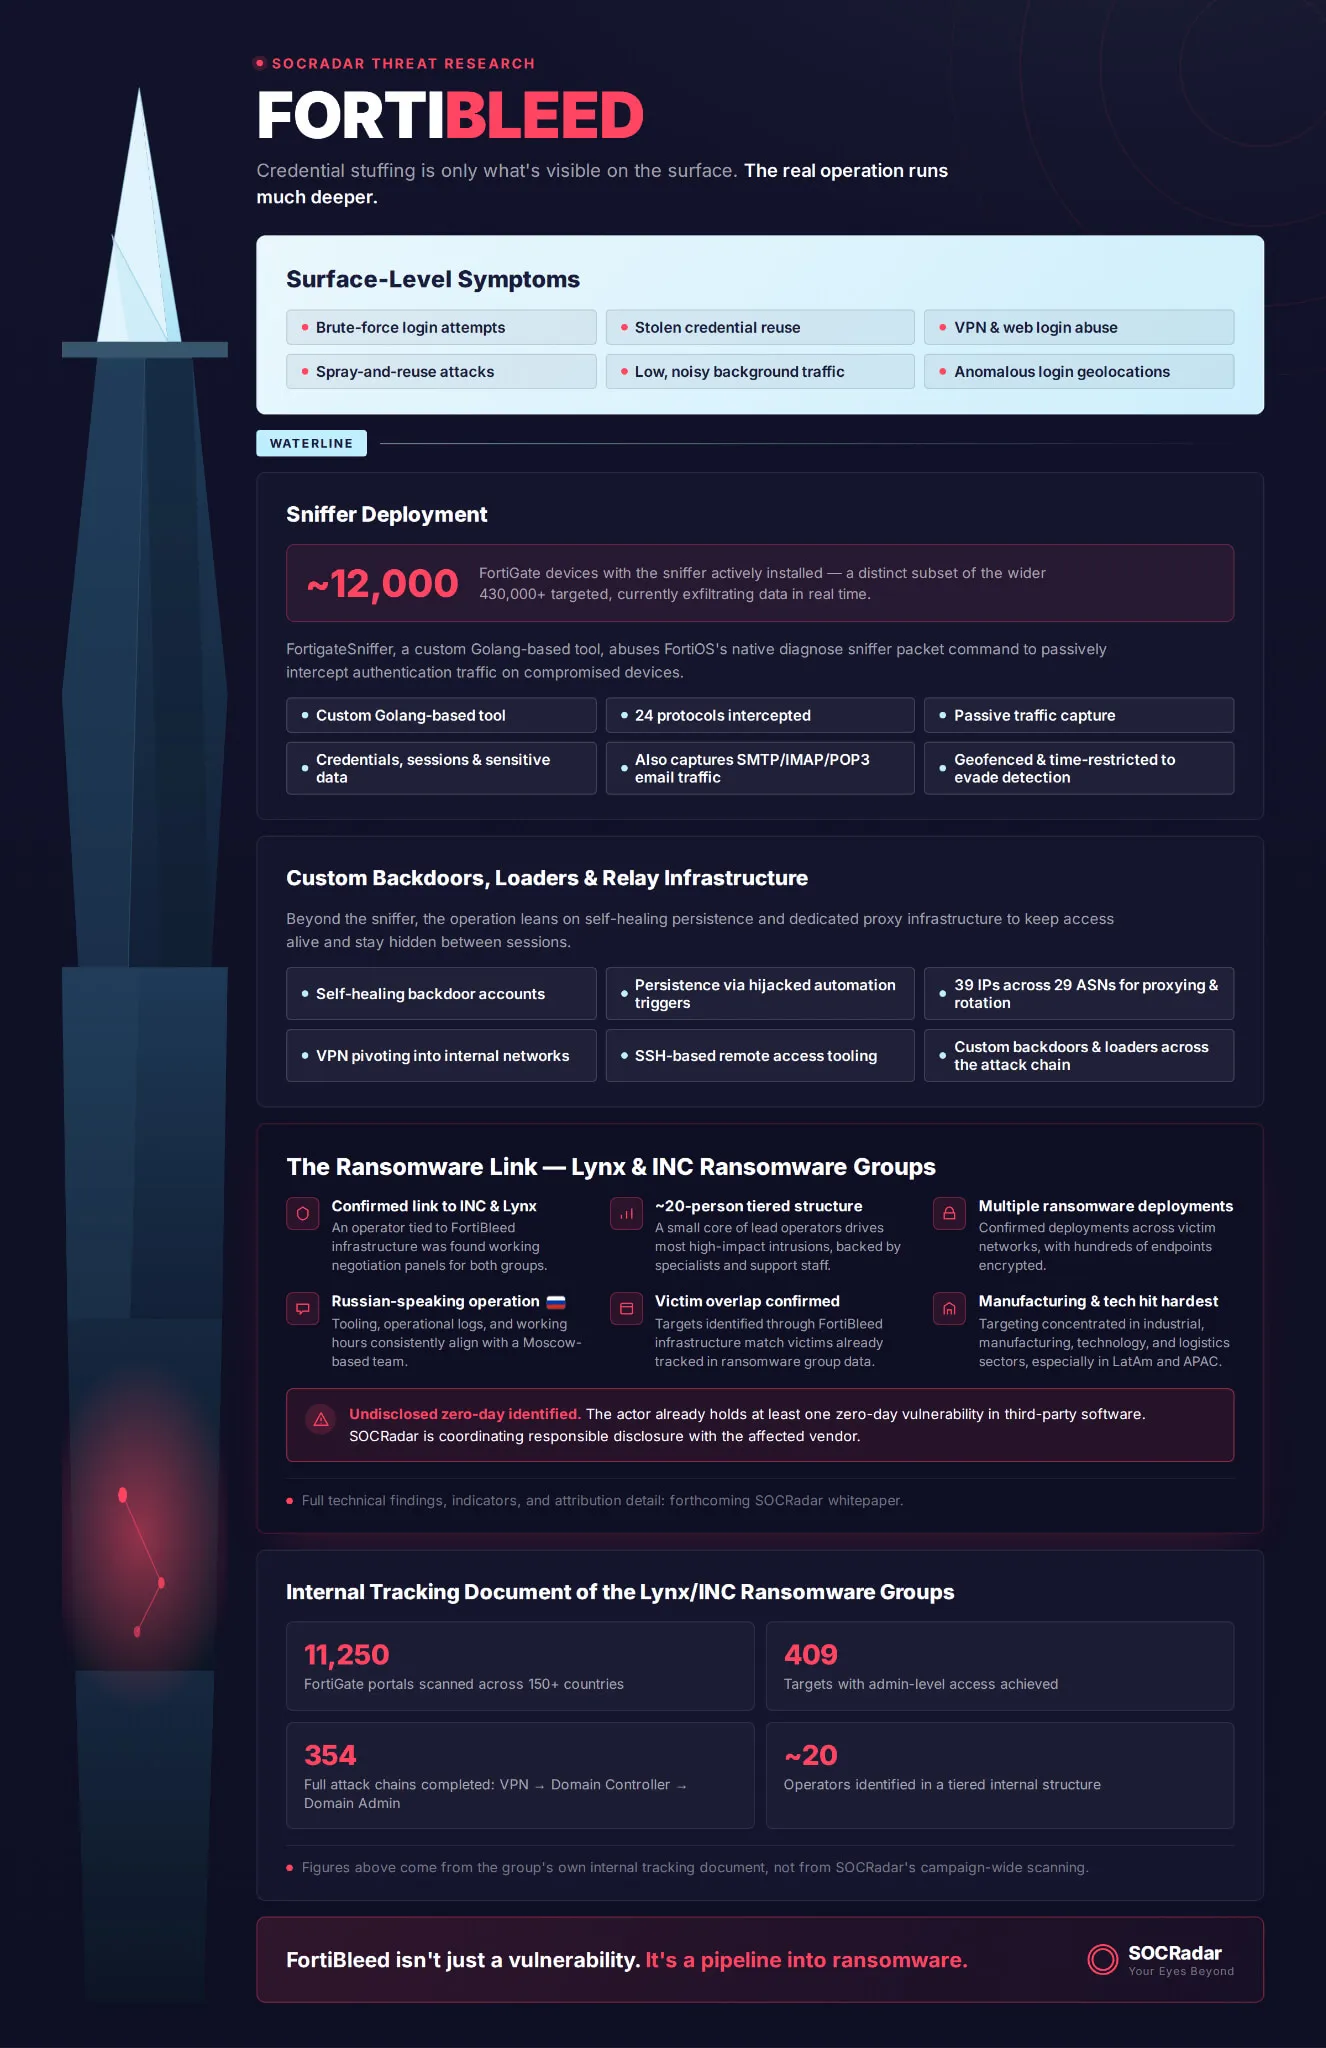
FortiBleed exposed 430,000 FortiGate firewalls, linked to INC Ransom and Lynx, enabling domain compromise and at least 12 ransomware attacks. SOCRadar’s Threat Research Unit has connected FortiBleed, a large-scale campaign that harvested credentials from over 430,000 FortiGate firewalls worldwide, directly to two active ransomware operations: INC Ransom and Lynx. The link isn’t circumstantial. An operator […]





