19319 results
 Pierluigi Paganini
 October 11, 2014
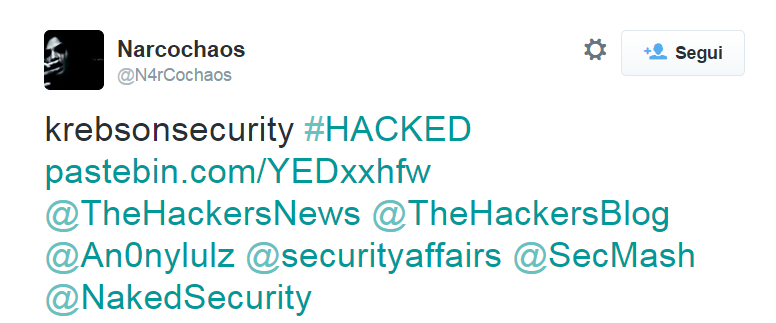
A man has published on PasteBin a fake dump of the database of the popular website KrebOnSecurity managed by the expert Brian Krebs. A few hours ago I received a tweet from the account Narcochaos (@N4rCochaos ) , which informed me and other illustrious colleagues that he has hacked the website of the popular security investigator Brian Krebs (http://krebsonsecurity.com/). […]
 Pierluigi Paganini
October 11, 2014
The Snappening, hundreds of thousands of unaware users have had their personal Snapchat photos and videos public disclosed by hackers. The Fappening is considered my mass media one of most interesting case of privacy violation, four archives containing a numerous celebrities nude photos have been released in the last weeks … and many experts sustain that the […]
 Pierluigi Paganini
October 11, 2014
An Authentication vulnerability in PayPal mobile API, discovered more than one year ago, allows access to restricted Accounts. Another authentication flaw affects PayPal mobile API, an attacker exploiting it could gain access to Blocked Accounts. The authentication restriction bypass vulnerability, resides in the mobile API authentication procedure of the PayPal online-service, according to Vulnerability Laboratory […]
 Pierluigi Paganini
October 10, 2014
A document on NCR ATM API Documentation disclosed on Baidu may have helped criminals to develop malware used in the recent attacks against ATMs worldwide. Recently Kaspersky Lab spotted a series of attacks on ATM machines which were infected by the Tyupkin malware, the malicious code is used by criminal organizations to compomise the banking machines […]
 Pierluigi Paganini
October 10, 2014
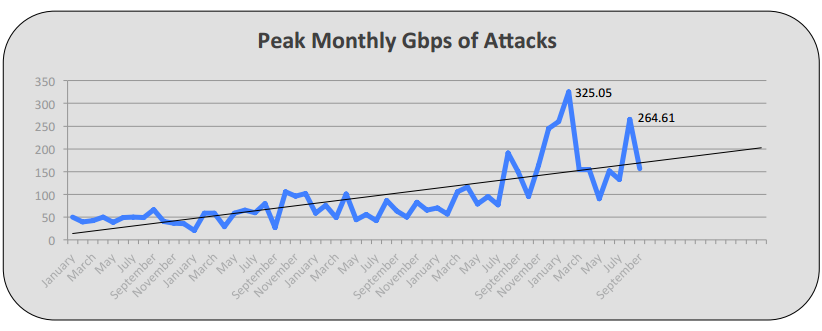
The last report issued by Arbor ATLAS Shows an increase in Reflection DDoS Attacks in Q3 2014, specifically for SSDP reflection attacks. Arbor Networks has published the quarterly report on global DDoS attack data related to Q3 2014, the slides show the distributed denial of service (DDoS) attack trends for the first three quarters of 2013. The data […]
 Pierluigi Paganini
October 10, 2014
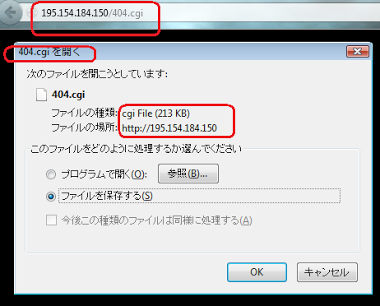
The experts at The Malware Must Die detected numerous attack worldwide exploiting the Bash Bug flaw to spread the Mayhem botnet. The researchers at Malware Must Die published a report warning of Mayhem Shellshock attack, the experts explained to have detected a significant number of Linux and UNIX systems infected by several IP addresses belonging to […]
 Pierluigi Paganini
October 09, 2014
Yahoo! Contributors Network was affected by a serious Time based Blind SQL Injection vulnerability which allows the theft of sensitive data. The Yahoo! Contributors Network allows writers to submit articles, videos, it also allows contributors to receive assignments from Yahoo related various domains like Sports and Finance. The security researcher Behrouz Sadeghipour reported to that The Yahoo! Contributors Network (contributor.yahoo.com) is […]
 Pierluigi Paganini
September 30, 2014
The Europol issued 2014 Internet Organised Crime Threat Assessment (iOCTA) report to provide details about on-going developments in the cyber criminal ecosystem. The Europol European Cybercrime Centre (EC3) has issued the 2014 Internet Organised Crime Threat Assessment (iOCTA) which describes the evolution of cybercrime an the models of sales adopted in the criminal ecosystem. This ‘Crime-as-a-Service‘ business […]
 Pierluigi Paganini
September 30, 2014
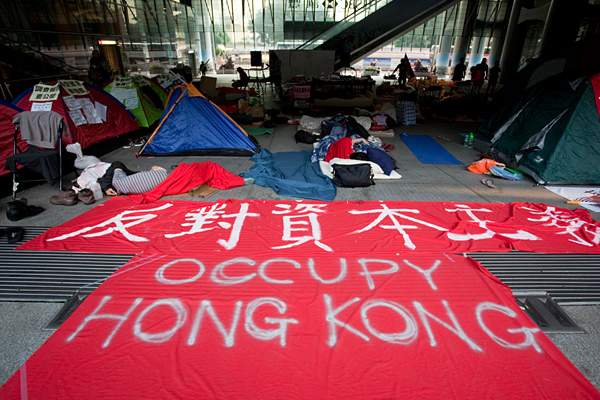
A Fake Occupy Central app containing a spyware is used by unknown to track activists in Hong Kong. Evidences suggest the involvement of Chinese entities. A Fake Occupy Central app is targeting the smartphones of the activists belonging to the Occupy Central pro-democracy movement with spyware. The malicious app has circulated online claiming to be an instrument […]
 Pierluigi Paganini
September 29, 2014
The SHA-1 cryptographic hash algorithm has been known vulnerable, Collision attacks against it are too affordable and attacks will get cheaper soon. Many websites today are using digital certificates signed using algorithms based on the hash algorithm called SHA-1. Hashing algorithms are used to ensure the integrity of the certificate in the signing processes, a flawed […]