 Pierluigi Paganini
 November 17, 2020
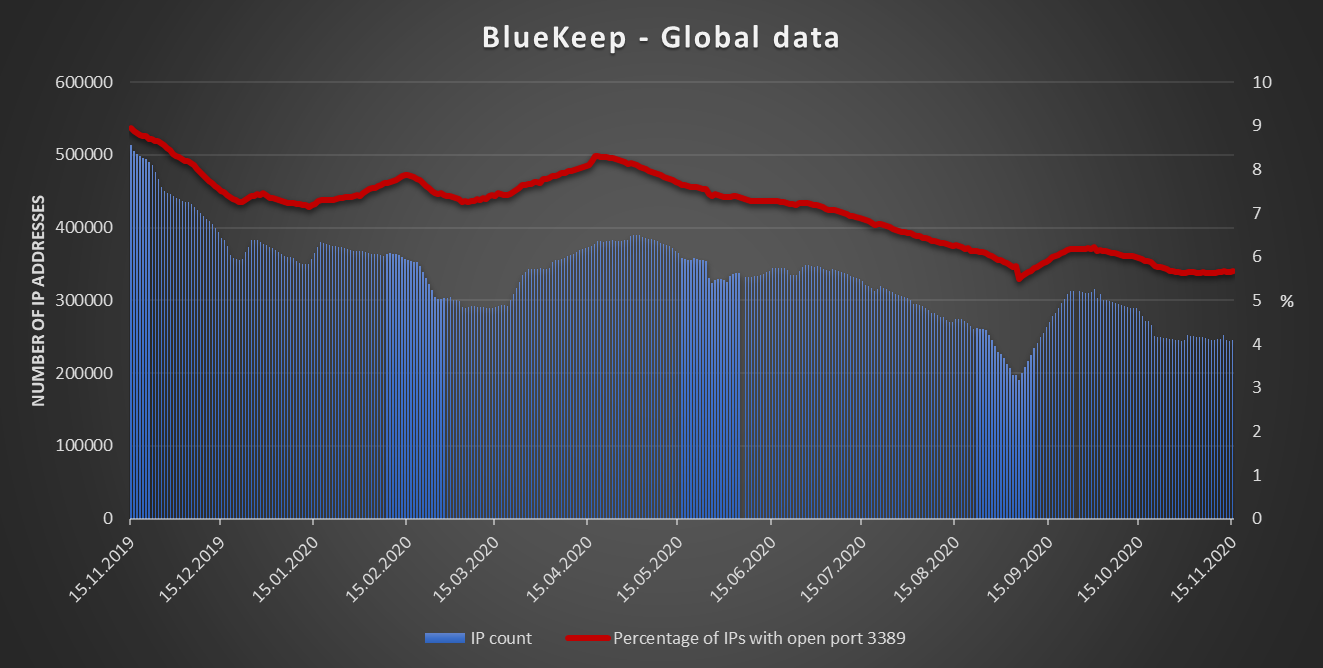
In May 2019, Microsoft disclosed the BlueKeep vulnerability, more than a year later over 245,000 Windows systems still remain unpatched. Over a year ago Microsoft Patch Tuesday updates for May 2019 addressed nearly 80 vulnerabilities, including the BlueKeep flaw. The issue is a remote code execution flaw in Remote Desktop Services (RDS) that can be exploited by […]
 Pierluigi Paganini
November 17, 2020
Boffins devised a new attack, dubbed VoltPillager, that can break the confidentiality and integrity of Intel SGX enclaves by controlling the CPU core voltage. A group of six researchers from the University of Birmingham has devised a new attack technique, dubbed VoltPillager, that can break the confidentiality and integrity of Intel Software Guard Extensions (SGX) […]
 Pierluigi Paganini
November 17, 2020
The popular video conferencing application Zoom implemented the new “At-Risk Meeting Notifier” feature to warn of Zoombombing threat. Zoom announced the launch a new feature dubbed “At-Risk Meeting Notifier” to warn conference organizers of potential Zoombombing attacks. The feature scans the web for links to Zoom meetings that have been posted online and warn organizers […]
 Pierluigi Paganini
November 16, 2020
North Korea-linked Lazarus APT group is behind new campaigns against South Korean supply chains that leverage stolen security certificates. Security experts from ESET reported that North-Korea-linked Lazarus APT (aka HIDDEN COBRA) is behind cyber campaigns targeting South Korean supply chains. According to the experts the nation-state actors leverage stolen security certificates from two separate, legitimate South […]
 Pierluigi Paganini
November 16, 2020
Experts spotted a new skimmer attack that used an alternative technique to exfiltrate payment information from payment cards. Researchers from Akamai discovered a new skimmer attack that is targeting several e-stores with a new technique to exfiltrate data. Threat actors are using fake credit card forum and WebSockets to steal the financial and personal information of the […]
 Pierluigi Paganini
November 16, 2020
Russian-speaking threat actors have been using a piece of malware, dubbed Jupyter malware, to steal information from their victims. Researchers at Morphisec have spotted Russian-speaking threat actors that have been using a piece of .NET infostealer, tracked as Jupyter, to steal information from their victims. The Jupyter malware is able to collect data from multiple […]
 Pierluigi Paganini
November 15, 2020
Retail giant The North Face has reset the passwords for some of its customers in response to a successful credential stuffing attack. Outdoor retail giant The North Face has forced a password reset for a number of its customers following a successful credential stuffing attack that took place on October 8th and 9th. Credential stuffing attacks involve botnets […]
 Pierluigi Paganini
November 15, 2020
Chilean-based retail giant Cencosud has suffered a ransomware attack that impacted operations at its stores, Egregor ransomware appears to be involved. A ransomware attack, allegedly launched by the Egregor ransomware gang, hit the Chilean-based retail giant Cencosud, the incident impacted operations at its stores. Cencosud the largest retail company in Chile and the third largest listed […]
Pierluigi Paganini
November 14, 2020
FBI and Spokane police are investigating an incident in which the Gonzaga University Black Student Union was hacked during a Zoom meeting. The FBI and Spokane police are investigating the hack of Gonzaga University Black Student Union. The hackers broke into a Zoom meeting and bombarded participants with racial and homophobic slurs. The attackers have […]
 Pierluigi Paganini
November 14, 2020
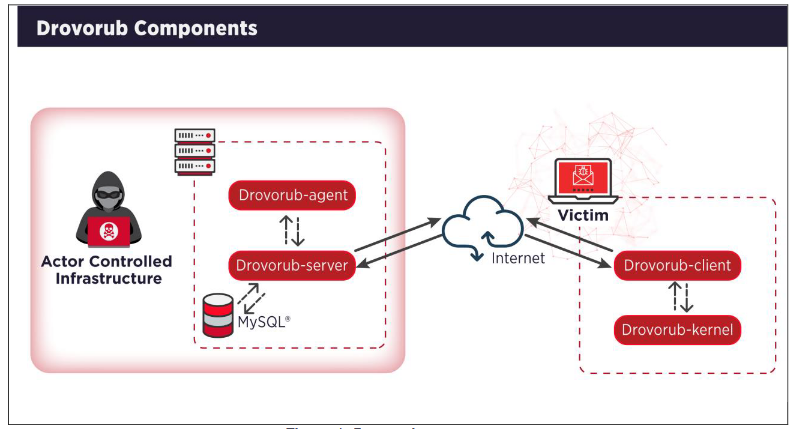
Schneider Electric is warning customers of the Drovorub Linux malware that was also analyzed recently by the NSA and the FBI. Schneider Electric published a security bulletin to warn customers of the Drovorub Linux malware, the malware was analyzed in a joint alert published in August by NSA and the FBI. According to the US […]