 Pierluigi Paganini
 May 30, 2019
Chinese Cyber-Spies Target Government Organizations in Middle East Chinese APT group Emissary Panda has been targeting government organizations in two different countries in the Middle East. Experts at Palo Alto Networks reported that the Chinese APT group Emissary Panda (aka APT27, TG-3390, Bronze Union, and Lucky Mouse) has been targeting government organizations in two different […]
 Pierluigi Paganini
May 30, 2019
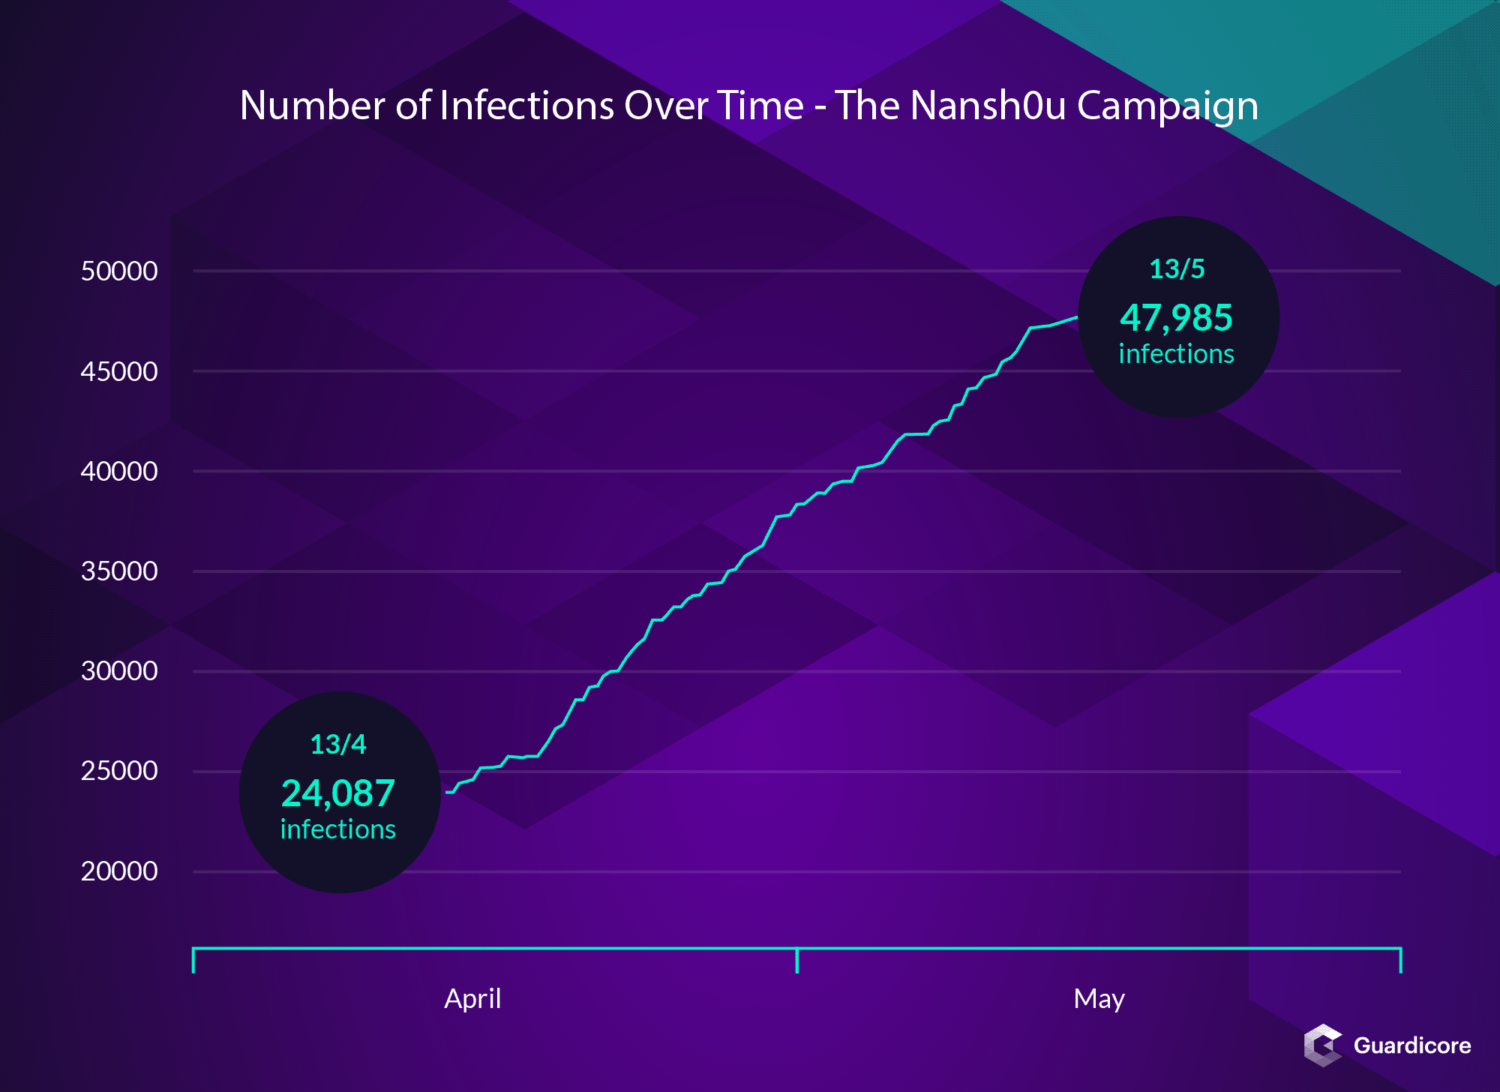
Guardicore Labs uncovered a widespread cryptojacking campaign tracked as Nansh0u and aimed at Windows MS-SQL and PHPMyAdmin servers. Security experts at Guardicore Labs uncovered a widespread cryptojacking campaign leveraging a malware dubbed Nansh0u. The malicious code aimed at Windows MS-SQL and PHPMyAdmin servers worldwide. According to the experts, the malicious campaign is being carried out […]
 Pierluigi Paganini
May 29, 2019
The popular white hat hacker Tavis Ormandy has announced the discovery of a code execution vulnerability in Microsoft’s Notepad text editor. The Google Project Zero researcher Tavis Ormandy announced the discovery of a code execution flaw in Microsoft’s Notepad text editor. Ormandy reported the issue to Microsoft and will wait 90 days according to Google vulnerability […]
 Pierluigi Paganini
May 29, 2019
Public Wi-Fi is easily accessible by everyone, as much as free surfing sounds cool, it is risky as well. Let’s see how your data can be hacked easily. In the contemporary world of networking, Wi-Fi has become a vital commodity. Wi-Fi are now installed in each and every place regardless of the size of the […]
 Pierluigi Paganini
May 29, 2019
A race condition flaw that could be exploited by an attacker to read and write any file on the host system affects any versions of Docker. Experts found a race condition vulnerability in any versions of Docker, the vulnerability could be exploited by an attacker to read and write any file on the host system. […]
 Pierluigi Paganini
May 29, 2019
An attack against an Italian organization lead the experts at Yoroi-Cybaze ZLab to shed the light on ongoing operations attributed to TA505. Introduction In the last few days, during monitoring activities, Yoroi CERT noticed a suspicious attack against an Italian organization. The malicious email contains a highly suspicious sample which triggered the ZLAB team to […]
 Pierluigi Paganini
May 28, 2019
The DuckDuckGo Privacy Browser application 5.26.0 for Android allows address bar spoofing via a setInterval call, as demonstrated by reloading every 50 ms. Technical Observation: A browser that’s scoring in the 50,00,000+ tier of Android download.It was observed that the DuckDuckGo privacy browser ominibar can be spoofed by a crafted javascript page spoofing `setInterval` function and reloading the […]
 Pierluigi Paganini
May 28, 2019
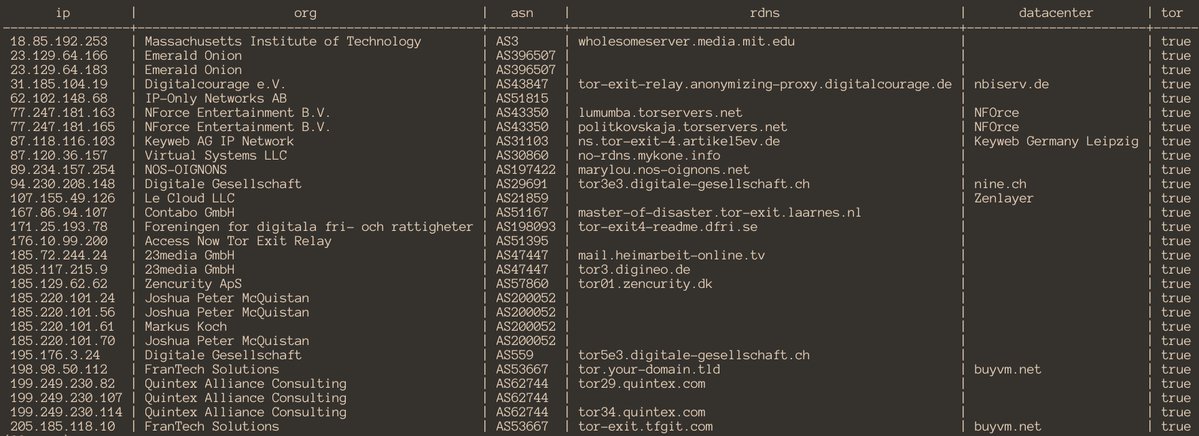
Roughly one million devices are vulnerable to attacks exploiting the BlueKeep Windows vulnerability and hackers are ready to hit them. Yesterday I reported the discovery made by experts at GreyNoise that detected scans for systems vulnerable to the BlueKeep (CVE-2019-0708) vulnerability. The scans were first detected on May 25, 2019, experts explained that a single […]
 Pierluigi Paganini
May 28, 2019
Several products made by Siemens Healthineers are affected by a recently patched Windows BlueKeep vulnerability (CVE-2019-0708). The BlueKeep issue is a remote code execution vulnerability in Remote Desktop Services (RDS) that it can be exploited by an unauthenticated attacker by connecting to the targeted system via the RDP and sending specially crafted requests. As explained by […]
 Pierluigi Paganini
May 28, 2019
The APT10 group has added two new malware loaders to its arsenal and used in attacks aimed at government and private organizations in Southeast Asia. In April 2019, China-linked cyber-espionage group tracked as APT10 has added two new loaders to its arsenal and used it against government and private organizations in Southeast Asia. The group […]