 Pierluigi Paganini
 November 29, 2020
The Dark Caracal APT group has carried out a series of attacks against multiple sectors using a new variant of a 13-year-old backdoor Trojan. The Dark Caracal cyberespionage group is back, researchers from Check Point uncovered a new series of attack against multiple industries. The Dark Caracal is an APT group associated with the Lebanese […]
 Pierluigi Paganini
November 27, 2020
The Reuters agency revealed in an exclusive that the COVID vaccine maker AstraZeneca was targeted by alleged North Korea-linked hackers. According to a report published by Reuters, suspected North Korea-linked hackers targeted AstraZeneca, one of the companies that are developing a COVID vaccine. The attack attempts took place in recent weeks, two people with knowledge […]
 Pierluigi Paganini
November 22, 2020
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. Chilean-based retail giant Cencosud hit by Egregor Ransomware ShinyHunters hacked Pluto TV service, 3.2M accounts exposed The North Face website suffered a credential stuffing attack Crooks use software skimmer that […]
 Pierluigi Paganini
November 16, 2020
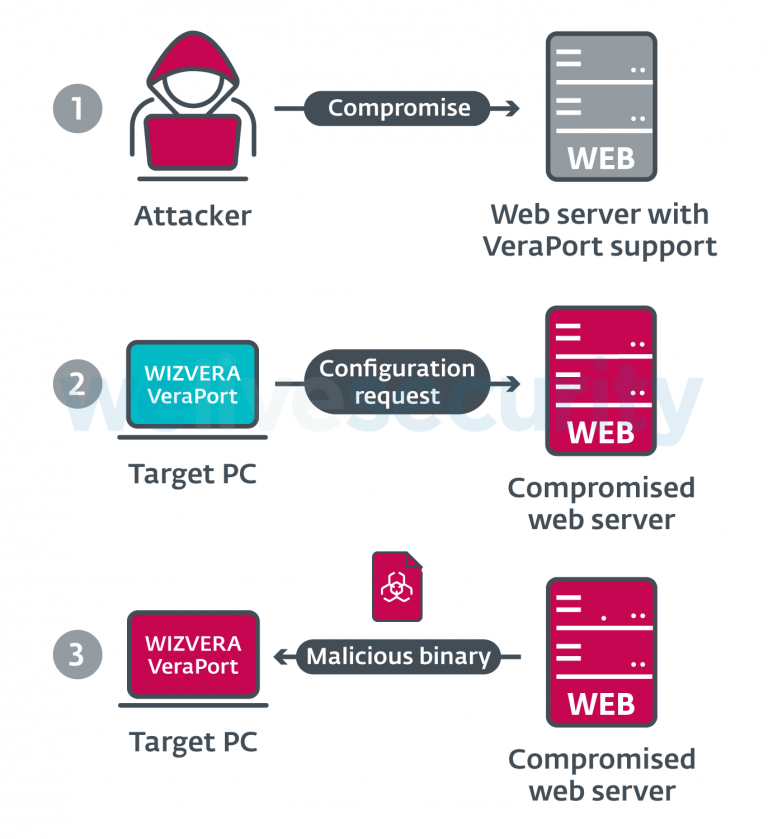
North Korea-linked Lazarus APT group is behind new campaigns against South Korean supply chains that leverage stolen security certificates. Security experts from ESET reported that North-Korea-linked Lazarus APT (aka HIDDEN COBRA) is behind cyber campaigns targeting South Korean supply chains. According to the experts the nation-state actors leverage stolen security certificates from two separate, legitimate South […]
 Pierluigi Paganini
November 13, 2020
At least the three nation-state actors have targeted seven COVID-19 vaccine makers, they are Strontium, Lazarus Group, and Cerium, Microsoft warns. Microsoft revealed that at least three APT groups have targeted seven companies involved in COVID-19 vaccines research and treatments. “In recent months, we’ve detected cyberattacks from three nation-state actors targeting seven prominent companies directly […]
 Pierluigi Paganini
November 12, 2020
CostaRicto APT is targeting South Asian financial institutions and global entertainment companies with undocumented malware. Blackberry researchers have documented the activity of a hackers-for-hire group, dubbed CostaRicto, that has been spotted using a previously undocumented piece of malware to target South Asian financial institutions and global entertainment companies. “During the past six months, the BlackBerry Research […]
 Pierluigi Paganini
November 05, 2020
A new Chinese APT group, tracked as KilllSomeOne, appeared in the threat landscape targeting corporate organizations in Myanmar. A new Chinese APT group, tracked as KilllSomeOne, was spotted by researchers at Sophos. The advanced cyber-espionage group is targeting corporate organizations in Myanmar with DLL side-loading attacks. The name KilllSomeOne comes from the phrase ‘KilllSomeOne’ used […]
 Pierluigi Paganini
November 02, 2020
North Korea-linked APT group Kimsuky was recently spotted using a new piece of malware in attacks on government agencies and human rights activists. North Korea-linked cyber espionage group Kimsuky (aka Black Banshee, Thallium, Velvet Chollima) was recently observed using a new malware in attacks aimed at government agencies and human rights activists. The Kimsuky APT […]
Pierluigi Paganini
November 01, 2020
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. HPE addresses critical auth bypass issue in SSMC console Is the Abaddon RAT the first malware using Discord as C&C? New Emotet attacks use a new template urging recipients to […]
 Pierluigi Paganini
October 29, 2020
US Cyber Command published technical details on malware implants used by Russia-linked APTs on multiple parliaments, embassies US Cyber Command shared technical details about malware implants employed by Russian hacking groups in attacks against multiple ministries of foreign affairs, national parliaments, and embassies. Experts from the US Cyber Command’s Cyber National Mission Force (CNMF) unit […]