 Pierluigi Paganini
 August 13, 2020
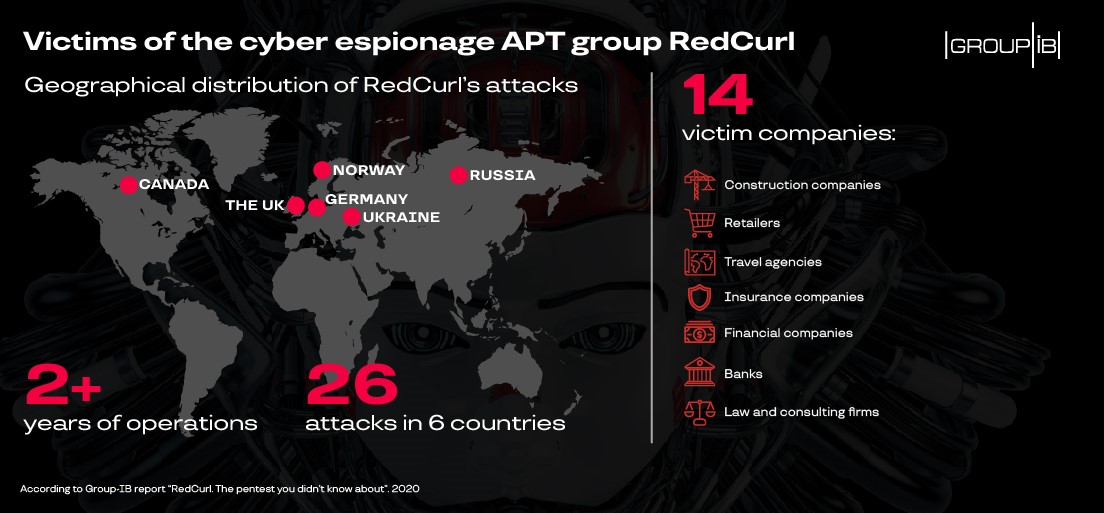
Threat Intel firm Group-IB has released an analytical report on the previously unknown APT group RedCurl, which focuses on corporate espionage Group-IB, a global threat hunting and intelligence company headquartered in Singapore, has released an analytical report on the previously unknown APT group RedCurl, which focuses on corporate espionage. In less than three years, RedCurl […]
 Pierluigi Paganini
July 16, 2020
CIA orchestrated dozens of hacking operations against targets worldwide, including APT34 and FSB hacks, states an exclusive report from Yahoo News. In 2018, US President Trump gave to the Central Intelligence Agency (CIA) more powers to conduct covert offensive cyber operations against hostile threat actors, including Iranian and Russian APT groups and intelligence agencies. In […]
 Pierluigi Paganini
July 11, 2020
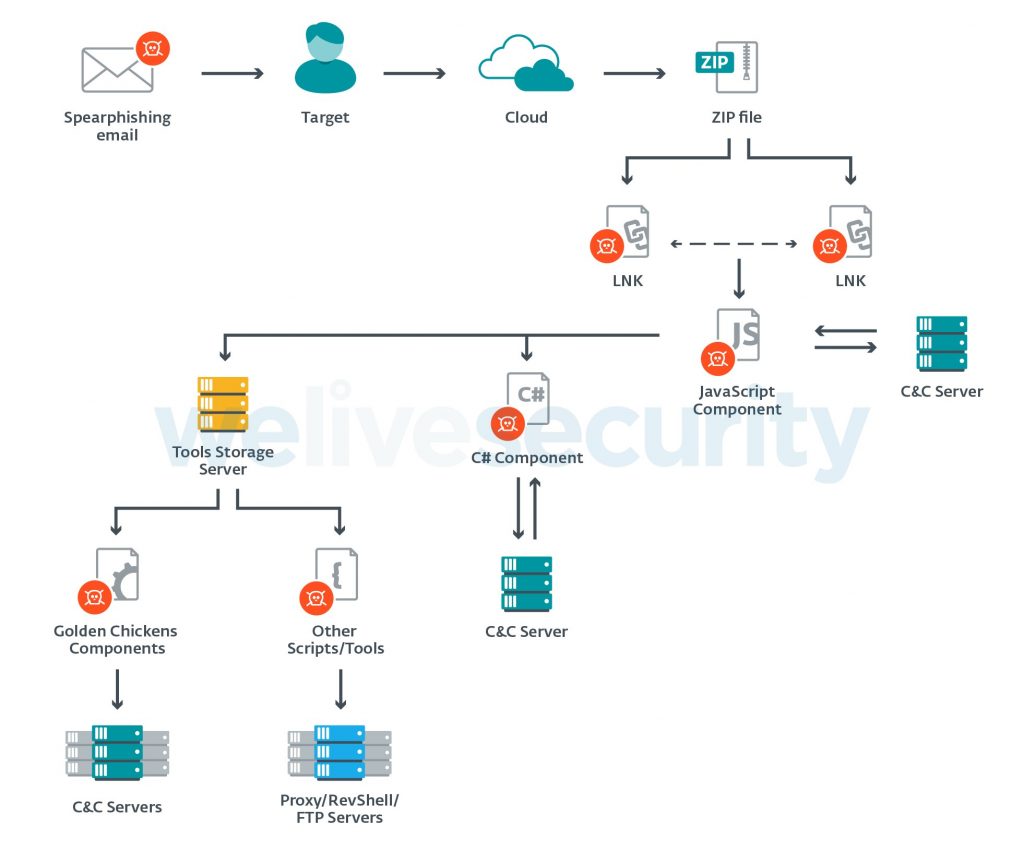
A threat actor tracked as Evilnum targeted financial technology companies, mainly the British and European ones, ESET researchers reported. Evilnum threat actor was first spotted in 2018 while using the homonym malware. Over the years, the group added new tools to its arsenal, including custom and homemade malware along with software purchased from the Golden […]
 Pierluigi Paganini
July 06, 2020
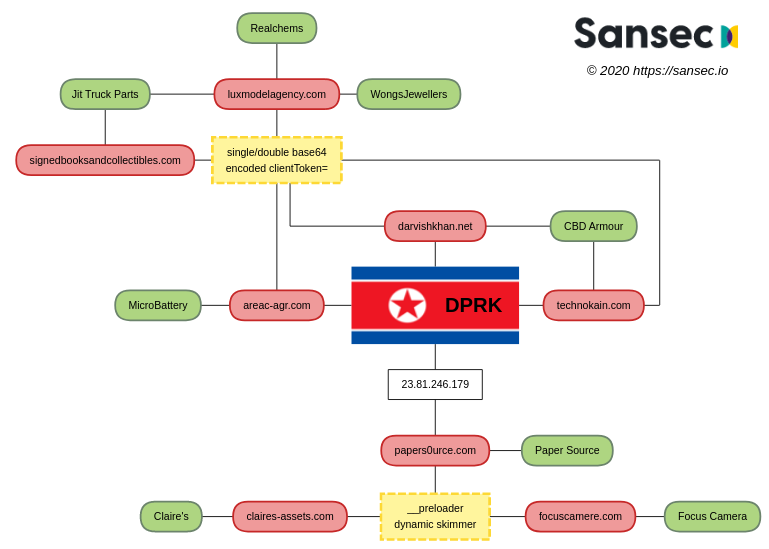
North Korea-linked Lazarus APT has been stealing payment card data from customers of large retailers in the U.S. and Europe for at least a year. Sansec researchers reported that North Korea-linked Lazarus APT group has been stealing payment card information from customers of large retailers in the U.S. and Europe for at least a year. […]
 Pierluigi Paganini
June 19, 2020
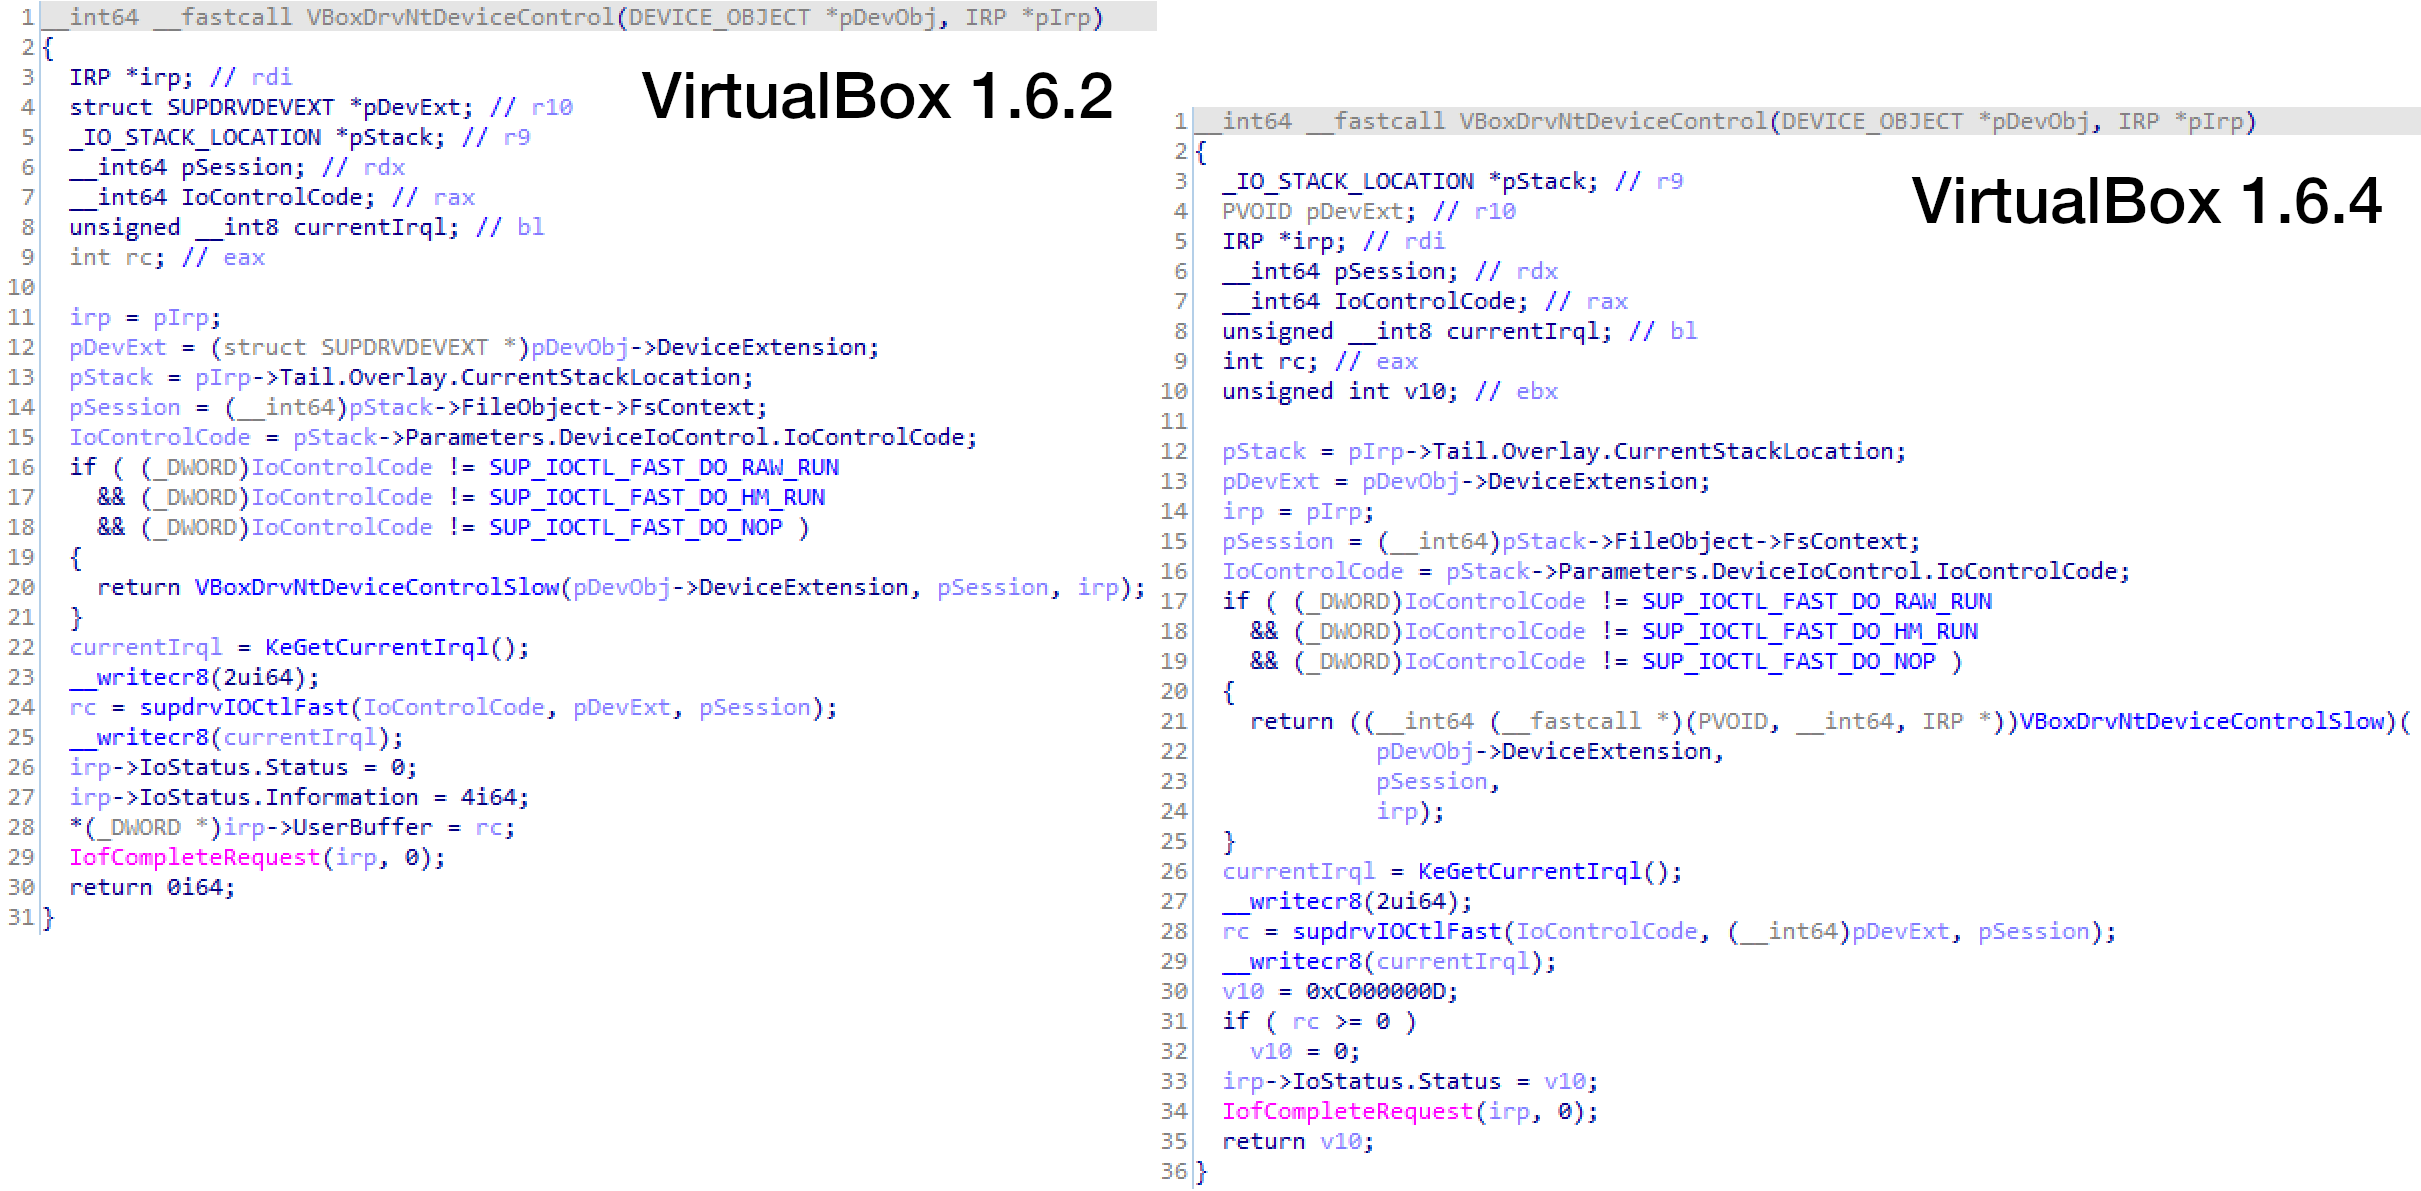
New AcidBox Malware employed in targeted attacks leverages an exploit previously associated with the Russian-linked Turla APT group. Palo Alto Networks researchers analyzed a new malware, dubbed AcidBox, that was employed in targeted attacks and that leverages an exploit previously associated with the Russian-linked Turla APT group. The Turla APT group (aka Snake, Uroburos, Waterbug, Venomous Bear and KRYPTON) has been active since at […]
 Pierluigi Paganini
June 17, 2020
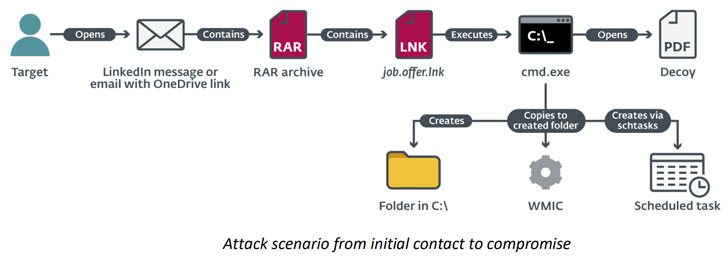
Experts uncovered a new cyber-espionage campaign, dubbed “Operation In(ter)reception,” aimed at aerospace and military organizations in Europe and the Middle East. Security experts from ESET uncovered a new sophisticated cyber-espionage campaign, dubbed “Operation In(ter)reception,” aimed at aerospace and military organizations in Europe and the Middle East. The attackers were attempting to spy on key employees […]
 Pierluigi Paganini
June 12, 2020
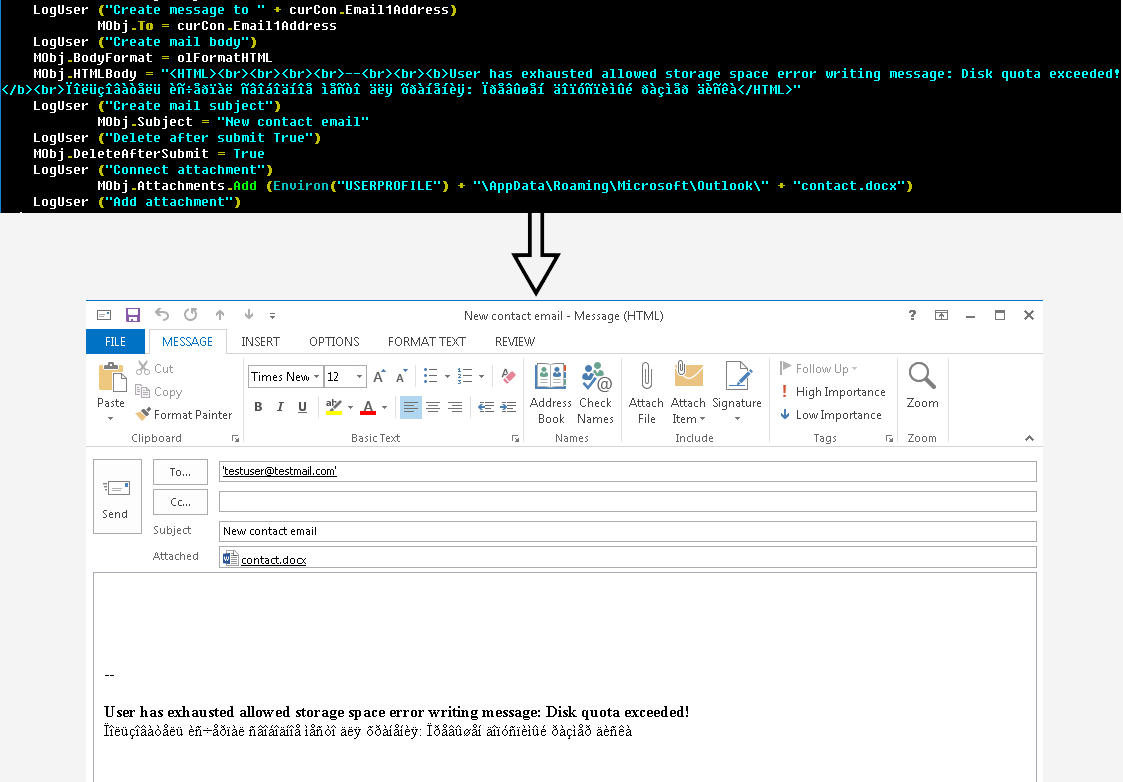
Russia-linked Gamaredon APT use a new module for Microsoft Outlook that creates custom emails with malicious documents and sends them to a victim’s contacts. Reseaerchers from ESET reported that Russia-linked Gamaredon APT has a new tool in its arsenal, it is a module for Microsoft Outlook that creates custom emails with malicious documents and sends […]
 Pierluigi Paganini
June 04, 2020
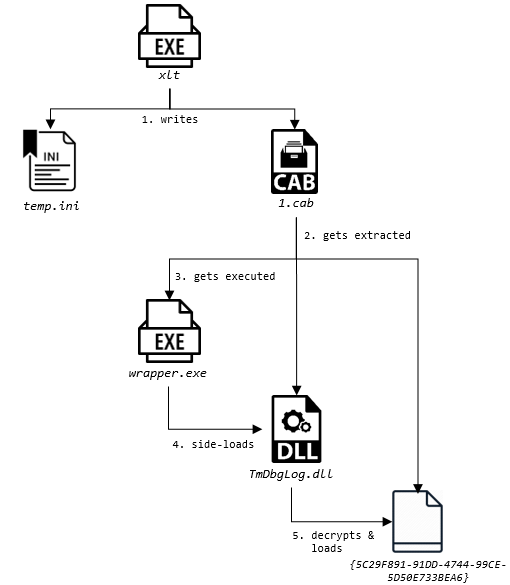
A Chinese threat actor tracked as Cycldek (aka Goblin Panda, or Conimes) has developed new tool to steal information from air-gapped systems. Security experts from Kaspersky Lab reported that the Chinese threat actor tracked as Cycldek (aka Goblin Panda, or Conimes) has developed new tool to steal information from air-gapped systems. The Cycldek group was […]
 Pierluigi Paganini
May 28, 2020
The U.S. NSA warns that Russia-linked APT group known as Sandworm Team have been exploiting a critical flaw in the Exim mail transfer agent (MTA). The U.S. National Security Agency (NSA) is warning that Russia-linked APT group tracked Sandworm Team has been exploiting a critical vulnerability (CVE-2019-10149) in the Exim mail transfer agent (MTA) software since […]
 Pierluigi Paganini
May 28, 2020
The Ke3chang hacking group added a new malware dubbed Ketrum to its arsenal, it borrows portions of code and features from older backdoors. The Ke3chang hacking group (aka APT15, Vixen Panda, Playful Dragon, and Royal APT) has developed new malware dubbed Ketrum by borrowing parts of the source code and features from their older Ketrican and […]