 Pierluigi Paganini
 April 24, 2019
Security researchers at Yoroi-Cybaze ZLab uncovered a new campaign carried out by the Russian state-actor dubbed Gamaredon. Introduction Few days after the publication of our technical article related to the evidence of possible APT28 interference in the Ukrainian elections, we spotted another signal of a sneakier on-going operation. This campaign, instead, seems to be linked […]
 Pierluigi Paganini
April 24, 2019
Iran-linked OilRig cyberespionage group is using the reconnaissance malware Karkoff along with DNSpionage in recent campaigns.Iran-linked OilRig cyberespione group is using the reconnaissance malware Karkoff along with DNSpionage in recent campaigns. The OilRig APT group, the threat actor behind the DNSpionage malware campaign, is carrying out a new sophisticated and targeted operation that infects victims […]
 Pierluigi Paganini
April 18, 2019
Iran-linked APT group OilRig is heavily leveraging on DNS tunneling for its cyber espionage campaigns, Palo Alto Networks reveals. Security researchers at Palo Alto Networks reported that Iran-linked APT group OilRig is heavily leveraging on DNS tunneling for its cyber espionage campaigns, Palo Alto Networks reveals. OilRig is an Iran-linked APT group that has been […]
 Pierluigi Paganini
April 11, 2019
According to a joint report published by the United States Department of Homeland Security (DHS) and Federal Bureau of Investigation (FBI), North Korea-linked Lazarus APT group is using a new Trojan in attacks. According to a joint report issued by the United States Department of Homeland Security (DHS) and Federal Bureau of Investigation (FBI), North […]
 Pierluigi Paganini
April 10, 2019
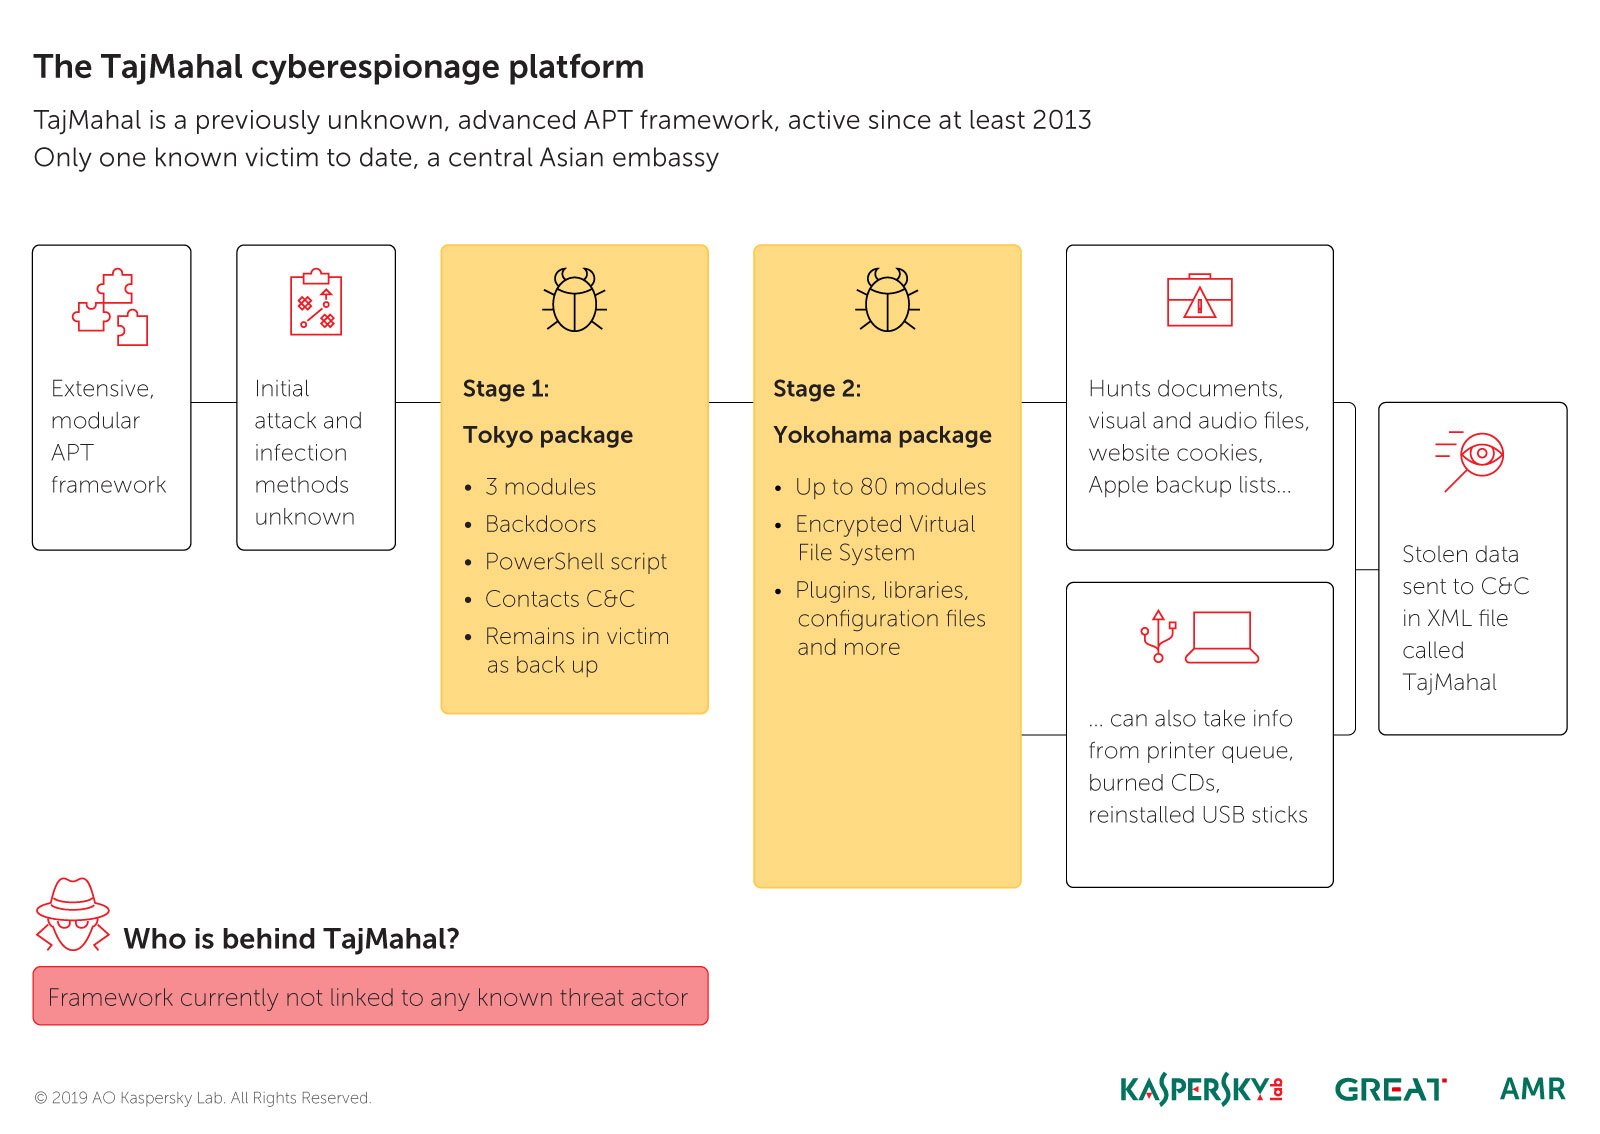
Cybersecurity experts at Kaspersky Lab uncovered a highly sophisticated spyware framework dubbed TajMahal that was involved in cyberespionage campaign for at least last 5 years. Cybersecurity researchers at Kaspersky discovered a highly sophisticated spyware framework, dubbed TajMahal, that has been used in cyber operations for at least last 5 years. The TajMahal framework remained undetected until […]
 Pierluigi Paganini
April 04, 2019
The German chemicals giant Bayer confirmed that of a cyber attack, it confirmed the incident but clarified that no data has been stolen. The chemicals giant Bayer is the last victims of a cyber attack, it confirmed the incident, but pointed out the hackers haven’t stolen any data. According to the company, at the beginning […]
 Pierluigi Paganini
April 03, 2019
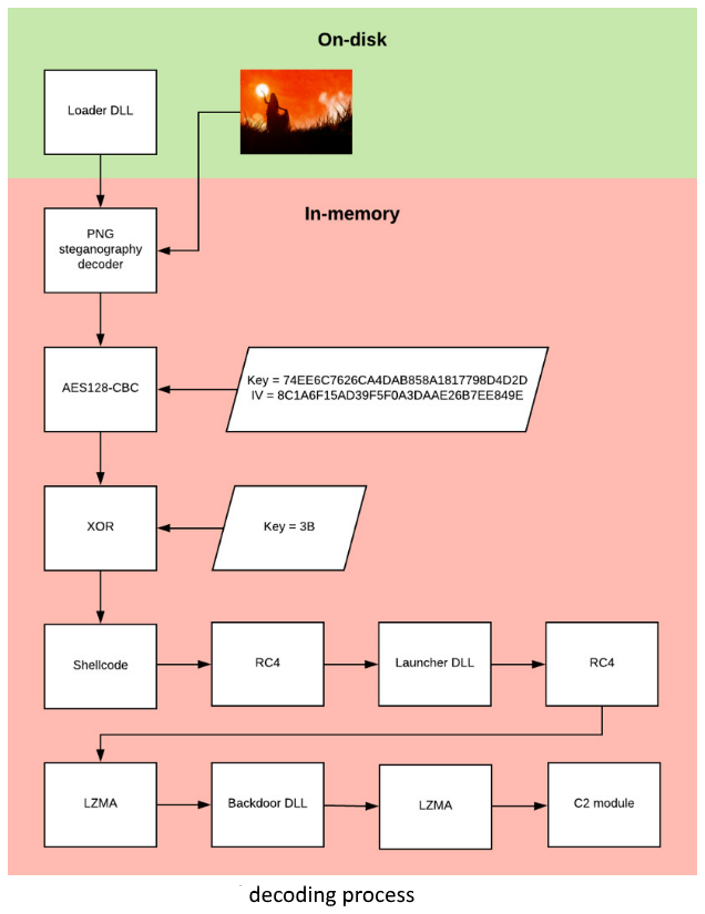
The OceanLotus APT group, also known as APT32 or Cobalt Kitty, leverages a steganography-based loader to deliver backdoors on compromised systems. Security researchers at Cylance discovered that the OceanLotus APT (also known as APT32 or Cobalt Kitty, group is using a loader leveragingsteganography to deliver a version of Denes backdoor and an updated version of […]
 Pierluigi Paganini
March 31, 2019
Microsoft this week announced that it had taken control of 99 domains used by an Iran-linked APT group tracked by the company as Phosphorus. Microsoft has recently announced that it had taken control of 99 domains used by an Iran-linked APT group tracked by the tech giant as Phosphorus (aka APT35, Charming Kitten, NewsBeef, Newscaster […]
 Pierluigi Paganini
March 28, 2019
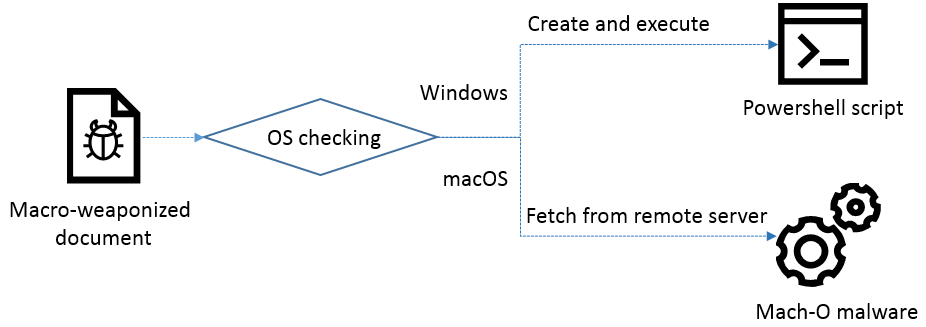
North Korea-linked Lazarus group made the headlines again, it has been leveraging PowerShell to target both Windows and macOS machines. The North Korea-linked Lazarus APT group made has been leveraging PowerShell to target both Windows and macOS machines in a new wave of attacks. The discovery was made by experts at Kaspersky Lab, the campaign […]
 Pierluigi Paganini
March 25, 2019
Operation ShadowHammer – ASUS is the last victim of a clamorous supply chain attack that delivered a backdoor to more than one million users, Kaspersky Lab reported. Over 1 million ASUS users may have been impacted by a supply chain attack that leveraged the ASUS Live Update utility to inject a backdoor in ASUS systems. […]