


 Pierluigi Paganini
 December 21, 2021
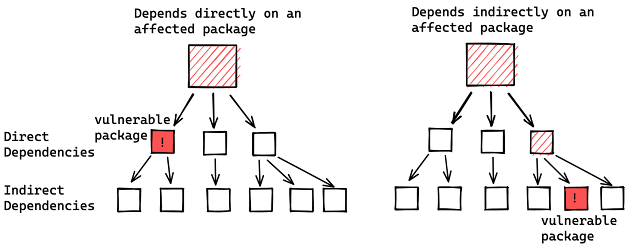
Google found more than 35,000 Java packages in the Maven Central repository that are impacted by flaws in the Apache Log4j library. The Google Open Source Team scanned the Maven Central Java package repository and found that 35,863 packages (8% of the total) were using versions of the Apache Log4j library vulnerable to Log4Shell exploit and […]
 Pierluigi Paganini
December 21, 2021
Uptycs researchers have observed attacks related to miners, DDOS malware and some variants of ransomware actively leveraging LogforShell flaw in log4j. Last week the Log4j vulnerability turned the internet upside down. The impact of the vulnerability is massive and attackers have started taking advantage of the flaw. So far we have observed attacks related to […]
 Pierluigi Paganini
December 20, 2021
The FBI warns that zero-day flaw in Zoho’s ManageEngine Desktop Central has been under active exploitation by nation-state actors since October. The Federal Bureau of Investigation (FBI) revealed that the critical CVE-2021-44515 zero-day vulnerability in Zoho’s ManageEngine Desktop Central has been under active exploitation by nation-state actors since at least October. The CVE-2021-44515 flaw is an authentication bypass vulnerability in ManageEngine Desktop […]
 Pierluigi Paganini
December 20, 2021
The Belgian defense ministry was hit by a cyber attack, it seems that threat actors exploited the Log4Shell vulnerability. The Belgian defense ministry confirmed it was hit by a cyberattack, it seems that threat actors exploited the Log4Shell vulnerability. The attack was uncovered on Thursday and today the government disclosed it, but according to local […]
Pierluigi Paganini
December 20, 2021
Security researchers devised a new attack vector exploiting the Log4Shell vulnerability on servers locally by using a JavaScript WebSocket connection. Researchers from cybersecurity firm Blumira devised a new attack vector that relies on a Javascript WebSocket connection to exploit the Log4Shell vulnerability on internal and locally exposed unpatched Log4j applications. Experts pointed out that this […]
 Pierluigi Paganini
December 19, 2021
Clop ransomware gang stolen confidential data from the UK police and leaked it in the dark web because the victim refused to pay the ransom Clop ransomware operators have stolen confidential information held by some British police, according to the media the cybercriminal gang targeted the IT firm Dacoll. According to the media, the cybercriminals […]
 Pierluigi Paganini
December 19, 2021
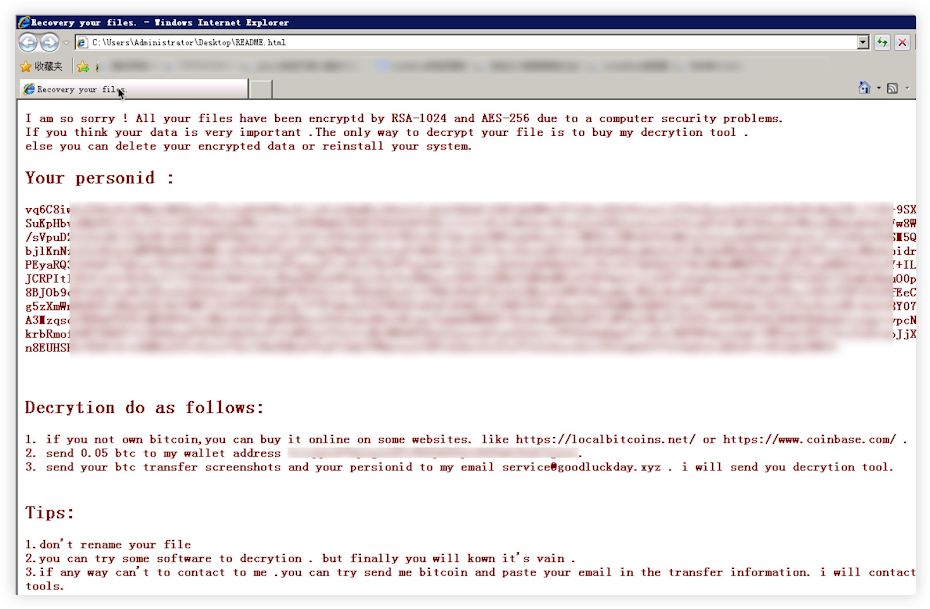
The TellYouThePass ransomware resurged and exploits the Apache Log4j flaw (Log4Shell) to target both Linux and Windows systems. Researchers from KnownSec 404 Team and Sangfor Threat Intelligence Team reported that the TellYouThePass ransomware resurged and is exploiting the Apache Log4j CVE-2021-44228 flaw to target both Linux and Windows systems. “On December 13, Sangfor’s terminal security […]
Pierluigi Paganini
December 18, 2021
Multiple flaws in the Log4J library are scaring organizations worldwide while threat actors are already exploiting them. 2.17 is the third fix issued in a week. While the experts were warning that threat actors are actively attempting to exploit a second vulnerability, tracked as CVE-2021-45046, disclosed in the Log4j library a third security vulnerability made the headlines. […]
 Pierluigi Paganini
December 18, 2021
A cyber attack hit four affiliated online sports gear sites and resulted in the theft of credit cards for 1,813,224 customers. Threat actors have stolen credit cards belonging to 1,813,224 customers of four affiliated online sports gear sites. Below are the affected websites: Tackle Warehouse LLC (tacklewarehouse.com) – Fishing gear Running Warehouse LLC (runningwarehouse.com) – Running apparel […]
 Pierluigi Paganini
December 17, 2021
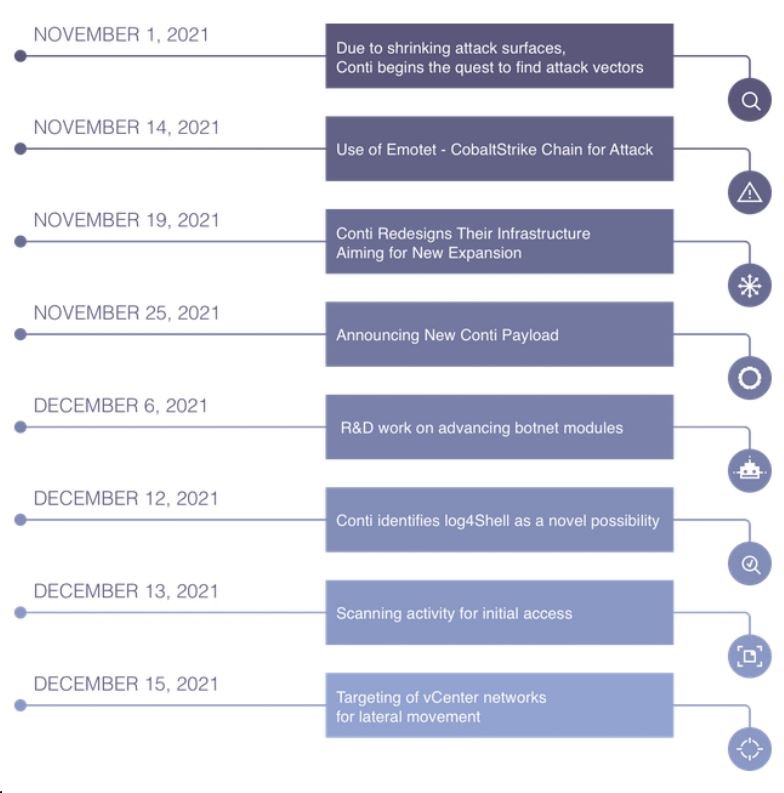
The Conti ransomware gang is the first ransomware operation exploiting the Log4Shell vulnerability to target VMware vCenter Servers. Conti ransomware gang is the first professional race that leverages Log4Shell exploit to compromise VMware vCenter Server installs. The ransomware group used the exploit to target internal devices that are not protected. Conti operators run a private Ransomware-as-a-Service (RaaS), […]
Hacking / September 29, 2026
Artificial Intelligence / September 29, 2026


