 Pierluigi Paganini
 April 24, 2023
EvilExtractor is a new “all-in-one” info stealer for Windows that is being advertised for sale on dark web cybercrime forums. Fortinet FortiGuard Labs researchers discovered a new “all-in-one” info stealer for Windows, dubbed EvilExtractor (sometimes spelled Evil Extractor) that is available for sale on dark web cybercrime forums. EvilExtractor is a modular info-stealer, it exfiltrates […]
 Pierluigi Paganini
April 23, 2023
Non-profit health insurer Point32Health suffered a ransomware attack and has taken systems offline in response to the incident. Non-profit health insurer Point32Health has taken systems offline in response to a ransomware attack that took place on April 17. The insurer immediately launched an investigation into the incident with the help of third-party cybersecurity experts to […]
 Pierluigi Paganini
April 23, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Abandoned Eval PHP WordPress plugin abused to backdoor websites CISA adds MinIO, PaperCut, and Chrome bugs […]
 Pierluigi Paganini
April 22, 2023
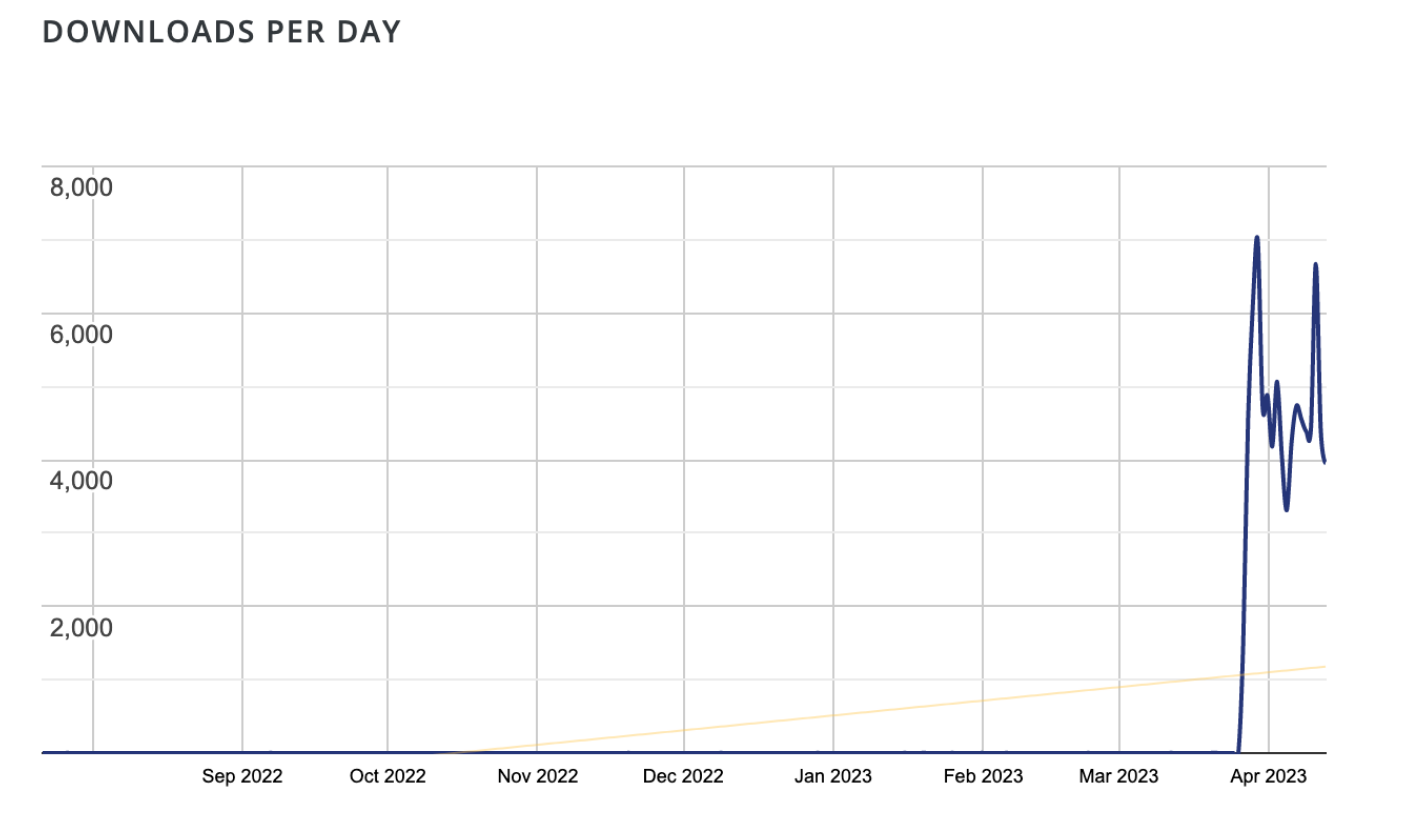
Threat actors were observed installing the abandoned Eval PHP plugin on compromised WordPress sites for backdoor deployment. Researchers from Sucuri warned that threat actors are installing the abandoned Eval PHP plugin on compromised WordPress sites for backdoor deployment. The Eval PHP plugin allows PHP code to be inserted into the pages and posts of WordPress […]
 Pierluigi Paganini
April 20, 2023
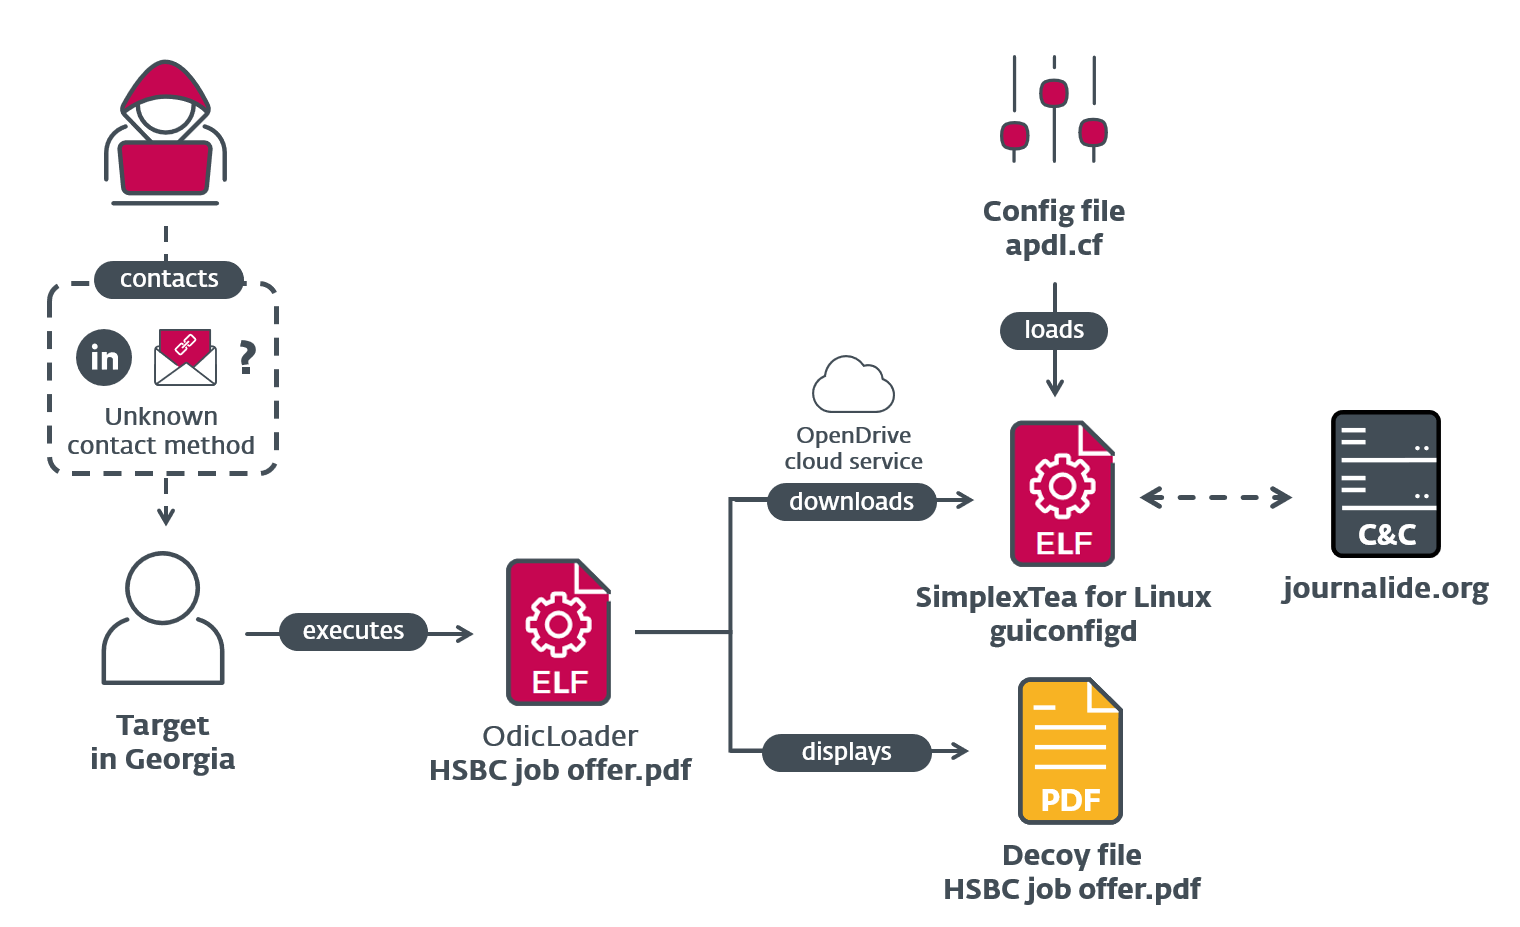
North Korea-linked APT group Lazarus employed new Linux malware in attacks that are part of Operation Dream Job. North Korea-linked APT group Lazarus is behind a new campaign tracked as Operation DreamJob (aka DeathNote or NukeSped) that employed Linux malware. The threat actors were observed using social engineering techniques to compromise its targets, with fake job offers […]
 Pierluigi Paganini
April 20, 2023
The researchers from Google TAG are warning of Russia-linked threat actors targeting Ukraine with phishing campaigns. Russia-linked threat actors launched large-volume phishing campaigns against hundreds of users in Ukraine to gather intelligence and aimed at spreading disinformation, states Google’s Threat Analysis Group (TAG). In Q1 2023, threat actors linked to Russia’s military intelligence service focused their phishing […]
 Pierluigi Paganini
April 20, 2023
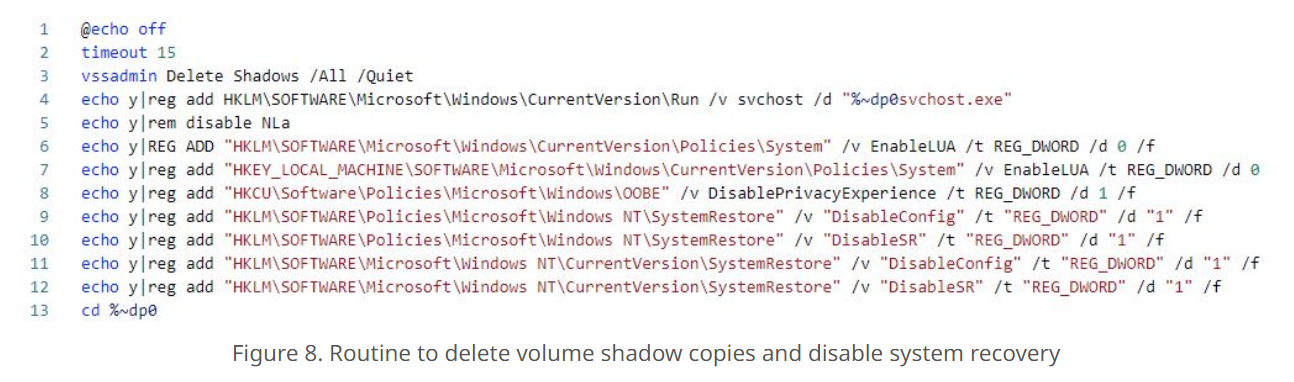
Threat actors are hacking poorly secured and Interned-exposed Microsoft SQL servers to deploy the Trigona ransomware. Threat actors are hacking into poorly secured and public-facing Microsoft SQL servers to deploy Trigona ransomware. Trigona is a malware strain that was discovered in October 2022, and Palo Alto Unit 42 researchers reported similarities between Trigona and the […]
 Pierluigi Paganini
April 19, 2023
UK and US agencies are warning of Russia-linked APT28 group exploiting vulnerabilities in Cisco networking equipment. Russia-linked APT28 group accesses unpatched Cisco routers to deploy malware exploiting the not patched CVE-2017-6742 vulnerability (CVSS score: 8.8), states a joint report published by the UK National Cyber Security Centre (NCSC), the US National Security Agency (NSA), US Cybersecurity and Infrastructure […]
 Pierluigi Paganini
April 19, 2023
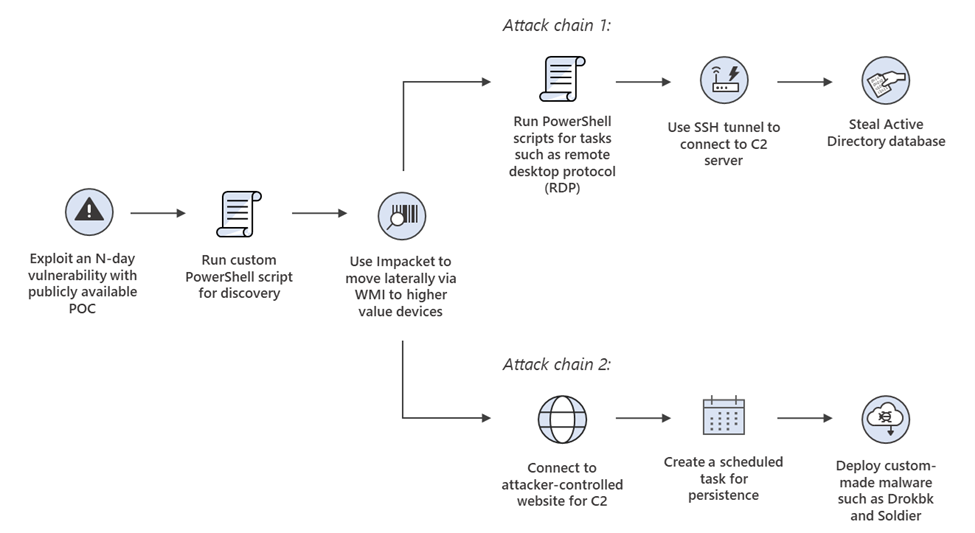
An Iran-linked APT group tracked as Mint Sandstorm is behind a string of attacks aimed at US critical infrastructure between late 2021 to mid-2022. Microsoft has linked the Iranian Mint Sandstorm APT (previously tracked by Microsoft as PHOSPHORUS) to a series of attacks aimed at US critical infrastructure between late 2021 to mid-2022. The IT giant reported Mint […]
 Pierluigi Paganini
April 18, 2023
Security experts from ESET, have temporarily disrupted the operations of the RedLine Stealer with the help of GitHub. ESET researchers announced to have temporarily disrupted the operations of the RedLine Stealer with the help of GitHub. The two companies teamed up with Flare to curb the operations of the malware operators. The experts discovered that […]
Artificial Intelligence / September 30, 2026


Security / September 30, 2026